
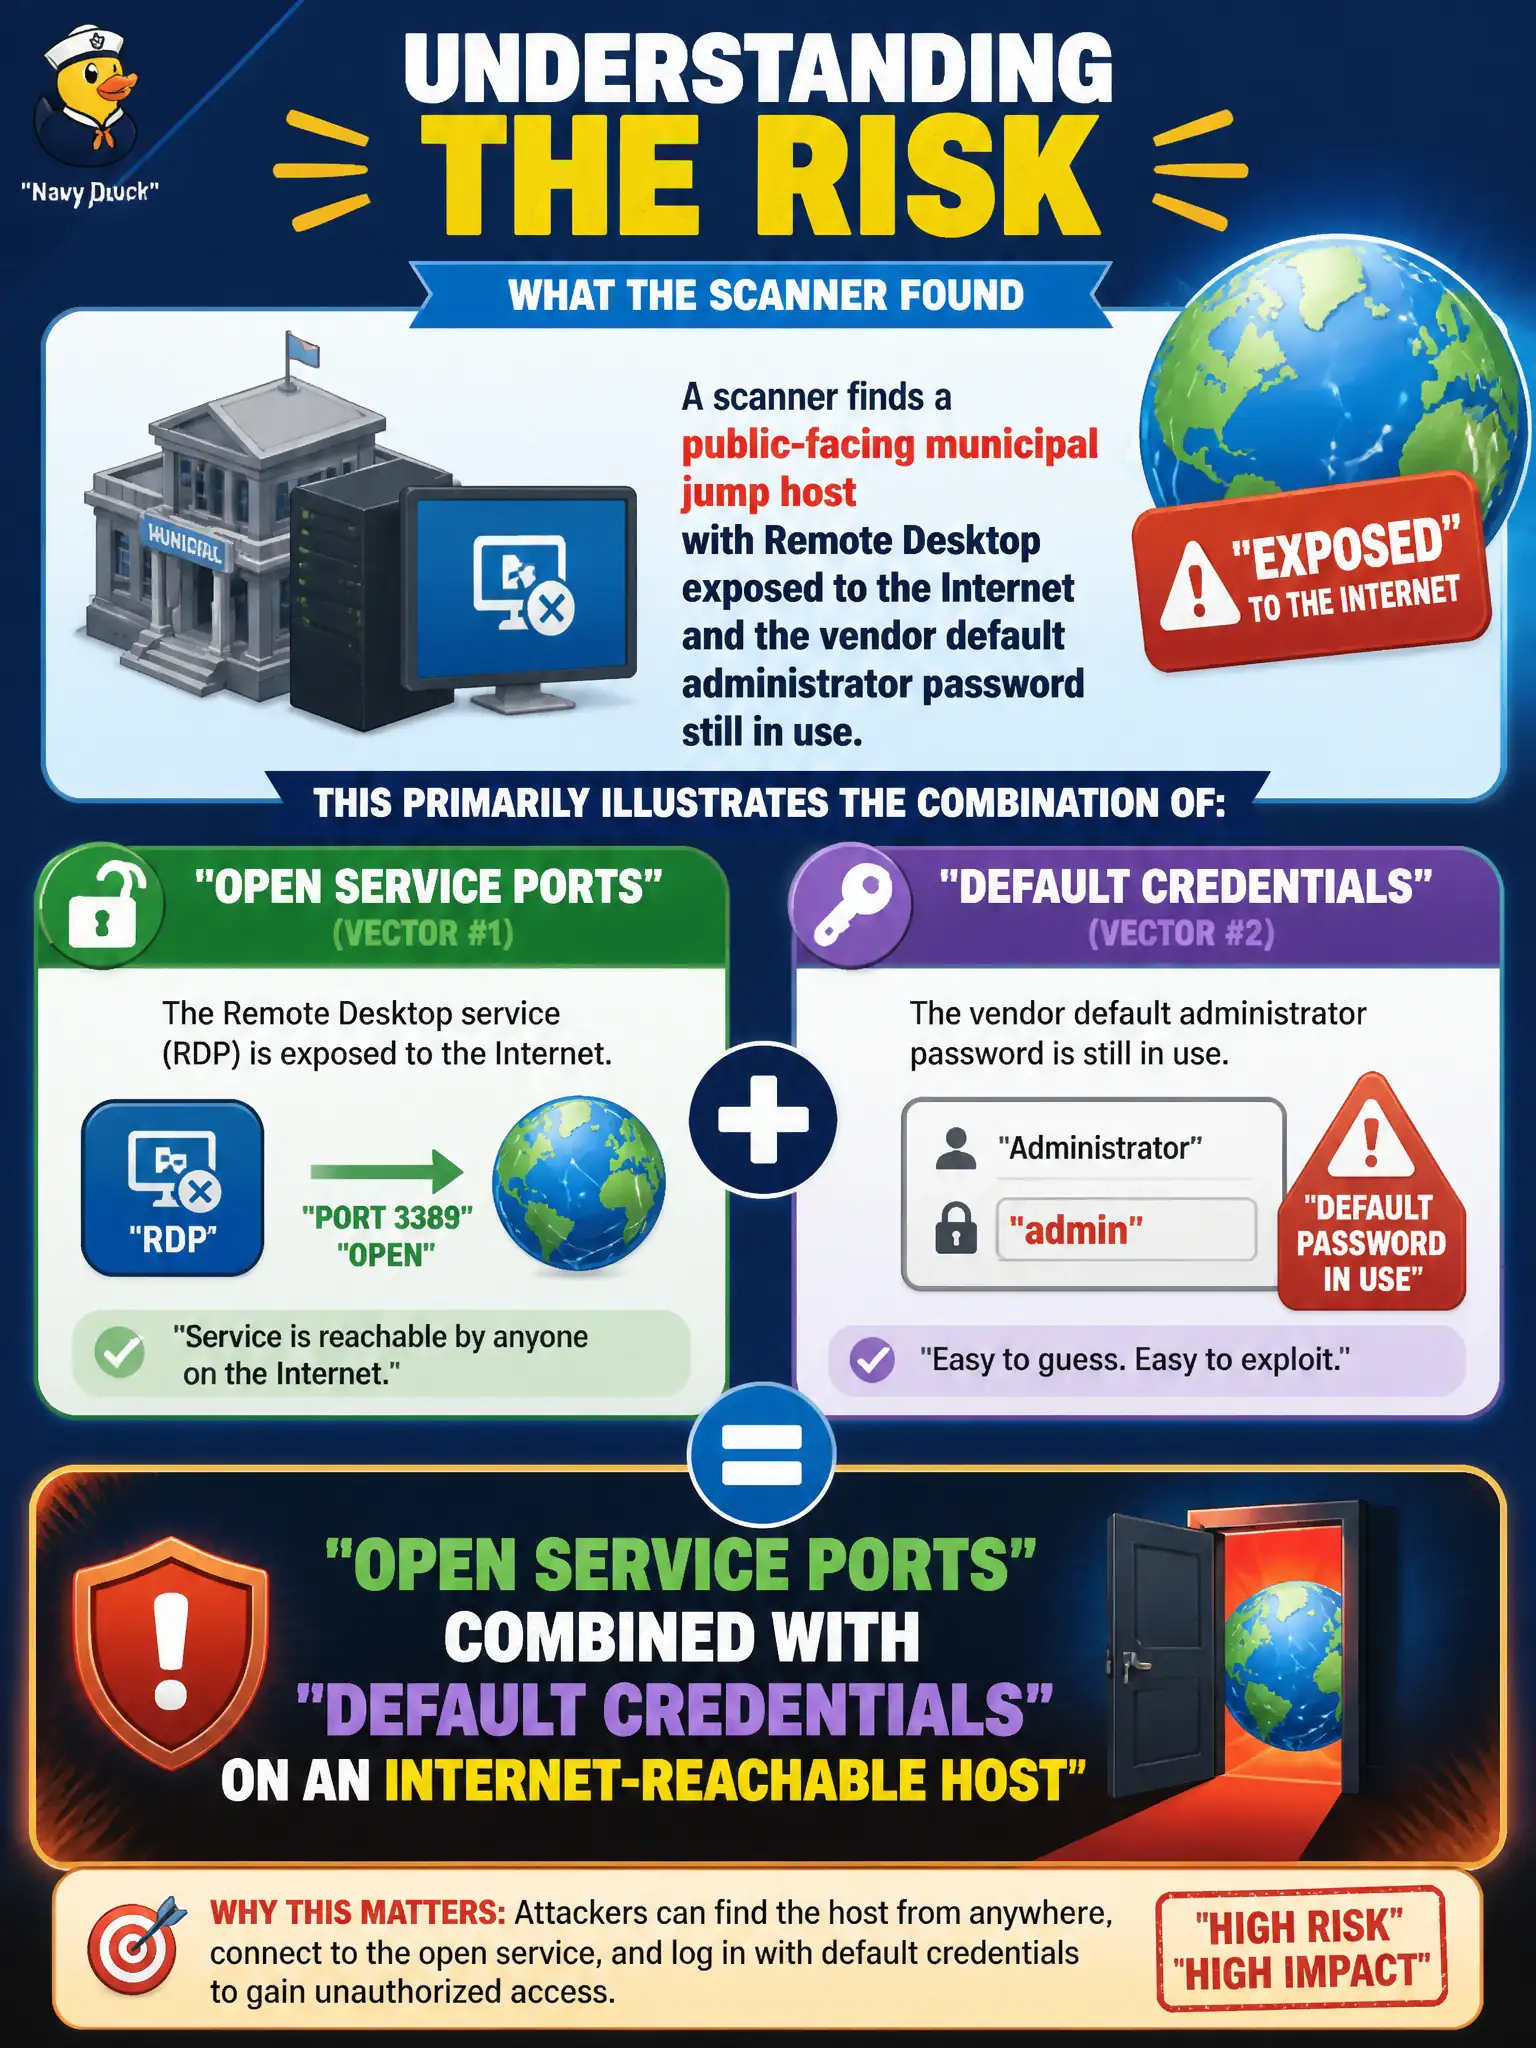
A scanner finds a public-facing municipal jump host with Remote Desktop exposed to the Internet and the vendor default administrator password still in use. Which combination of vectors does this primarily illustrate?
Select an answer to reveal the explanation.
Short Explanation
Open RDP on the Internet plus the factory admin password is the "open ports + default credentials" combo — an unlocked front door with the spare key still under the mat. Fix exposure and change defaults before inventing exotic race-condition theories. Jump hosts belong behind MFA and restricted access, not on the public Internet.
Full Explanation
Open service ports combined with default credentials on an Internet-reachable host is a classic high-severity exposure pair. Remote Desktop published to the world advertises an administrative protocol, and leaving the vendor default administrator password means authentication is trivial. Attackers do not need a novel exploit—scanning plus trying factory defaults often suffices. Municipal jump hosts used for remote administration become ideal footholds when both conditions exist together.
Supply-chain compromise of an MSP’s remote-support tooling abuses trust in a vendor channel after the provider itself is breached. That path may also reach endpoints, but the scanner finding here is direct Internet exposure plus defaults on the city’s own host—not poisoned MSP tooling.
Misinformation on social channels manipulates public trust and can enable phishing during chaos. It does not explain an open RDP listener with factory credentials.
A race condition in a file-permission check is a concurrency/application flaw (TOC/TOU). It is unrelated to network exposure of RDP or unchanged default passwords.
Exam caveat: Questions often combine two simple weaknesses—unnecessary Internet exposure and weak/default credentials—because either alone is bad and together they are catastrophic. Do not reach for exotic vulnerability classes when the stem already names an open administrative port and defaults. Distinguish "default credentials" from "weak but customized passwords" and from "no authentication."
Operational check: remove RDP from public address space; place jump access behind VPN or zero-trust brokers with MFA; rotate all vendor defaults at commissioning; continuously scan Internet-facing ports; and alert on successful logons to privileged local accounts from unexpected geographies. Municipal remote admin should never rely on an unlocked RDP front door.