
City employees receive text messages pretending to be the municipal MFA reset help line and asking for one-time codes. Which attack type is this?
Select an answer to reveal the explanation.
Short Explanation
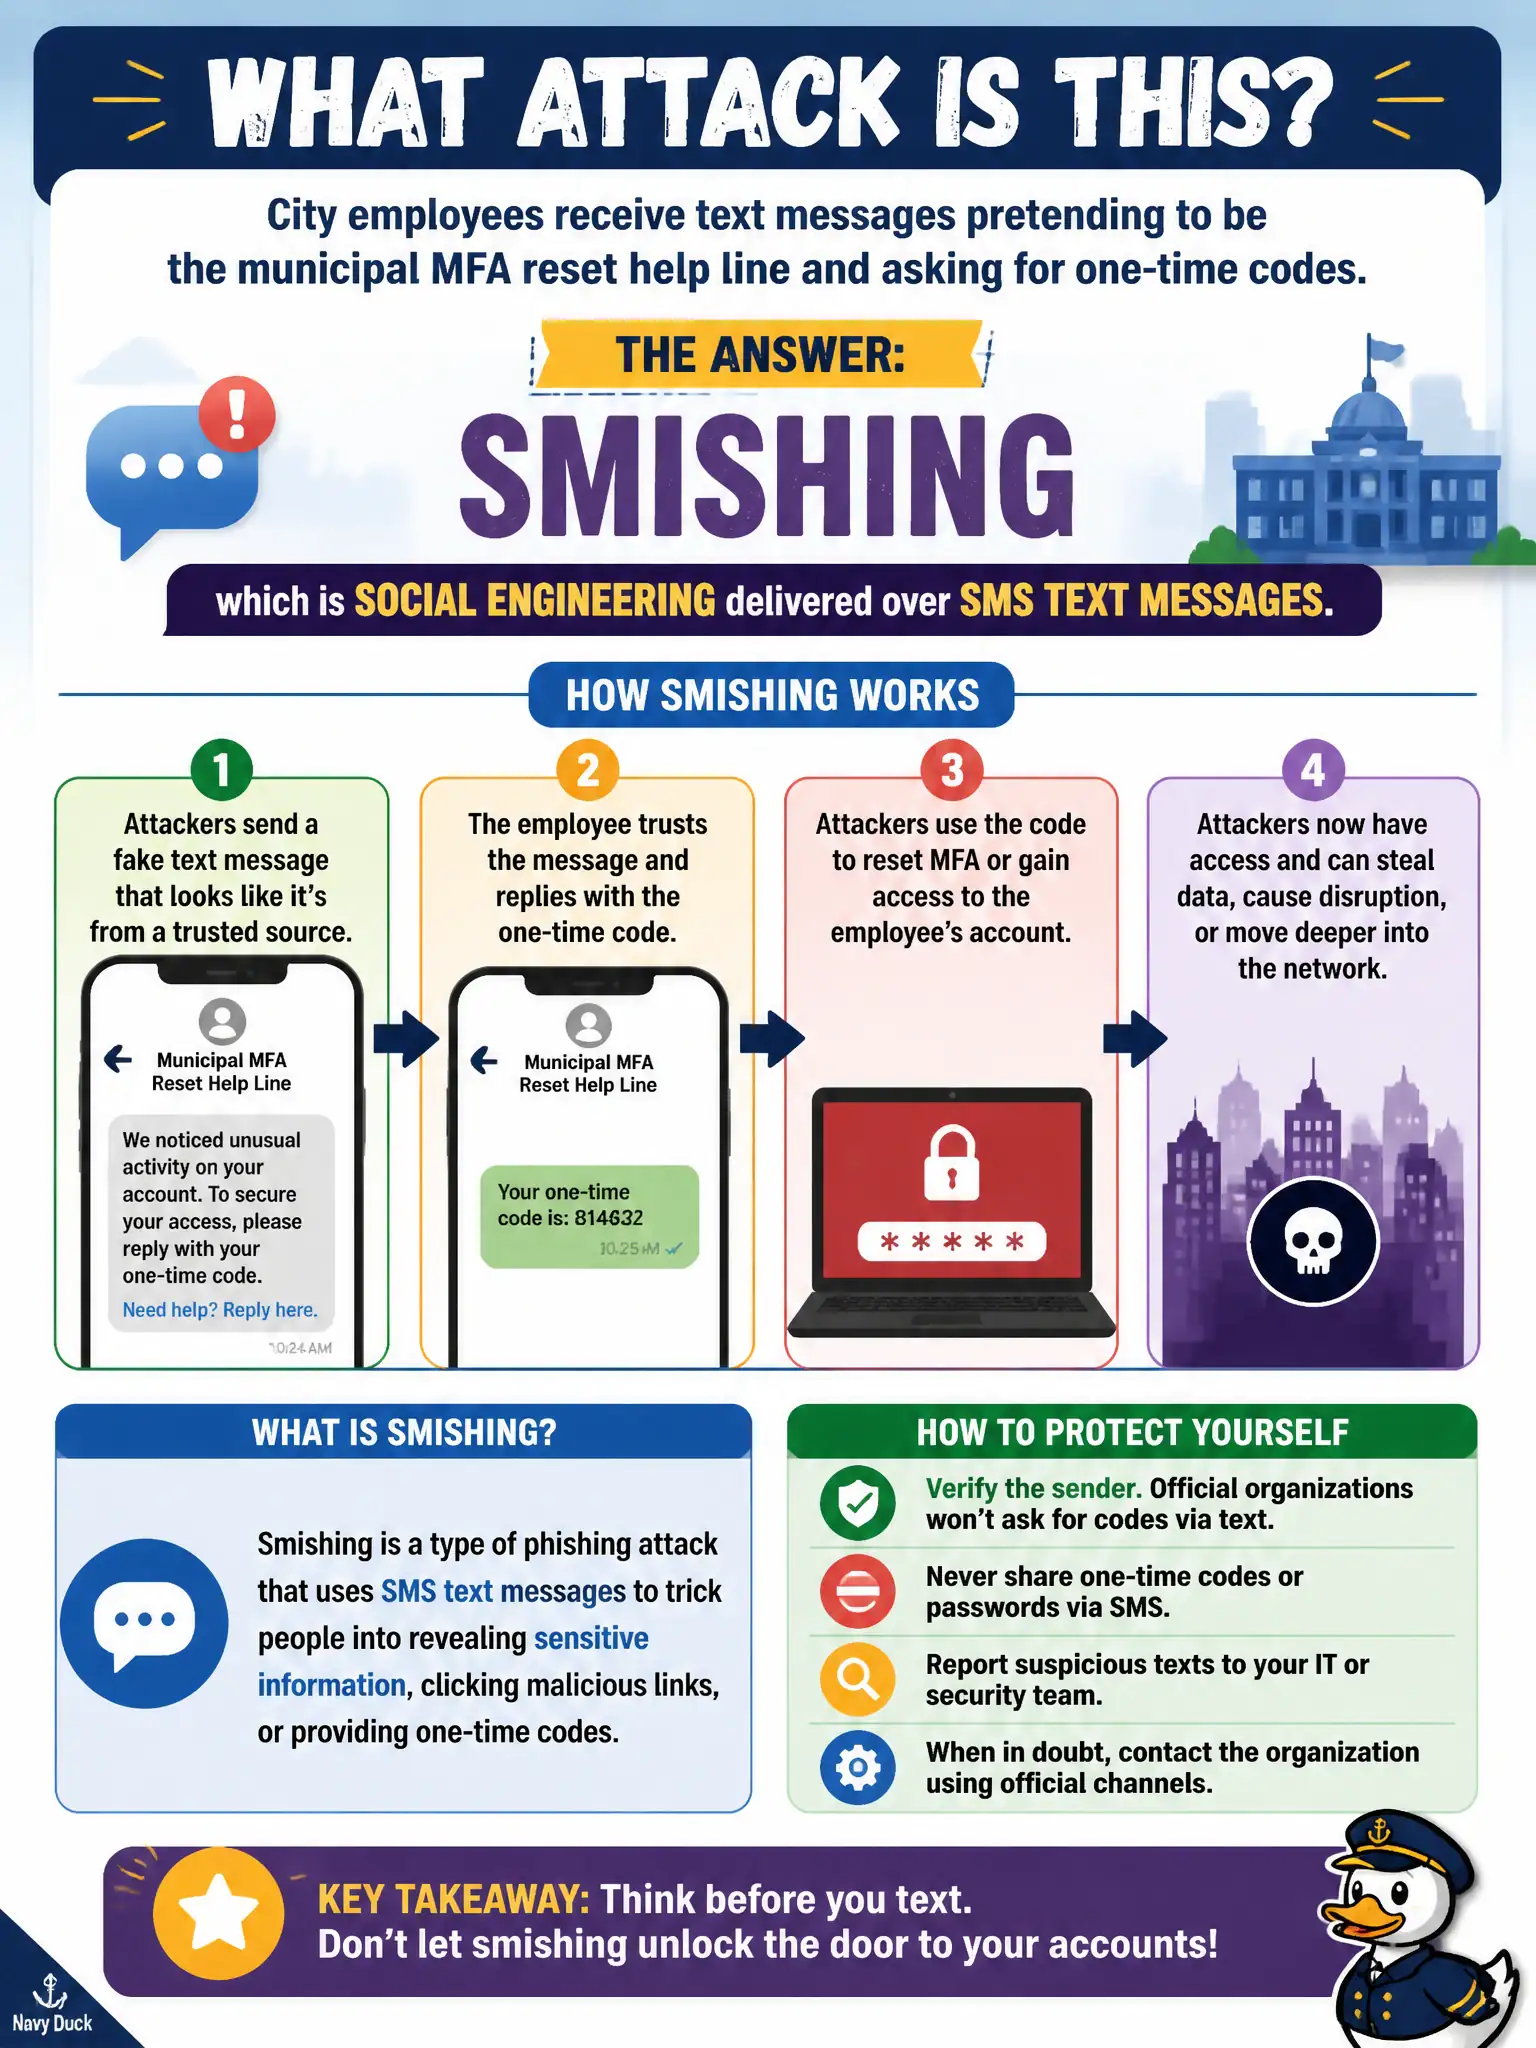
Smishing is phishing's text-message cousin—same con, smaller screen. If the fake MFA help desk shows up as an SMS asking for codes, name the vector smishing, not SQL injection.
Full Explanation
Text messages pretending to be the municipal MFA reset help line and asking for one-time codes are smishing: social engineering delivered over SMS or similar text channels. The lure impersonates a trusted IT function to harvest credentials or MFA codes on a small screen where users may scrutinize URLs and grammar less carefully than on desktop email. Naming the vector correctly drives the right user training and filtering controls.
Whaling that exclusively targets executives through paper postal mail is a different channel and typically a high-value executive-focused pretext, not mass SMS MFA harvesting. SQL injection against a public web form is an application injection attack with no messaging channel. Credential stuffing that only replays breached passwords against VPN portals is automated reuse of leaked password pairs, not an interactive SMS social-engineering conversation requesting codes.
Exam caveat: smishing equals phishing over SMS; distinguish by channel from email phishing, vishing, whaling, and technical attacks like SQLi or stuffing. Operational check: tell city staff that MFA help never solicits codes by text, enable SMS filtering where feasible, prefer authenticator apps or hardware tokens less exposed to SMS interception, and monitor identity systems for MFA fatigue or sudden code misuse after reported smishing waves.