
A federal grantor asks for a formal assurance statement on security controls for a homelessness-services platform. Which engagement type is designed to provide that kind of assurance reporting?
Select an answer to reveal the explanation.
Short Explanation
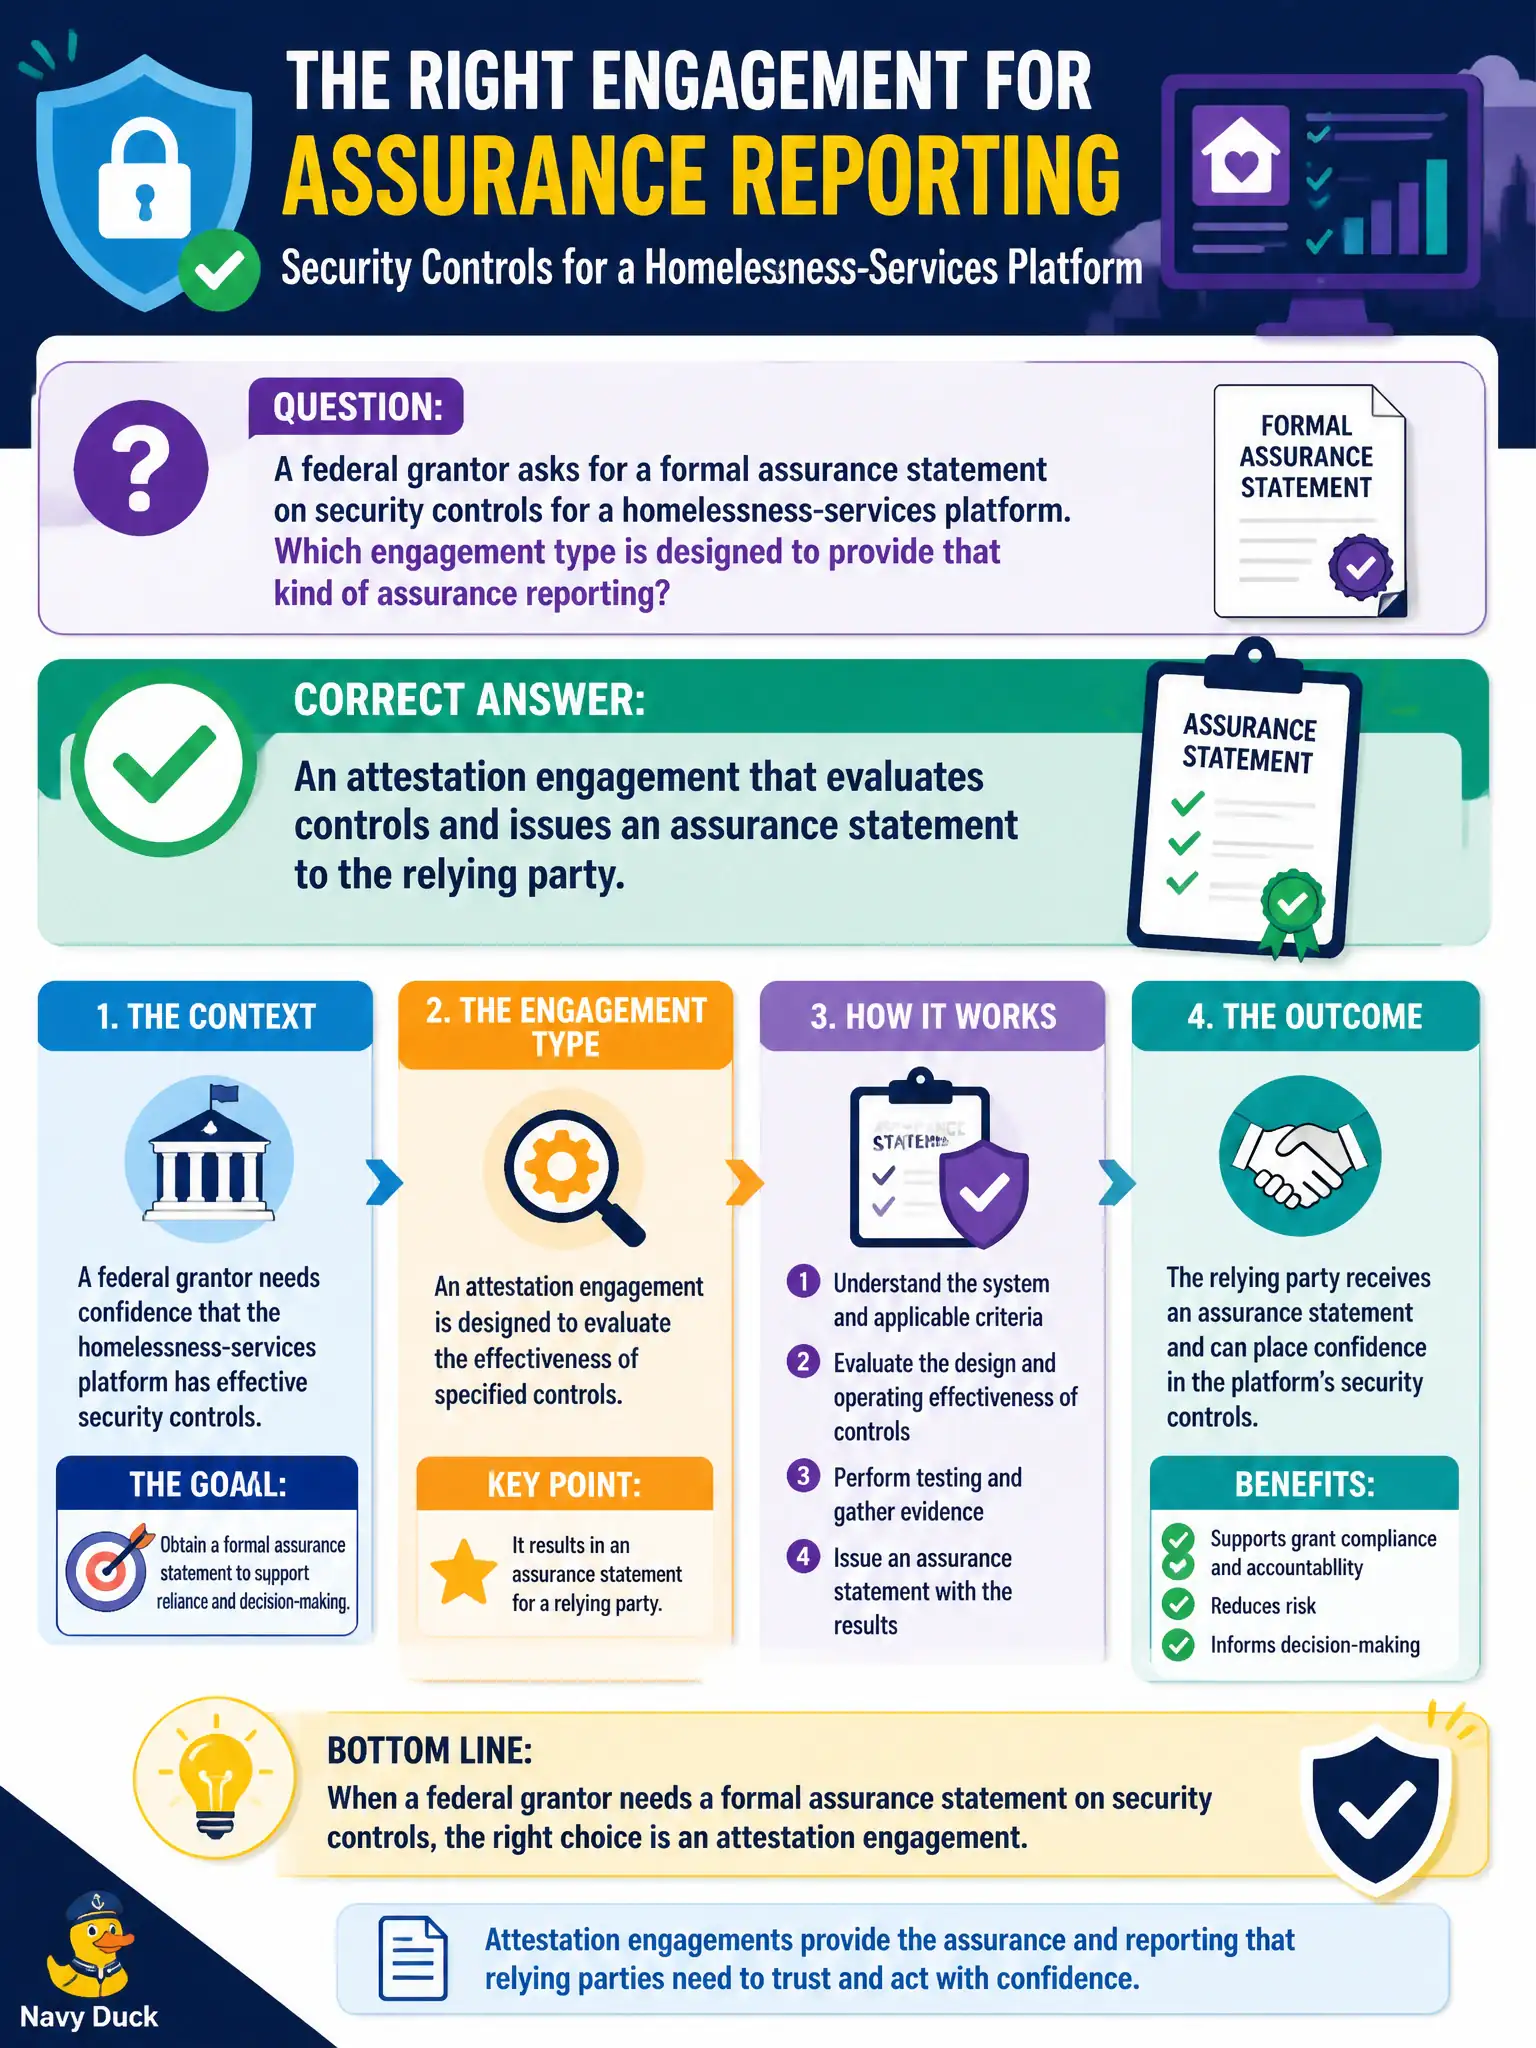
Grantors don’t want vibes—they want an attestation: a formal 'we looked, here’s our assurance' letter. That’s different from a pep talk or a poster.
Full Explanation
When a federal grantor asks for a formal assurance statement on security controls for a homelessness-services platform, the engagement type designed for that outcome is an attestation engagement. Attestation evaluates controls against defined criteria and issues an assurance statement the relying party can use. That differs from informal sentiment checks, marketing narratives, or exercises that practice communications without producing control assurance.
An informal Slack poll about how secure developers feel is opinion, not assurance. A marketing case study without testing or control evaluation cannot support a grantor’s reliance. A tabletop focused only on ransomware talking points may improve incident communication readiness but does not substitute for control evaluation and an assurance report.
Exam caveat: Security+ program and oversight content links attestation to assurance reporting for relying parties (customers, grantors, regulators). Do not confuse it with polls, marketing, or limited tabletops.
Operational check: engage qualified independent practitioners, agree criteria and scope (system description, trust services categories or equivalent), remediate material gaps before fieldwork when possible, and deliver the resulting report package to the grant office on schedule with management representation letters as required.