
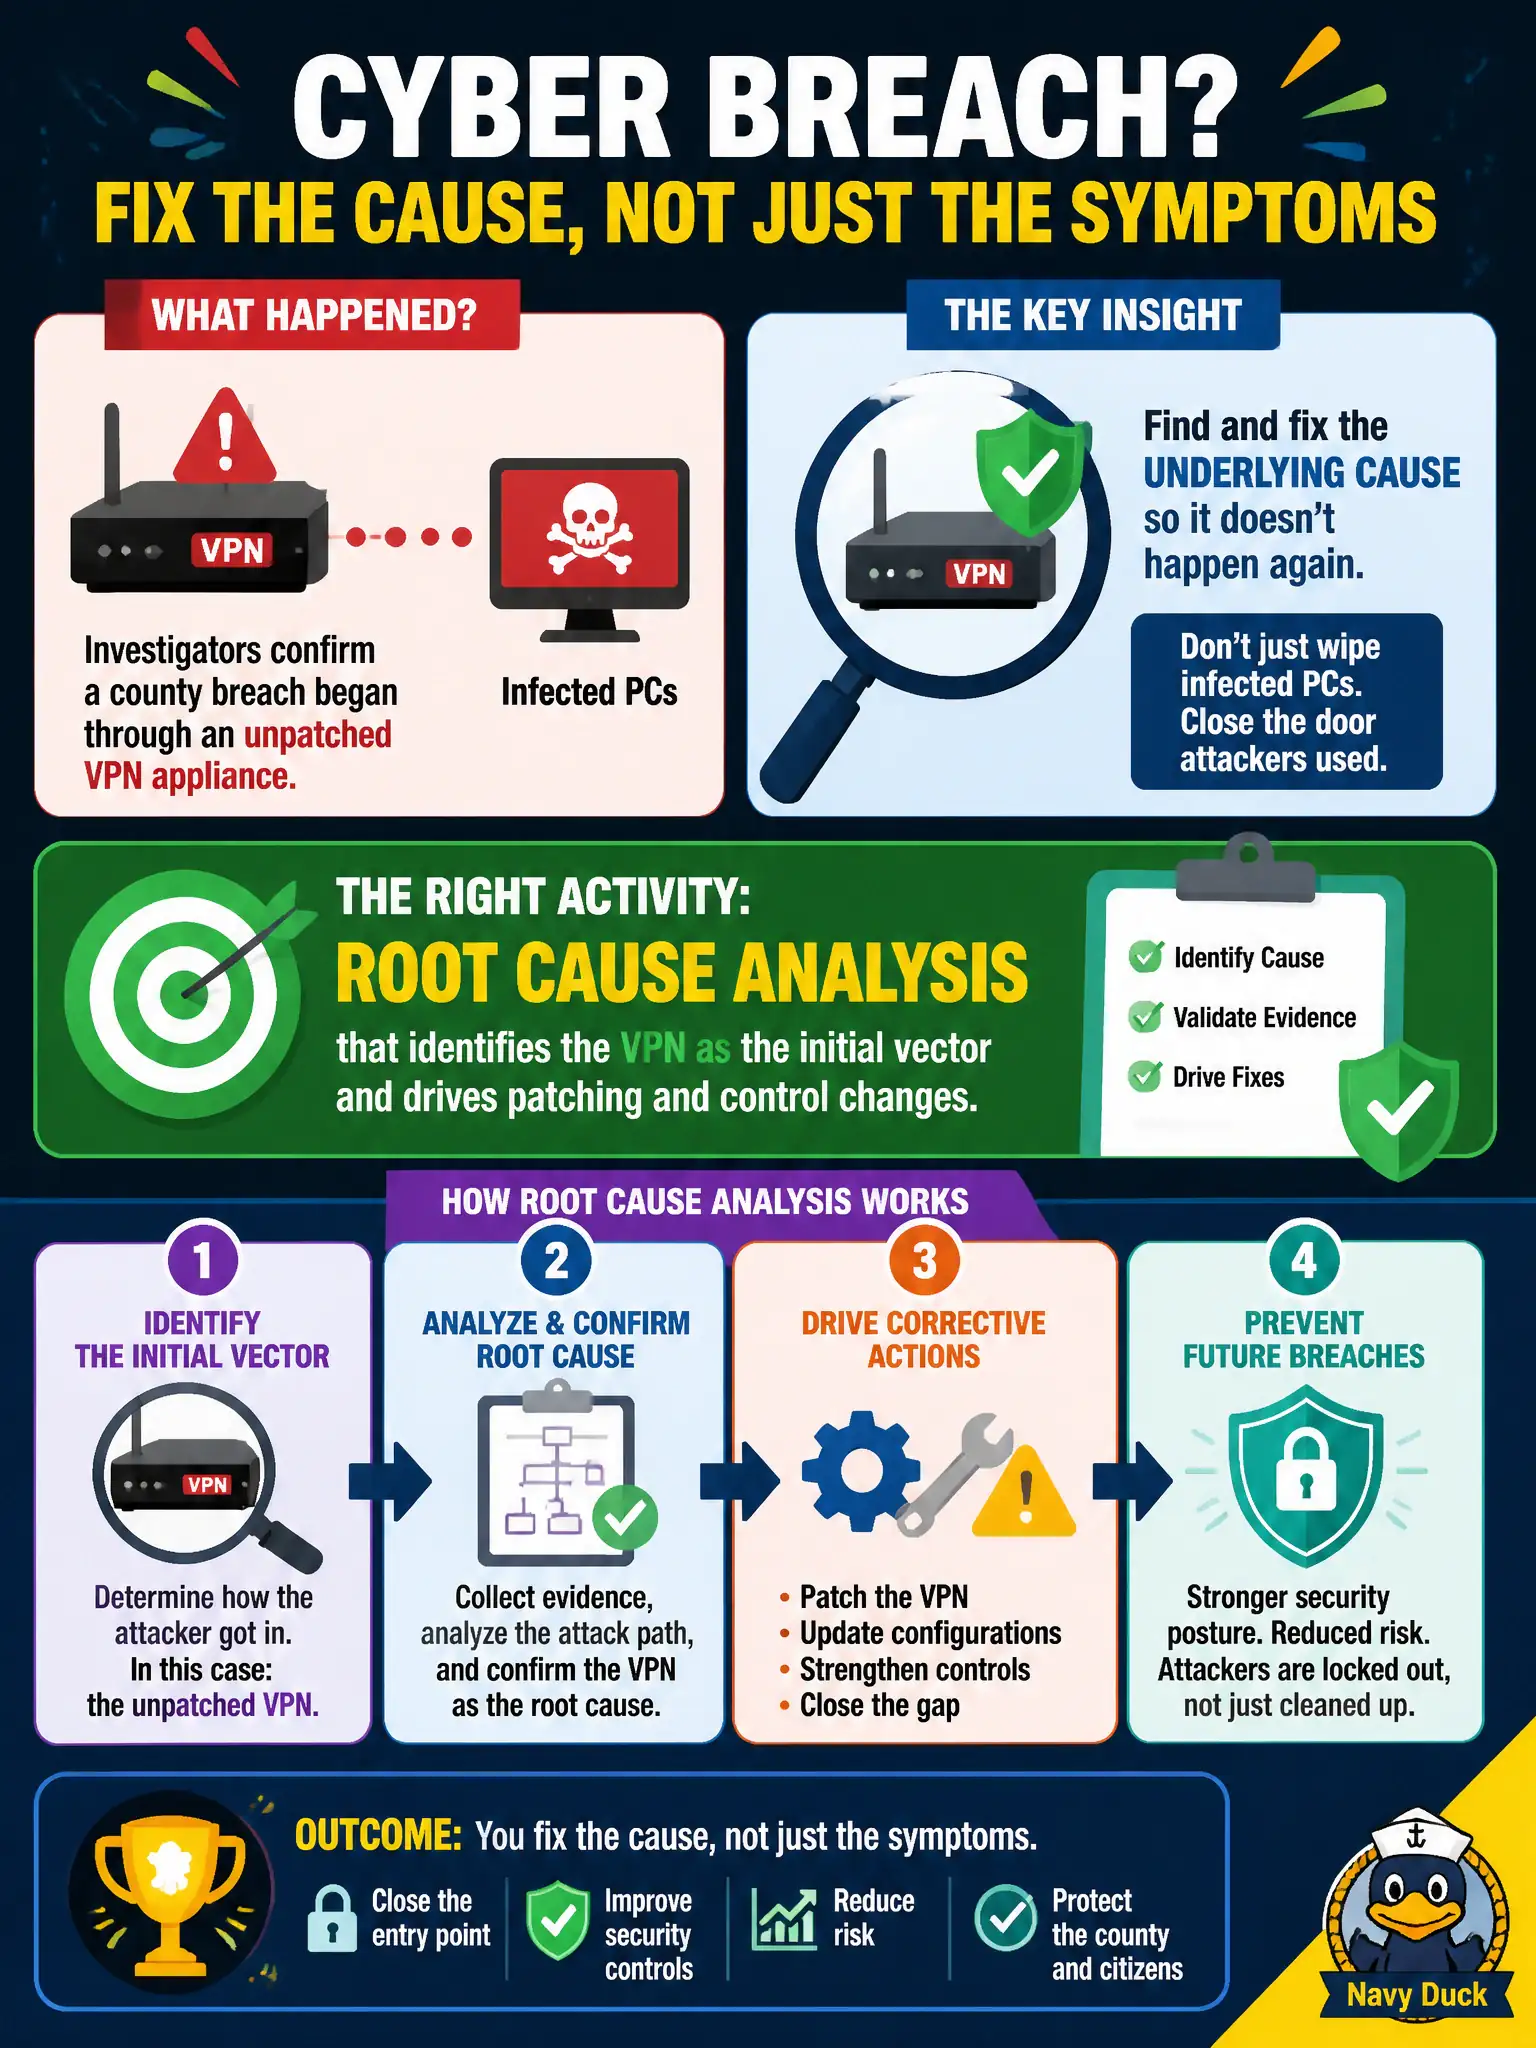
Investigators confirm a county breach began through an unpatched VPN appliance. Which activity ensures fixes address that underlying cause rather than only wiping infected PCs?
Select an answer to reveal the explanation.
Short Explanation
Root cause analysis asks how the burglar got the key, not just which rooms look messy. Finding the unpatched VPN as the entry means the county patches and hardens that path, not only scrubbing laptops. Wipe-and-restore without RCA invites the same break-in next week.
Full Explanation
Root cause analysis determines how the attacker gained and retained access so remediation closes the real entry path. When investigators confirm an unpatched VPN appliance as the initial vector into county systems, RCA drives patching or replacement of that VPN, hardening of remote-access controls, improved vulnerability management, and verification that similar edge devices are not equally exposed. Cleaning laptops without fixing the VPN leaves the burglar’s key under the mat. Sound RCA uses timelines, log correlation, and asset/vulnerability context to separate initial access, execution, persistence, and impact—then assigns owners to each corrective action.
Deleting endpoint malware samples without reviewing how access was obtained preserves neither evidence nor understanding of the vector. Restoring user files while leaving the VPN on obsolete firmware reconstitutes data on a still-exposed path and invites immediate reinfection. Password resets for accounts that never used the VPN may be irrelevant theater if the foothold was appliance-level compromise or VPN-authenticated accounts that still need targeted credential and session invalidation after the edge is fixed. Exam tip: stems that contrast wiping symptoms with fixing the entry point are pointing at root cause analysis. Operationally, require an RCA section in every major county IR report naming the initial vector, contributing control failures, and verified remediation (patch level, config baseline, monitoring coverage) before declaring the VPN-related incident fully closed.