
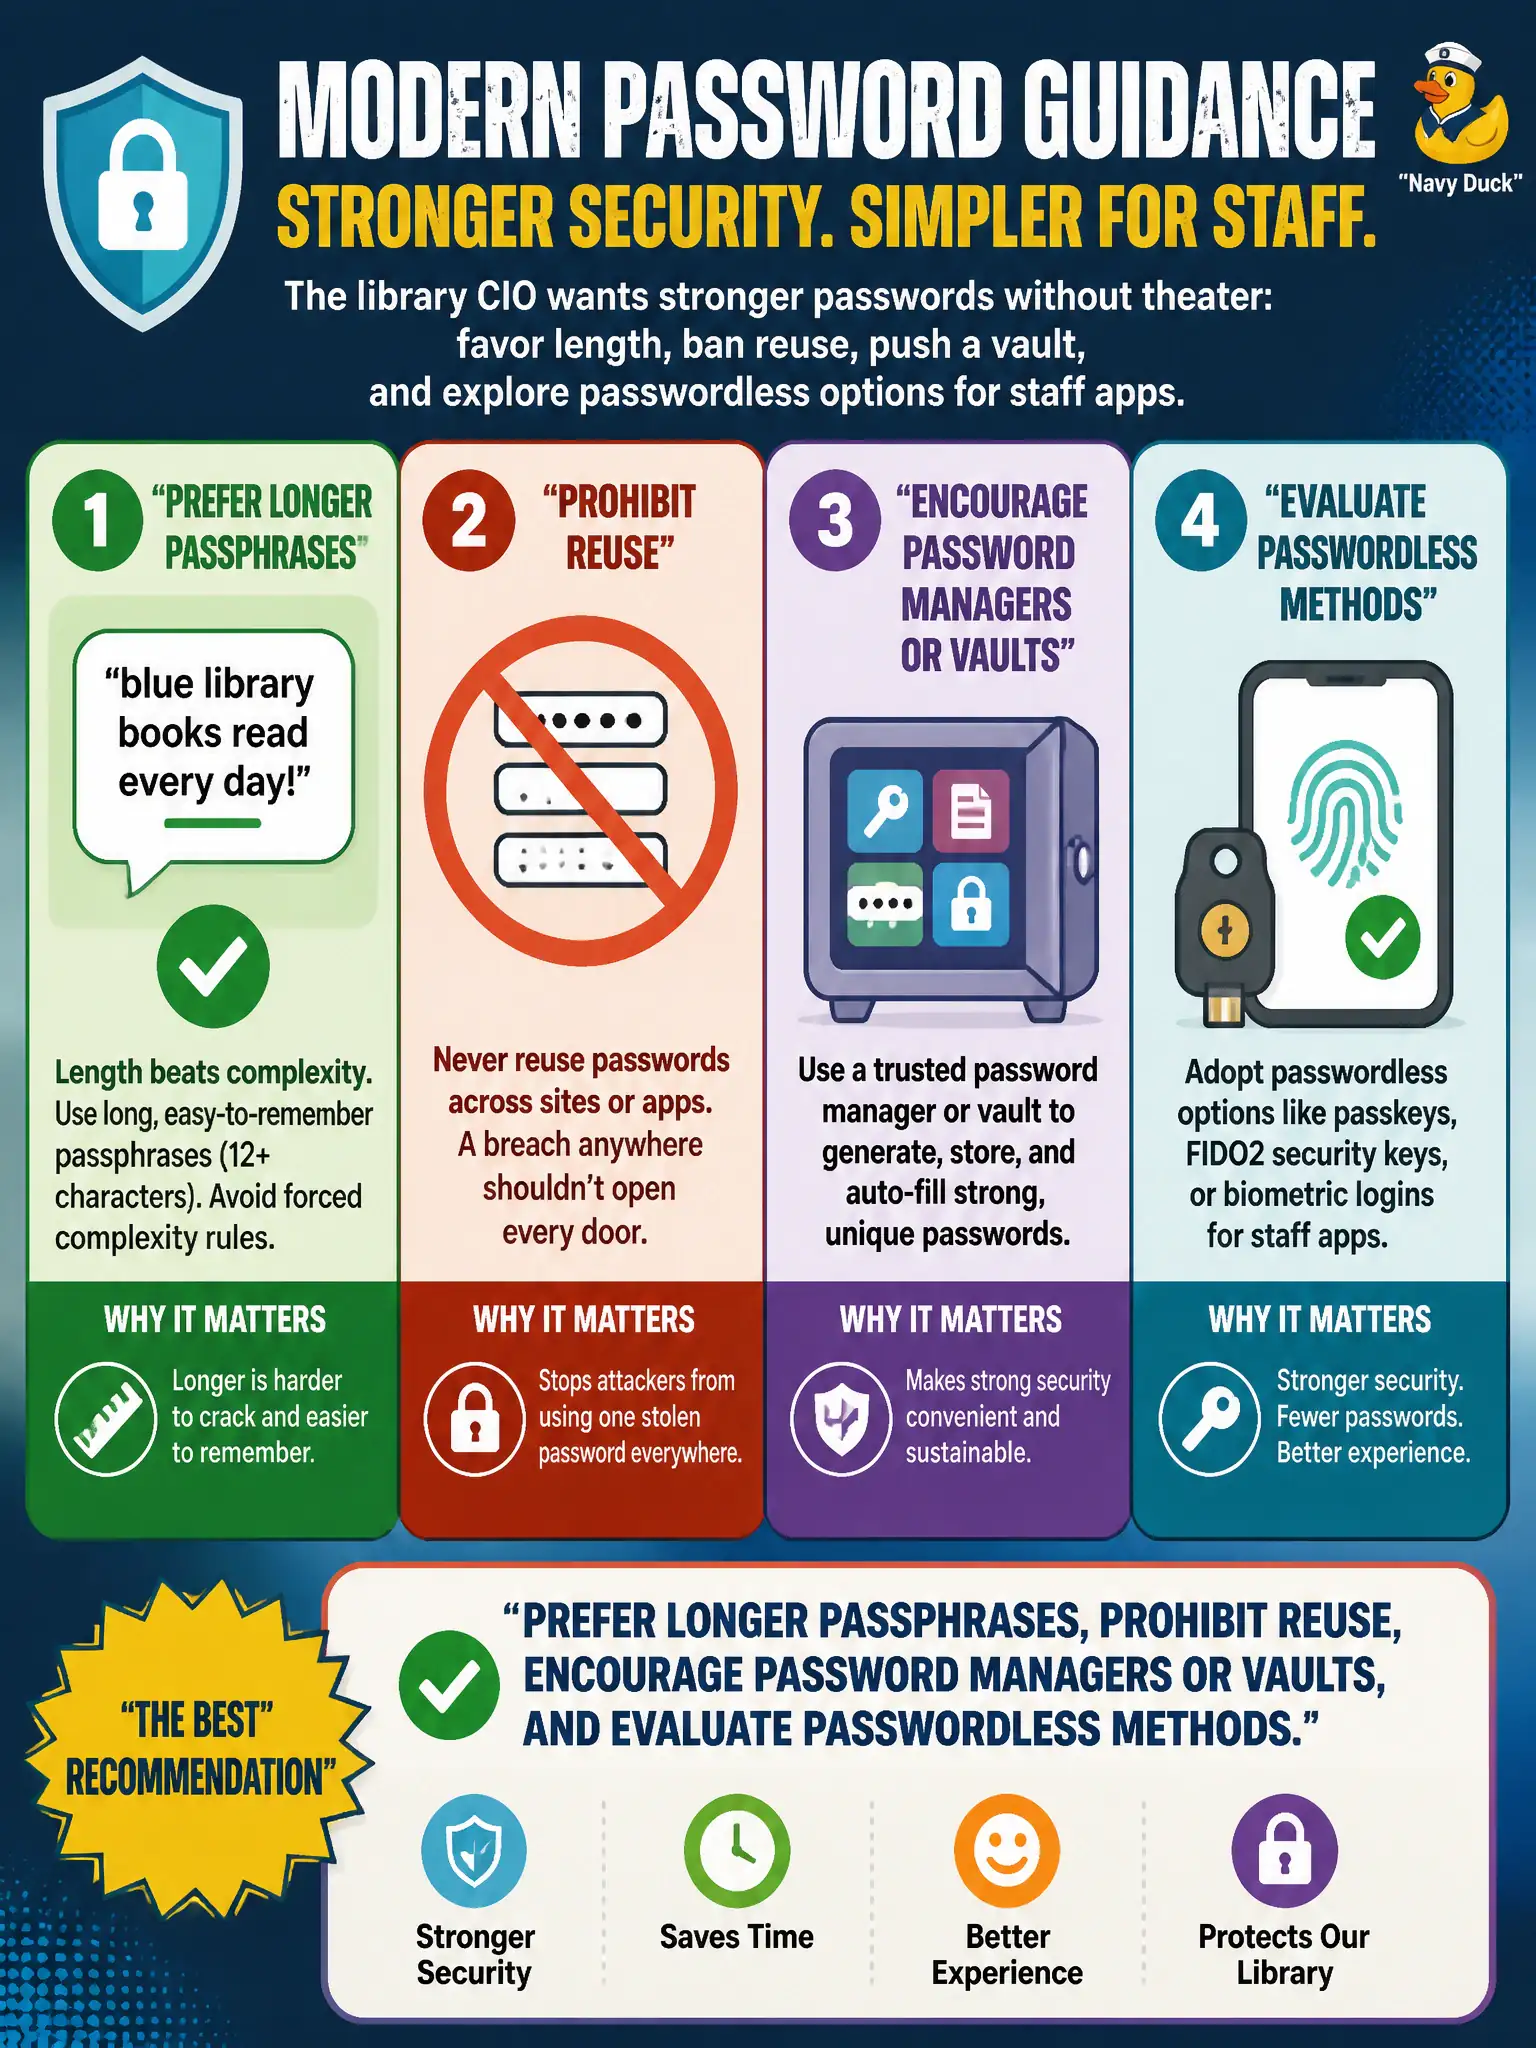
The library CIO wants stronger passwords without theater: favor length, ban reuse, push a vault, and explore passwordless options for staff apps. Which recommendation best matches modern password guidance?
Select an answer to reveal the explanation.
Short Explanation
Long unique passphrases in a vault beat short 'P@ssw0rd1' gymnastics every week. Add passwordless where it fits and stop recycling the same secret across library apps.
Full Explanation
Modern password guidance for municipal library staff favors longer passphrases, bans reuse across applications, encourages password managers or enterprise vaults, and evaluates passwordless methods where supported. Length and uniqueness beat short, frequently rotated complexity theater; vaults reduce unsafe reuse and sticky-note storage; passwordless options (for example FIDO/passkeys where apps allow) can further shrink password exposure for staff-facing systems. That package matches current best practice without inventing security theater that users will bypass.
Mandating weekly changes to short complex passwords while forbidding password managers drives predictable patterns, reuse, and written secrets—contrary to modern guidance that de-emphasizes arbitrary frequent rotation absent compromise. Requiring only eight characters with a mandatory special character while allowing reuse across apps leaves accounts vulnerable to stuffing after any single breach. Printing passwords on laminated badges worn in public stacks is credential exposure by design.
Exam caveat: longer is better, but blocked common/breached passwords and MFA still matter; passwordless is an evaluation path, not an instant mandate for every legacy library system. Distinguish password policy from MFA—strong passwords do not replace a second factor for remote and privileged access.
Operational check: set library IdP policy for high minimum length or passphrase-friendly rules, enable breached-password blocking if available, deploy an approved vault, prohibit reuse via policy and tooling, and trial passwordless on a pilot staff app before broad rollout.