
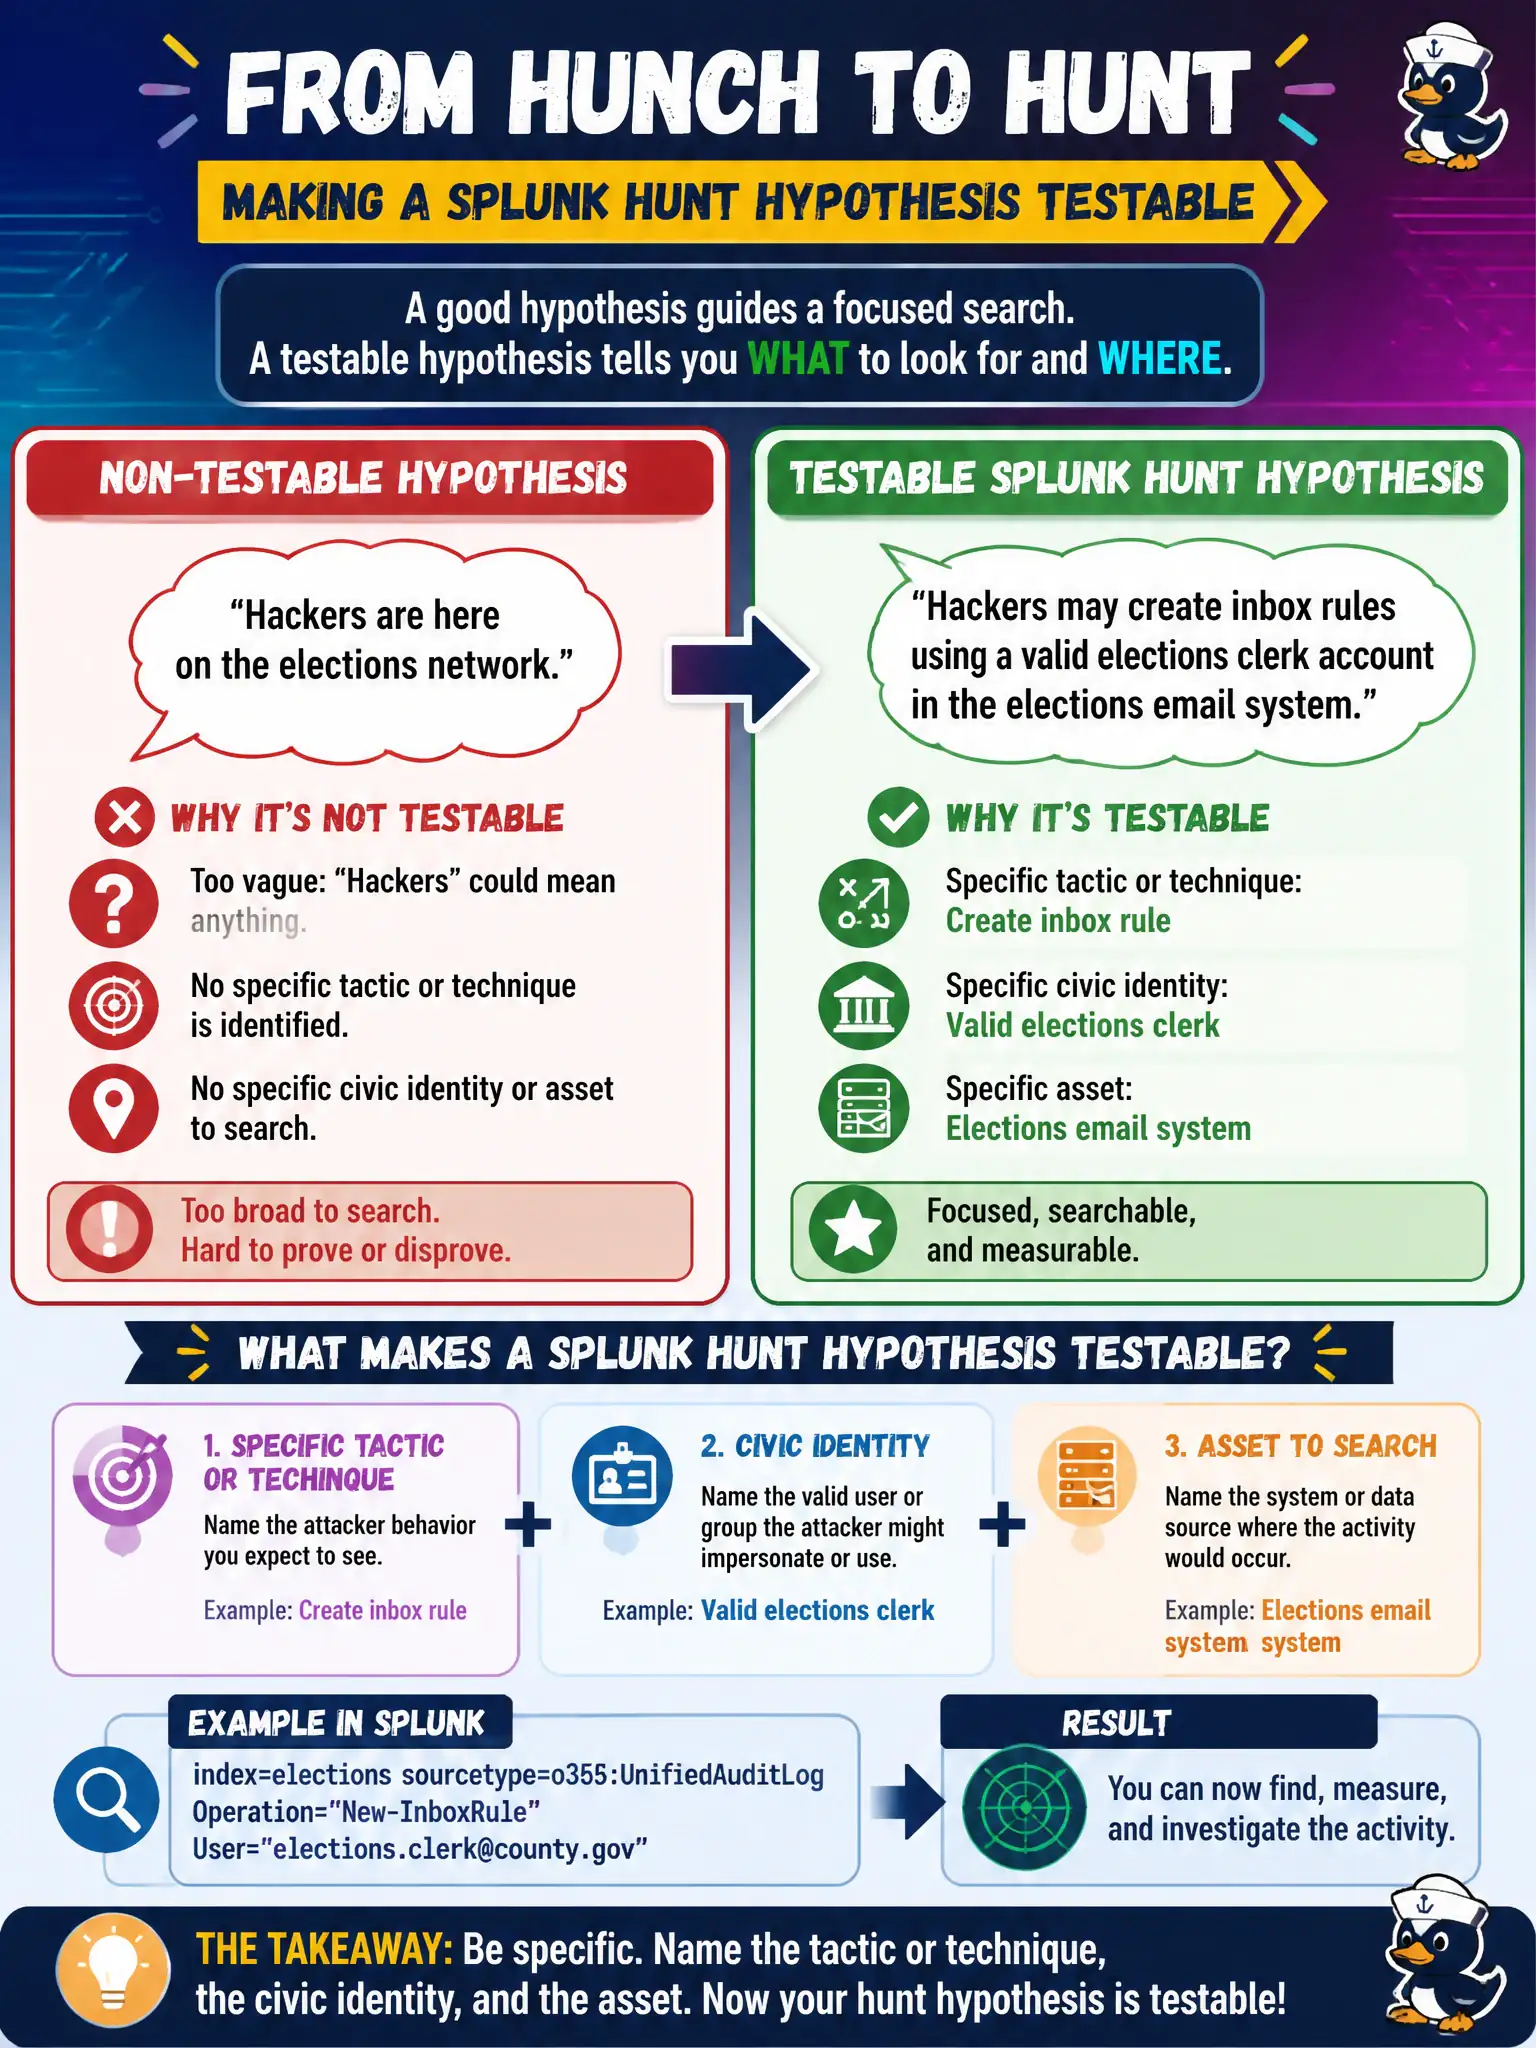
A junior hunter proposes the hypothesis that hackers are here on the elections network. What change makes it a testable Splunk hunt hypothesis?
Select an answer to reveal the explanation.
Short Explanation
Saying hackers are here is like saying something is wet during a flood. Name the tactic and the civic identity or asset so Splunk has somewhere to look. Vague hunts never refute anything.
Full Explanation
A useful Splunk hunt hypothesis names a specific tactic or technique plus the civic identity or asset under test so SPL can confirm or refute a concrete claim. Changing "hackers are here on the elections network" into a testable hypothesis means specifying something such as a valid elections clerk creating an inbox forwarding rule—or another named technique on a named municipal identity or asset—rather than a slogan. Broadening the claim to any attacker anywhere in the city makes the hypothesis unfalsifiable and unsearchable. Replacing it with a plan to wait until ES dashboards surface something abandons active hypothesis hunting. Converting it into a SOAR Python playbook before searching jumps to automation authoring that is outside the Defense Analyst hunting sequence and still lacks a testable claim. Exam caveat: Defense Analyst hunting starts with a specific, testable story tied to tactic and civic object—not slogans, dashboard waiting, or premature playbook coding. Operational check: rewrite the junior's claim as "valid elections clerk creates inbox rule then accesses elections file share," identify Authentication and Email sources, run constrained SPL for that identity, and record confirm or refute with contributing events.