
A court SOC wants CIS Controls and NIST mappings on the same notables that already show MITRE ATT&CK. What should the defense analyst understand about Enterprise Security annotations?
Select an answer to reveal the explanation.
Short Explanation
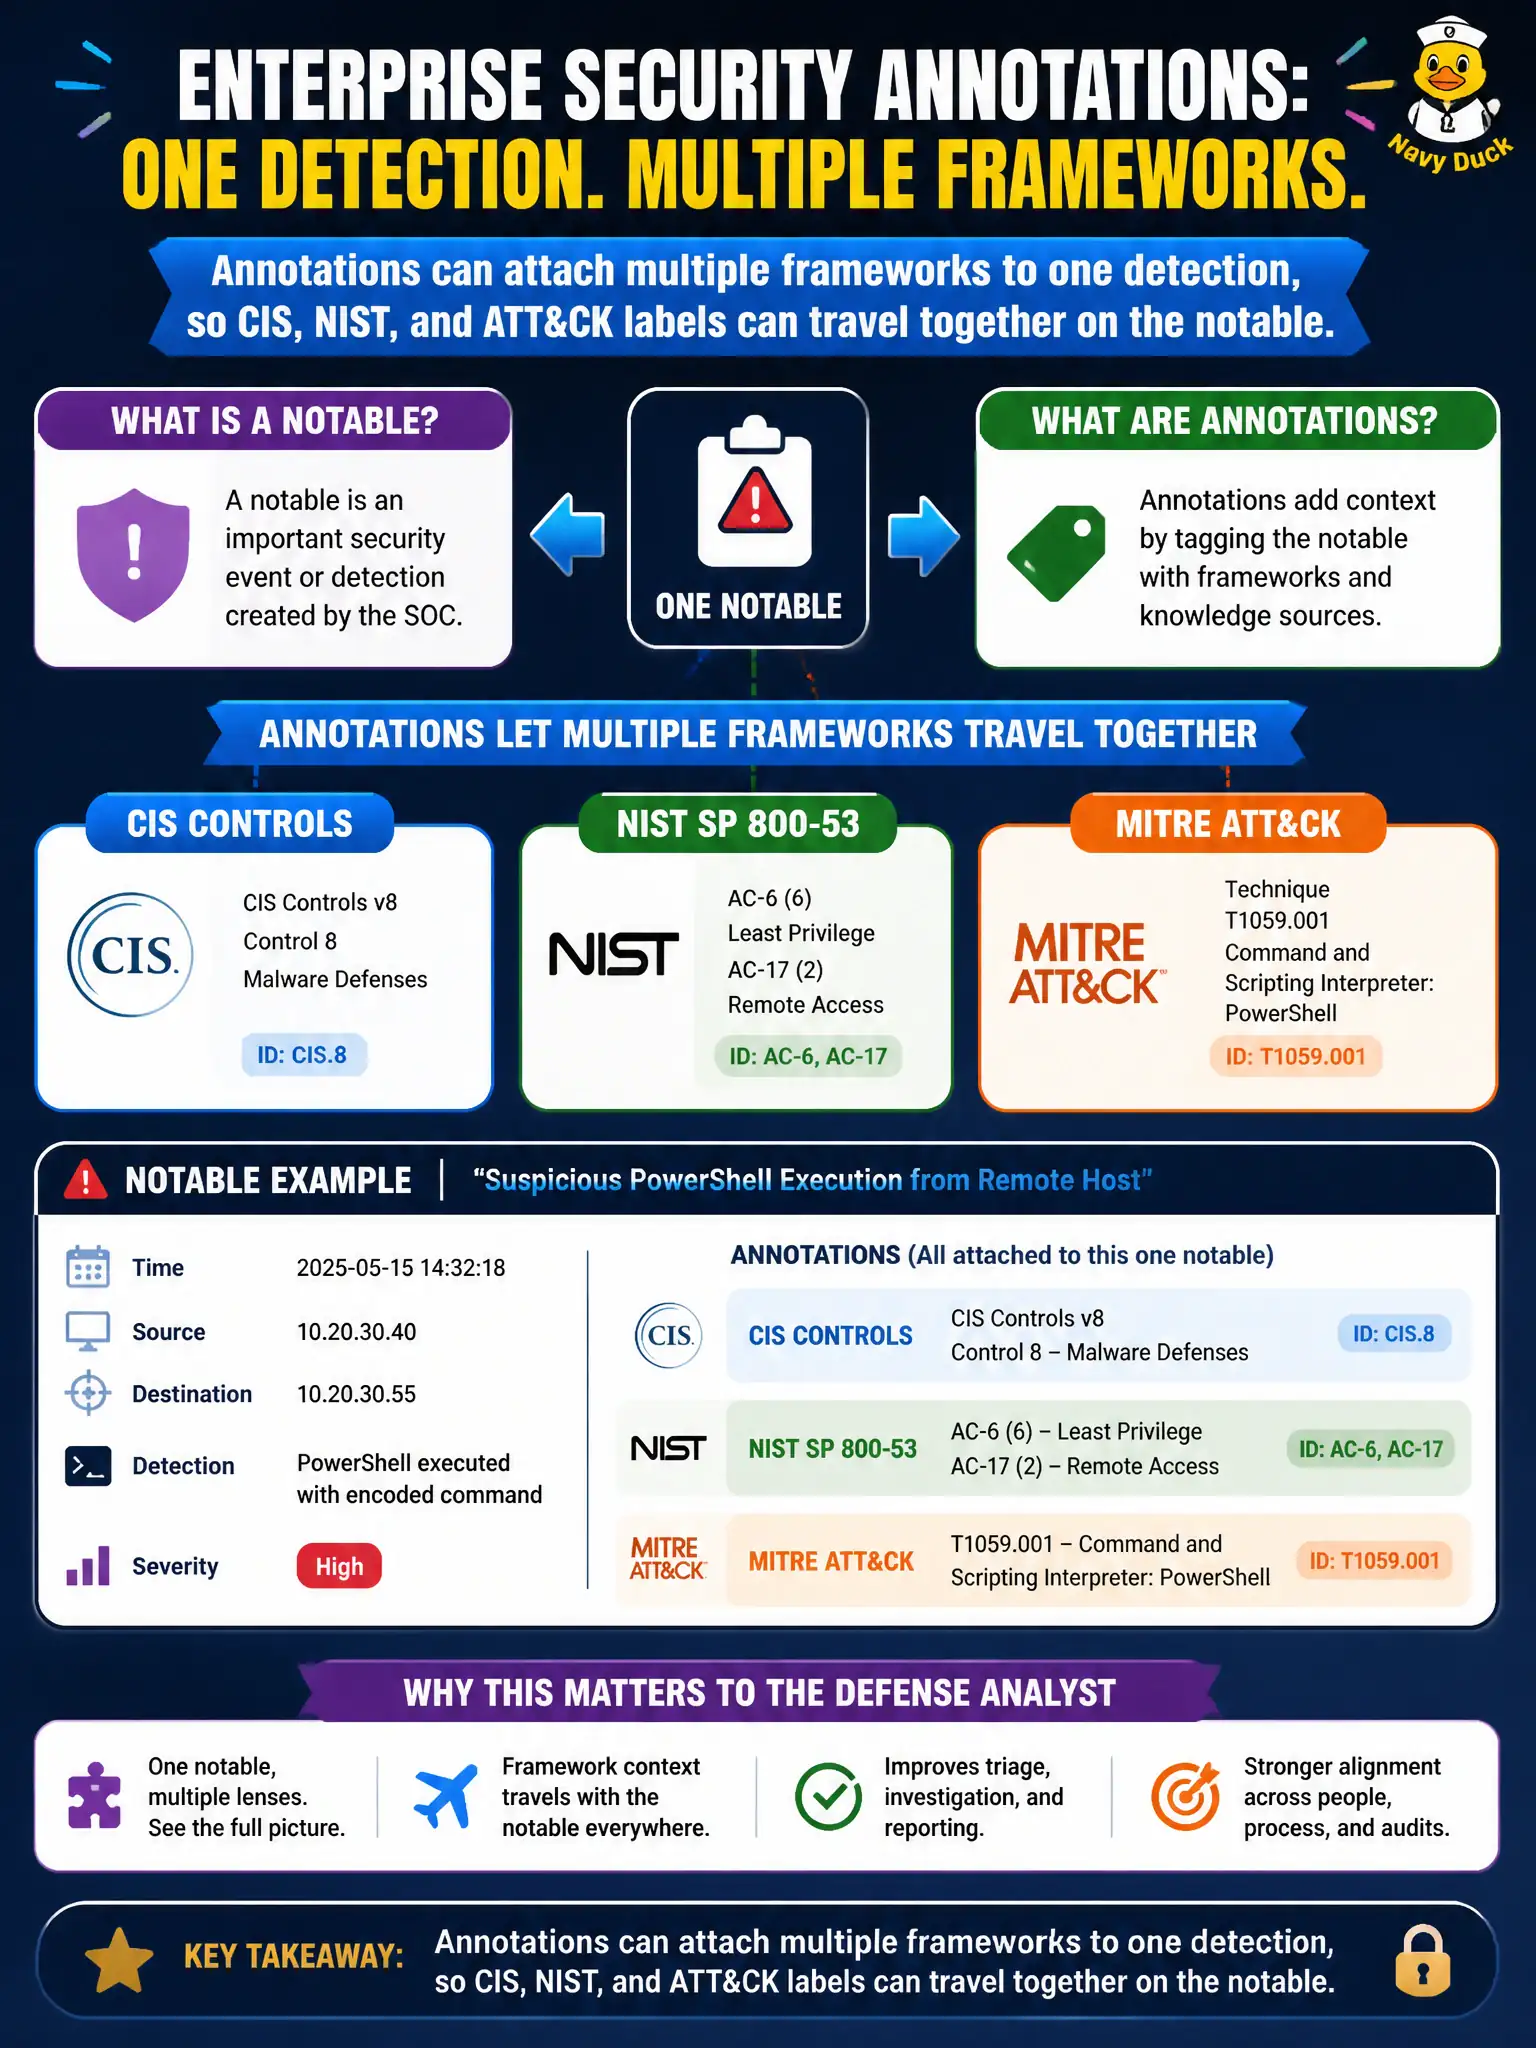
Think of an annotation like a shipping label that can list more than one code—ATT&CK, CIS, and NIST can all ride on the same court notable. It is not an ATT&CK-only sticker, and it is not a SOAR playbook or an indexer diagram.
Full Explanation
Enterprise Security annotations are framework metadata attached to correlation searches, risk rules, and the notables those searches create. For a court SOC that already surfaces MITRE ATT&CK on Incident Review, the correct understanding is that the same detection can carry multiple frameworks at once—CIS Controls, NIST control families, and ATT&CK technique or tactic labels can travel together on one civic notable. That multi-framework stamp is how analysts, auditors, and counsel share a single story without maintaining three disconnected ticketing taxonomies. Content owners attach the mappings on the detection; triage staff then read them where the notable appears.
Treating annotations as ATT&CK-only fails by concept: scope is not limited to a single technique ID, and CIS or NIST labels are first-class companions rather than forbidden extras. Requiring a SOAR playbook to replace the annotation on Incident Review confuses orchestration with content metadata—playbooks may act on a notable, but they are not the mechanism that authors framework mappings onto the correlation search. Claiming NIST and CIS live only on the indexer cluster map fails by separating infrastructure topology from security content: cluster maps describe data paths, not control-framework labels on detections.
Exam caveat: SPLK-5001 items often bait candidates to equate "annotation" with a single ATT&CK sticker or with SOAR automation; remember annotations are multi-framework detection metadata consumed on the notable.
Operational check: open the court correlation search (or risk rule) content, confirm CIS, NIST, and ATT&CK annotations are populated together, create or refresh a test notable, and verify Incident Review shows all three framework labels without any SOAR playbook or indexer-map change.