
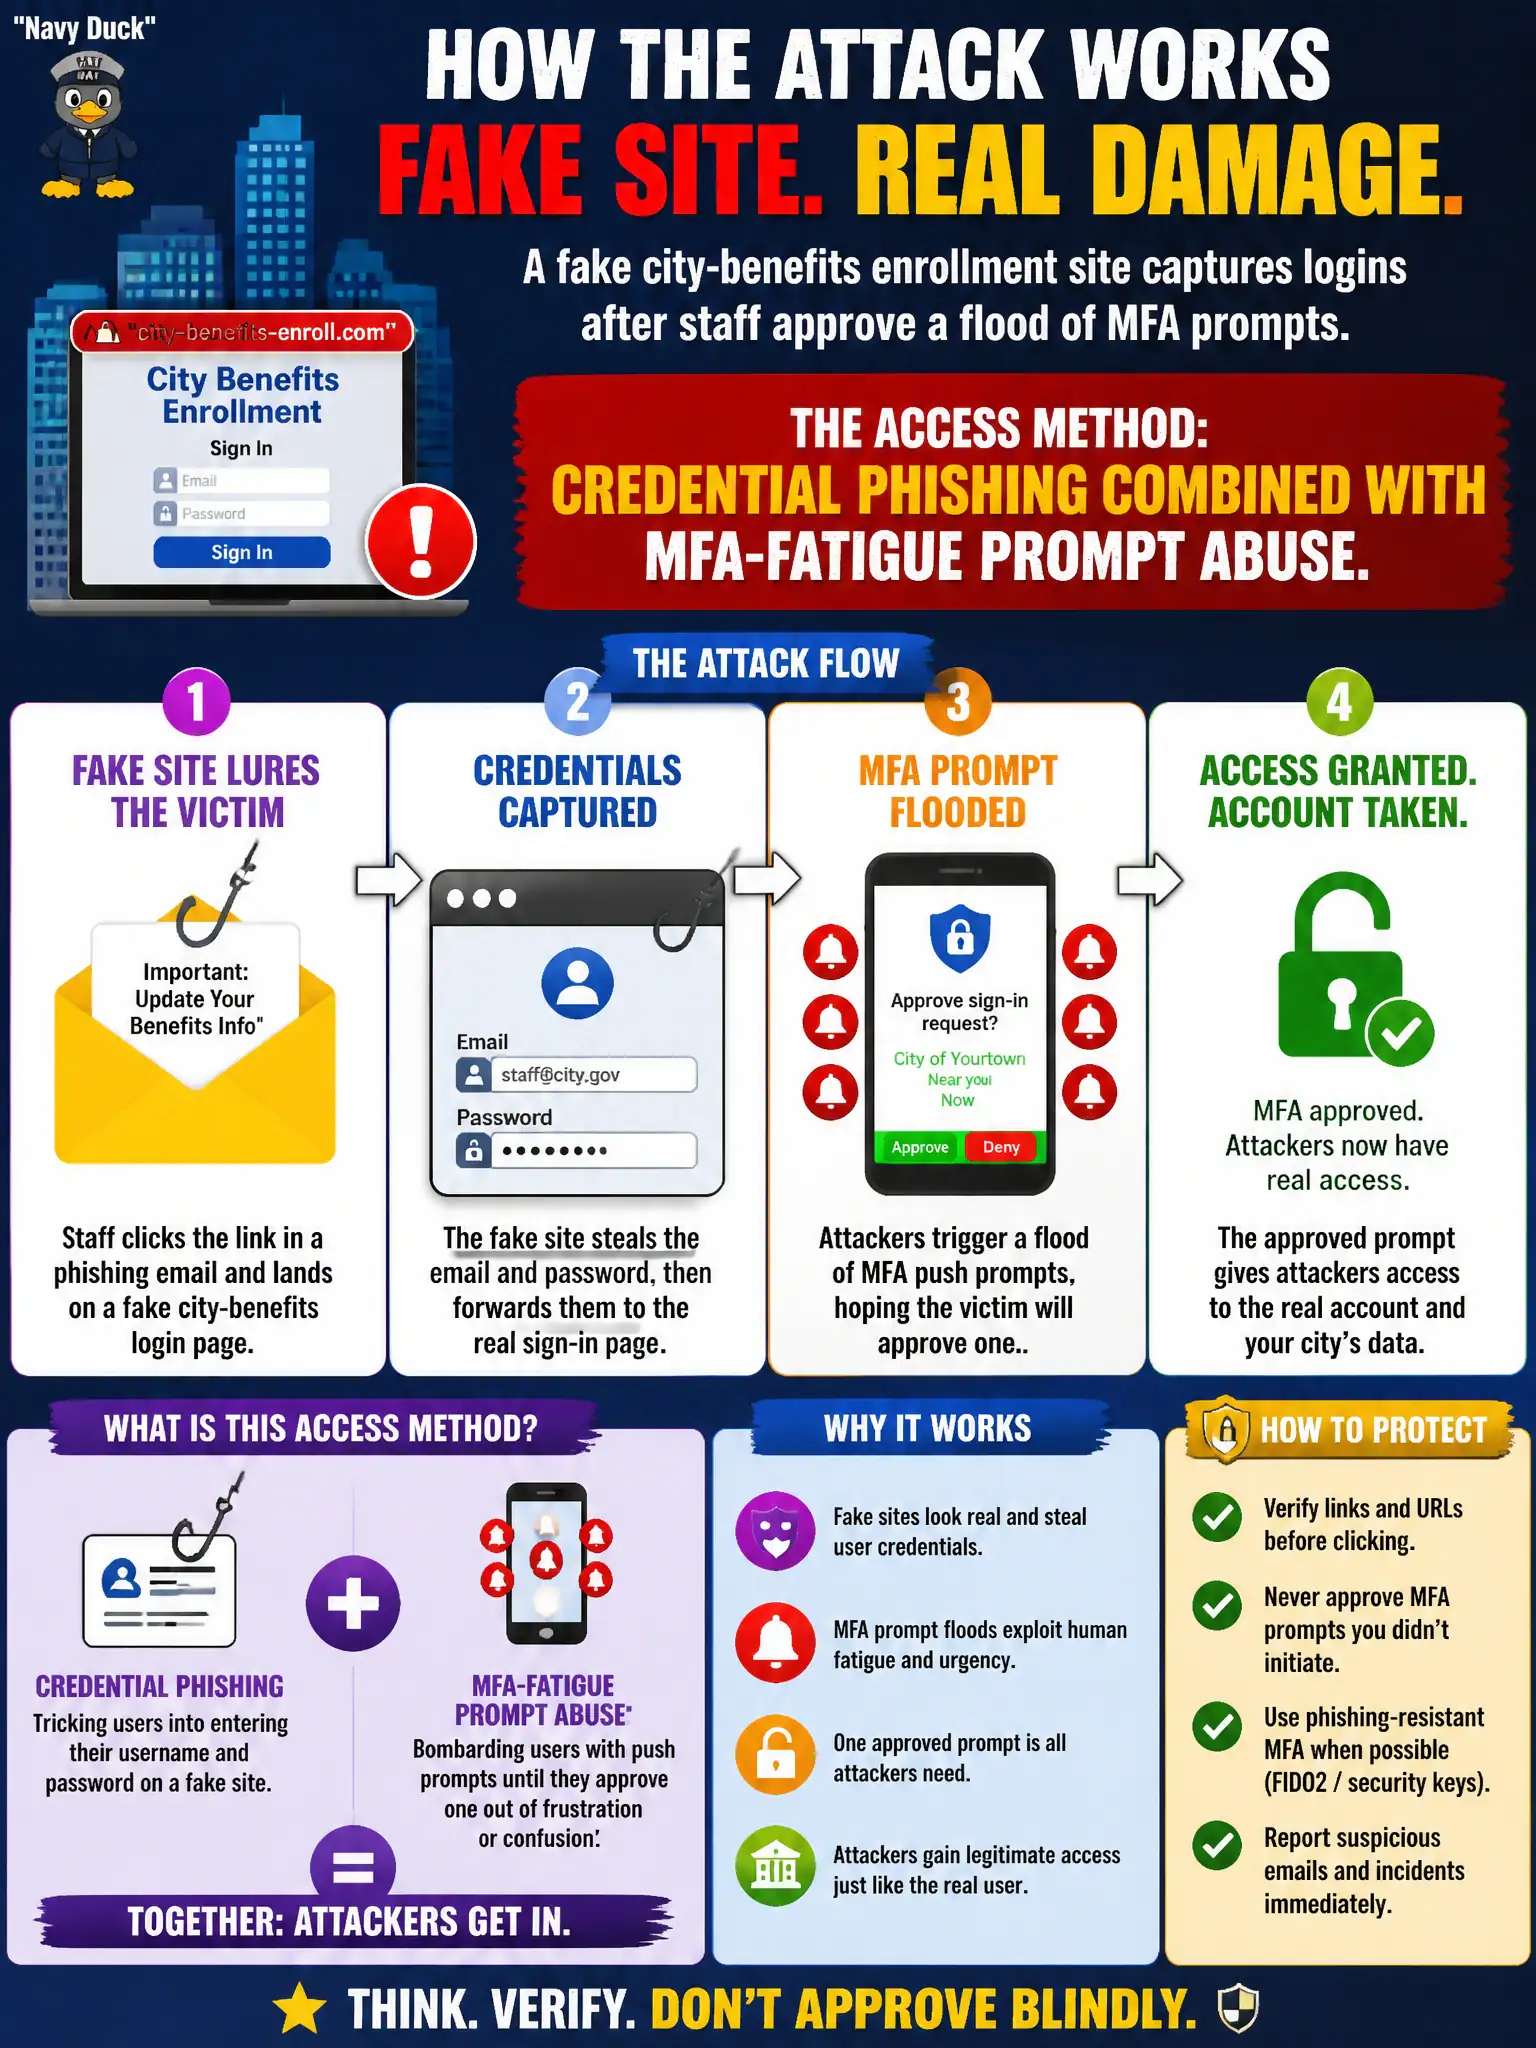
A fake city-benefits enrollment site captures logins after staff approve a flood of MFA prompts. What access method is this?
Select an answer to reveal the explanation.
Short Explanation
Staff got tired of tapping Allow and walked their real login into a fake benefits page. That is credential phishing plus MFA fatigue—social pressure on the prompt, not a kernel bug. The phone buzzed them into handing over the session.
Full Explanation
A fake city-benefits enrollment site that captures logins after staff approve a flood of MFA prompts is credential phishing combined with MFA-fatigue prompt abuse. Staff grew tired of tapping Allow on repeated prompts and walked real credentials into a lookalike benefits page. Civic identity attacks increasingly pair convincing lure sites with prompt spam; the access method is social pressure on MFA plus phishing, not a kernel exploit, SQL injection, or vendor worm class.
Calling it a kernel exploit on the benefits workstation fails by concept: no local privilege-escalation exploit is described—the path is fake site plus prompt fatigue. Calling it SQL injection against the benefits API fails by concept: the capture path is a fraudulent enrollment site and MFA prompt abuse, not hostile API input. Calling it wormable malware from a vendor laptop fails by concept: no vendor endpoint introducing wormable malware is present in the stem.
Exam caveat: Fake site plus MFA prompt flooding equals credential phishing with MFA fatigue—not endpoint exploit classes.
Operational check: Reset affected identities, review MFA method enrollment for attacker-added factors, hunt similar fatigue patterns in identity logs within Enterprise Security, and coach staff to report unexpected MFA storms instead of approving them.