
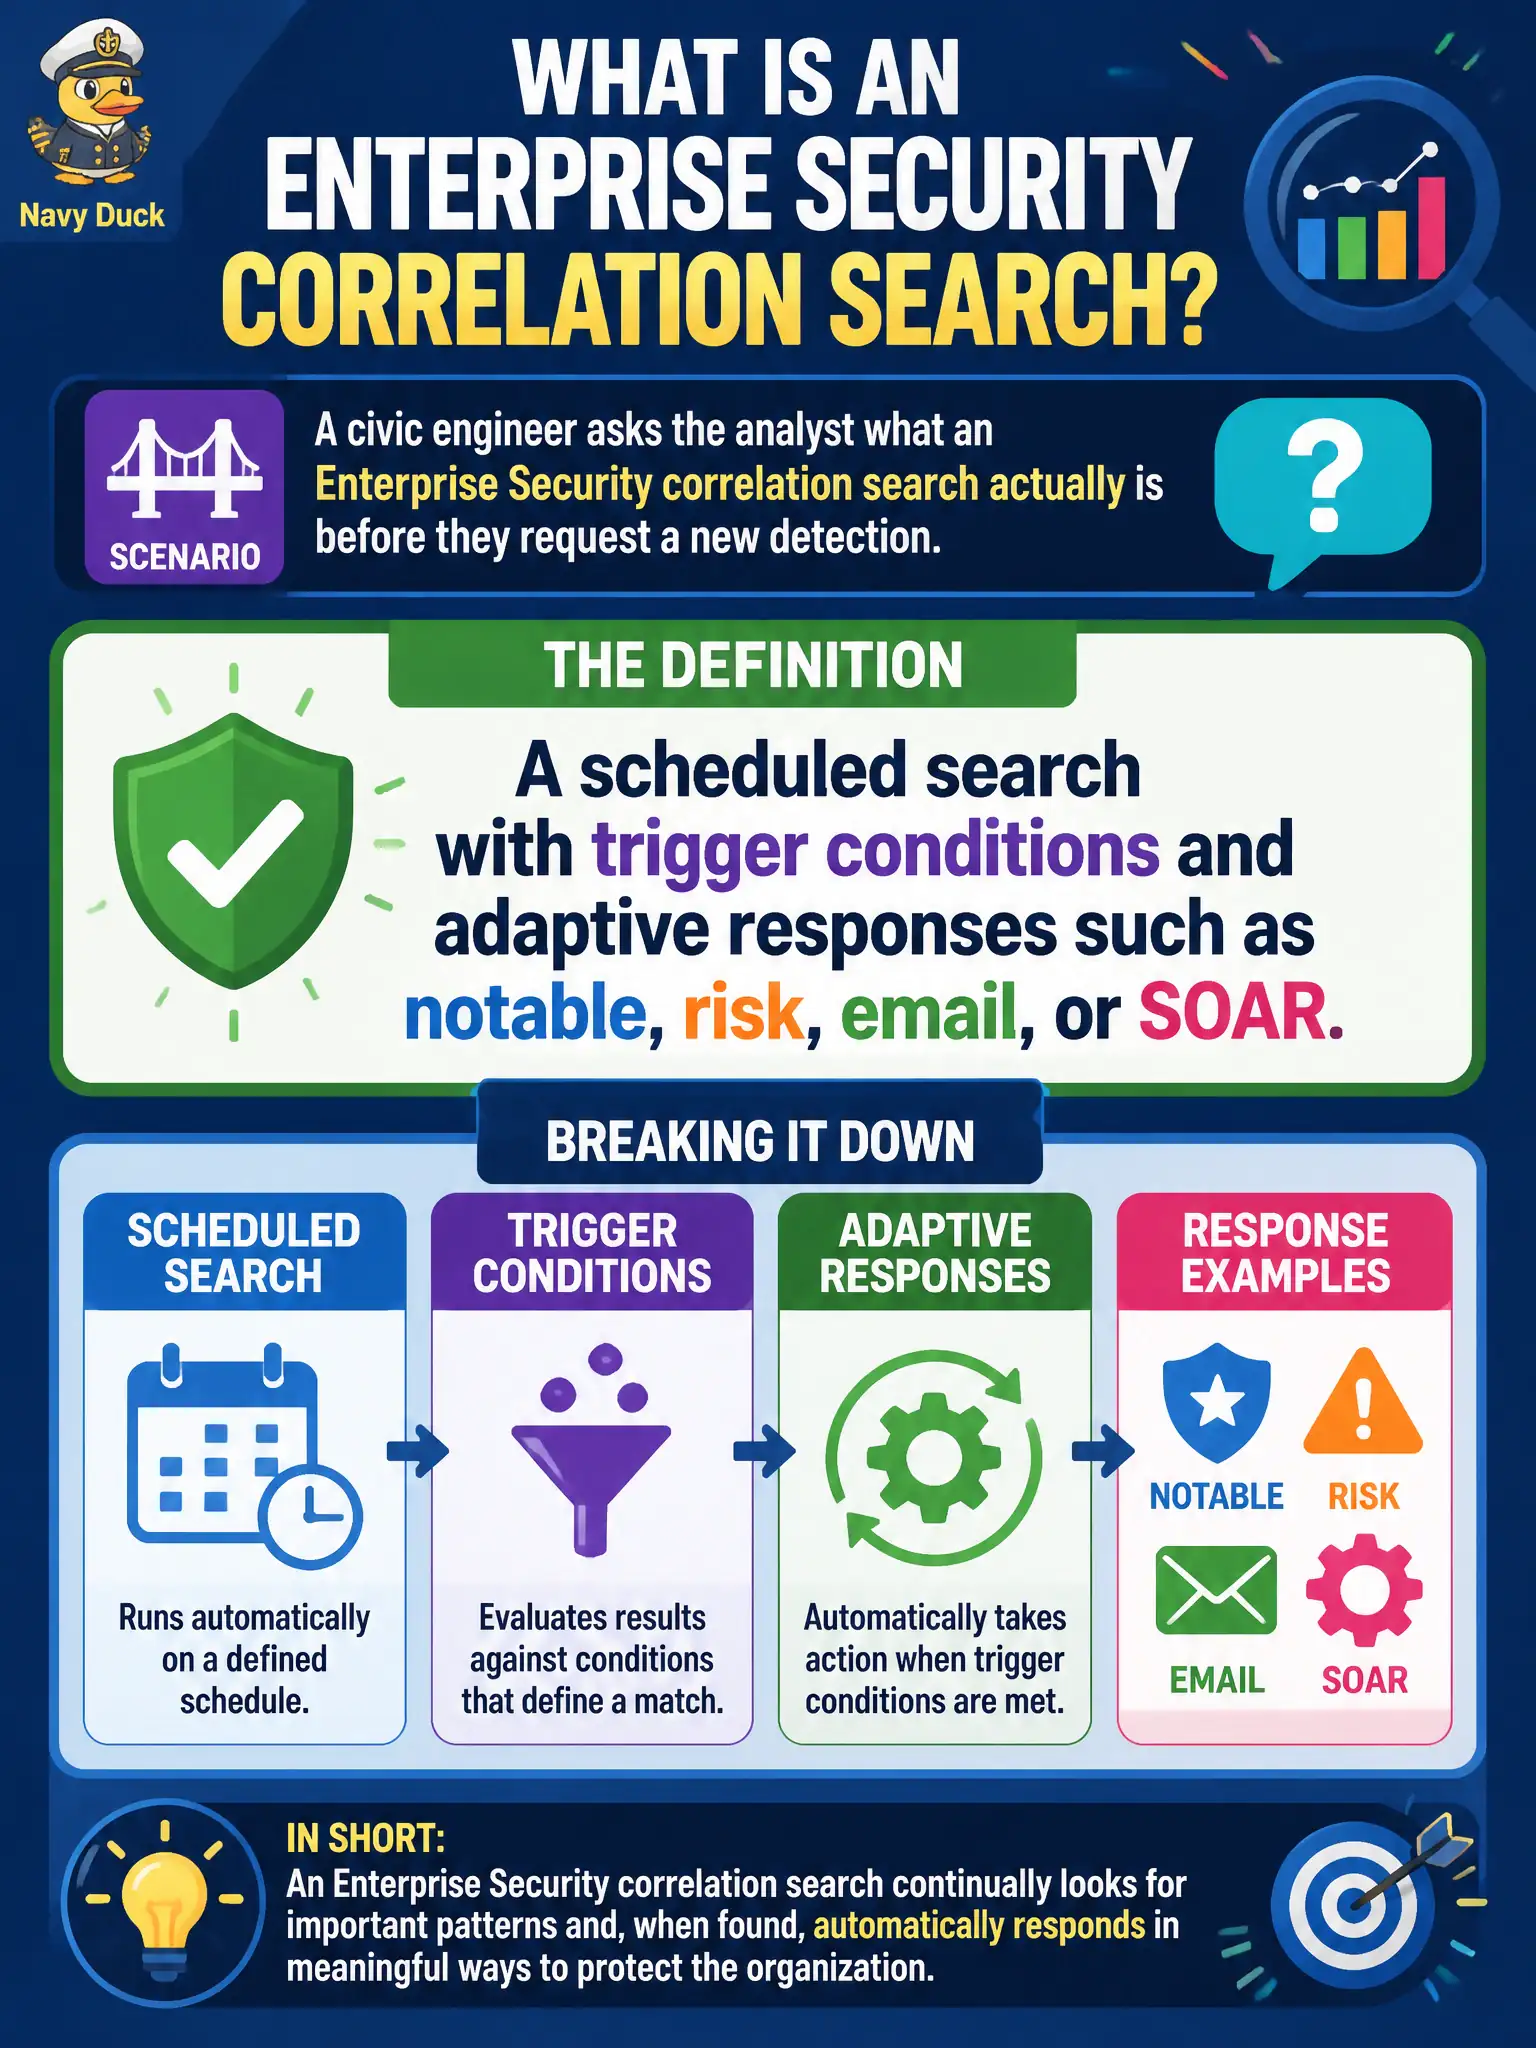
A civic engineer asks the analyst what an Enterprise Security correlation search actually is before they request a new detection. Which definition should the analyst use?
Select an answer to reveal the explanation.
Short Explanation
A correlation search is a scheduled detector with a trigger and an action, not a one-off search typed at lunch. Notable, risk, email, SOAR—those ARs fire when the trigger hits. Dashboards and Python classes are other products.
Full Explanation
An Enterprise Security correlation search is a scheduled search with trigger conditions and Adaptive Responses such as create notable, risk analysis, email, or send to SOAR. That definition is what a civic engineer needs before requesting new detection content so analysts and engineers share vocabulary. Calling any ad-hoc SPL the analyst types once in Search a correlation search fails by concept because ad-hoc investigation SPL is not scheduled detection content with triggers and Adaptive Responses. Calling the Security Posture dashboard's styling a correlation search fails by concept because Posture is an overview UI for notables by domain and urgency, not a scheduled detection. Calling a SOAR Python class the analyst must compile a correlation search fails by concept because SOAR playbooks are optional automation downstream; correlation searches live in ES content management as scheduled analytics. Exam caveat: SPLK-5001 defines correlation searches as scheduled detections with triggers and adaptive responses for municipal use cases. Operational check: when requesting a new search, specify SPL or CIM logic, schedule, trigger conditions, and which Adaptive Responses (risk versus notable, email, SOAR) should fire—using that shared definition with engineering.