
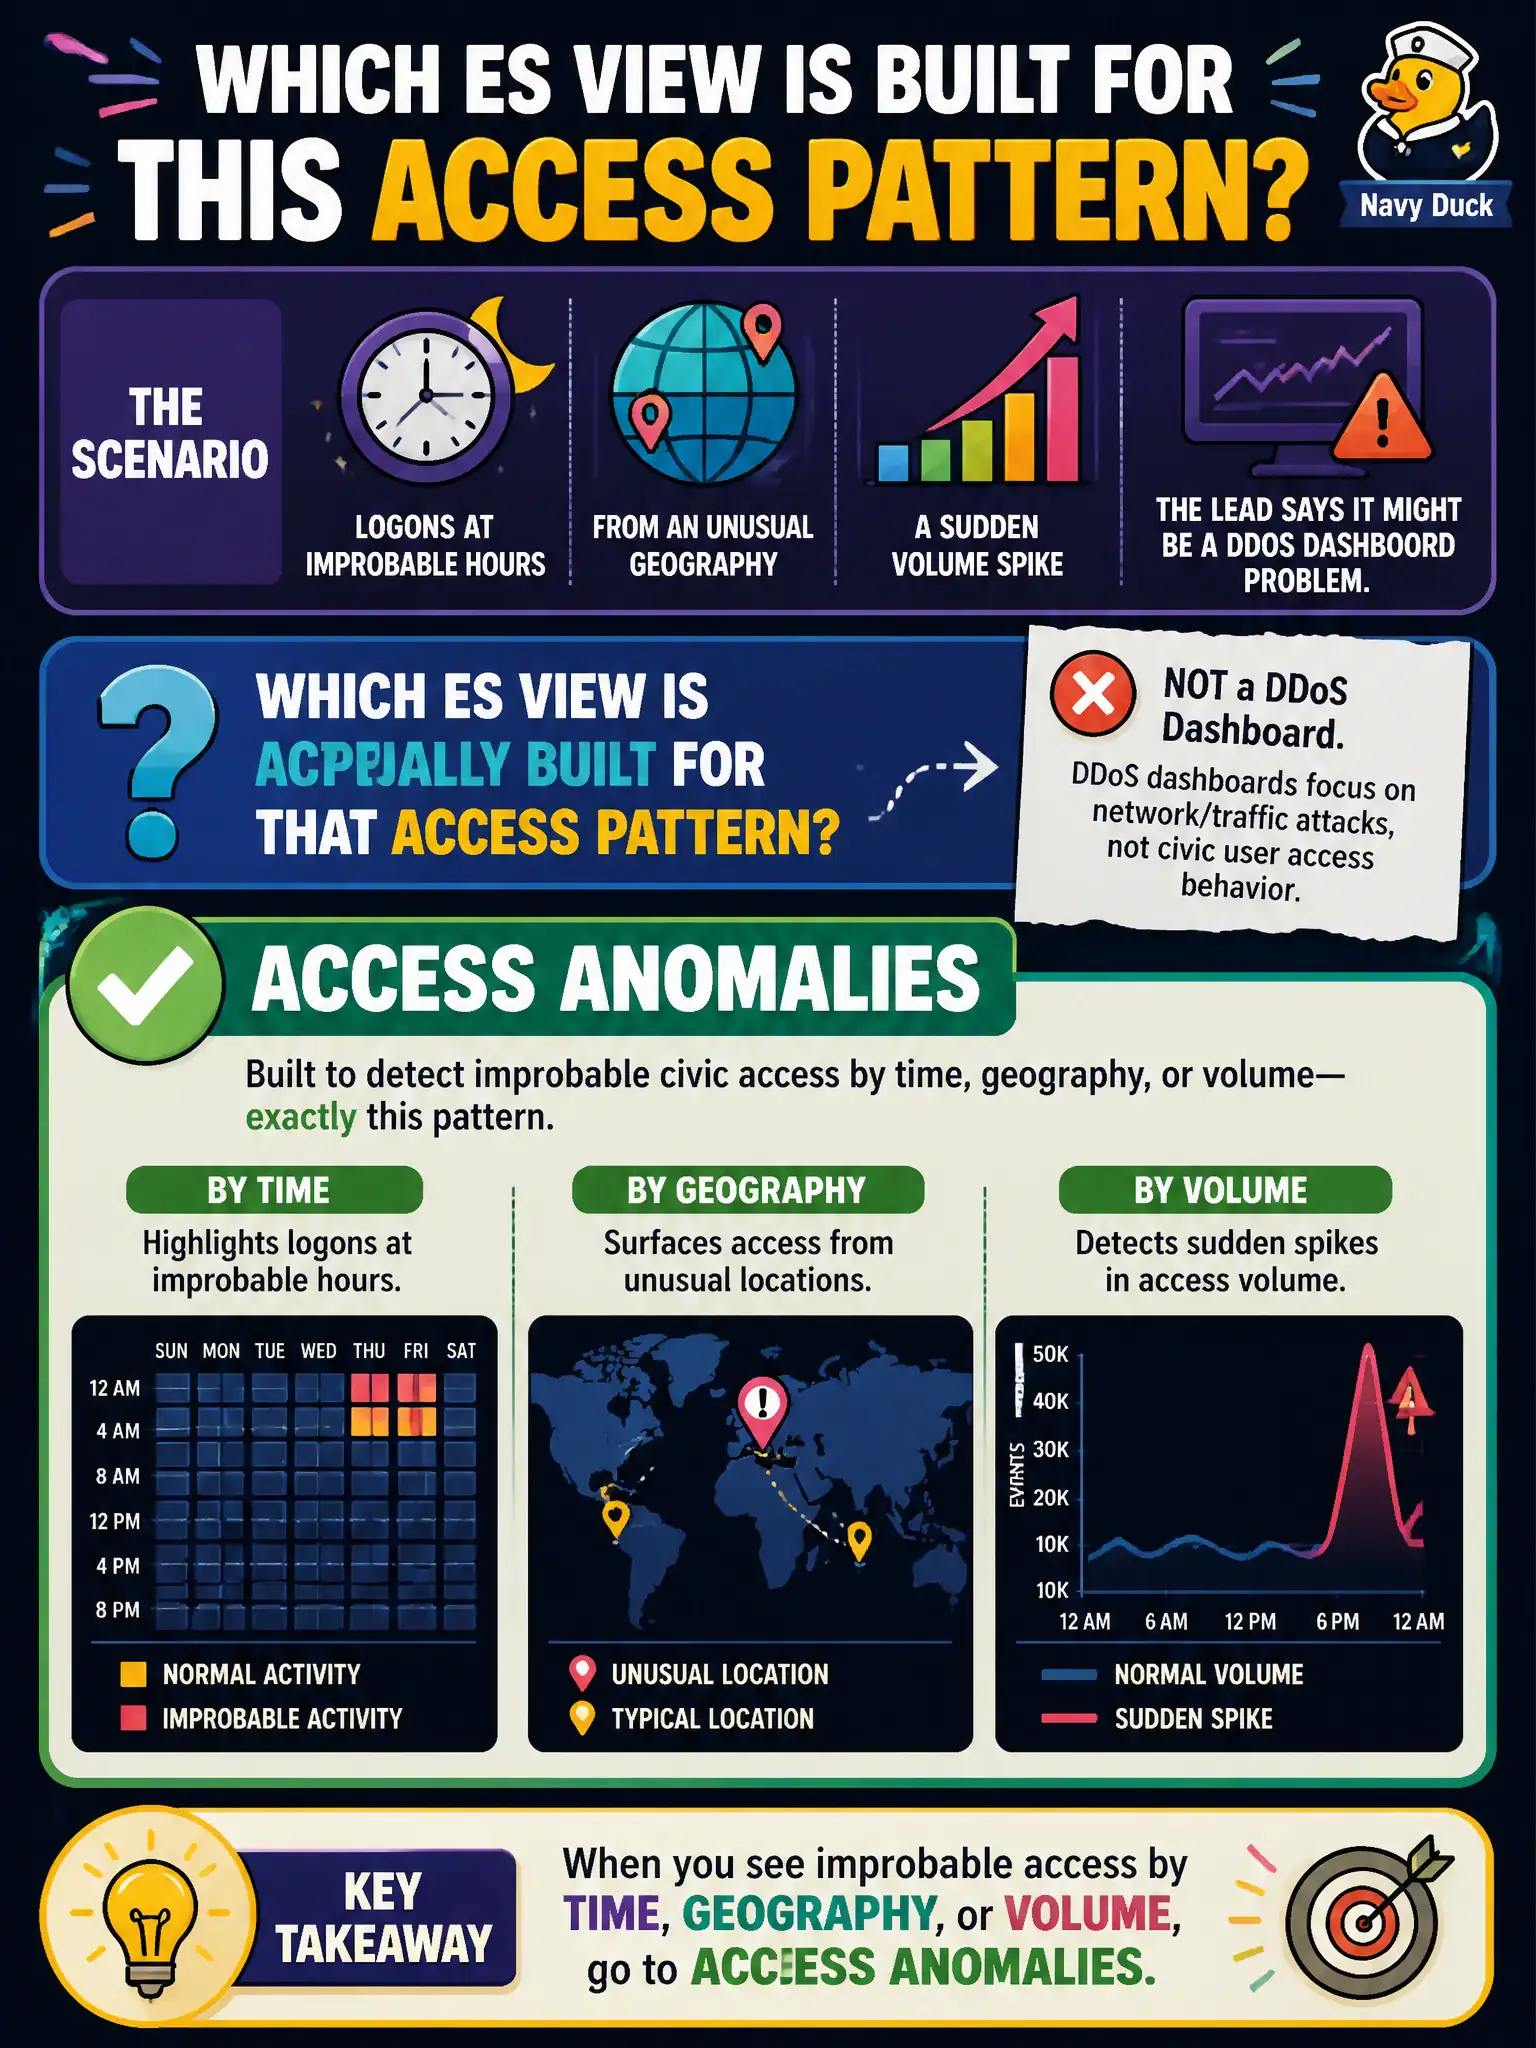
A housing-authority account shows logons at improbable hours from an unusual geography and a sudden volume spike. The lead says it might be a DDoS dashboard problem. Which ES view is actually built for that access pattern?
Select an answer to reveal the explanation.
Short Explanation
A 3 a.m. logon from another country is an access-anomaly problem, not a DDoS weather map. Access Anomalies is built for weird time, place, and volume on accounts. Don't send that to packet decode or the audit log.
Full Explanation
Access Anomalies highlights improbable civic access by time, geography, or volume—exactly the housing-authority pattern of odd-hour logons, unusual geography, and a sudden spike. It is not a DDoS dashboard, and framing the case as a DDoS tile problem misroutes the investigation away from identity analytics. Protocol Intelligence as the DDoS tile for account logons fails by concept because Protocol Intelligence is protocol and Stream oriented and is not the access-anomaly identity view for logon impossibility patterns. Security Posture packet decode fails by concept because Posture summarizes notables by domain and urgency and is not a packet decoder for account anomalies. Incident Review Audit of analyst comments fails by concept because Audit shows how analysts handled notables over time, not live improbable-access analytics on housing-authority accounts. Exam caveat: SPLK-5001 maps improbable time, geography, and volume access patterns to Access Anomalies rather than DDoS or protocol views. Operational check: open Access Anomalies for the housing-authority account, validate the time/geo/volume signals against Authentication data, and create or triage a notable if the pattern is unauthorized.