
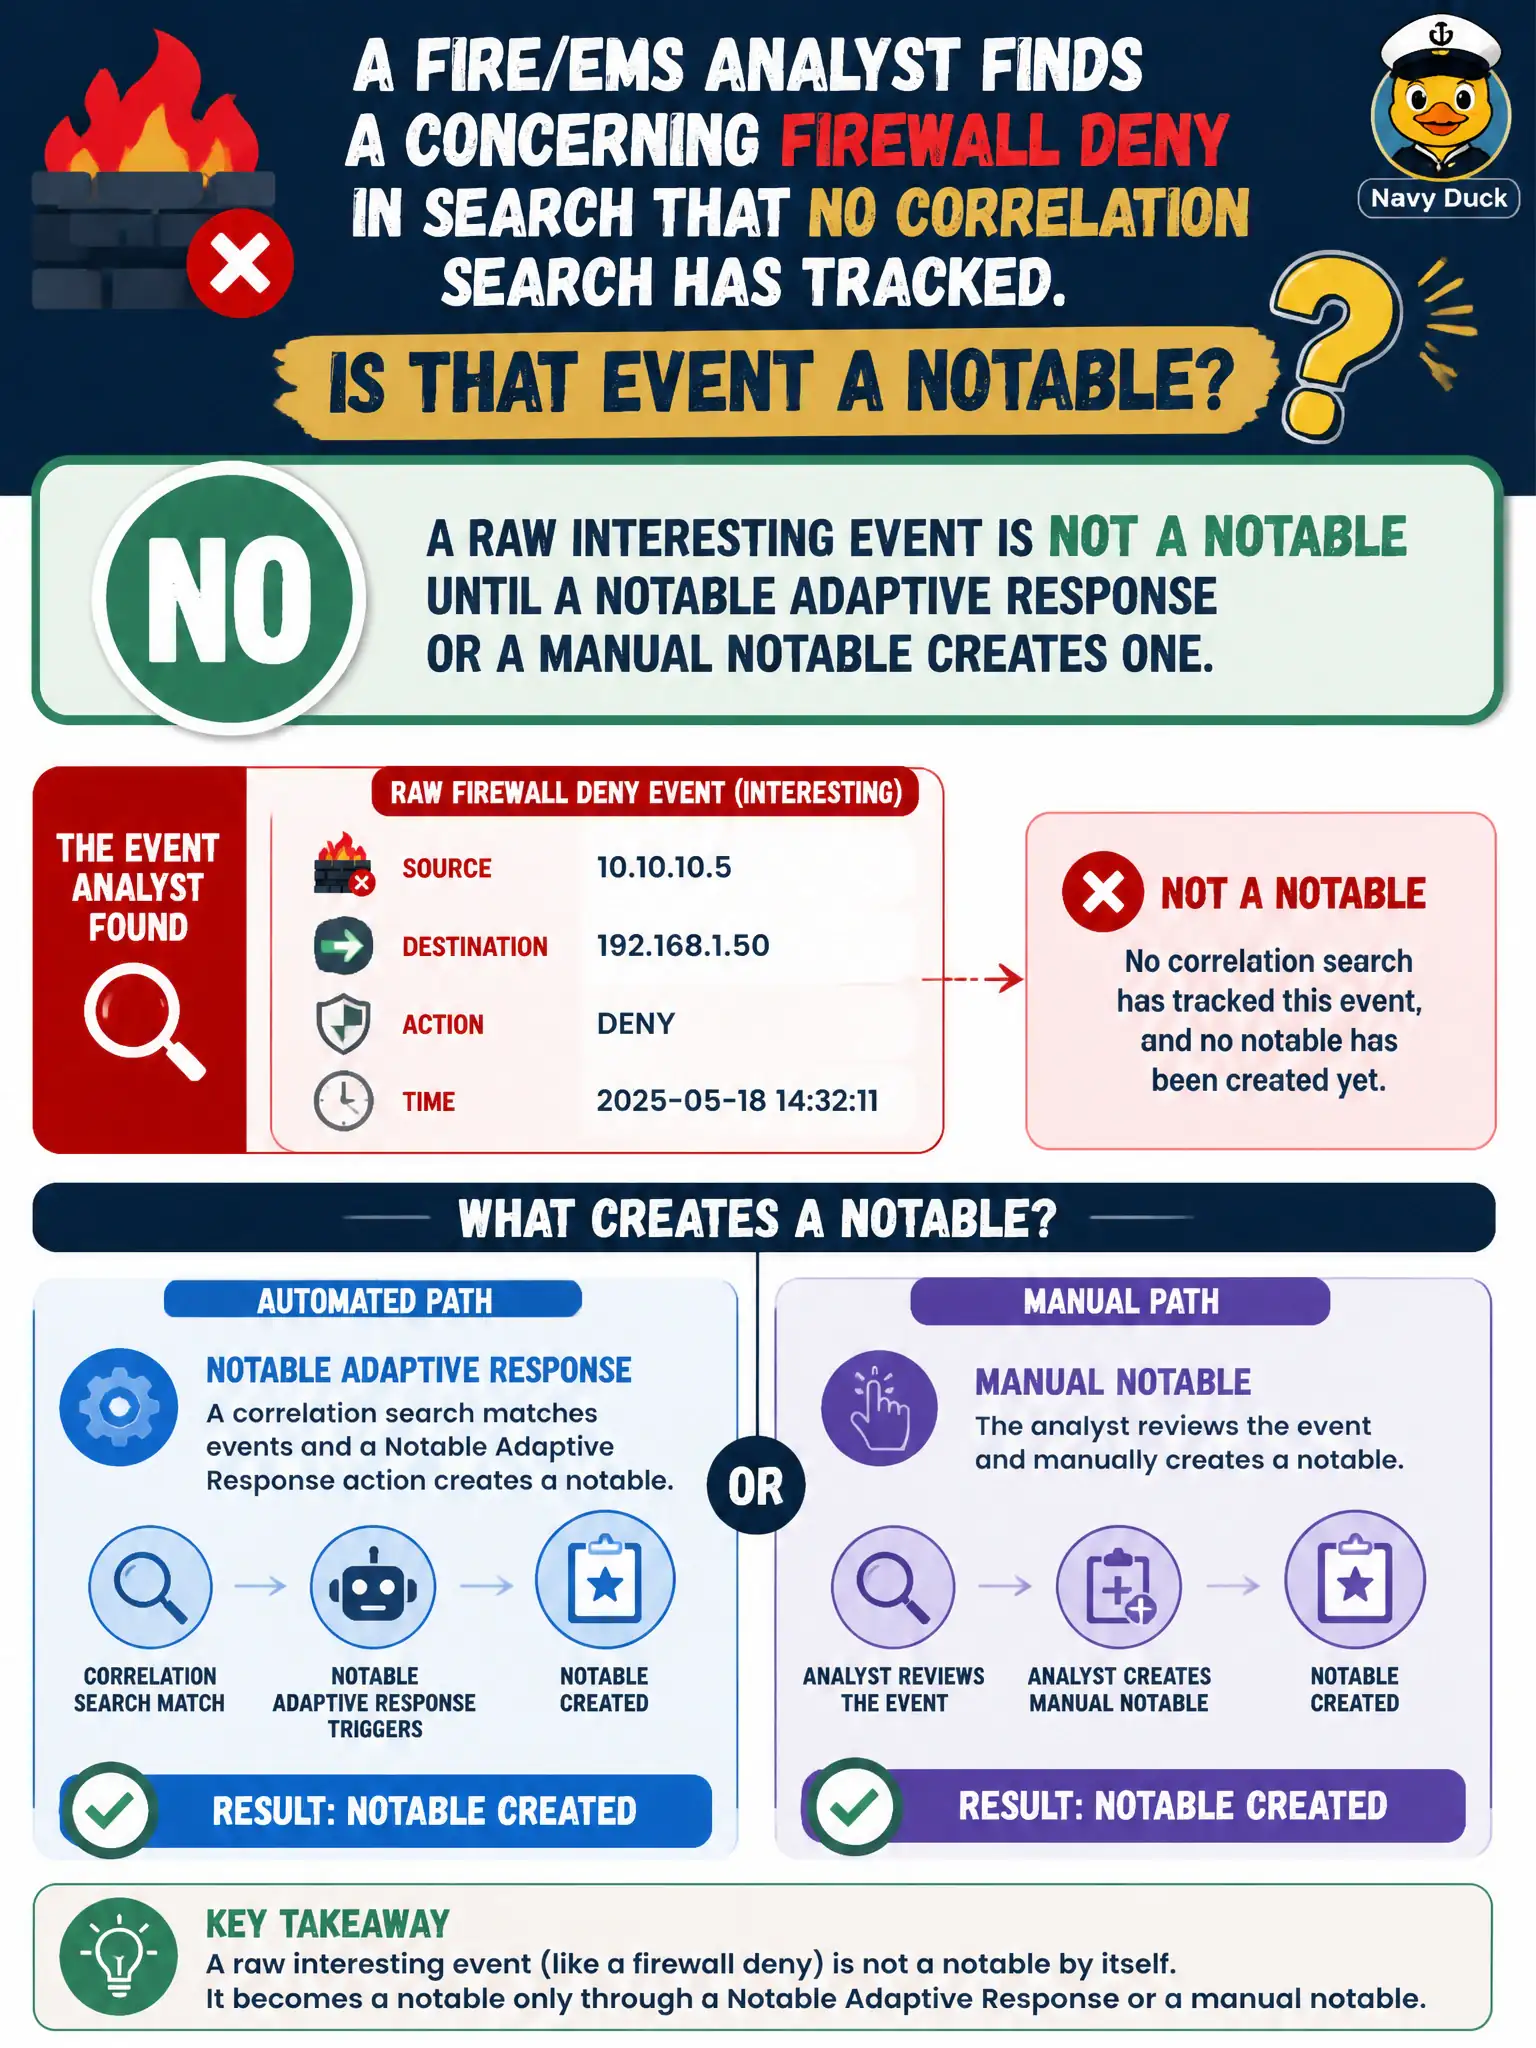
A fire/EMS analyst finds a concerning firewall deny in Search that no correlation search has tracked. Is that event a notable?
Select an answer to reveal the explanation.
Short Explanation
A scary line in the log is evidence, not a case. Nothing is a notable until ES (or the analyst) actually creates one. Color in Search and CIM fields do not magically open a queue item.
Full Explanation
A concerning firewall deny found only in Search during a fire/EMS investigation is an interesting raw event, not a notable, until a notable Adaptive Response or a manual notable/finding creates a tracked object on Incident Review / Analyst Queue. Color highlighting in Search and CIM normalization do not auto-promote events to notables. Claiming every red syslog line is automatically a notable fails by concept because Search highlighting is a visual cue for analysts, not the notable framework. Claiming any CIM-normalized event is a notable fails by concept because CIM mapping enables analytics, tstats, and domain dashboards; it does not create queue incidents by itself. Claiming a privileged dest_port makes an event a notable fails by concept because port privilege may raise suspicion but does not instantiate a tracked case. Exam caveat: SPLK-5001 distinguishes interesting events from notables; analysts may manually create notables when correlation searches missed fire/EMS evidence. Operational check: if the firewall deny must be tracked, create an ad-hoc notable or enable/fix a correlation search with notable AR, assign owner and status on Analyst Queue, and treat the Search hit as evidence under that case.