
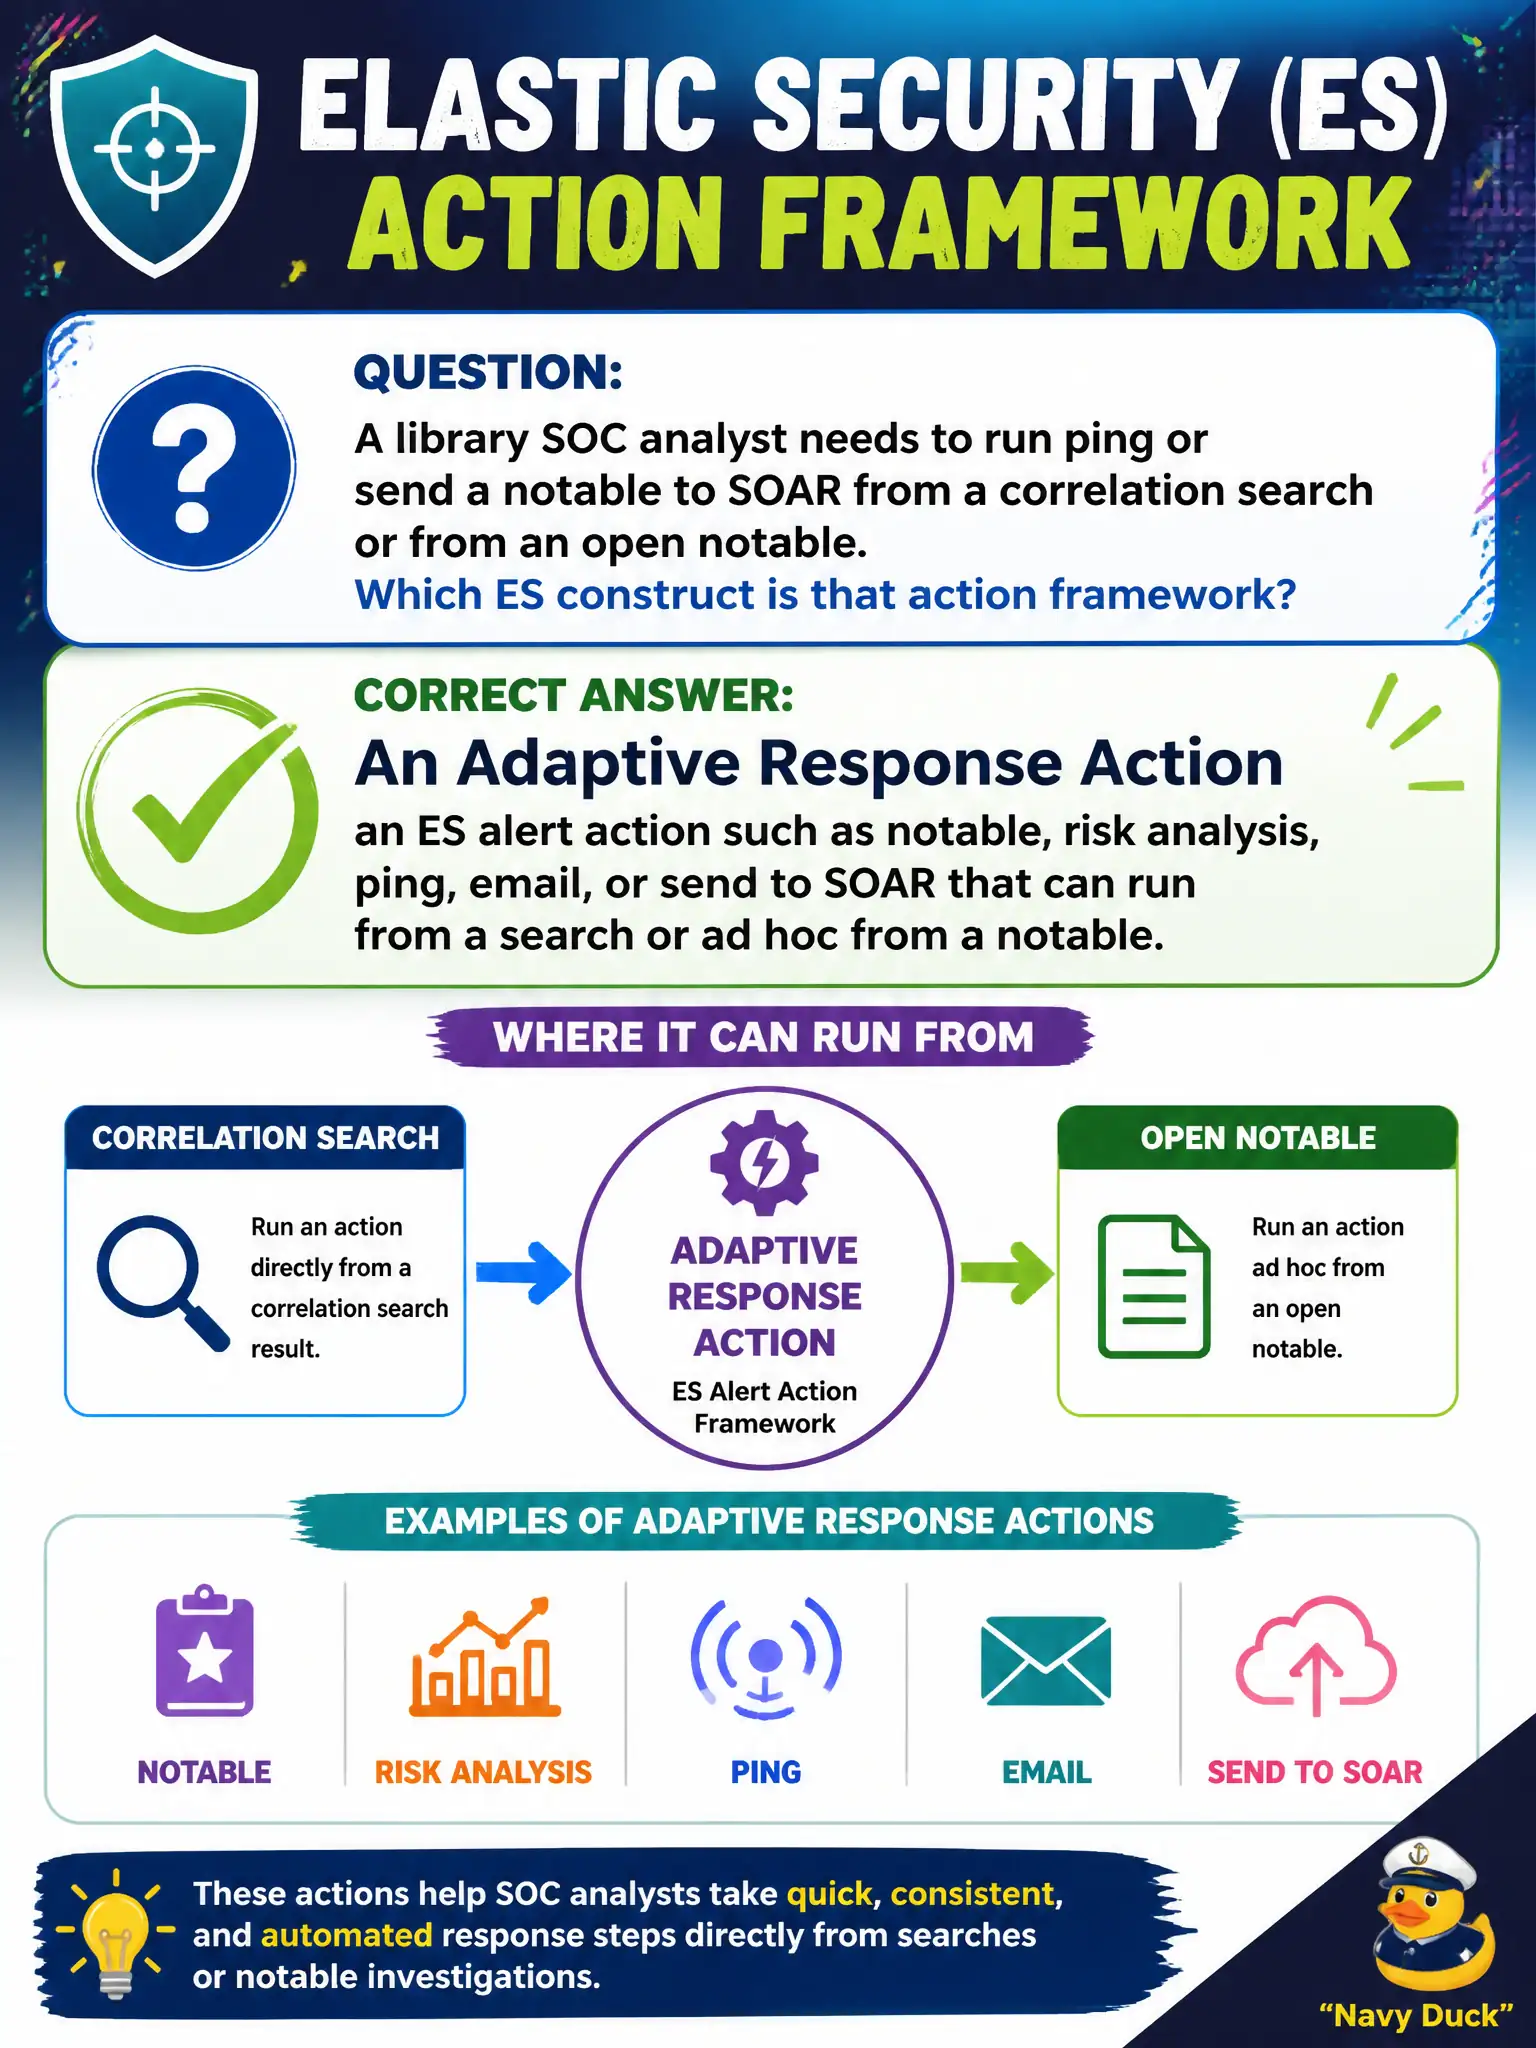
A library SOC analyst needs to run ping or send a notable to SOAR from a correlation search or from an open notable. Which ES construct is that action framework?
Select an answer to reveal the explanation.
Short Explanation
Adaptive Response is the action button on the alert, not a Windows service hiding on the clerk PC. From a search or from the notable, ES can create a notable, write risk, ping, email, or hand off to SOAR. You do not have to write the Python playbook on this exam.
Full Explanation
An Adaptive Response Action is an Enterprise Security alert action—create notable, risk analysis, ping, email, send to SOAR, and similar—that can run from a correlation search schedule or ad hoc from an open notable. That is the framework a library SOC analyst uses to ping a host or escalate without leaving ES or inventing a custom service. Calling Adaptive Response a Windows service installed on every clerk workstation fails by concept because AR executes as ES alert actions on the search head side of the workflow, not as an endpoint service rollout to library PCs. Calling it the Protocol Intelligence dashboard fails by concept because Protocol Intelligence is a network-protocol visualization dependent on Stream-like data, not the action framework that creates notables or enriches cases. Calling it a SOAR Python playbook the analyst must author before any response fails by concept because built-in AR actions can run without the analyst writing playbooks; SOAR integration is an optional escalation path. Exam caveat: SPLK-5001 treats Adaptive Response as ES alert actions usable from searches and notables in civic SOCs. Operational check: from a library notable or correlation search, review configured Adaptive Responses, run an approved enrichment action such as ping if needed, and confirm notable or risk AR remains the tracking path for the case.