
The housing authority has an on-prem domain controller plus Entra ID for cloud apps. A privileged-logon hunt used only Entra content. What did the hunt miss?
Select an answer to reveal the explanation.
Short Explanation
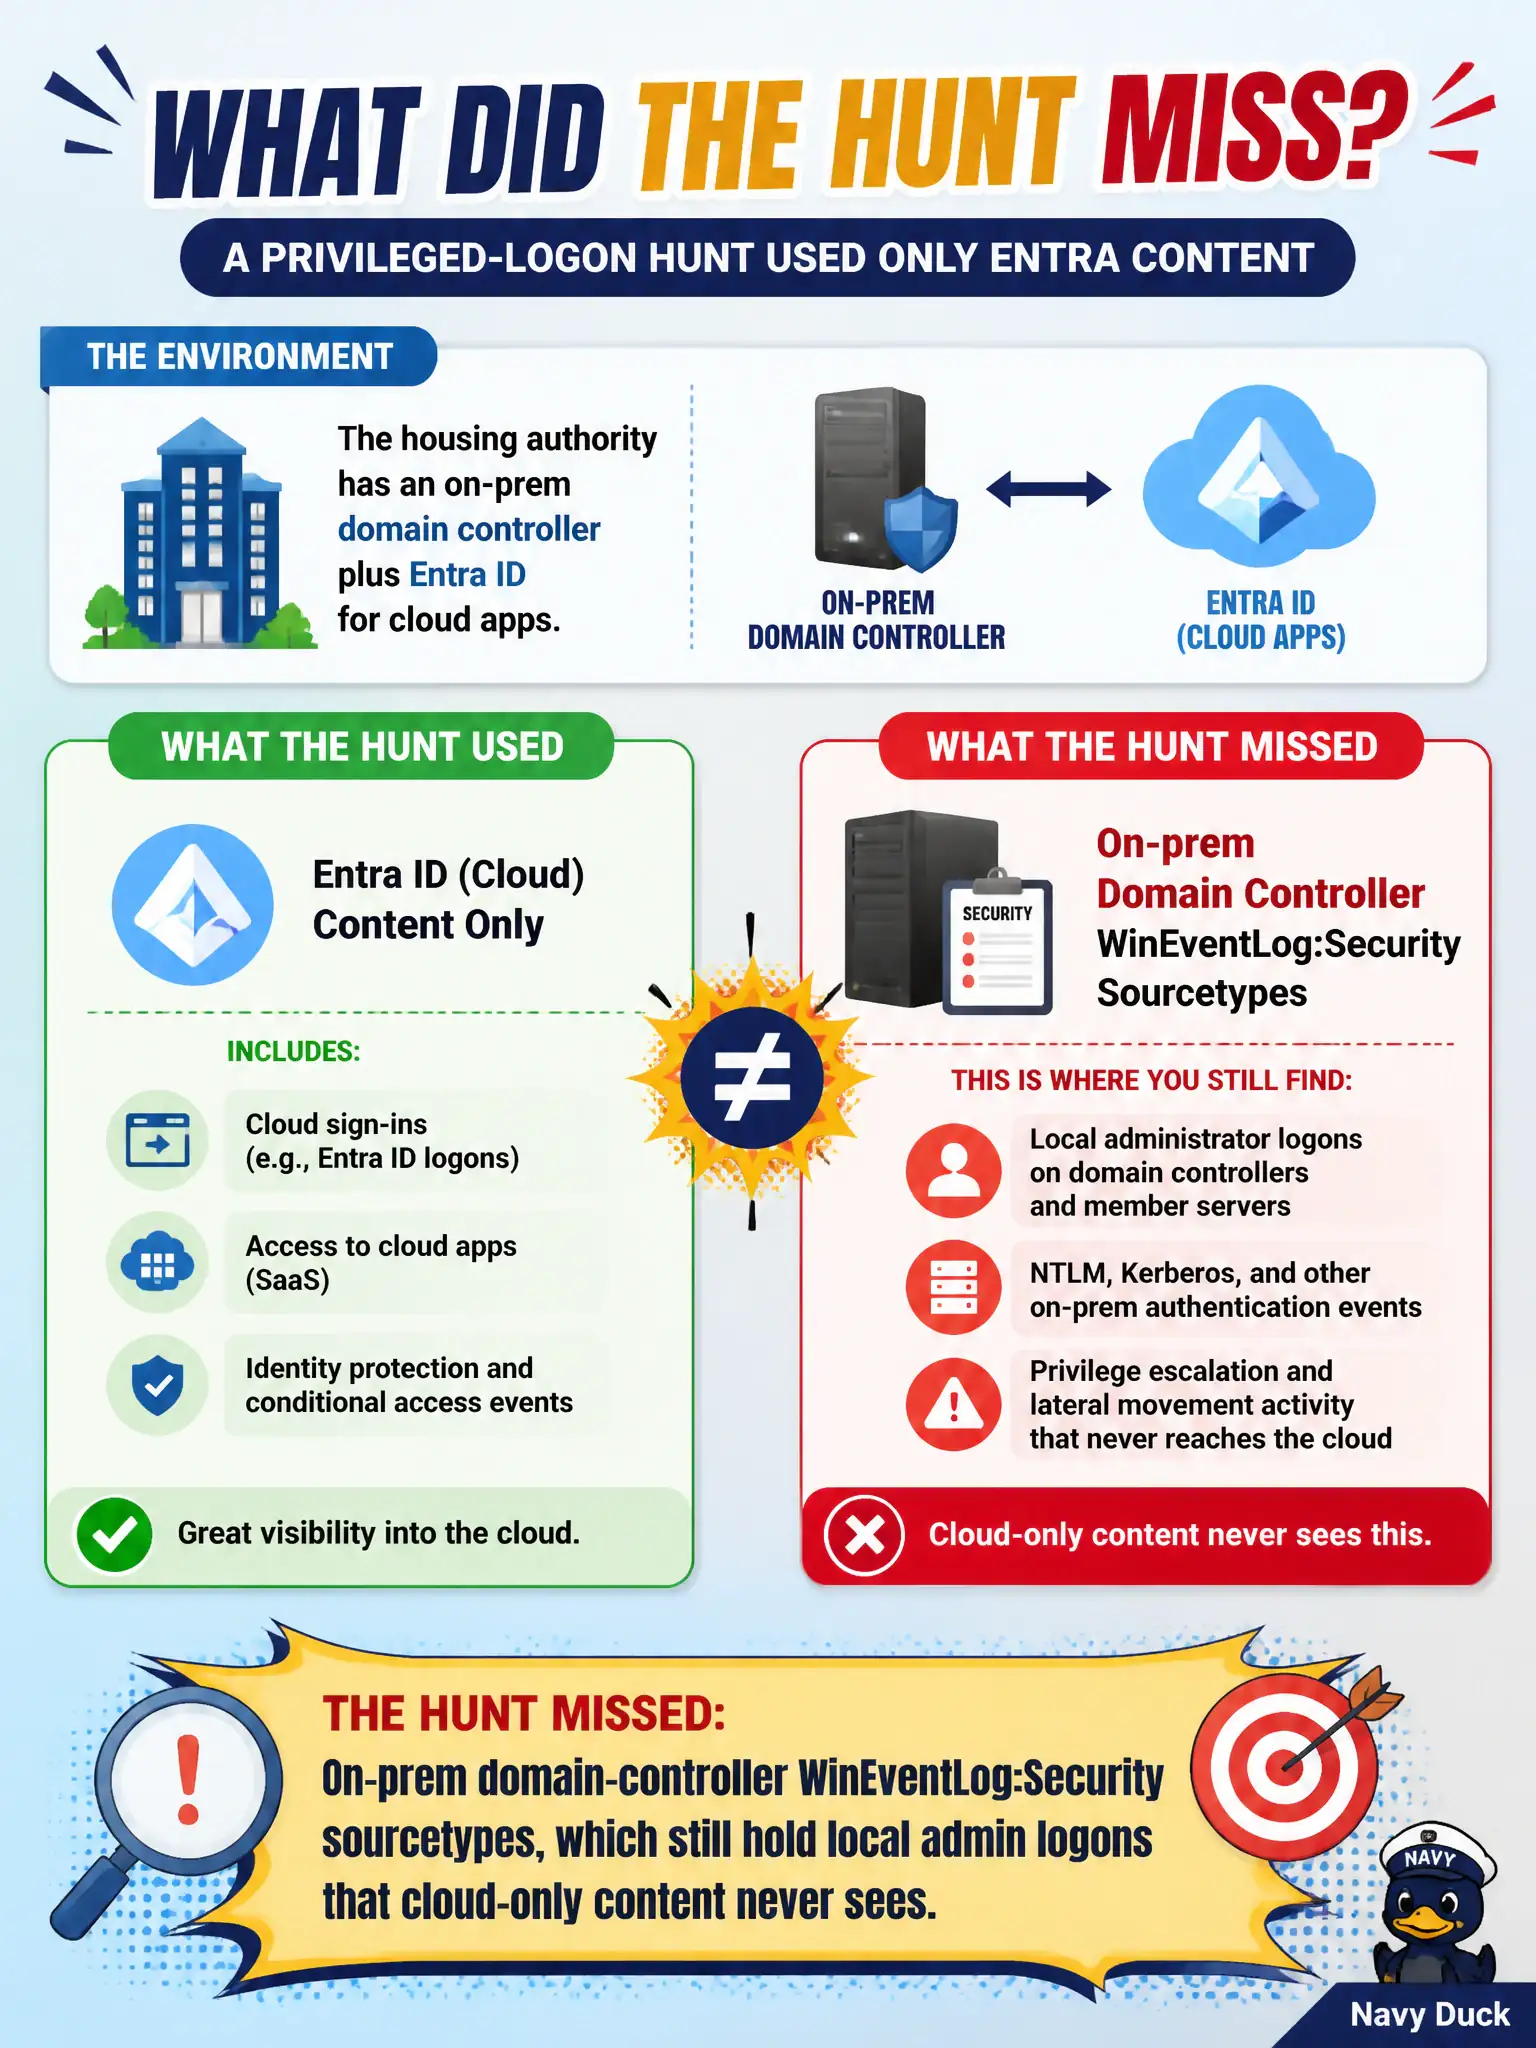
Hybrid identity is two cameras, not one. Entra sees the cloud apps; the domain controller still sees the on-prem admin logon. Hunt both sourcetypes or the local path stays invisible.
Full Explanation
The housing authority has an on-premises domain controller plus Entra ID for cloud apps. A privileged-logon hunt that used only Entra content missed on-premises domain-controller WinEventLog:Security sourcetypes, which still hold local admin logons that cloud-only content never sees. Hybrid identity means both planes matter for civic housing systems: Entra covers cloud sign-ins; domain-controller security covers Kerberos, NTLM, and local privileged activity on servers.
Claiming Entra sign-in logs replicate every on-premises domain-controller event automatically is false for hybrid estates and leaves admin logons unmonitored. Claiming only VPC Flow Logs replace Windows security on hybrid identity confuses AWS network flow with directory authentication evidence. Claiming the _audit index on the deployment server is the system of record for civic admin logons misplaces authoritative authentication telemetry.
Exam caveat: hybrid identity hunts need both Entra and on-premises WinEventLog:Security coverage to avoid blind spots.
Operational check: extend the privileged-logon hunt to Authentication from housing-authority domain controllers and Entra sign-ins, compare privileged groups across both planes, and document residual blind spots if either source is missing.