
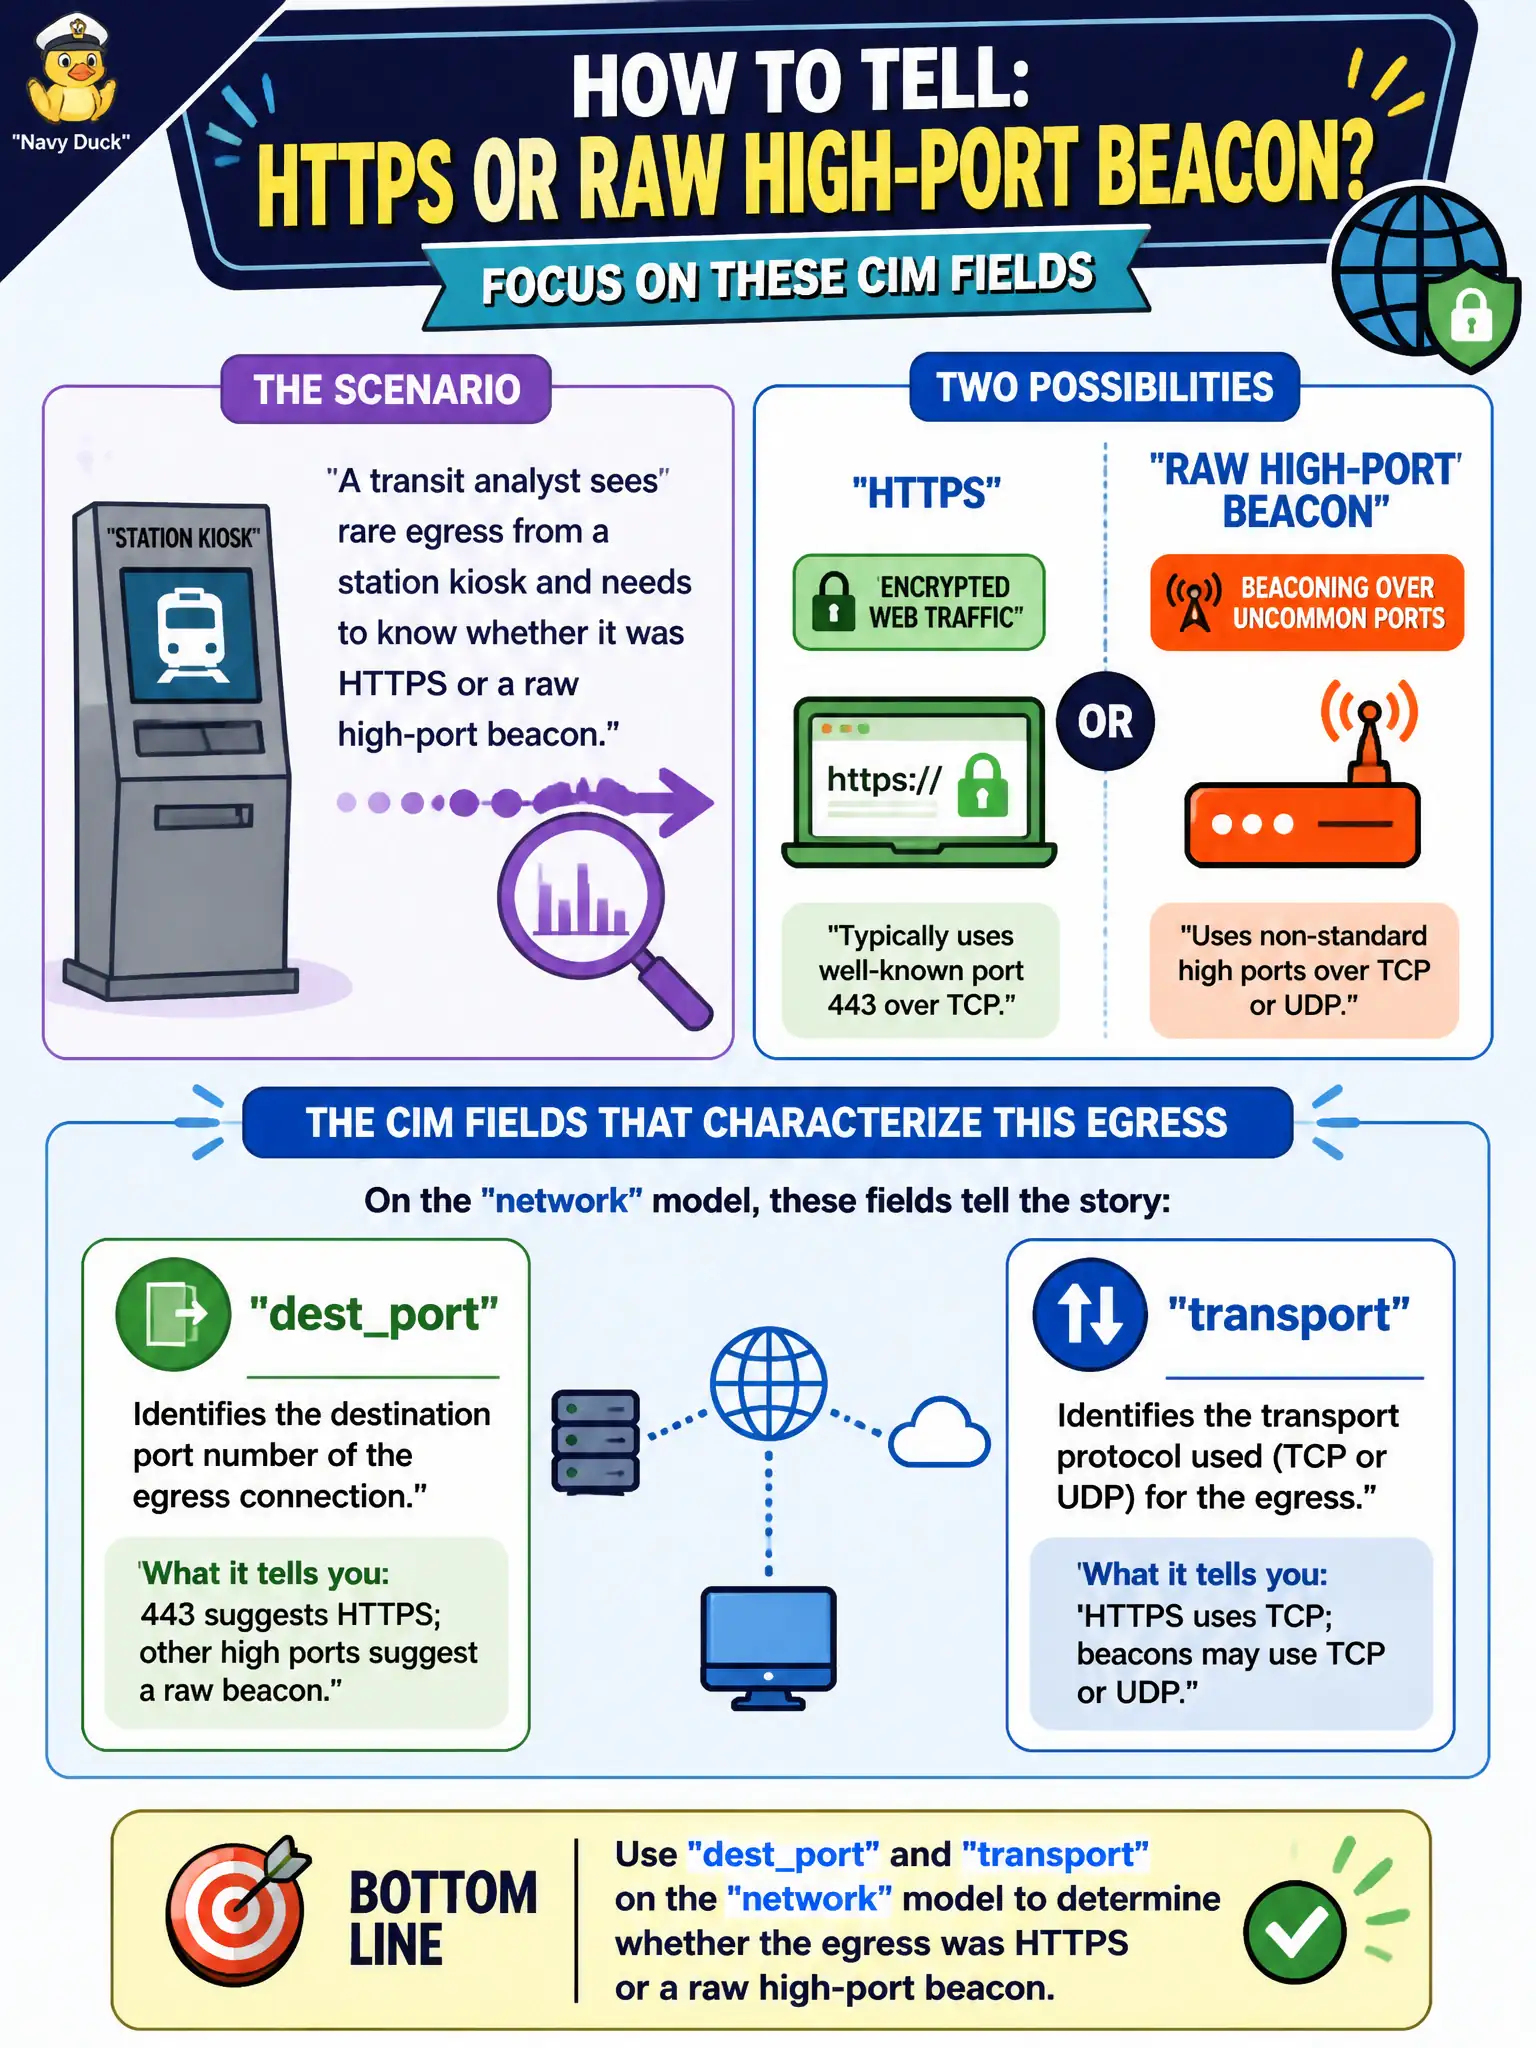
A transit analyst sees rare egress from a station kiosk and needs to know whether it was HTTPS or a raw high-port beacon. Which CIM fields characterize that egress?
Select an answer to reveal the explanation.
Short Explanation
HTTPS versus a weird high-port beacon is a port-and-protocol question. dest_port plus transport on the network model is that nametag. Mail users and hashes will not tell you TLS versus raw TCP.
Full Explanation
Rare egress from a transit station kiosk that might be HTTPS or a raw high-port beacon is characterized with dest_port and transport on the Network_Traffic model. Port 443 with tcp versus an unusual high port with atypical transport is how analysts classify the egress channel before deeper payload inspection or Stream capture. Mail identity fields and authentication malware fields cannot answer that network-characterization question for civic OT-adjacent kiosks.
src_user and dest_user on a mail hop describe mailbox identities, not kiosk egress protocol or destination ports. file_hash and signature on Authentication misuse both the model and the fields—authentication events do not store beacon ports or transport for egress classification. http_user_agent on the Asset and Identity lookup fails because Asset and Identity is not a Web event store and user-agent is not an asset join key.
Exam caveat: protocol and port characterization maps to Network_Traffic dest_port and transport; keep identity and malware fields for their own exam stems.
Operational check: search Network_Traffic for the kiosk source address, tabulate dest_port and transport, flag rare high-port beacons for IR, and only then pull PCAP or proxy detail if HTTPS inspection is in policy scope.