
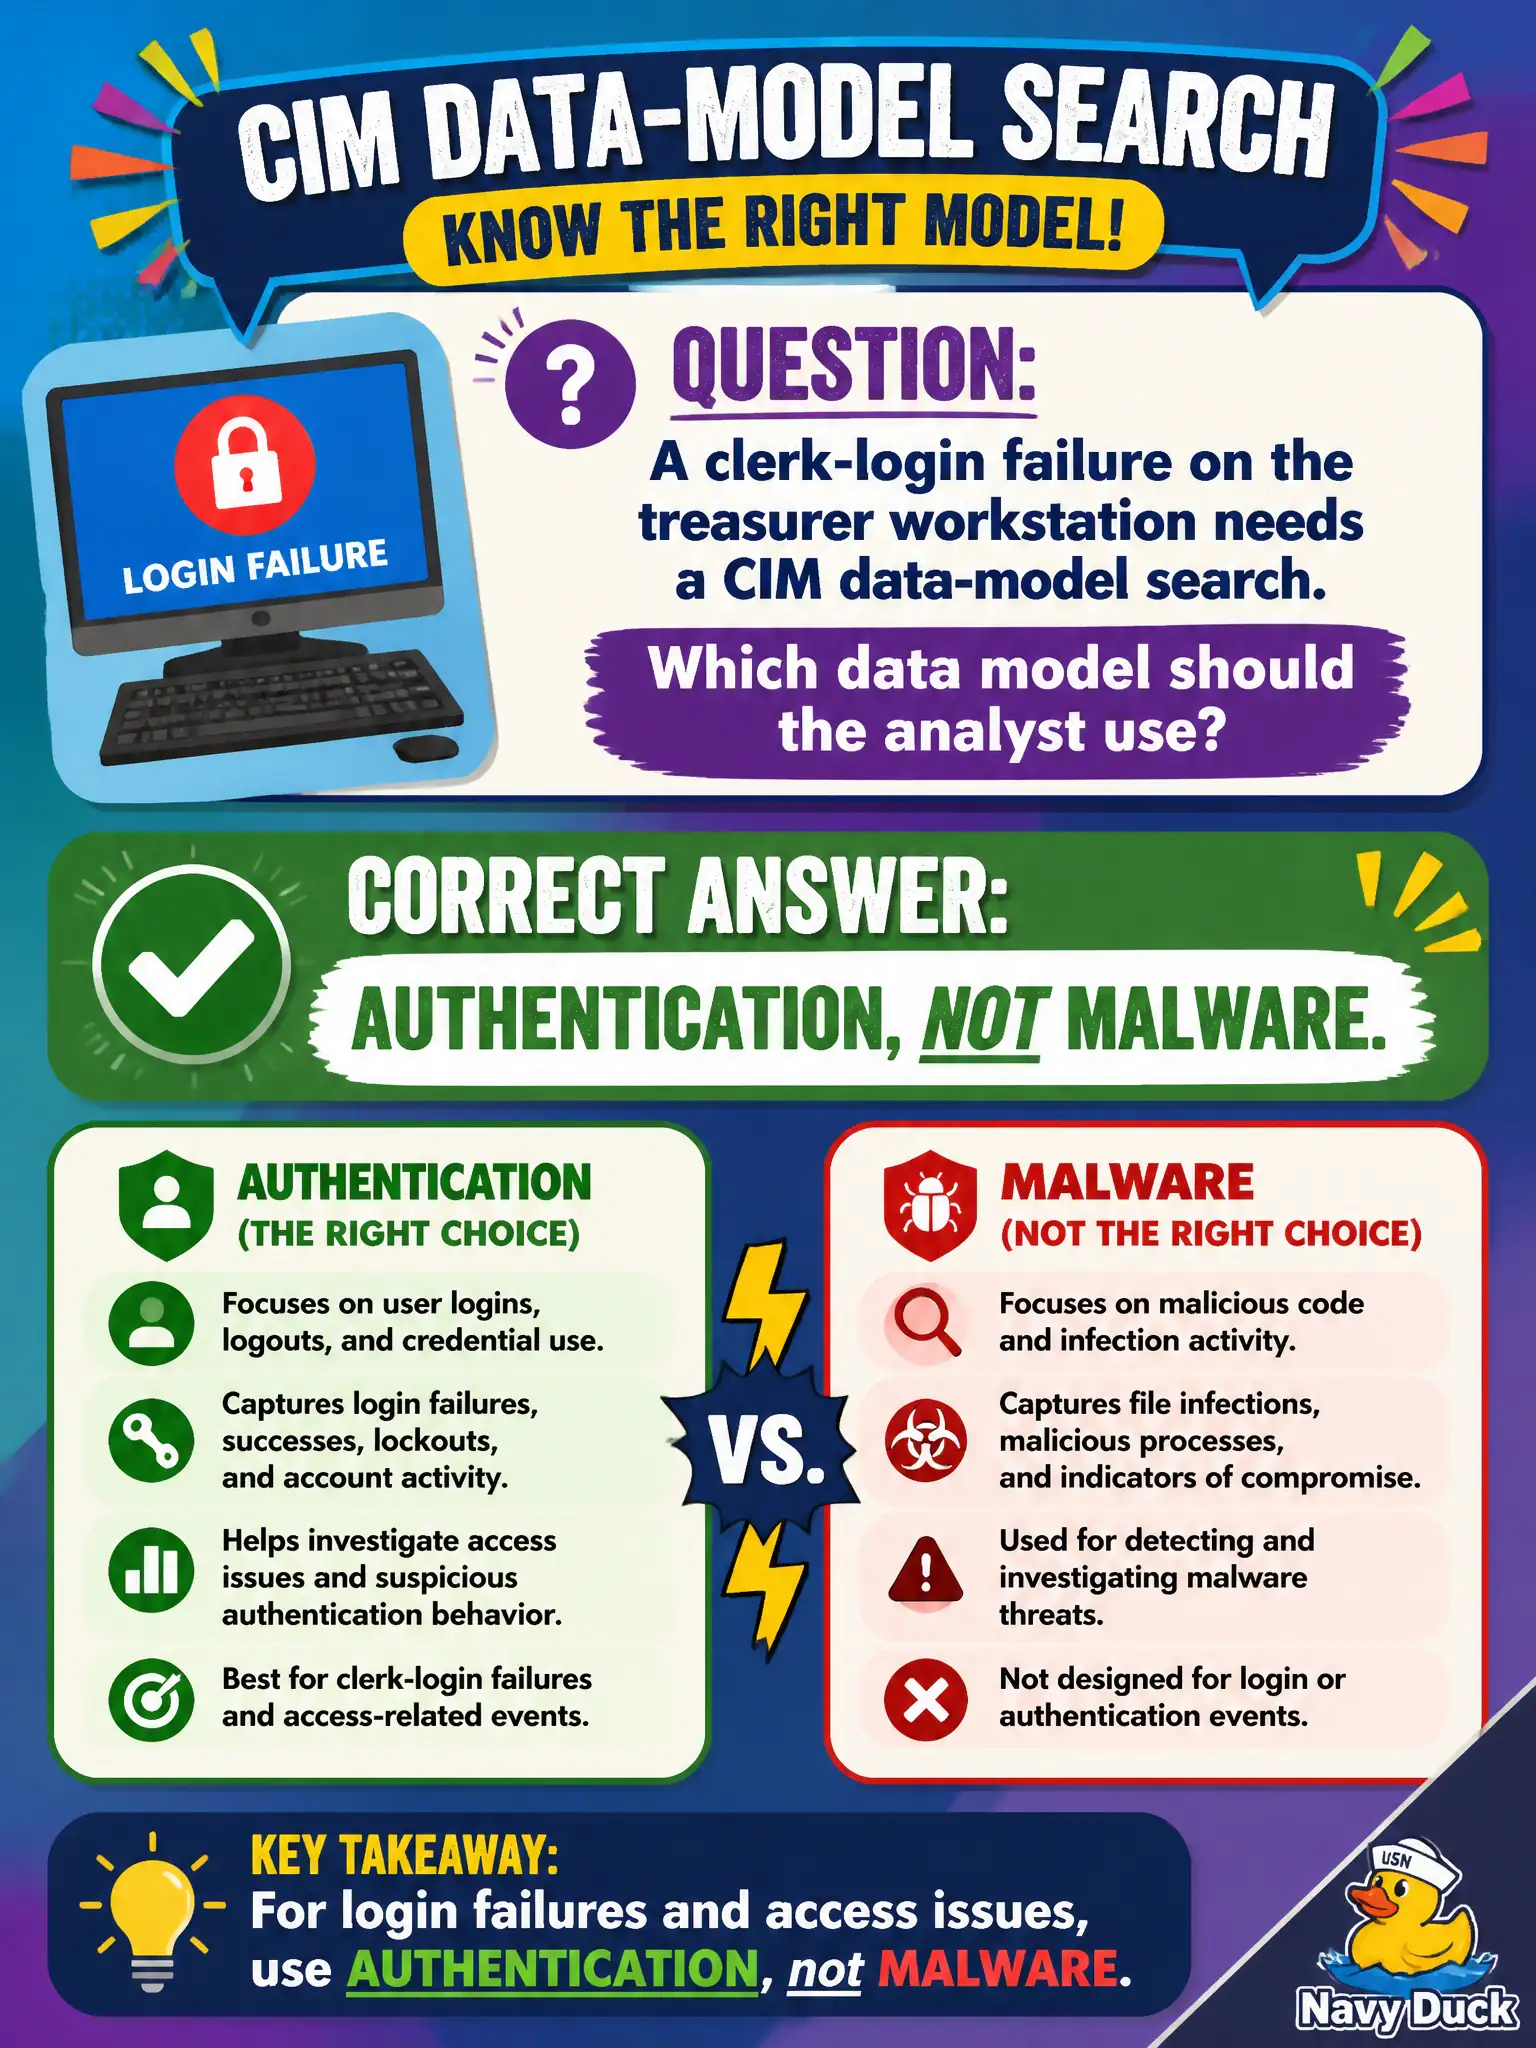
A clerk-login failure on the treasurer workstation needs a CIM data-model search. Which data model should the analyst use?
Select an answer to reveal the explanation.
Short Explanation
A failed clerk login is a badge-reader event, not a virus event. Put it in the Authentication data model. Having a browser or a firewall nearby does not move the event into Web or Malware.
Full Explanation
A clerk-login failure on the treasurer workstation is an authentication event. The correct CIM data model is Authentication, not Malware. Failed logons, successes, and related identity fields live under Authentication so Enterprise Security Access dashboards and tstats searches return consistent civic identity results for that workstation and account.
Choosing Malware because failed logons are supposedly a malware event fails by category—logon failure is authentication telemetry, not malware telemetry. Choosing Web because the workstation has a browser fails by irrelevance to the login-failure question. Choosing Network_Traffic because logons supposedly appear only as firewall sessions fails; Windows or IdP authentication events belong in Authentication, not as a substitute firewall model.
Exam caveat: map activity to the CIM model by semantics—authentication versus malware versus web versus traffic—not by whichever nearby system is convenient.
Operational check: search Authentication where user equals the treasurer account and action indicates failure on the workstation, confirm the sourcetype is tagged for Authentication, and avoid Malware-model filters for pure login-failure hunts.