
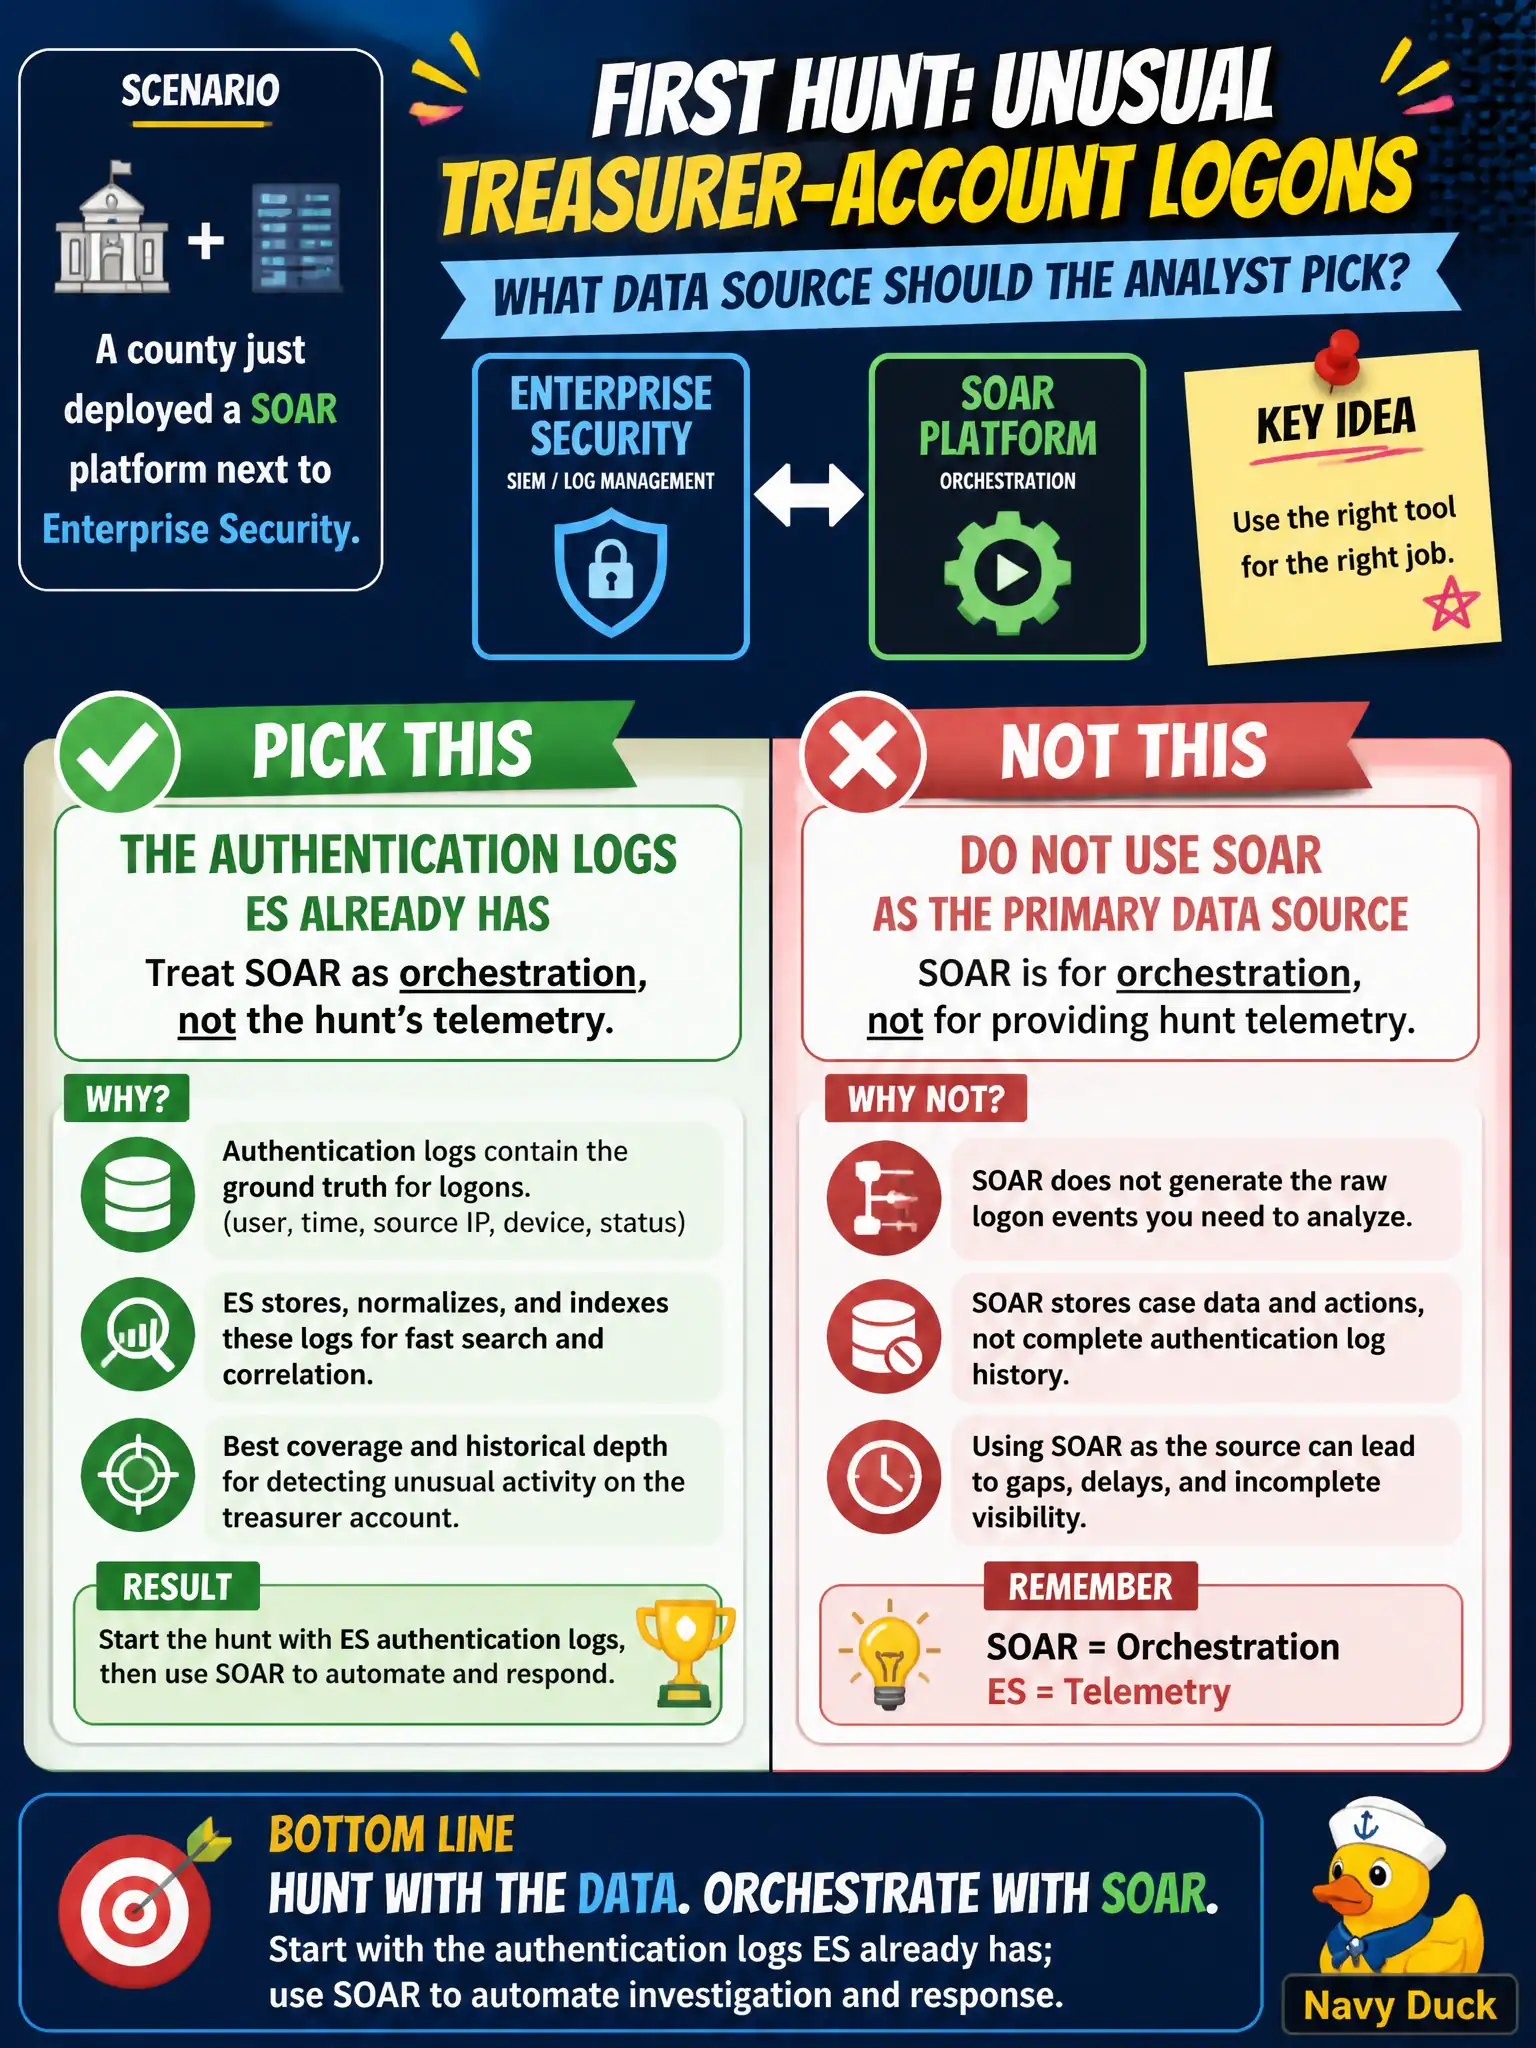
A county just deployed a SOAR platform next to Enterprise Security. The first hunt for unusual treasurer-account logons still needs a primary data source. What should the analyst pick?
Select an answer to reveal the explanation.
Short Explanation
SOAR is the dispatch radio, not the 911 recording. The hunt still starts in the logs ES already has. Playbook audits and case comments will not be the treasurer's logon sourcetype.
Full Explanation
A newly deployed SOAR platform next to Enterprise Security orchestrates response; it is not the primary telemetry for hunting unusual treasurer-account logons. The analyst should pick the authentication logs ES already has—domain, Entra, or VPN sign-ins—as the hunt's data source, and treat SOAR as the layer that may later open cases or run containments. Hunting begins in the SIEM's authentication data, not in orchestration audit trails.
Using the SOAR playbook audit log as the sourcetype that holds original domain logons fails by layer—playbook audits record automation actions, not domain-controller events. Using the SOAR asset inventory as a substitute for Authentication events confuses CMDB-like inventory with logon telemetry. Using SOAR case comments as if they store raw DC telemetry mistakes human or automation notes for Security event logs.
Exam caveat: SOAR is not the data source for the first hunt; Enterprise Security authentication or raw auth indexes remain primary.
Operational check: run the treasurer-account hunt on Authentication in ES, create notables or risk findings as needed, then optionally trigger SOAR for enrichment or containment without treating SOAR logs as the authentication corpus.