
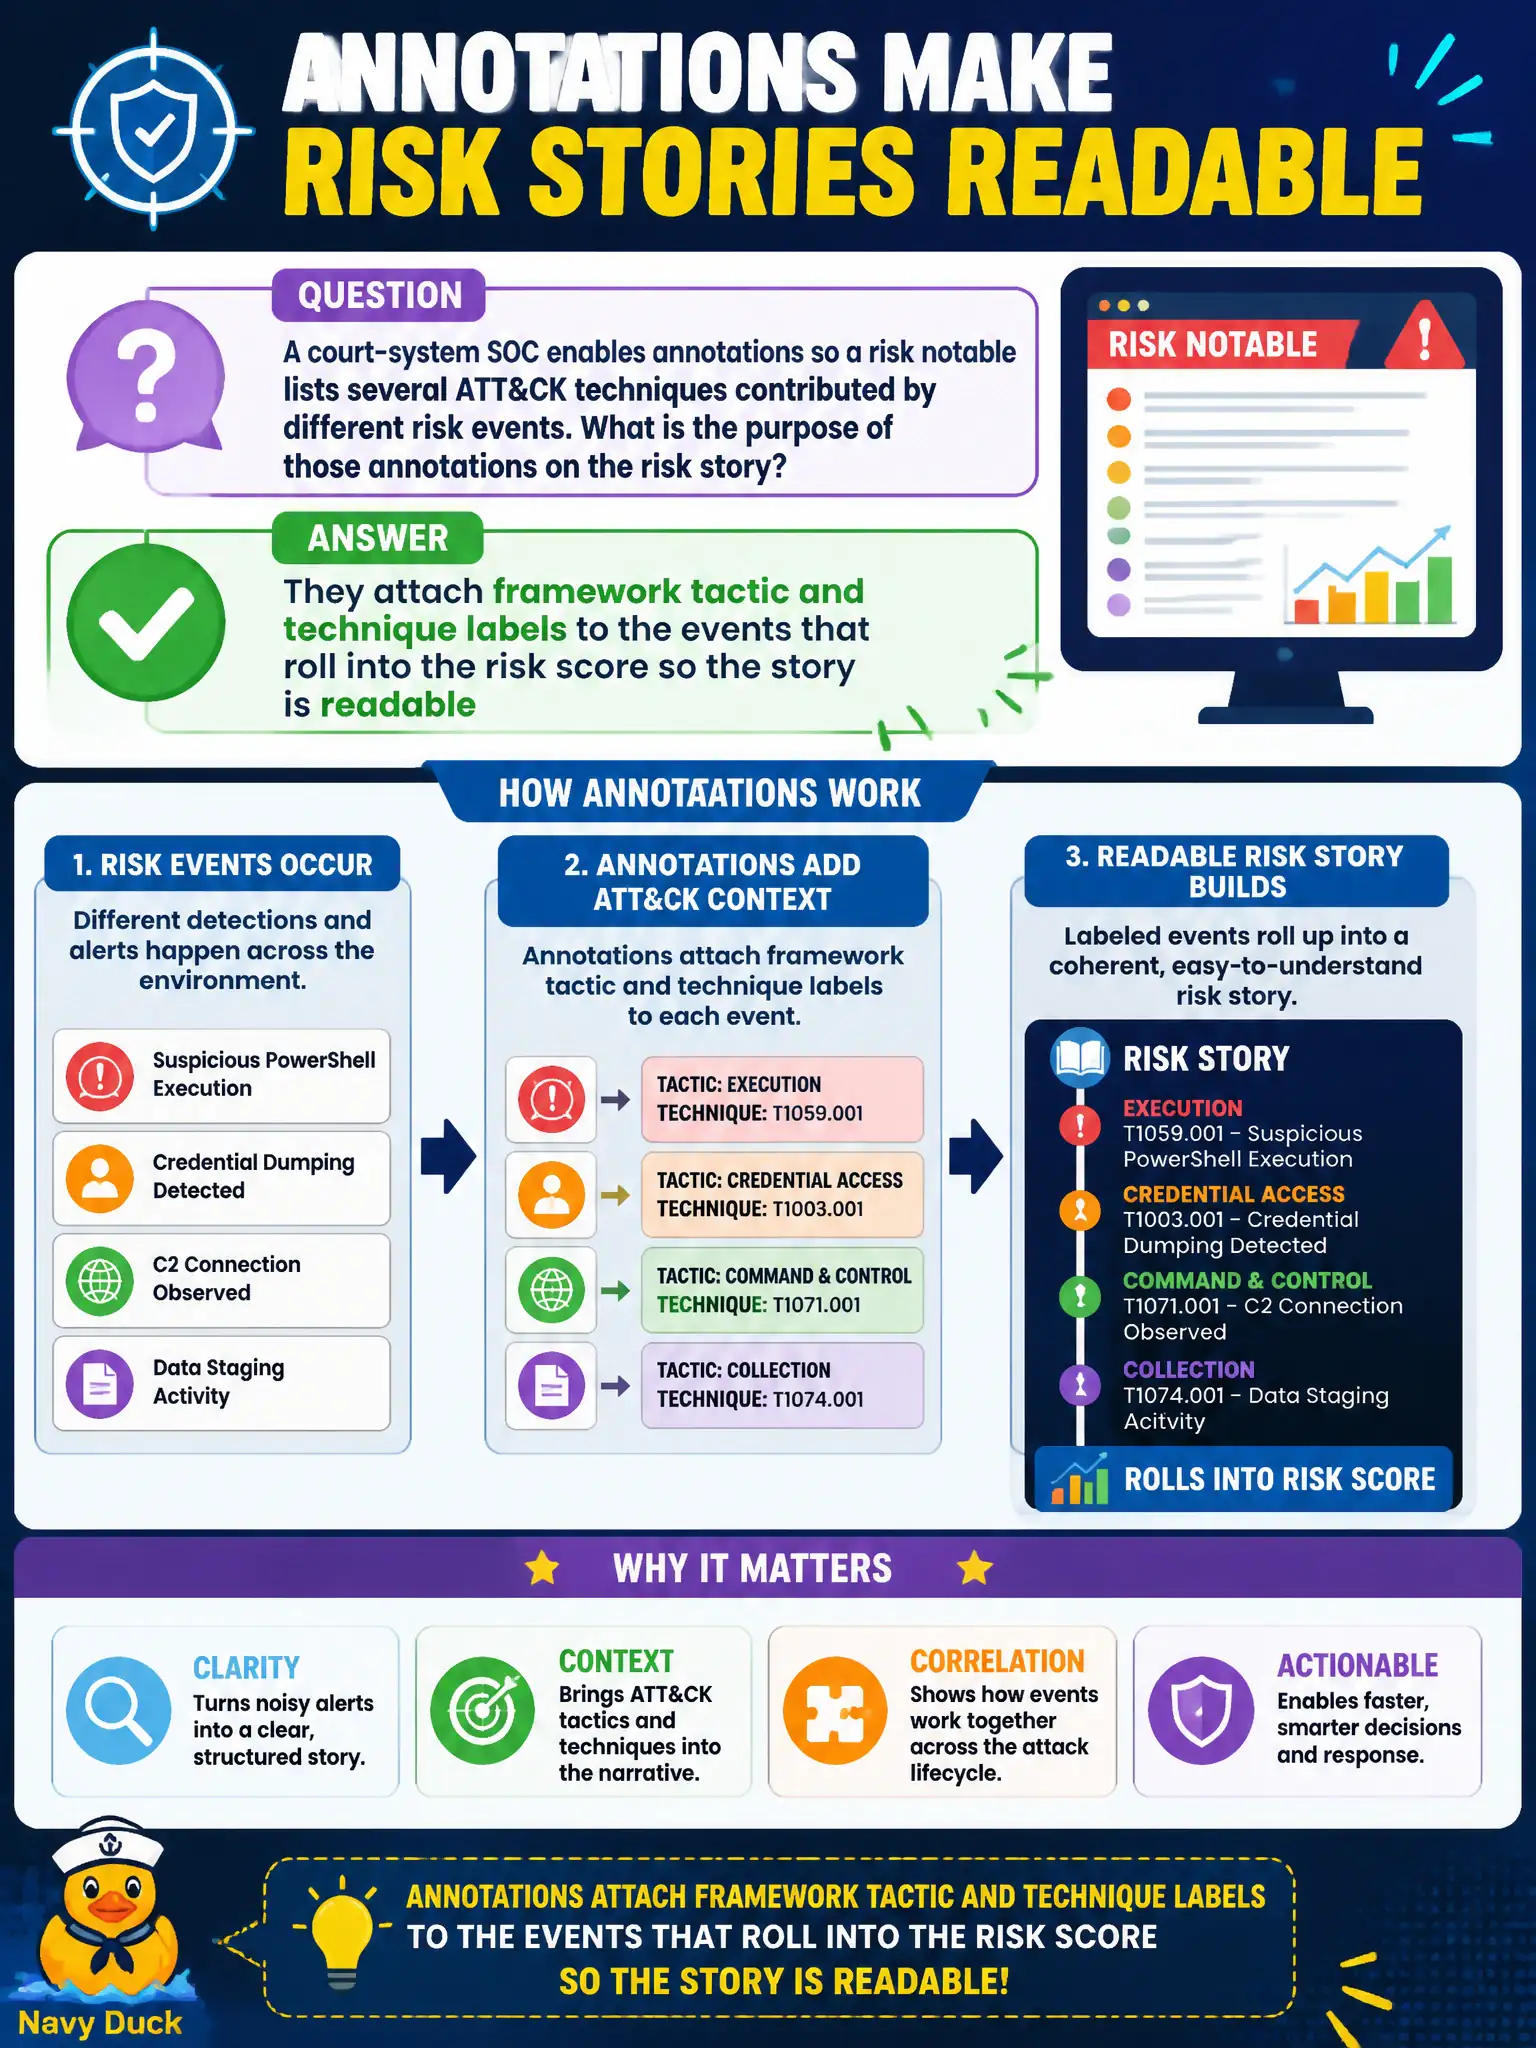
A court-system SOC enables annotations so a risk notable lists several ATT&CK techniques contributed by different risk events. What is the purpose of those annotations on the risk story?
Select an answer to reveal the explanation.
Short Explanation
Annotations are the captions on a photo album of risk. Each contributing event keeps its ATT&CK label so the risk notable reads as a story — credential access then lateral movement — not a bare number. They do not delete detections or mint admin accounts.
Full Explanation
When a court-system SOC enables annotations so a risk notable lists several ATT&CK techniques from different risk events, those annotations attach framework tactic and technique labels to the events that roll into the risk score so the story is readable. Civic Analysts need that captioned album of risk—credential access then lateral movement—rather than a bare numeric score. Annotations make aggregated risk investigable without deleting content or minting admin accounts.
Claiming annotations replace contributing events with a single CIM field fails by concept: annotations label events; they do not collapse them into one CIM field. Claiming they convert the risk object into an ES administrator account fails by concept: risk objects and admin accounts are unrelated. Claiming they delete unannotated detections from the correlation-search list fails by concept: annotation is metadata, not a delete filter for content lists.
Exam caveat: Annotations on risk stories = readable framework labels on contributing events; they are not deletion tools or privilege changes.
Operational check: Open a sample finance or court risk notable, confirm each contributing event shows its ATT&CK labels, and coach Analysts to narrate the multi-technique path before disposition.