
A multinational energy corporation operates in dynamic regulatory environments globally. The Chief Compliance Officer schedules annual reviews of all compliance policies and procedures. Why is this regular update cycle essential?
Select an answer to reveal the explanation.
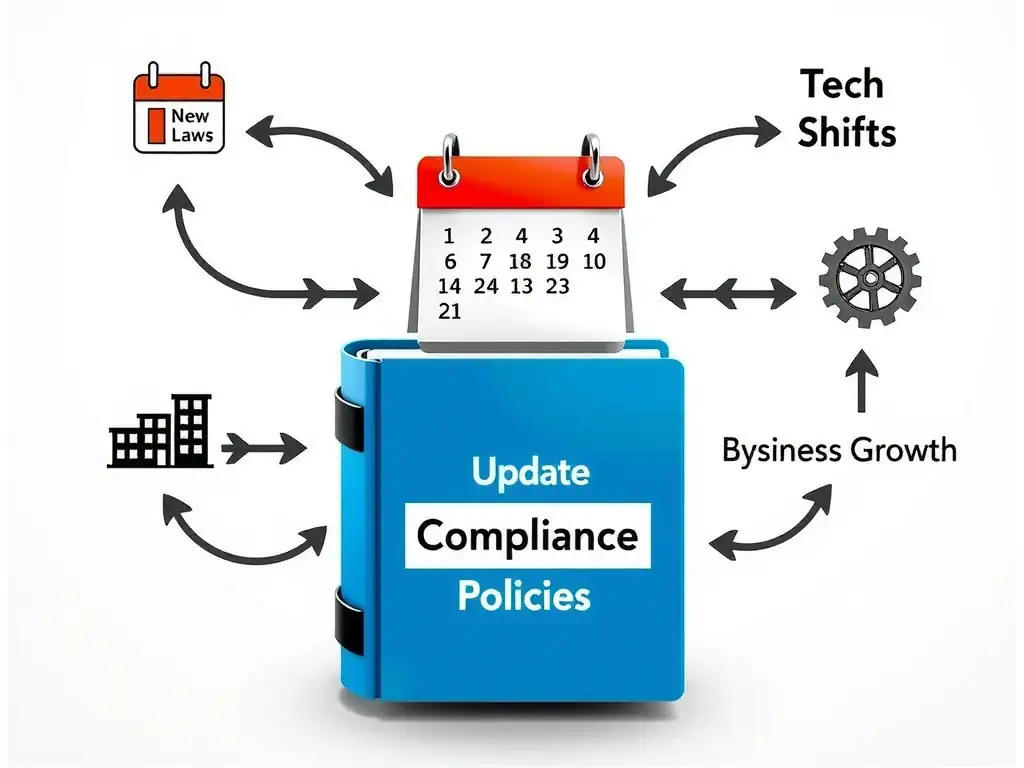
Short Explanation
Think about your home router or firewall. You don't set it up once and ignore firmware updates, because new threats keep showing up. Compliance policies are the same: you update them to keep defenses current as laws, risks, and business realities change.
Full Explanation
Policies and procedures form the structural foundation of a corporate compliance program, setting expectations for employee behavior and operational controls. A compliance program cannot be static. Regulators, including the U.S. DOJ and international bodies, emphasize that a compliance program must evolve alongside the company's business model, risk profile, and external regulatory environment. The correct choice is the one that says regular updates maintain the relevance of internal standards in response to evolving regulations and emerging risks. The primary objective of reviewing and updating policies is to keep them relevant, practical, and effective in mitigating new and emerging risks. For example, the rise of remote work, new sanctions regimes, or updated data privacy laws, such as GDPR updates, require immediate policy adjustments to prevent compliance gaps. The choice about creating an impression of compliance that hides a lack of actual program enforcement is wrong because keeping policies updated merely as window dressing, or a 'paper program,' without operationalizing them is viewed negatively by regulators and does not protect the company from liability. The choice about expanding the volume of compliance manuals to make them as lengthy and detailed as possible is wrong because policy updates should aim for clarity, conciseness, and usability. Simply making manuals longer and more complex reduces employee comprehension and compliance rates. The choice about eliminating the need for a dedicated, full-time corporate compliance officer is wrong because regular policy updates require expert oversight; they do not replace the need for a compliance officer, but rather serve as a core tool for the compliance officer to manage risk.