
To maintain regulatory alignment and mitigate emerging threats, how should an organization approach the operational execution of its compliance risk assessment process?
Select an answer to reveal the explanation.
Short Explanation
Think of compliance risk assessment like driving: you can't glance at the road once and expect to stay safe. New laws, new products, and new threats pop up all the time, so you need a continuous, living process that adapts as your business and the world change.
Full Explanation
An effective compliance risk assessment is not a static event but a dynamic, ongoing management process. Regulatory guidance, including the Department of Justice's Evaluation of Corporate Compliance Programs, emphasizes that a compliance program should be constantly evolving based on continuous risk assessments.
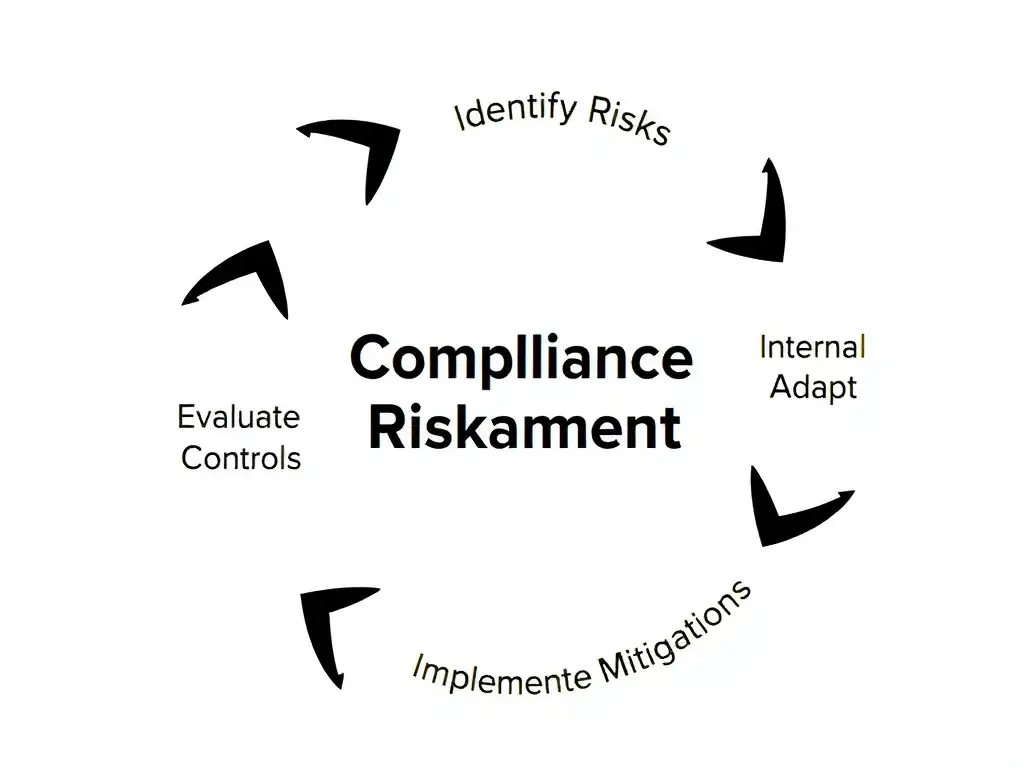
The correct approach is the continuous, iterative cycle that dynamically adapts to internal operational changes and shifts in the external regulatory landscape, because risk assessment must be continuous and adaptive. An organization's risk profile changes constantly due to factors such as entering new geographic markets, introducing new products, technological advancements, organizational restructuring, or changes in laws and regulations. The continuous loop of assessment, mitigation, and re-evaluation ensures that the compliance program remains tailored to the company's actual, current risk profile.
The approach of a static, periodic exercise performed exclusively by external consulting firms to ensure objectivity is incorrect because while external auditors or consultants can provide valuable independent oversight, relying exclusively on them ignores the critical need for internal operational knowledge and ownership of risks. Additionally, a static audit is insufficient for risk management.
The approach of a specialized audit focusing strictly on financial reporting accuracy and tax compliance is incorrect because compliance risk extends far beyond financial risks. It encompasses operational, legal, reputational, data privacy, environmental, health and safety, and employment risks. Focusing solely on financial risks leaves massive vulnerabilities unaddressed.
The approach of a one-time baseline project designed to establish static policy controls for the organization's lifetime is incorrect because a one-time baseline project will quickly become obsolete. It fails to account for new regulatory threats or internal changes, rendering the established controls ineffective over time.
Best practices for compliance risk assessments include establishing a cross-functional risk committee, utilizing data analytics to monitor risk indicators in real time, and systematically updating policies and training materials in response to new risk findings.