
When establishing a third-party risk management (TPRM) framework, what is the primary objective of conducting risk assessments on external business partners, such as agents, distributors, and suppliers?
Select an answer to reveal the explanation.
Short Explanation
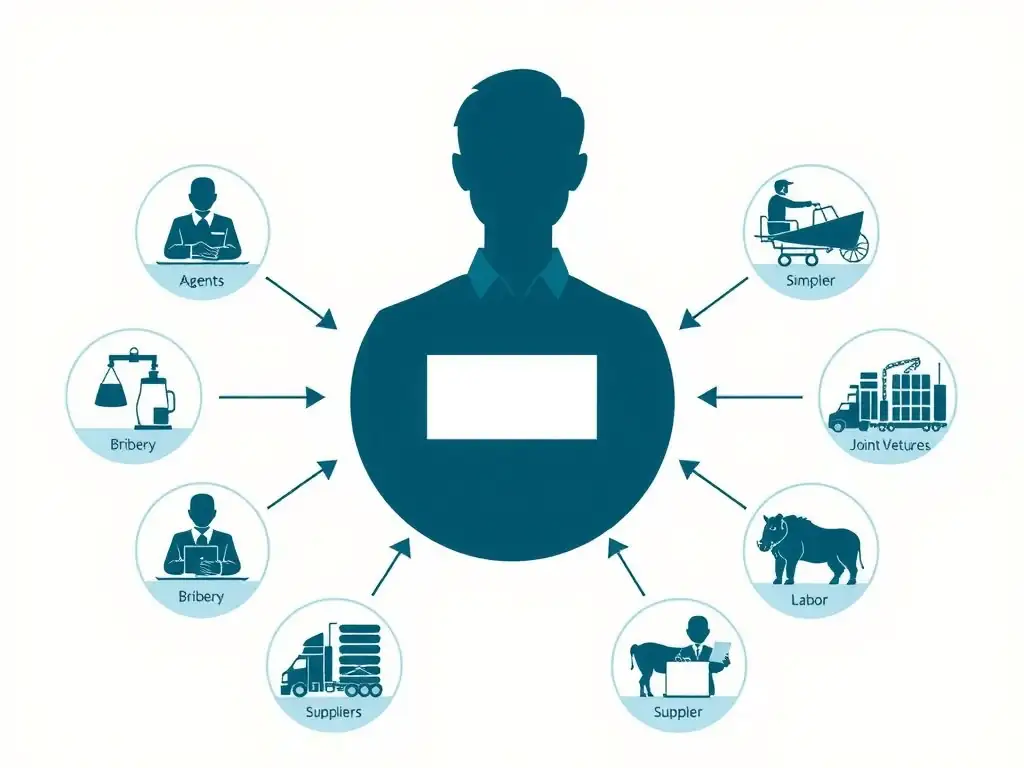
Here's the deal: you can outsource work, but you can't outsource risk. If a third-party agent pays a bribe, your company can still be on the hook under laws like the FCPA, so you have to vet partners for bribery, weak controls, and regulatory issues before signing.
Full Explanation
Third-party risk management (TPRM) is a critical component of any effective compliance program. Under international anti-corruption frameworks, such as the Foreign Corrupt Practices Act (FCPA) and the UK Bribery Act, organizations are frequently held criminally liable for the corrupt acts of their intermediaries, agents, joint venture partners, distributors, and suppliers. Therefore, conducting comprehensive due diligence and risk assessments on these entities is not optional; it is a regulatory necessity.
The correct objective is to identify and evaluate the likelihood that a third party's conduct could expose the hiring company to legal, regulatory, or reputational liability. This assessment determines the level of due diligence required, the compliance clauses needed in the contract, and the ongoing monitoring activities necessary to mitigate those risks.
The payroll-tax audit objective is incorrect because while payroll tax compliance is important, auditing a third party's internal payroll is typically not the primary objective of a standard compliance risk assessment for external partners.
The accounts-payable invoice-processing objective is incorrect because invoice processing and timely payment are operational accounting tasks, not compliance risk management functions designed to detect regulatory exposures.
The vendor-pricing cost-saving objective is incorrect because sourcing the cheapest provider is a procurement or supply chain optimization goal, which is separate from the compliance risk assessment process.