
Finance staff manage consolidated billing in the payer account while the SOC runs Security Hub and GuardDuty admin tooling elsewhere. How should those roles be separated in the org design?
Select an answer to reveal the explanation.
Short Explanation
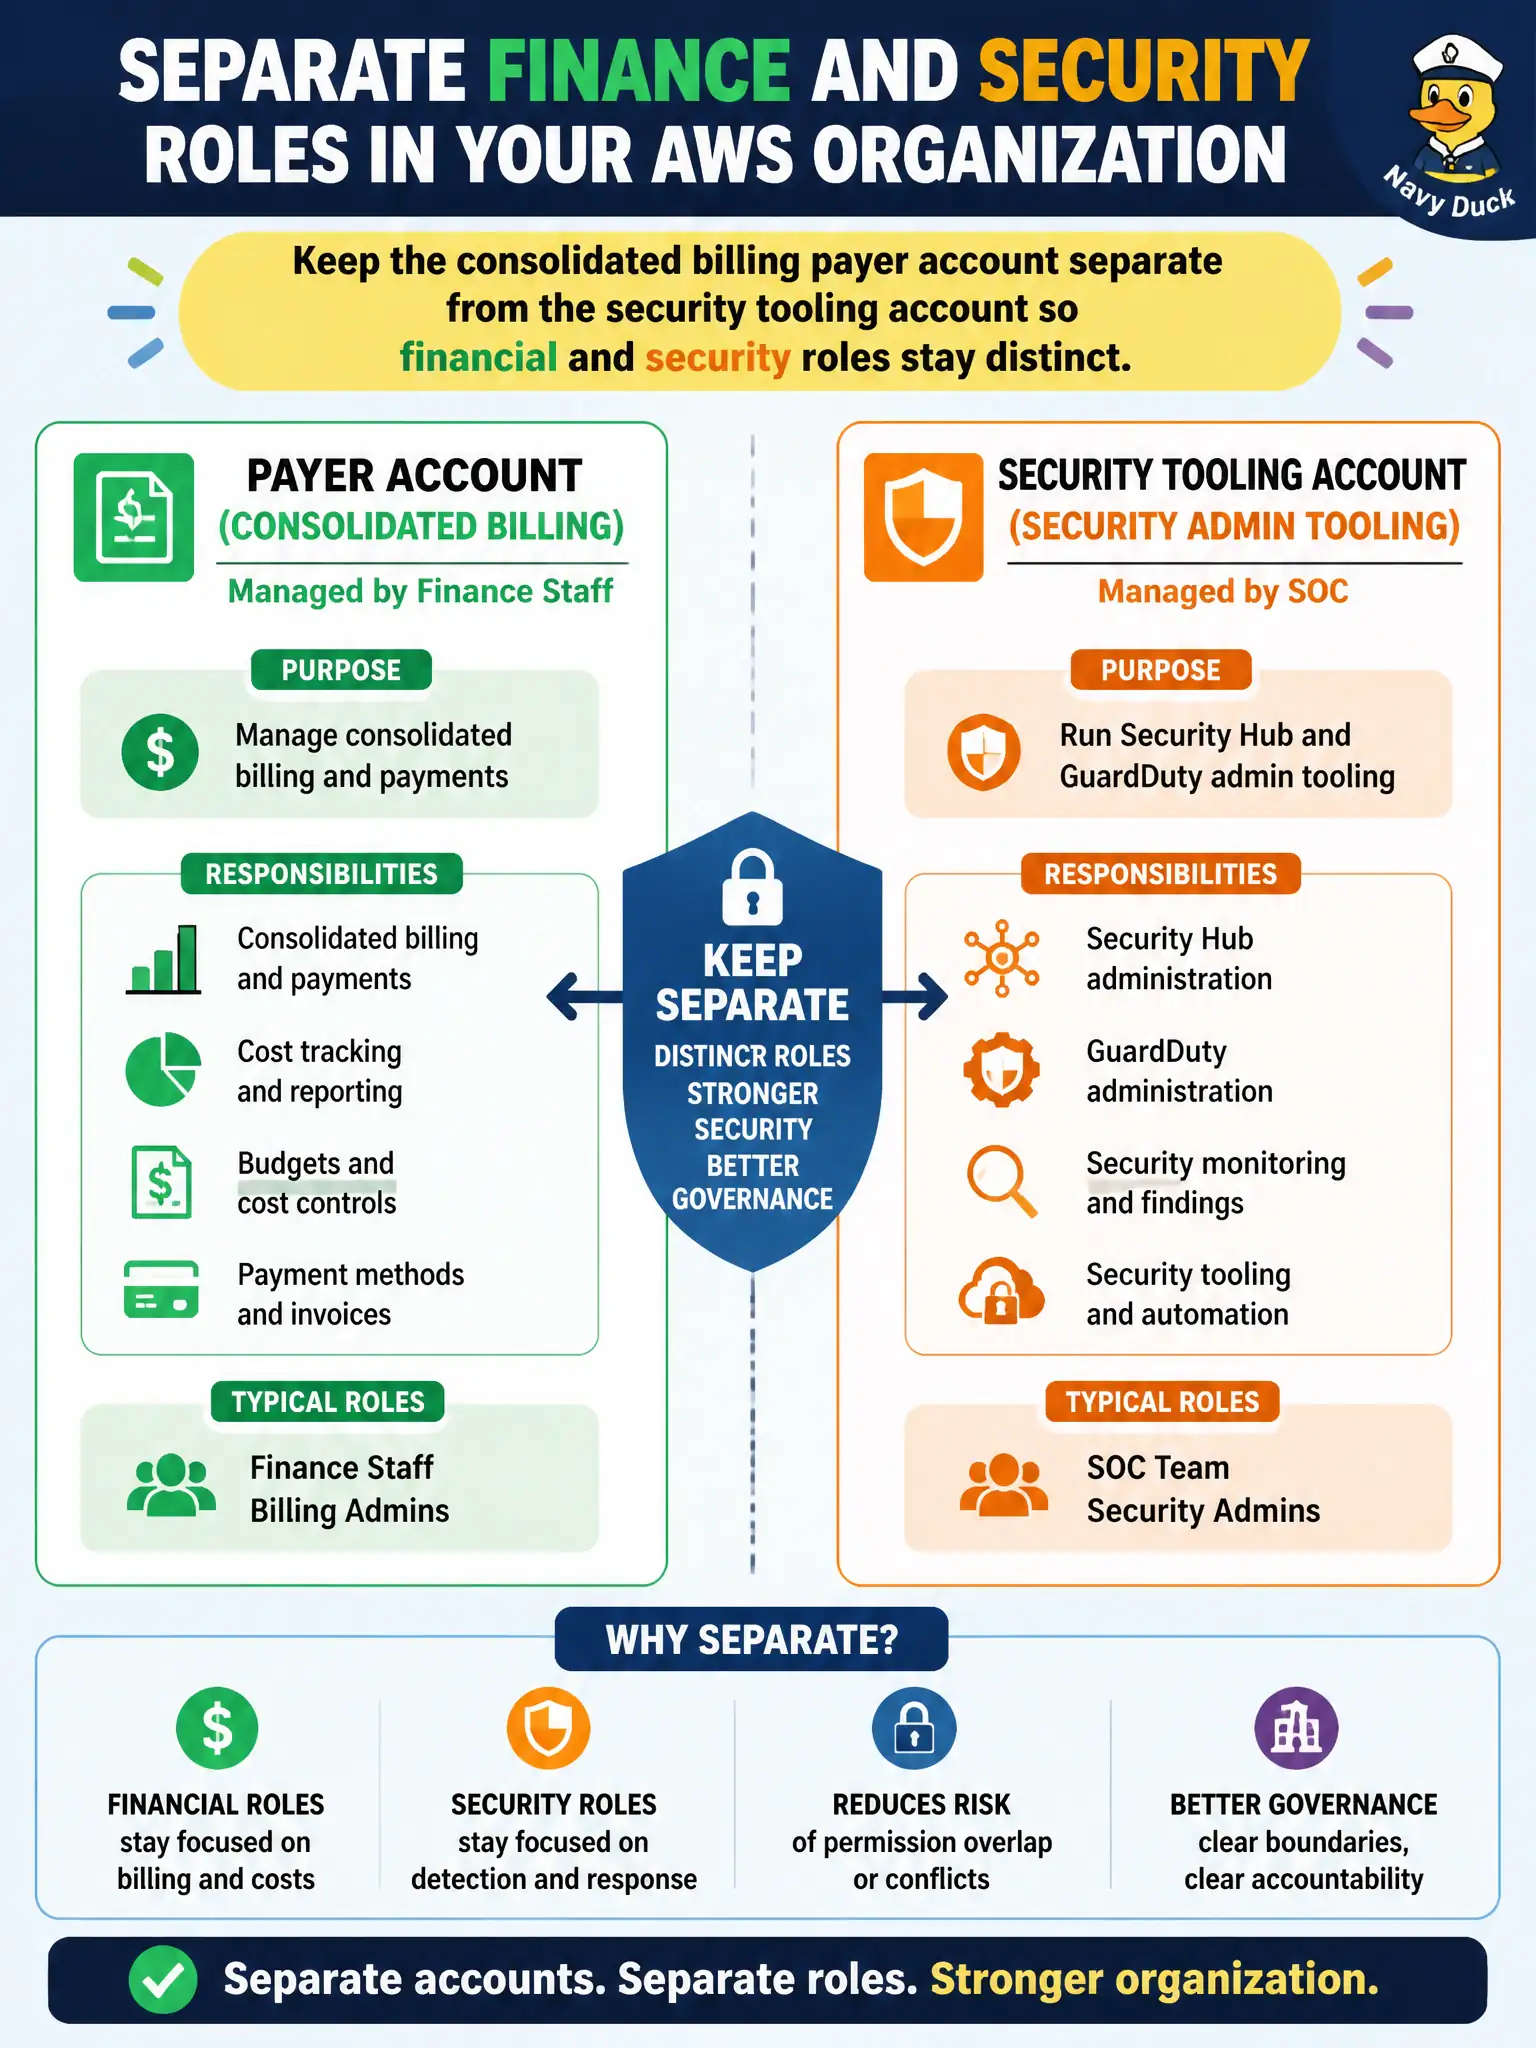
The city treasurer's office is not the police evidence room — different locks, different staff. Keep the payer account for consolidated billing and a separate security account for Hub and GuardDuty admin.
Full Explanation
Finance staff who manage consolidated billing in the payer account and a SOC that runs Security Hub and GuardDuty administration should keep those roles in separate accounts. The consolidated billing payer account remains the financial control plane, while a dedicated security tooling account holds delegated Security Hub and GuardDuty administration. Separating financial and security duties reduces conflicts of interest, limits blast radius if either account is compromised, and matches multi-account landing-zone norms for municipalities.
Colocating billing payer functions and all security tooling admin in one overloaded root or management-centric account concentrates privilege and muddies who owns which control plane. Giving every developer AdministratorAccess in the payer account to simplify invoices expands financial blast radius far beyond finance staff. Deleting the security account and running GuardDuty only from personal IAM users in workload accounts abandons org-level detection administration.
Exam caveat: payer/management financial functions and security tooling delegated admin are intentionally separable concerns on SAP-C02 multi-account designs. Operational check: document which account is payer versus security admin, confirm GuardDuty/Security Hub delegated admin is not the same role set as billing owners, and review IAM Identity Center permission sets so developers lack payer AdministratorAccess.