
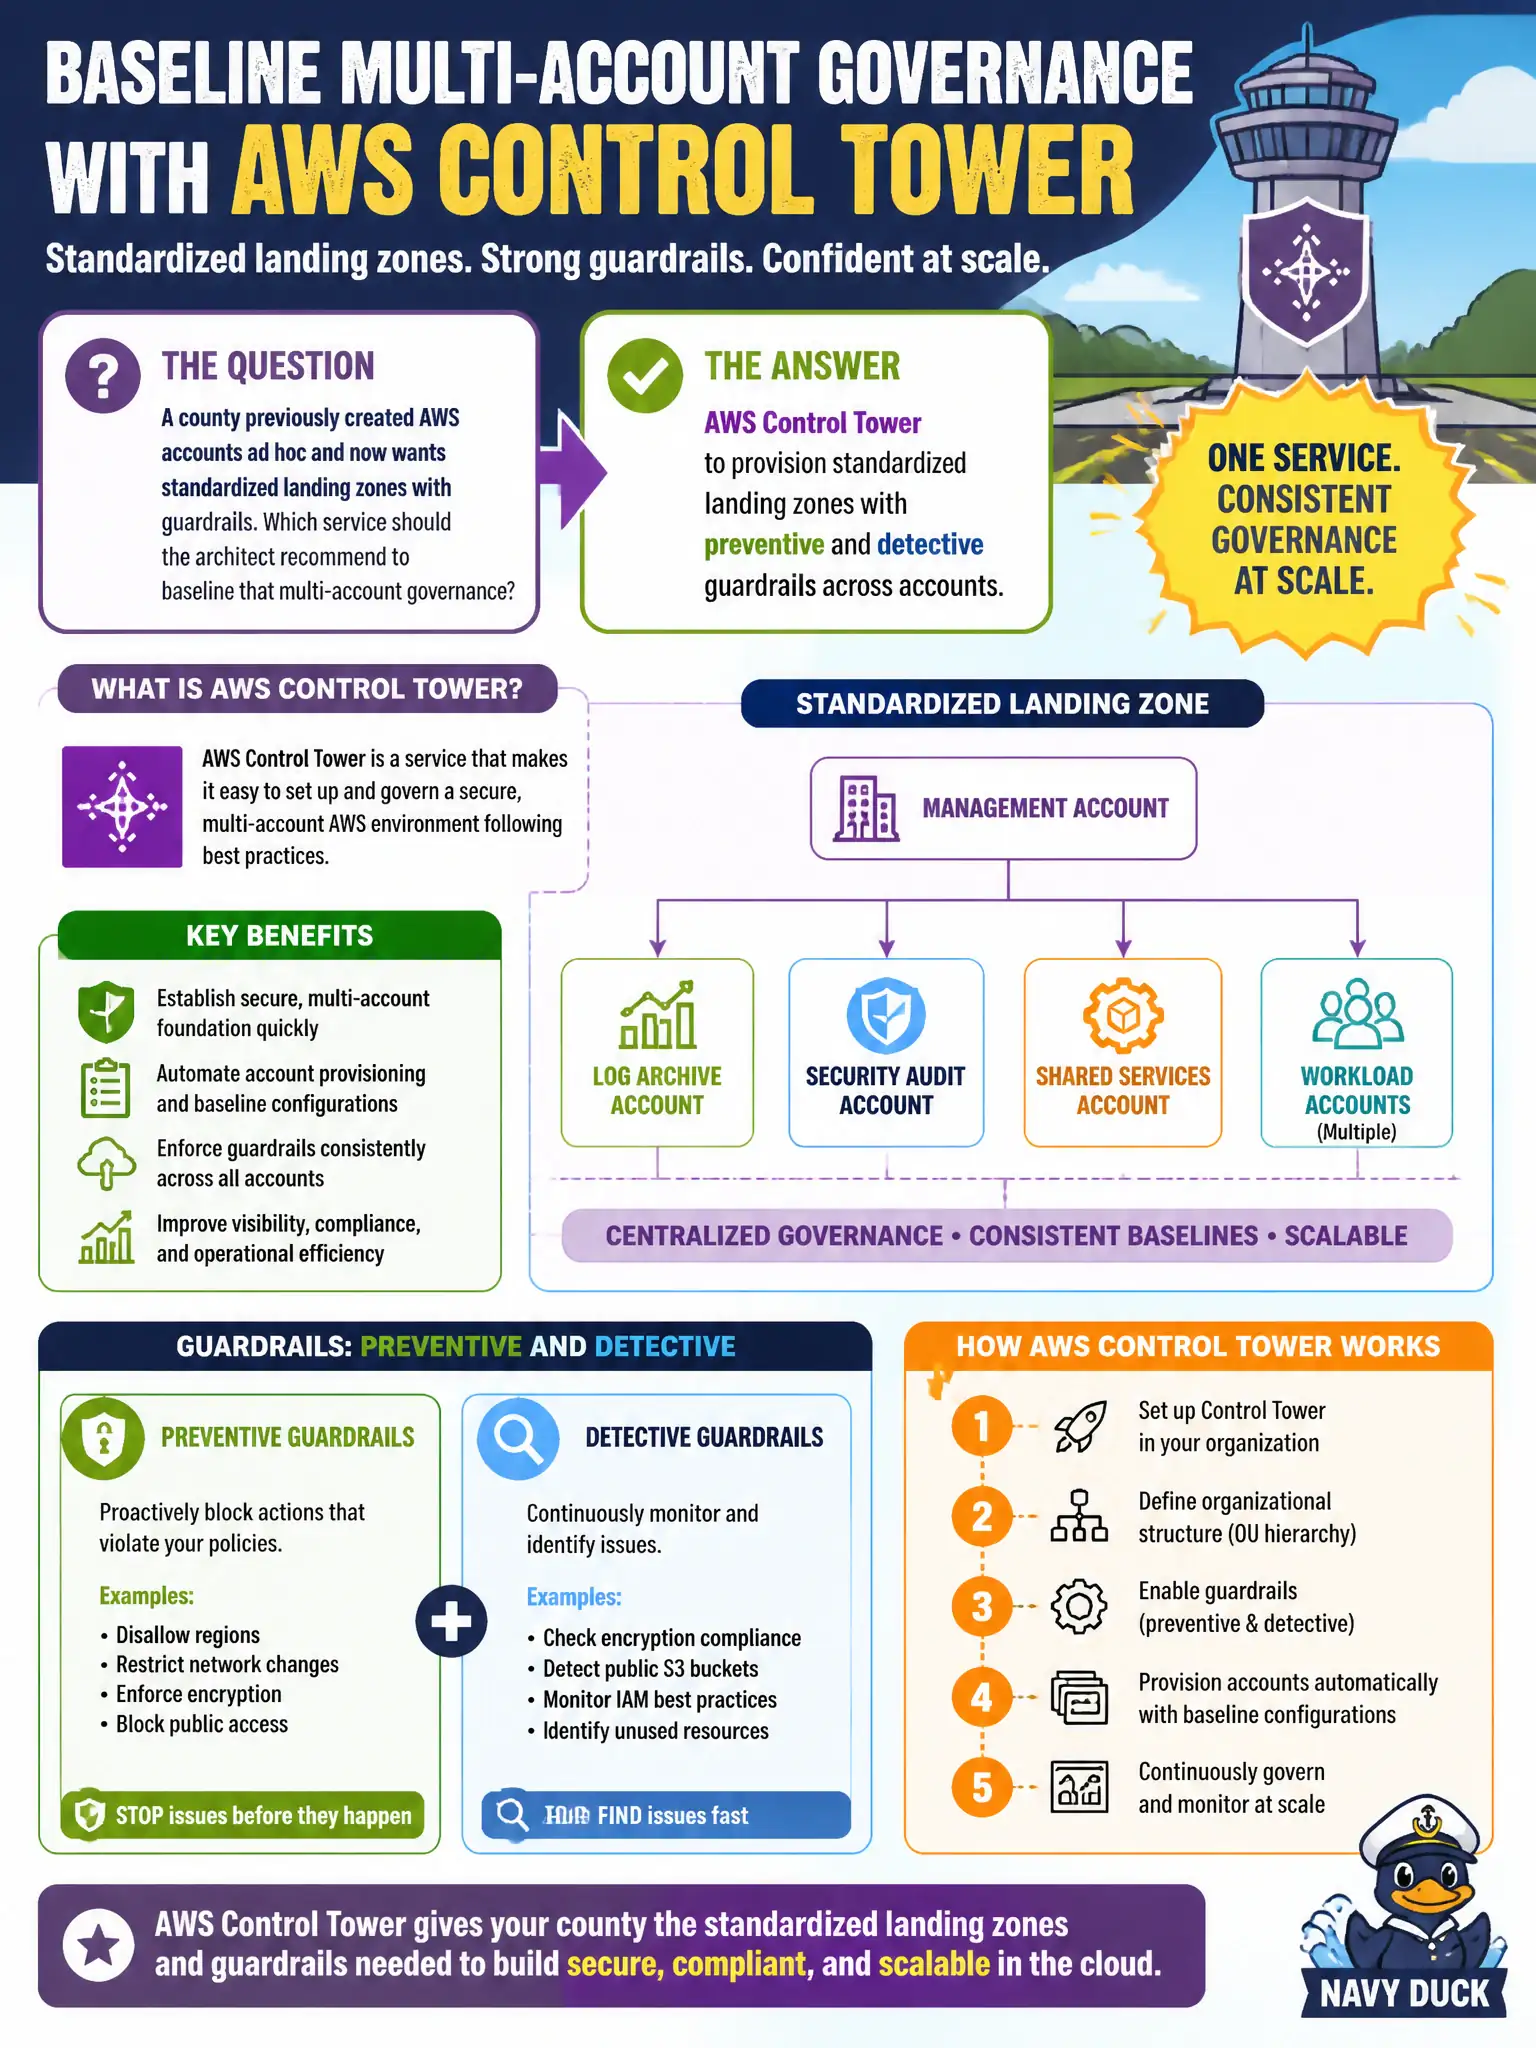
A county previously created AWS accounts ad hoc and now wants standardized landing zones with guardrails. Which service should the architect recommend to baseline that multi-account governance?
Select an answer to reveal the explanation.
Short Explanation
Control Tower is the county’s standard starter kit for new buildings—wiring, locks, and inspectors included. It replaces one-off accounts and wiki hopes. GameLift is for games (out of scope here), and ditching Organizations undoes governance.
Full Explanation
Counties that previously opened AWS accounts ad hoc should baseline multi-account governance with AWS Control Tower. Control Tower provisions standardized landing zones, Account Factory vending, and preventive plus detective guardrails so new accounts inherit centralized logging, AWS Config, CloudTrail, and SCP baselines instead of wiki-only exceptions. That recommendation replaces one-off account opens with a governed municipal landing zone that auditors can recognize and operations can repeat.
Continuing ad hoc account opens with no baseline and documenting exceptions only in a wiki perpetuates configuration drift, inconsistent security tooling, and findings that surface during every assessment. Amazon GameLift orchestrates game server fleets for multiplayer workloads; it is not a government account-vending or landing-zone service. Disabling AWS Organizations so each account remains fully independent forever removes the organizational control plane that Control Tower, SCPs, and delegated security administrators require.
Exam caveat: Control Tower builds on AWS Organizations and is the managed landing-zone answer when a stem asks to standardize accounts and guardrails after a period of unmanaged growth. Operational check: enable Control Tower in the management account, vend a pilot workload account through Account Factory into the correct OU, confirm mandatory guardrails and log-archive connectivity, and retire the wiki-only exception process for all newly requested county accounts.