
After a phishing wave, a city needs org-wide visibility into suspicious API activity correlated across accounts for investigation and notifications. Which approach should the architect prescribe?
Select an answer to reveal the explanation.
Short Explanation
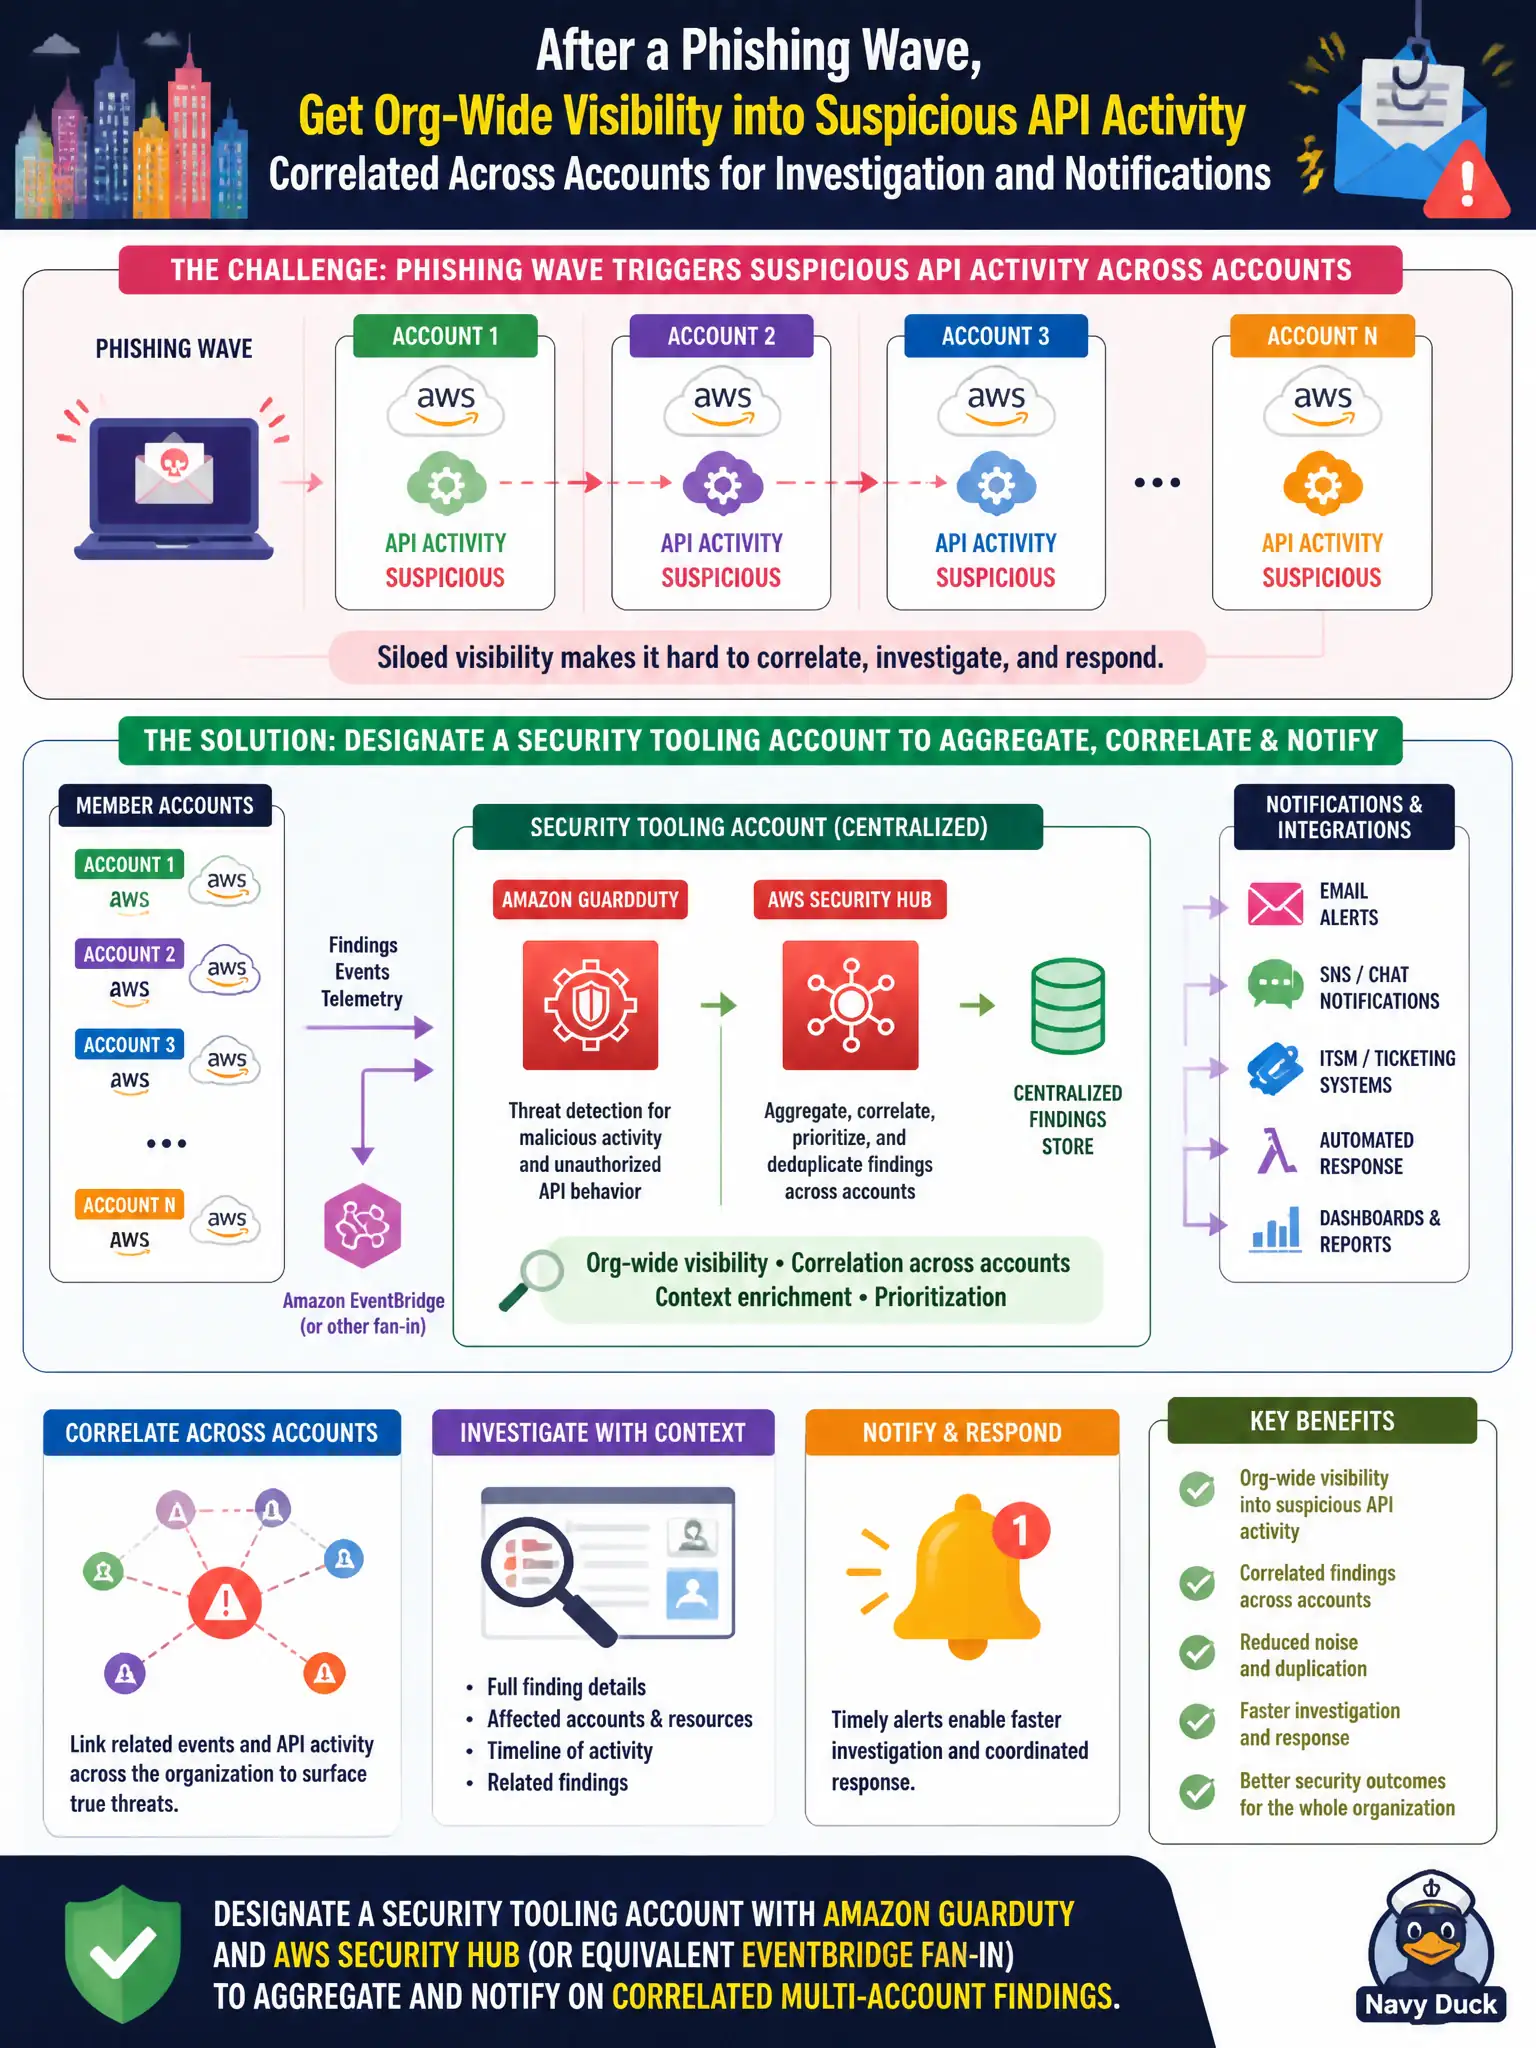
Think of one city-wide 911 console instead of every precinct keeping its own paper tip jar. Central GuardDuty/Security Hub (with EventBridge into a security account) correlates suspicious API activity across accounts so phishing fallout is visible org-wide. Weekly screenshot emails, turning GuardDuty off, or dumping keys in a bucket leave the SOC blind.
Full Explanation
After a phishing wave, org-wide visibility into suspicious API activity requires a security tooling account that aggregates Amazon GuardDuty and AWS Security Hub findings (or equivalent EventBridge fan-in) across member accounts for investigation and notifications. GuardDuty analyzes CloudTrail, DNS, and VPC flow telemetry for threat findings; Security Hub correlates and normalizes multi-account signal so the city SOC can notify on-call without hopping account consoles. That centralized detective pattern is how municipalities investigate credential abuse at Organization scale.
Relying on each department to review its own CloudTrail console weekly and email screenshots cannot meet incident timelines after phishing. Disabling GuardDuty in member accounts to reduce noise and keeping only VPC Flow Logs in networking removes the API-behavior detections phishing investigations need. Storing long-lived access keys for every account in a shared S3 bucket so the SOC can poll DescribeEvents manually creates a credential honey-pot and is not an architecture.
Exam caveat: GuardDuty + Security Hub delegated administrator is the standard multi-account detection answer; CloudTrail is the log source, not the correlation UI. Operational check: designate the security account as GuardDuty/Security Hub admin, auto-enable members, simulate a Finding with a known technique in a sandbox, confirm central notification via EventBridge/SNS, and verify member accounts cannot simply turn detectors off if SCPs forbid it.