
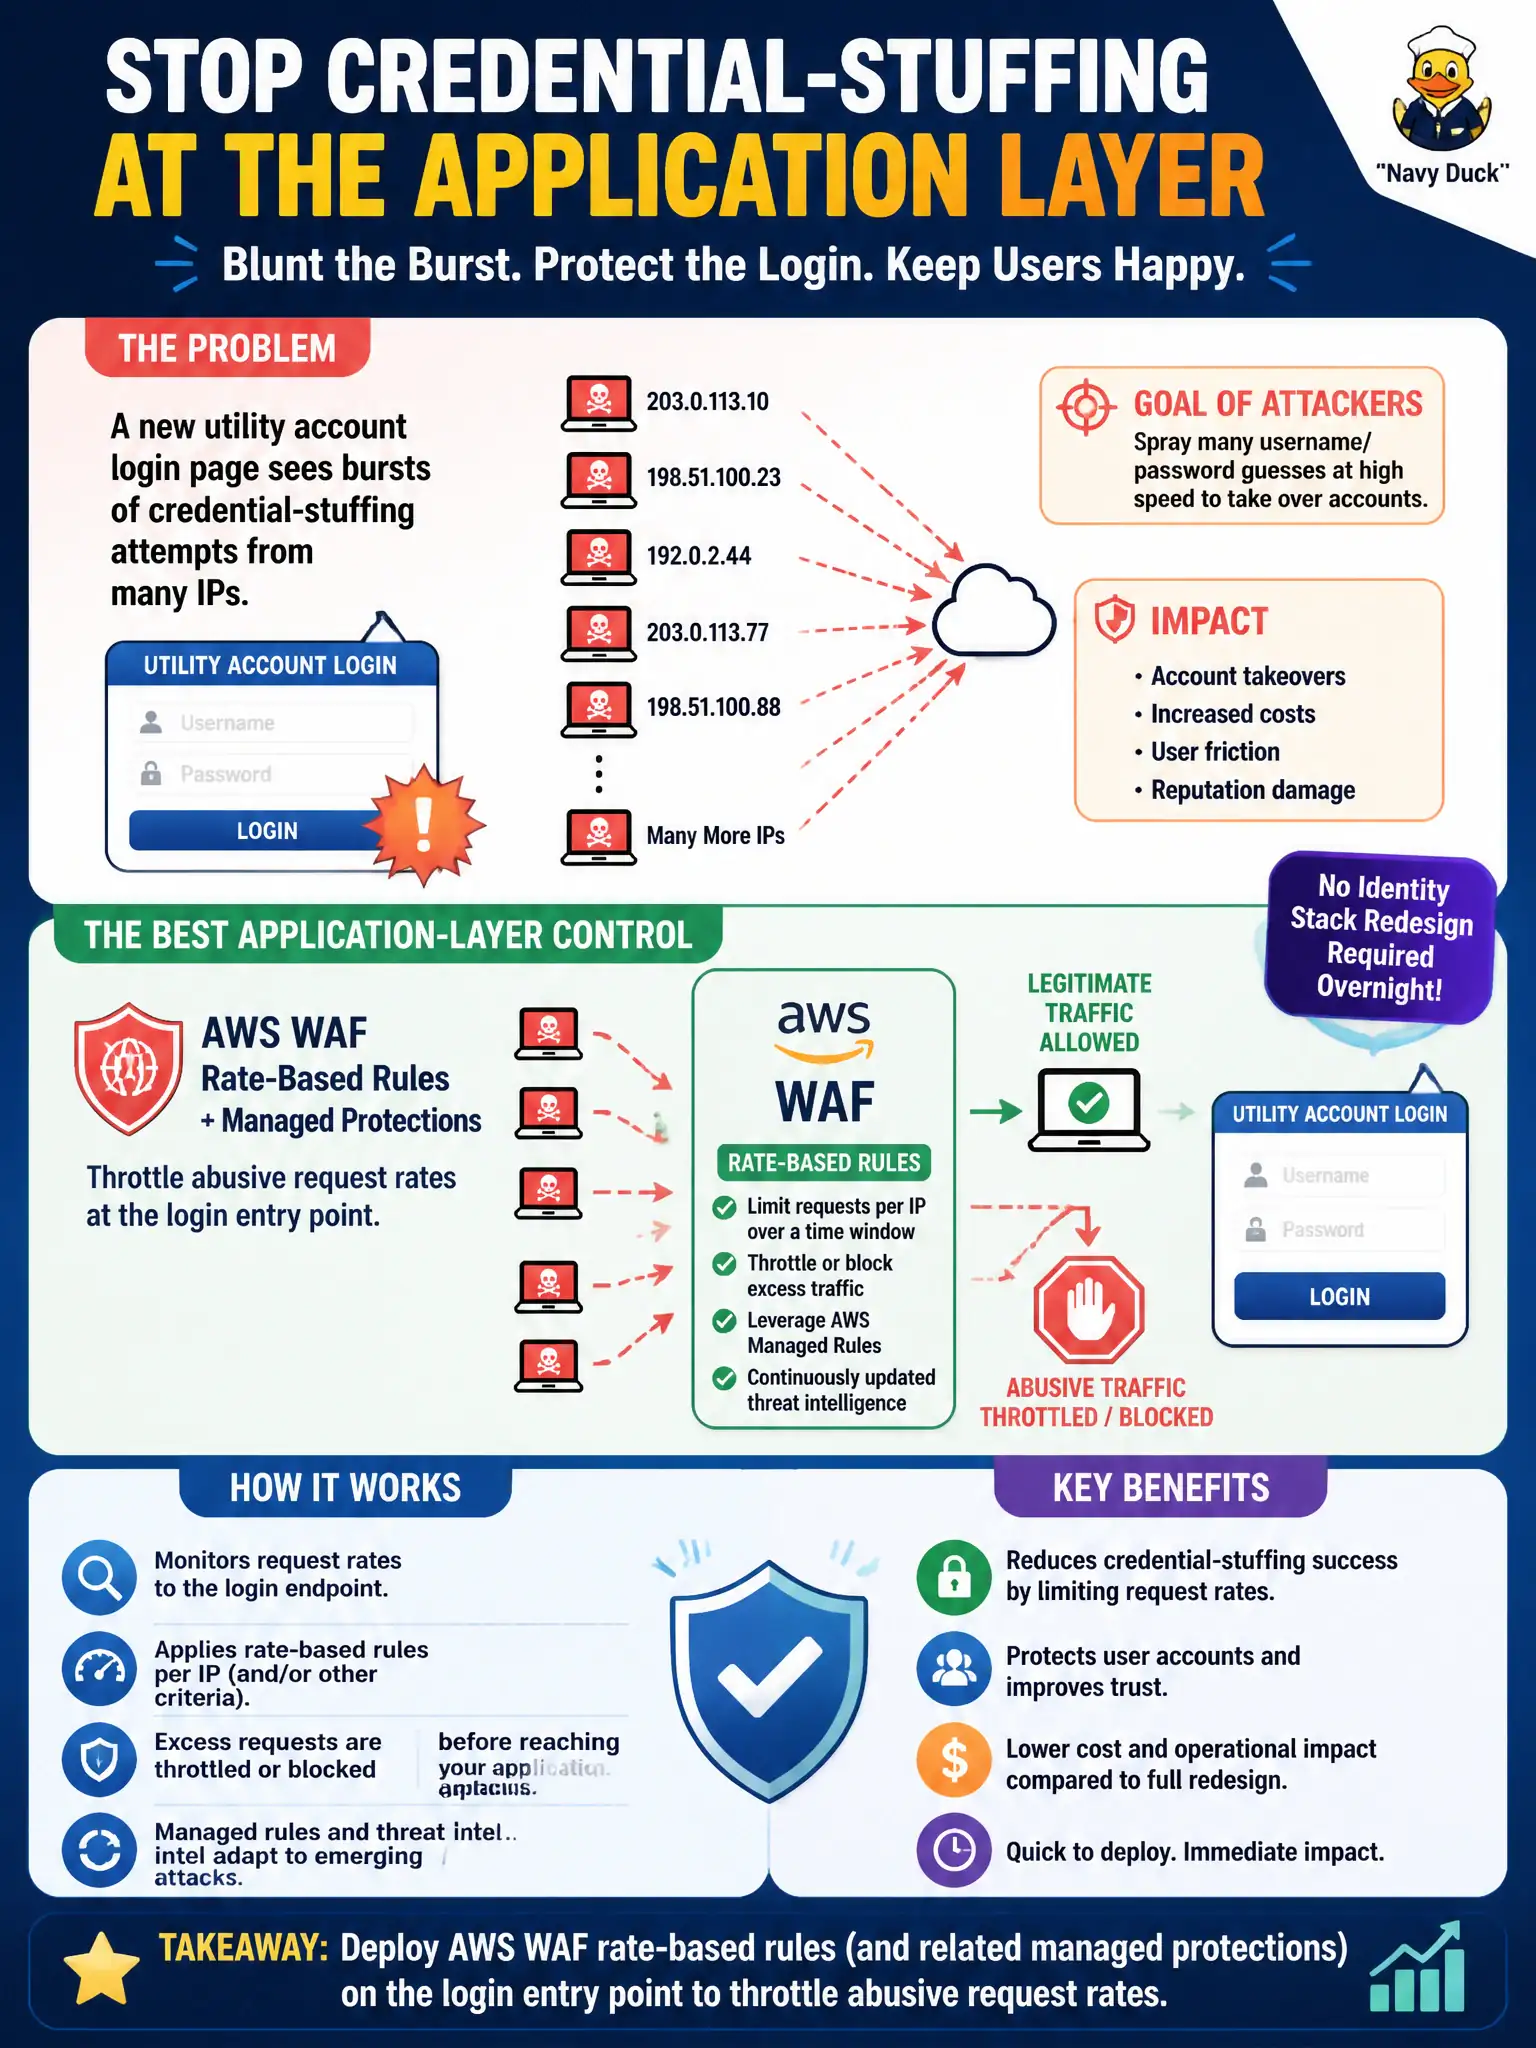
A new utility account login page sees bursts of credential-stuffing attempts from many IPs. Which application-layer control best blunts that pattern without redesigning the whole identity stack overnight?
Select an answer to reveal the explanation.
Short Explanation
Credential stuffing is a firehose of guessed passwords. A WAF rate-based rule is the valve that slows the spray while you keep real customers moving.
Full Explanation
Credential-stuffing bursts against a utility account login page are an application-layer abuse pattern best blunted with rate controls at the edge or login entry point. Deploying AWS WAF rate-based rules and related managed protections throttles abusive request rates without an overnight identity redesign. Removing authentication entirely so stuffing has nothing to target destroys account security. Publishing the login form as an unauthenticated FTP directory listing is unrelated and insecure. Moving the login page to an obscure URL and assuming attackers will not find it is security through obscurity. Exam caveat: rate rules need thresholds that spare legitimate peak login storms such as outage-driven account checks; tune with metrics and consider bot control features where licensed. Operational check: place WAF in front of the login, simulate distributed stuffing from a test harness, confirm blocks or challenges, and verify legitimate users still authenticate under expected load. In municipal cloud governance, record the owners, success metrics, and rollback or restore contacts beside this technical choice so the next incident, budget review, or audit does not rediscover the decision from scratch under time pressure.