
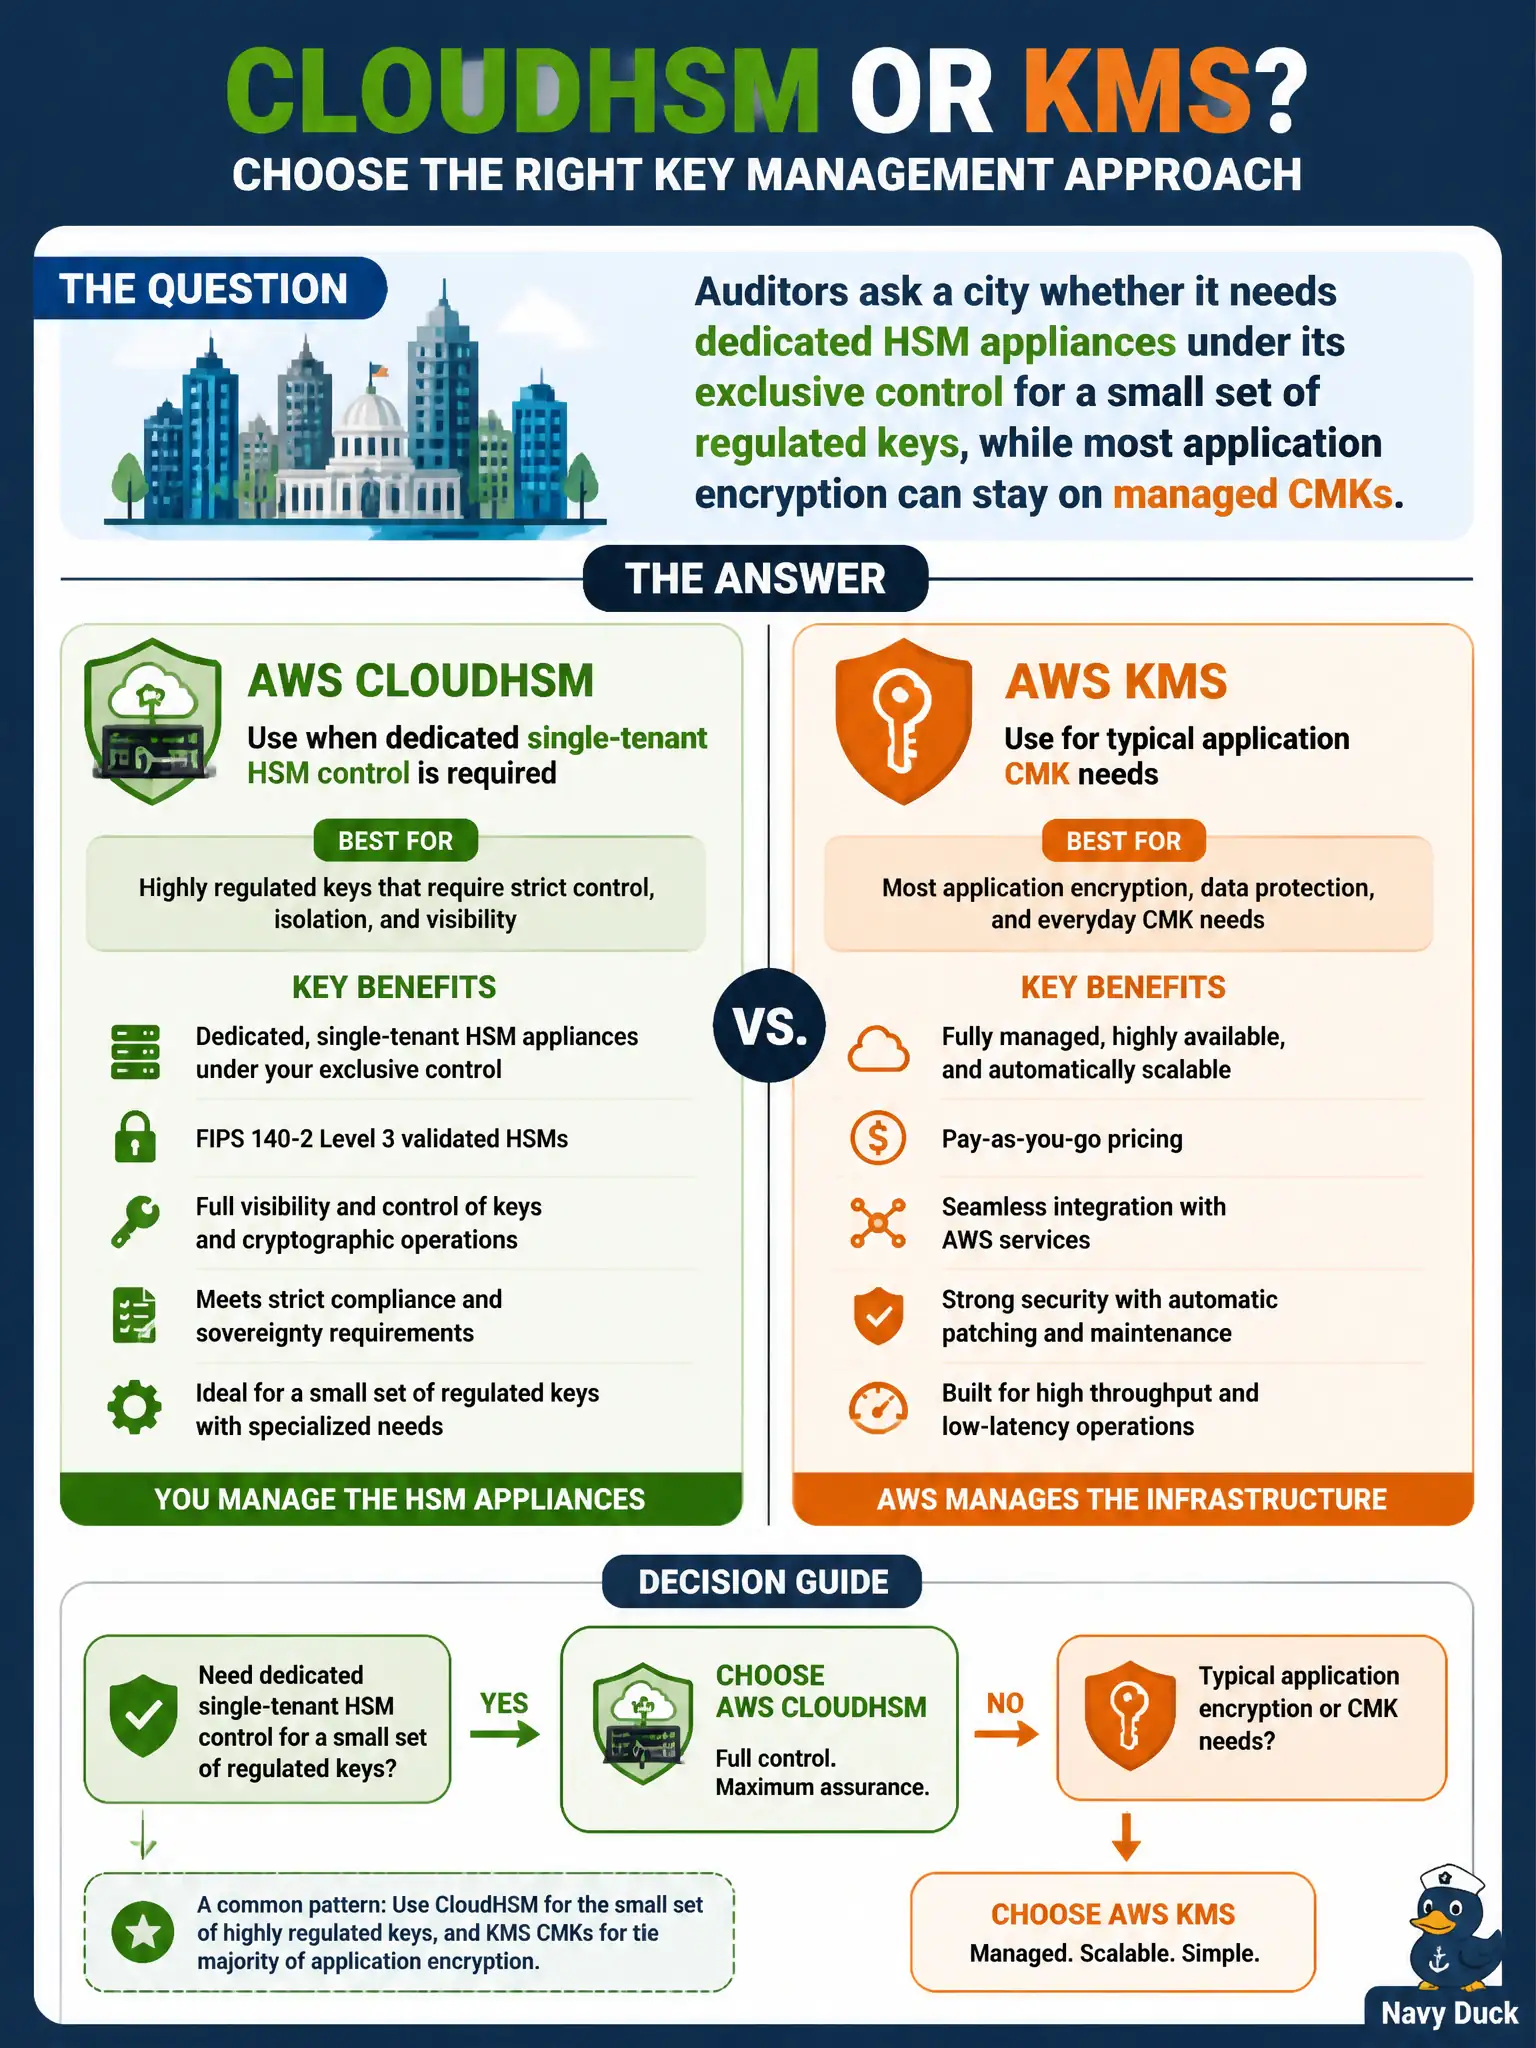
Auditors ask a city whether it needs dedicated HSM appliances under its exclusive control for a small set of regulated keys, while most application encryption can stay on managed CMKs. How should the architect decide between AWS CloudHSM and AWS KMS?
Select an answer to reveal the explanation.
Short Explanation
Most city apps are fine with KMS CMKs—managed keys with good policies. Reach for CloudHSM when auditors demand a dedicated HSM you effectively control, not because “HSM” sounds cooler. Dumping plaintext masters in Parameter Store is not cryptography.
Full Explanation
Architects should separate the common case from the exceptional control. AWS KMS customer managed keys cover most municipal application encryption—RDS, S3 SSE-KMS, envelope encryption in apps—with centralized policies, CloudTrail auditability, and integration across AWS services. AWS CloudHSM is appropriate when auditors or regulations demand dedicated, single-tenant HSM appliances under the city’s exclusive operational control for a small set of regulated keys. The decision is requirement-driven: use CloudHSM where dedicated HSM control is mandatory; keep KMS CMKs for typical application needs rather than forcing every workload onto HSMs.
Replacing all KMS usage with CloudHSM because “KMS cannot encrypt any AWS service data” is factually false—KMS is the native integration point for many AWS encryption features. Using only AWS-owned keys for regulated workloads and never creating CMKs removes customer key policy control and audit knobs that many civic compliance programs expect. Storing plaintext master keys in Parameter Store SecureString without KMS or HSM backing misunderstands SecureString (which uses KMS) and, if truly plaintext, abandons cryptography entirely.
Exam caveat: CloudHSM vs KMS is about tenancy and control requirements, not a blanket “HSM is always stronger so always pick it.” Operational check: document which keys truly need CloudHSM, keep application CMKs in KMS with rotation and key policies, and validate that service integrations still encrypt via KMS where CloudHSM is not required.