
A county shares a Transit Gateway across departments and needs consistent firewall policies in many accounts and VPCs. Which service helps centrally manage those firewall policies?
Select an answer to reveal the explanation.
Short Explanation
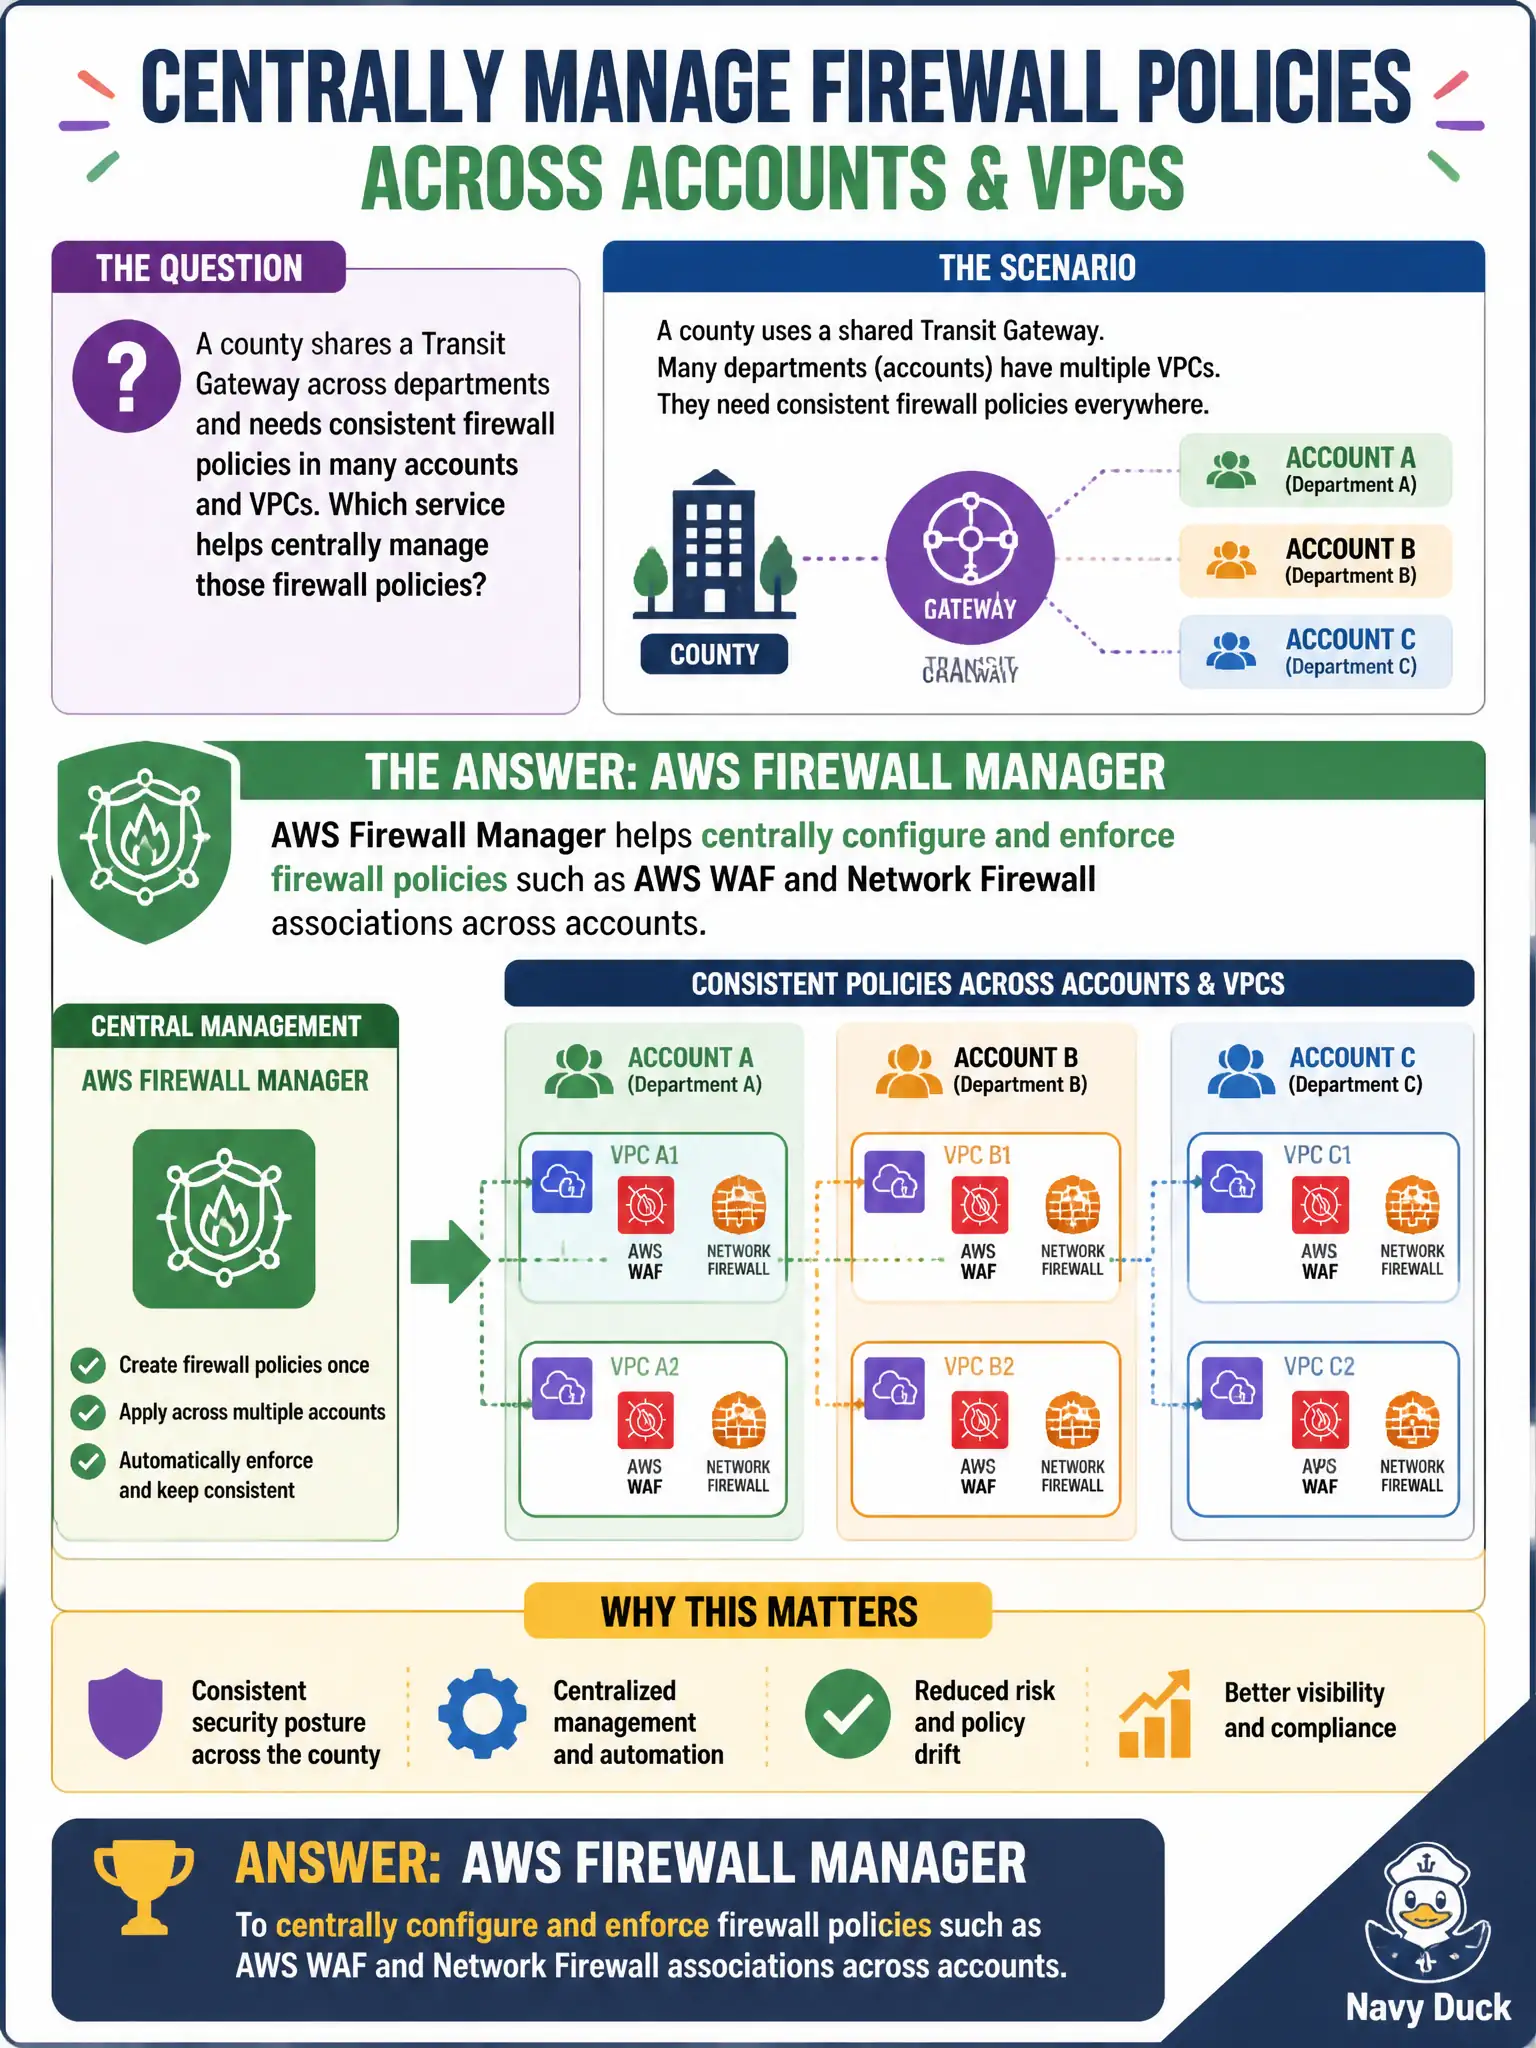
When every department shares the transit highway, you want one policy office—not seventeen hand-tuned gates. Firewall Manager centrally rolls out WAF and Network Firewall policies across accounts. Personalize, QuickSight, and License Manager are not that central firewall policy plane.
Full Explanation
A county that shares a Transit Gateway across departments and needs consistent firewall policies in many accounts and VPCs should use AWS Firewall Manager to centrally configure and enforce policies such as AWS WAF and Network Firewall associations across accounts. Firewall Manager, working with AWS Organizations, reduces configuration drift when every department attaches to the same transit “highway” but must still meet common inspection baselines.
Amazon Personalize recommending random security group rules per department fails because Personalize is a recommendation ML service, not a multi-account firewall policy engine. Amazon QuickSight dashboards alone pushing firewall rule changes fails conceptually: dashboards visualize data; they do not authoritatively enforce WAF or Network Firewall associations. AWS License Manager allocating Network Firewall rule group licenses to citizens fails because License Manager tracks software licenses, not central firewall policy enforcement across accounts.
Exam caveat: Firewall Manager enforces associated policy types you configure—it does not magically secure Transit Gateway routing mistakes or replace per-VPC security groups for micro-segmentation. Operational check: designate a Firewall Manager administrator account, define WAF/Network Firewall policies with automatic remediation, verify new department accounts receive associations, and audit noncompliant resources weekly.