
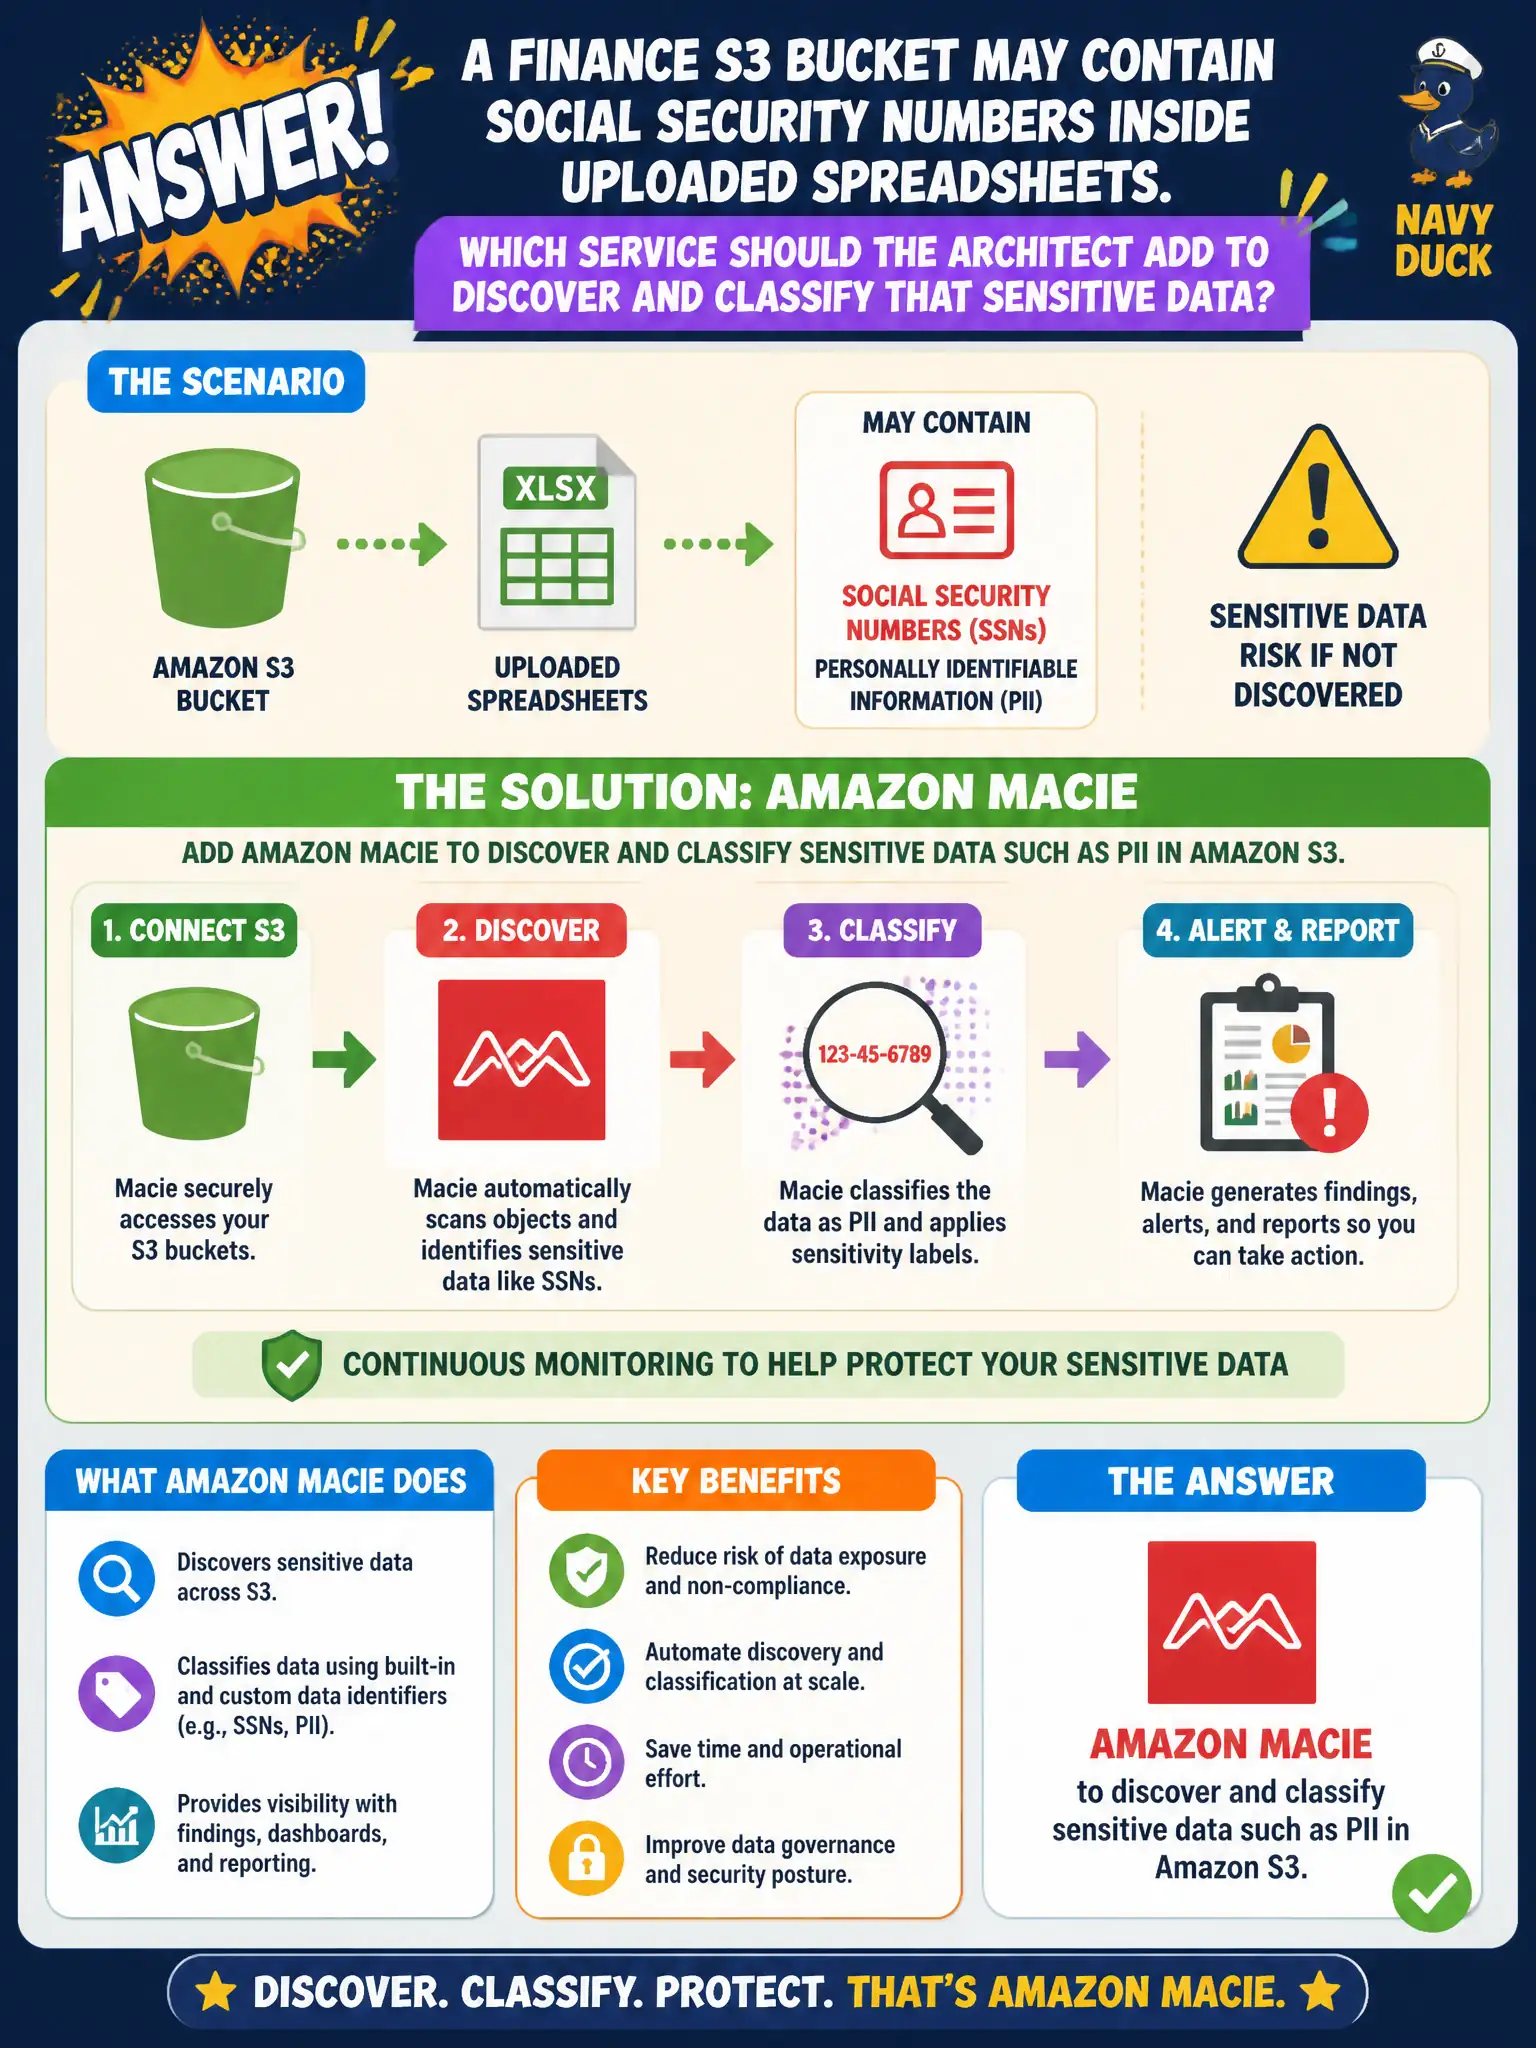
A finance S3 bucket may contain Social Security numbers inside uploaded spreadsheets. Which service should the architect add to discover and classify that sensitive data?
Select an answer to reveal the explanation.
Short Explanation
Macie is the records clerk who actually opens the boxes and flags SSNs—not the speaker that announces filenames. Point Macie at the finance bucket to discover and classify sensitive data in S3. Polly, Snowcone shuttles, and one desktop per spreadsheet miss that discovery job.
Full Explanation
When a finance S3 bucket may contain Social Security numbers inside uploaded spreadsheets, Amazon Macie is the service that discovers and classifies sensitive data such as PII in Amazon S3. Macie uses managed and custom sensitive-data detection to identify SSNs and related identifiers so the township can prioritize encryption, access tightening, and retention decisions on civic finance uploads.
Amazon Polly reading object names aloud fails because narration of filenames neither inspects object contents nor classifies PII. Shipping every spreadsheet nightly on AWS Snowcone to an offsite vault fails conceptually: physical shipment is a transfer pattern, not continuous discovery and classification inside S3. Giving each spreadsheet its own Amazon WorkSpaces desktop fails because desktops do not scan bucket contents for sensitive data at rest and multiply unmanaged copies.
Exam caveat: Macie findings identify likely sensitive data; they do not automatically remediate bucket policies—you must still restrict access, encrypt with KMS, and fix overly broad shares. Operational check: enable Macie on the finance account/buckets, review SSN-related findings, verify only finance roles can GetObject on those prefixes, and document a response for newly discovered PII (quarantine prefix, notify privacy officer, adjust lifecycle).