
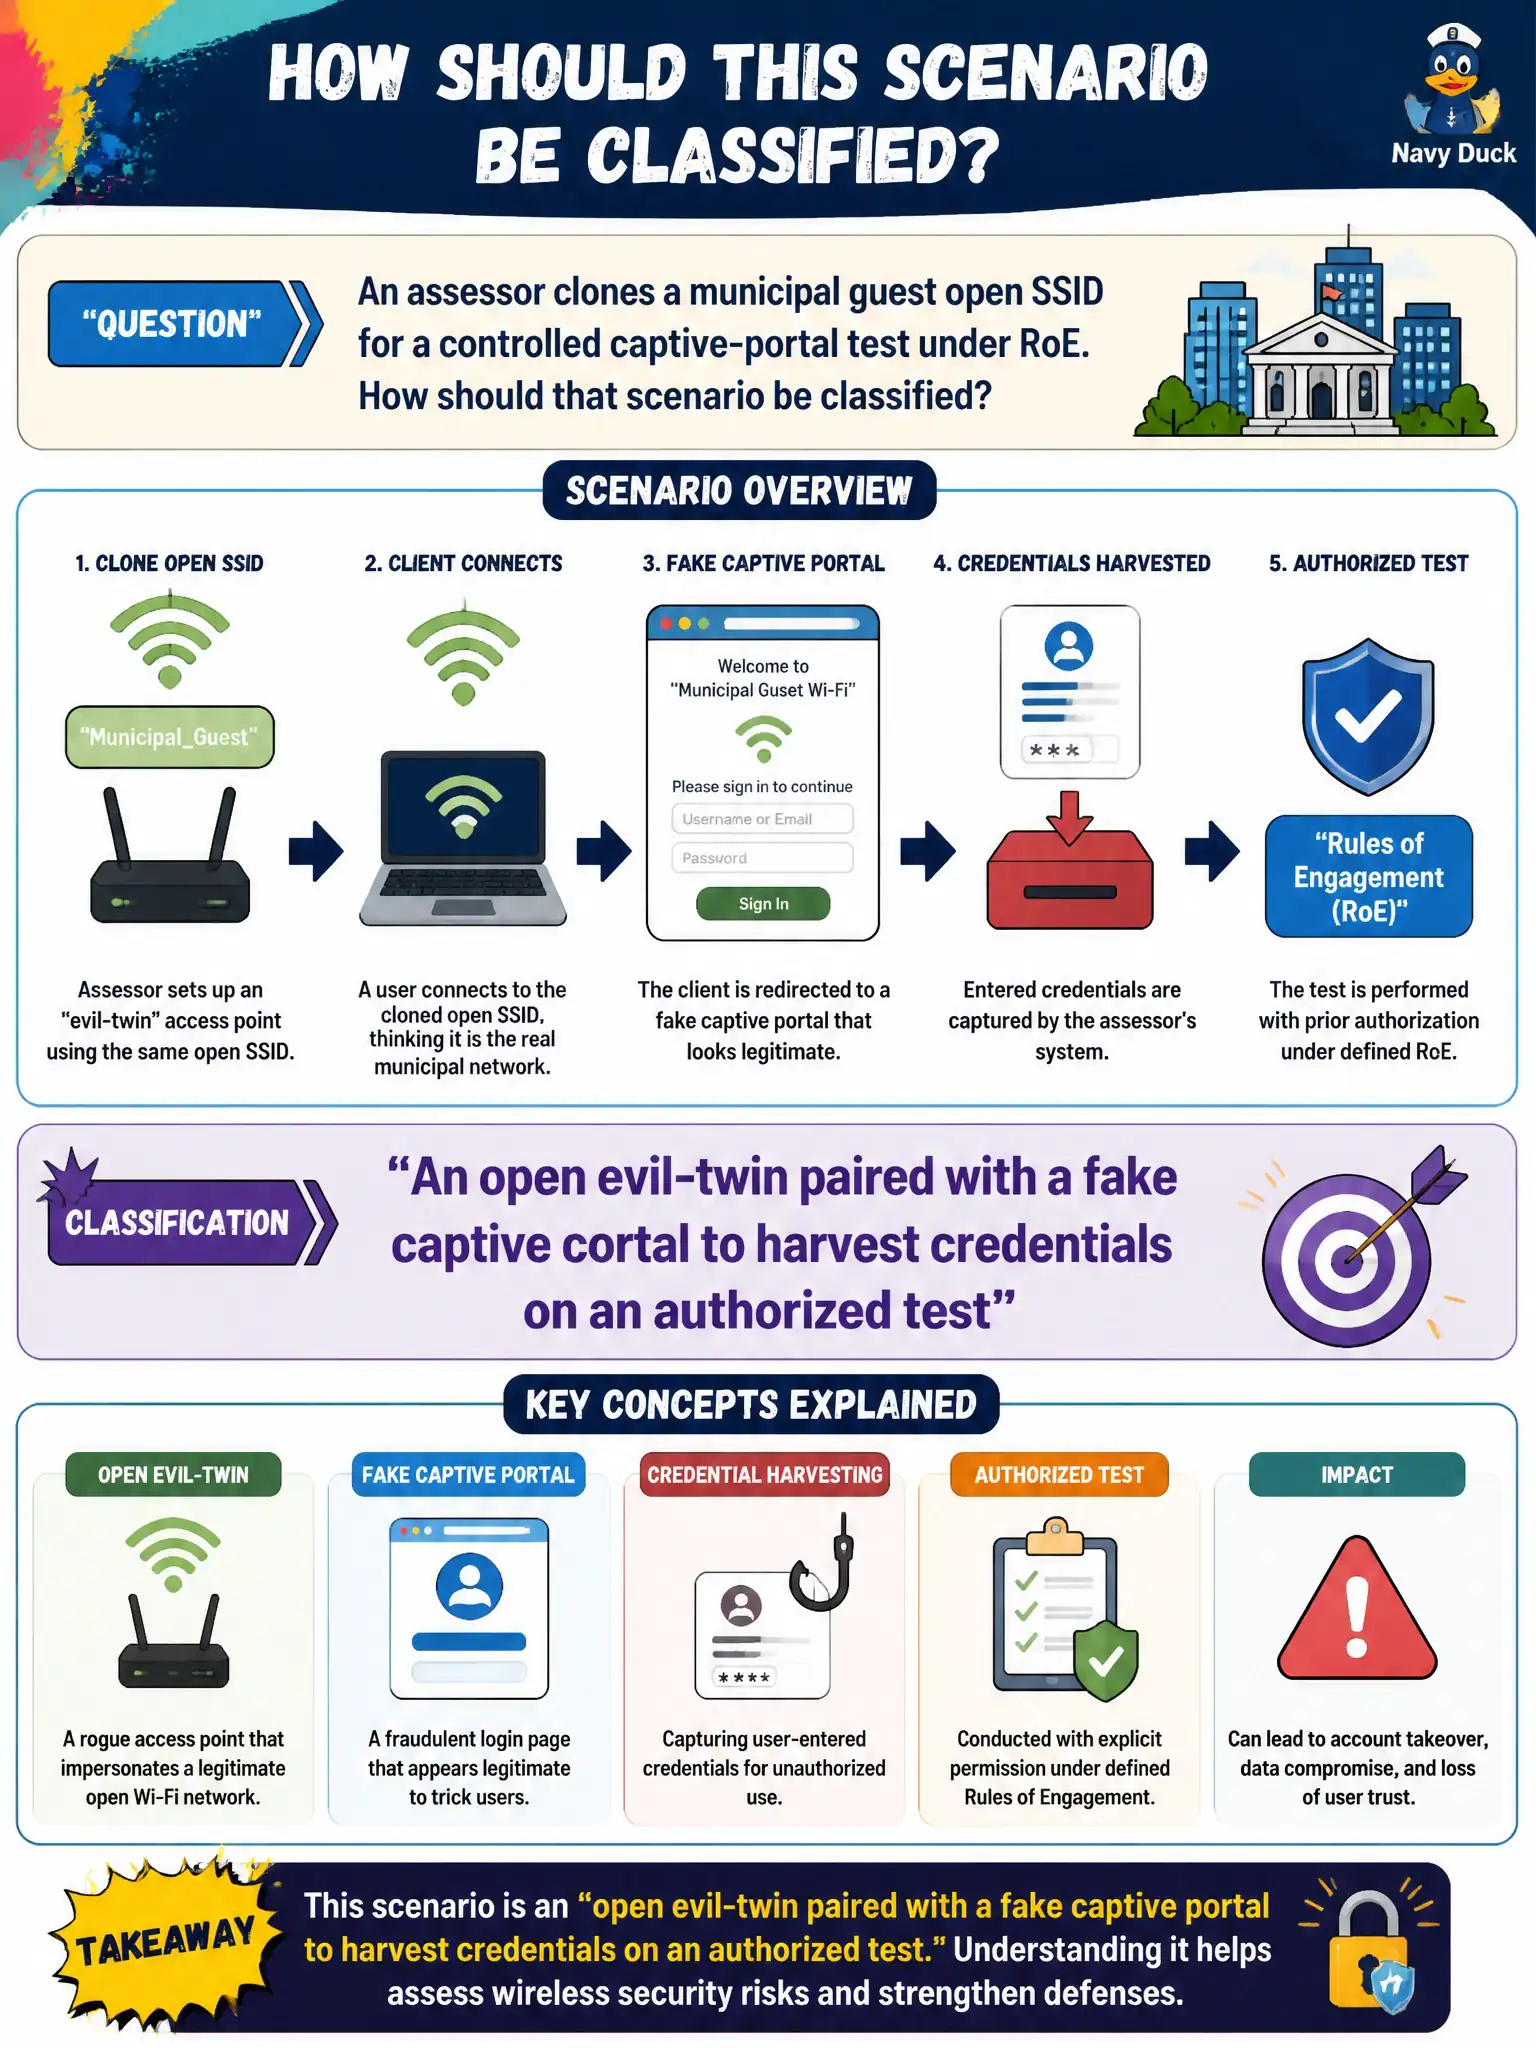
An assessor clones a municipal guest open SSID for a controlled captive-portal test under RoE. How should that scenario be classified?
Select an answer to reveal the explanation.
Short Explanation
Open guest twin plus fake 'login for Internet' page is the classic authorized captive-portal harvest class—not antenna homework, not a mythical WEP exam mandate, and not a PoE cable drill. You are testing whether people hand secrets to a lookalike network you control.
Full Explanation
Cloning a municipal guest open SSID for a controlled captive-portal test under RoE classifies as an open evil-twin paired with a fake captive portal to harvest credentials on an authorized test. That is a Domain 6 technique class for awareness of credential harvest risk—not CWNE portfolio work, mandatory WEP cracking, or PoE technician drills. Civic purple teams must keep the portal offline to unintended victims.
'A CWNE antenna-pattern certification portfolio exercise' fails because the scenario is not a CWNE antenna-pattern certification portfolio exercise. 'A mandatory production WEP crack required by OffSec scoring rules' fails because it is not a mandatory production WEP crack required by OffSec scoring rules. 'A PoE injector troubleshooting drill for CWT technicians' fails because it is not a PoE injector troubleshooting drill for CWT technicians.
Exam caveat: open twin plus portal is disruptive—authorization, signage, and containment matter. Operational check: run the civic portal test on an approved SSID/time window, capture only consented or clearly in-scope lab credentials, screenshot the portal for evidence, and dismantle immediately. Exclude neighboring private SSIDs from any harvest tooling. In municipal wireless operations, record the rationale in the engagement notes so future assessors know which control or technique class was chosen and which failure modes the rejected options would create for city services.