
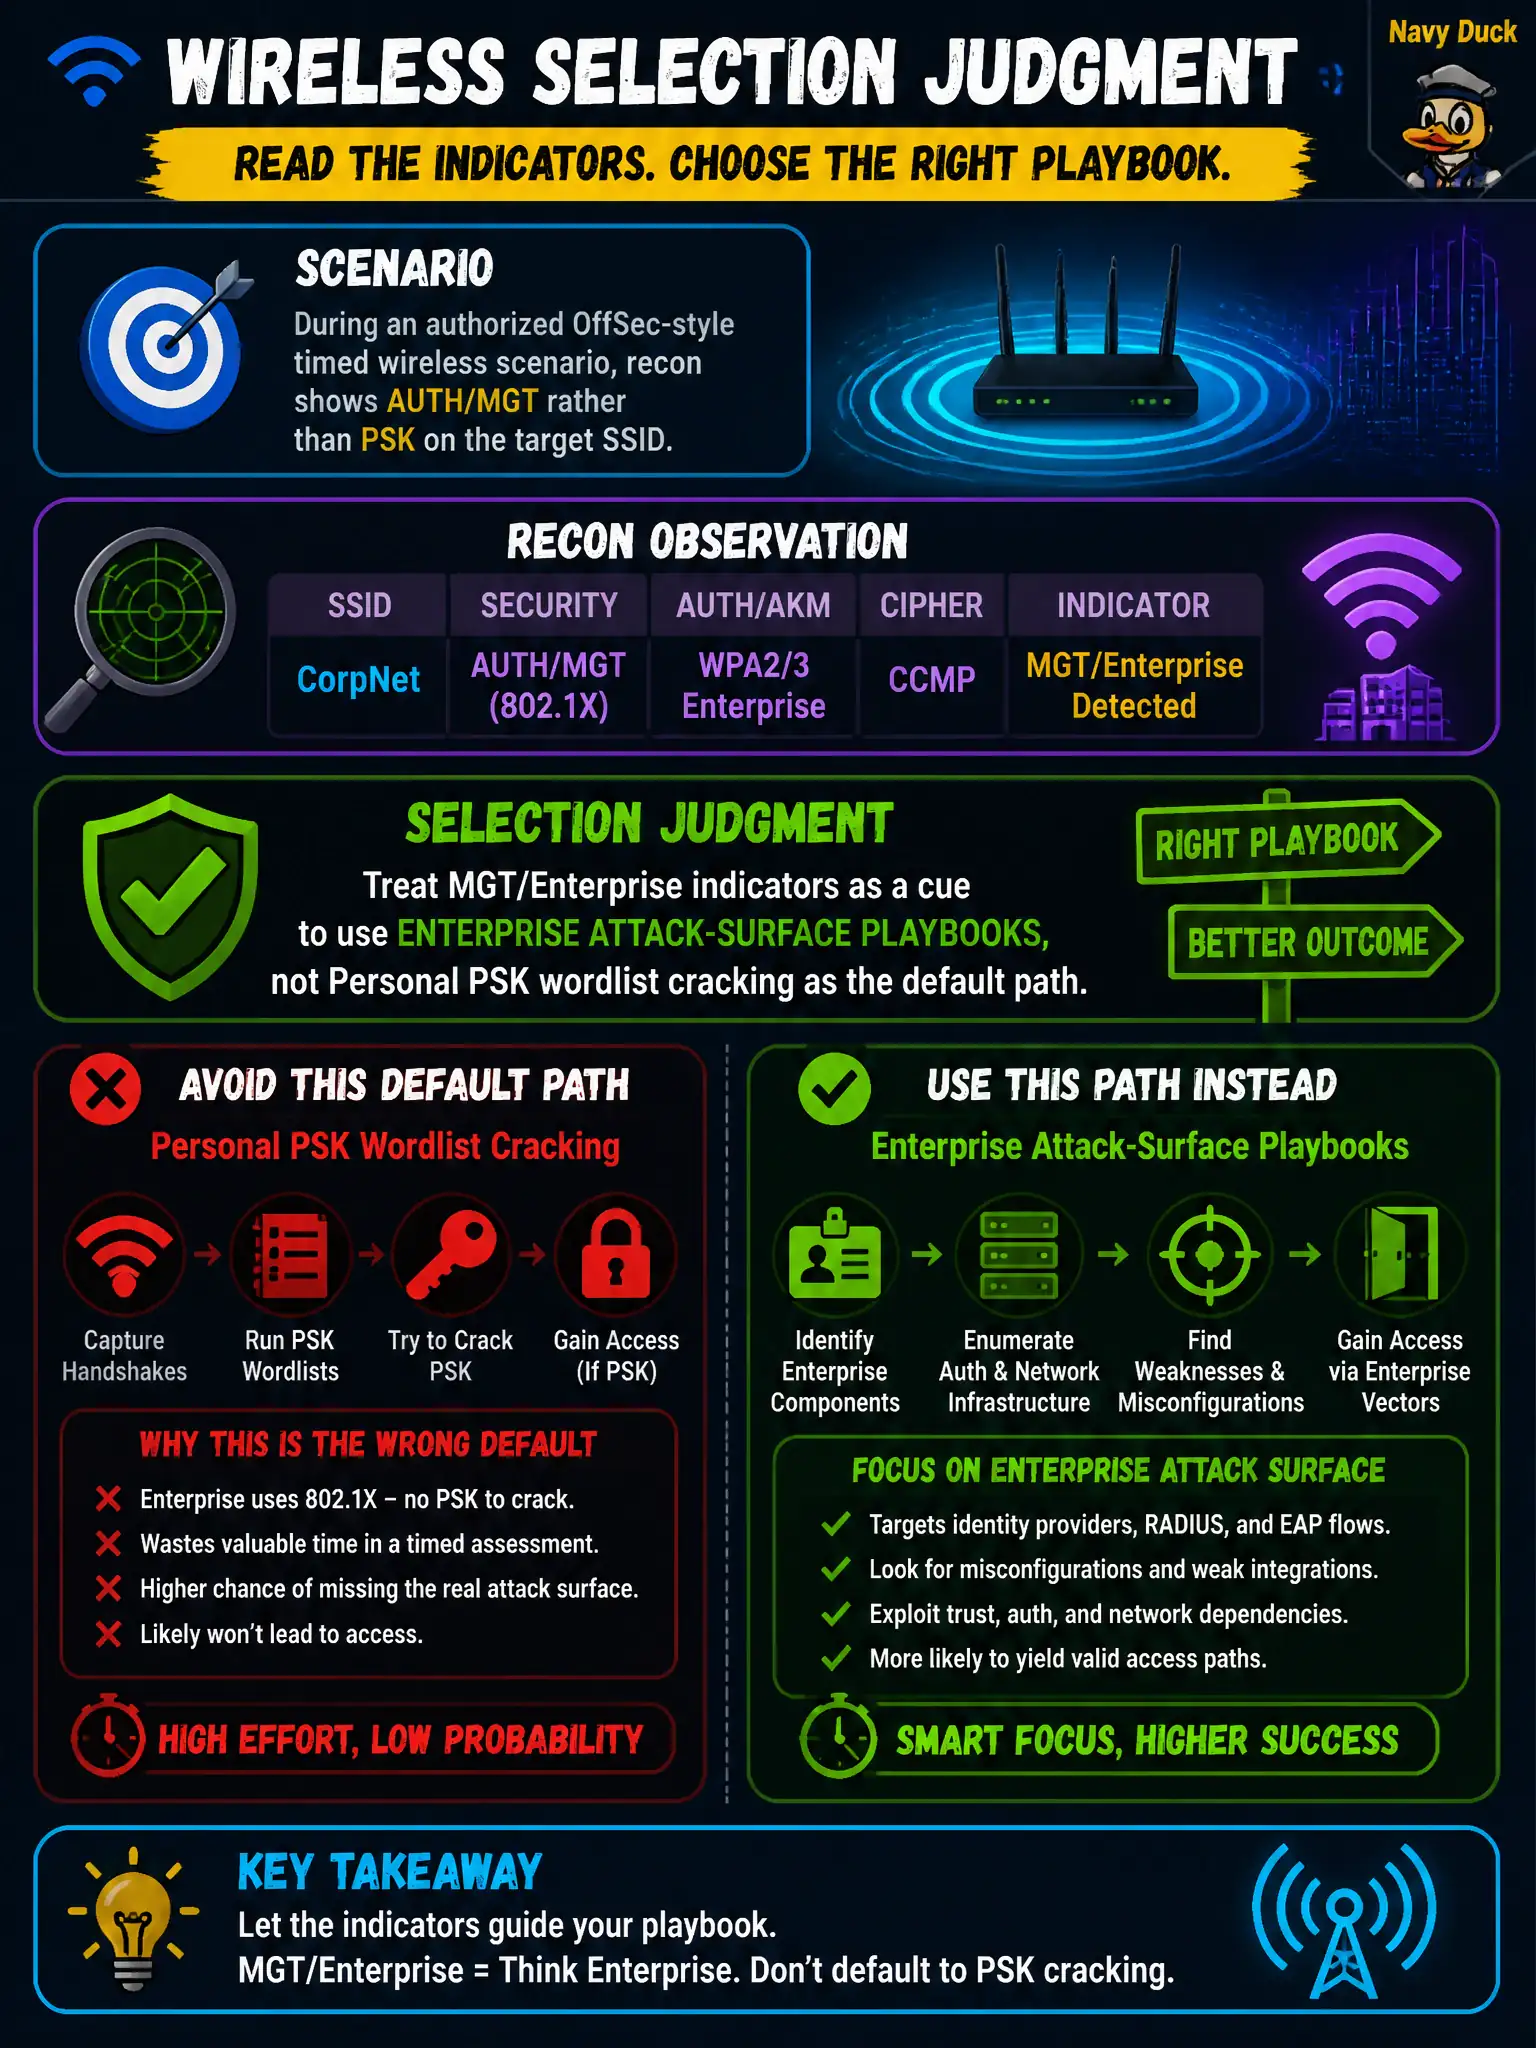
During an authorized OffSec-style timed wireless scenario, recon shows AUTH/MGT rather than PSK on the target SSID. Which selection judgment should guide the candidate?
Select an answer to reveal the explanation.
Short Explanation
If recon says MGT, do not blindly dump a PSK wordlist like it is still a home router. Match Enterprise technique classes to Enterprise clues. Wrong-mode hustle burns the clock.
Full Explanation
During an authorized OffSec-style timed wireless scenario, recon showing AUTH/MGT rather than PSK should cue the candidate to use Enterprise attack-surface playbooks, not Personal PSK wordlist cracking as the default path. Ignoring AUTH columns and always starting with the longest rockyou-derived PSK list wastes the exam clock on the wrong class. MGT does not mean the scenario is out of scope and should be skipped without documentation. Candidates must not convert the AP to WEP in the control panel before continuing. Exam caveat: reading security mode from recon is a core OSWP judgment skill and mirrors civic assessments where tool choice follows observed crypto. Operational check: on seeing MGT, switch notes to EAP and certificate themes, select the matching lab scenario techniques, and record why PSK wordlists were rejected for that target. For municipal and campus engagements, keep the finding language tied to authorized scope, name the building or SSID class affected, and state the residual risk to residents or staff if the rejected option had been chosen. Re-validate after the next change window that the selected control still matches inventory, monitoring, and RoE abort criteria used by the city wireless program.