
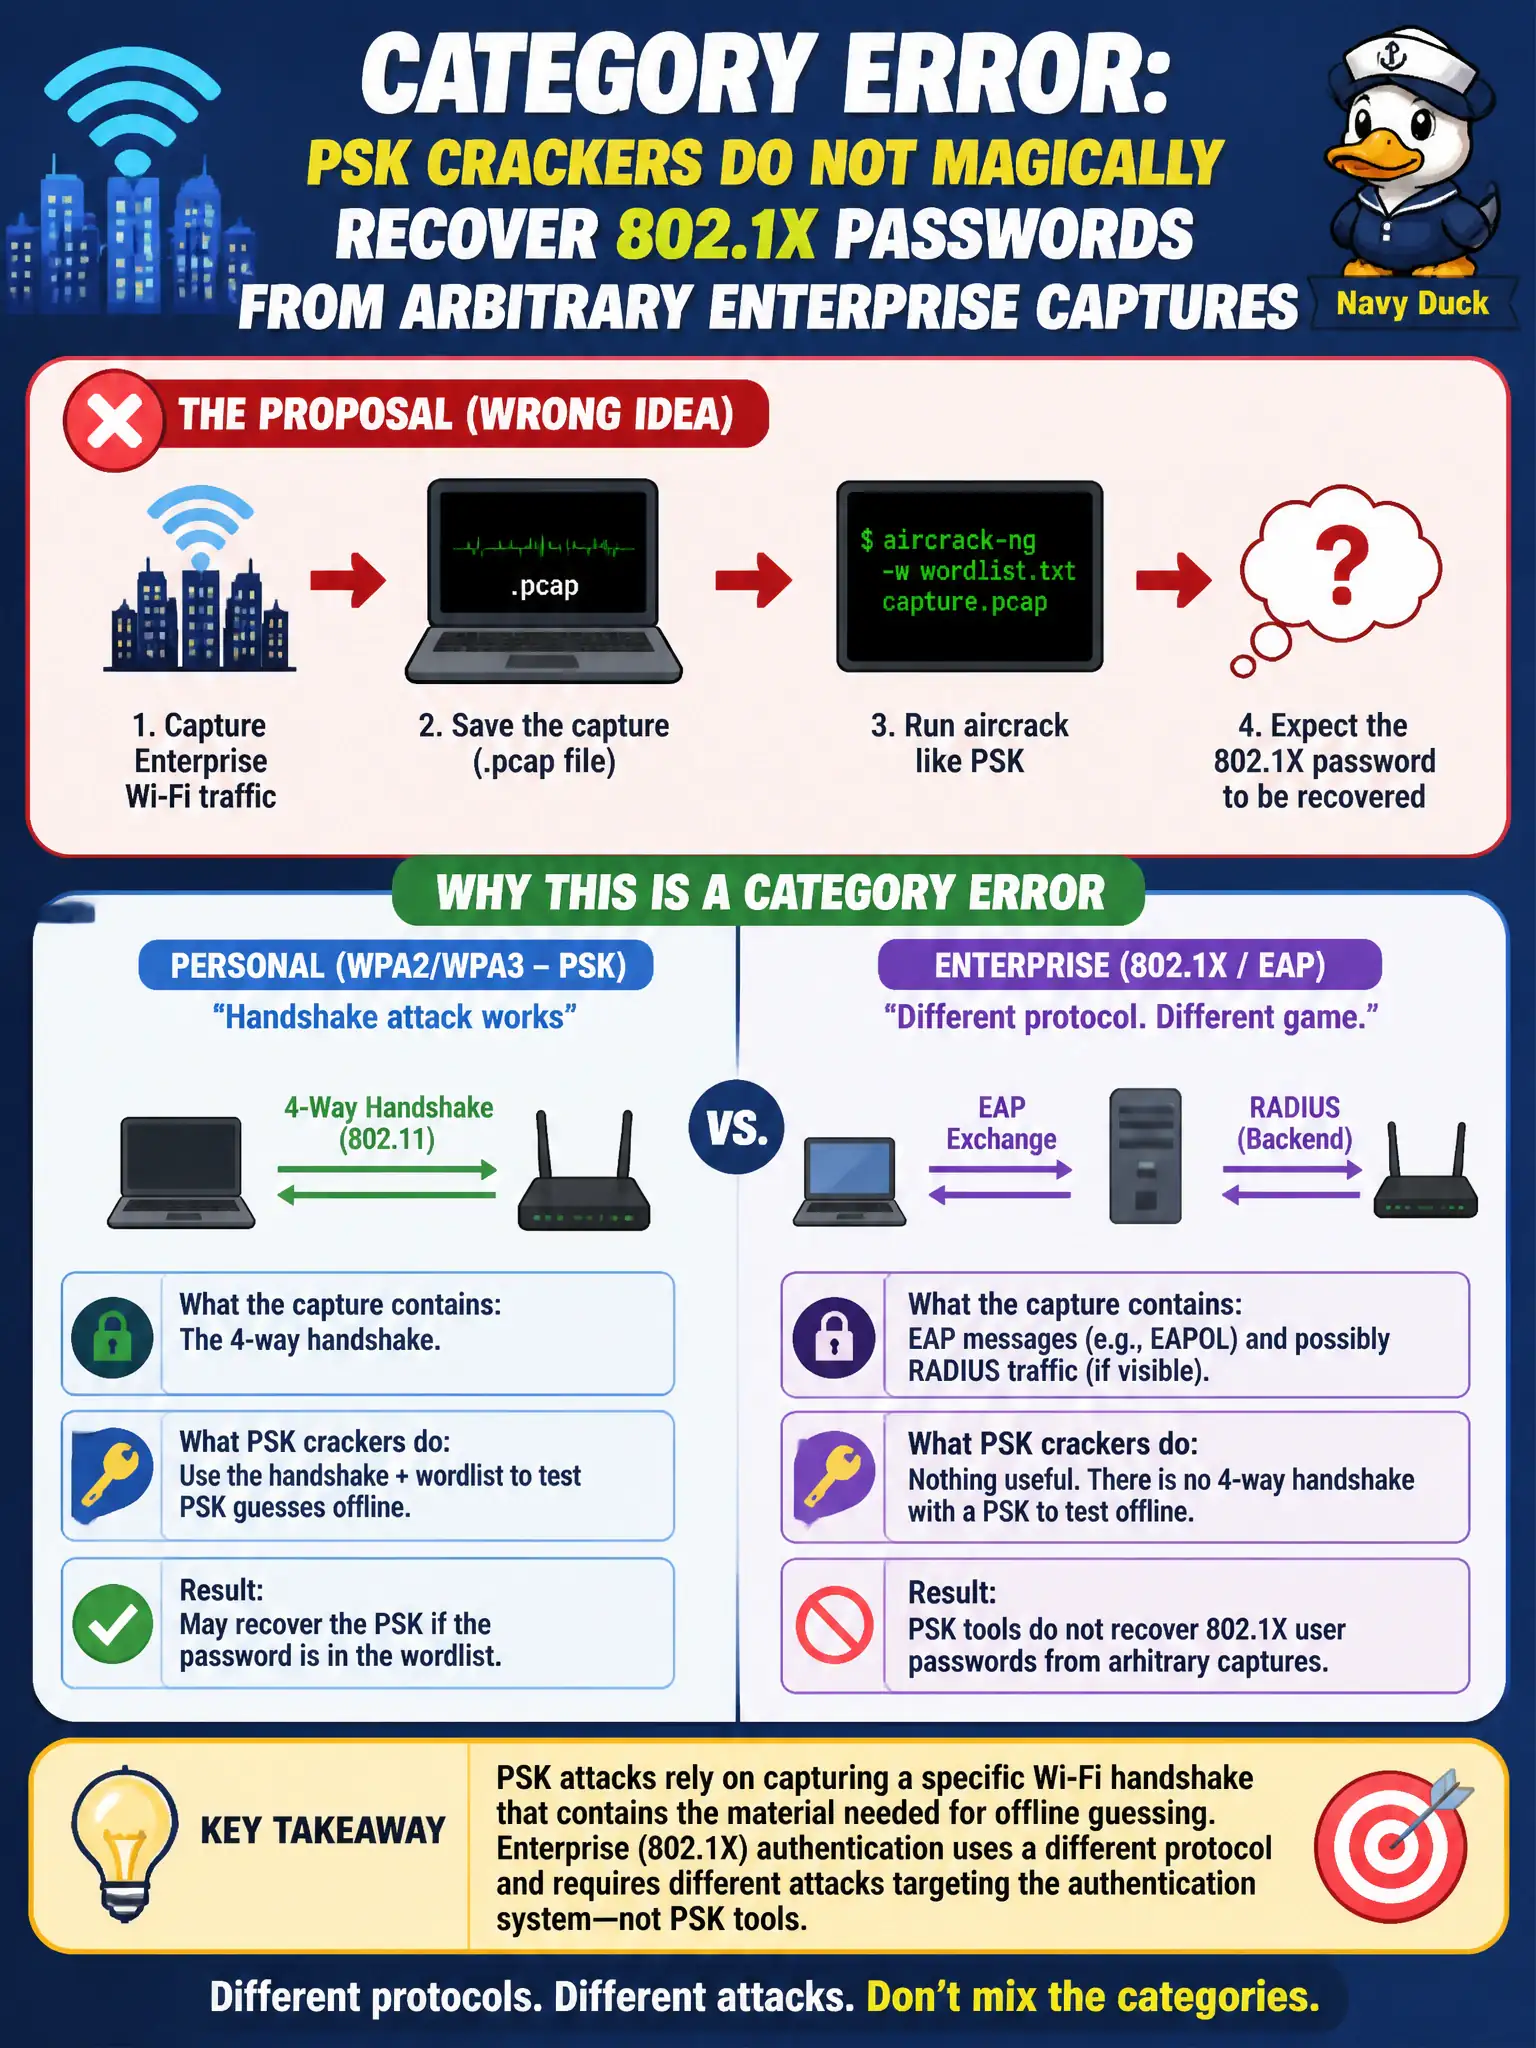
A student on a city internship proposes capturing Enterprise Wi-Fi traffic and “just running aircrack like PSK.” What category error should the mentor correct?
Select an answer to reveal the explanation.
Short Explanation
You cannot treat Enterprise like a giant shared passphrase and feed random 802.1X traffic into a PSK cracker hoping for magic. Personal and Enterprise attack classes are different animals. Match the tool class to the auth model you actually saw.
Full Explanation
A student who proposes capturing Enterprise Wi-Fi traffic and just running aircrack like PSK commits a category error: PSK crackers do not magically recover 802.1X passwords from arbitrary Enterprise captures the way Personal handshake attacks work. Enterprise captures do not always contain the PSK in cleartext beacon IEs. Aircrack is not banned in every municipal lab for authorized Personal WPA practice; the error is misapplying Personal tooling to Enterprise mode. Enterprise networks commonly use RADIUS, so claiming only WPS PIN tools apply is also wrong. Exam caveat: mode dictates method—MGT or 802.1X indicators require Enterprise playbooks, not rockyou against a nonexistent network PSK. Operational check: when civic recon shows Enterprise, mentor the intern to inventory EAP methods, certificate validation, and authorized twin or credential-material classes permitted by RoE instead of defaulting to Personal crackers. For municipal and campus engagements, keep the finding language tied to authorized scope, name the building or SSID class affected, and state the residual risk to residents or staff if the rejected option had been chosen. Re-validate after the next change window that the selected control still matches inventory, monitoring, and RoE abort criteria used by the city wireless program.