
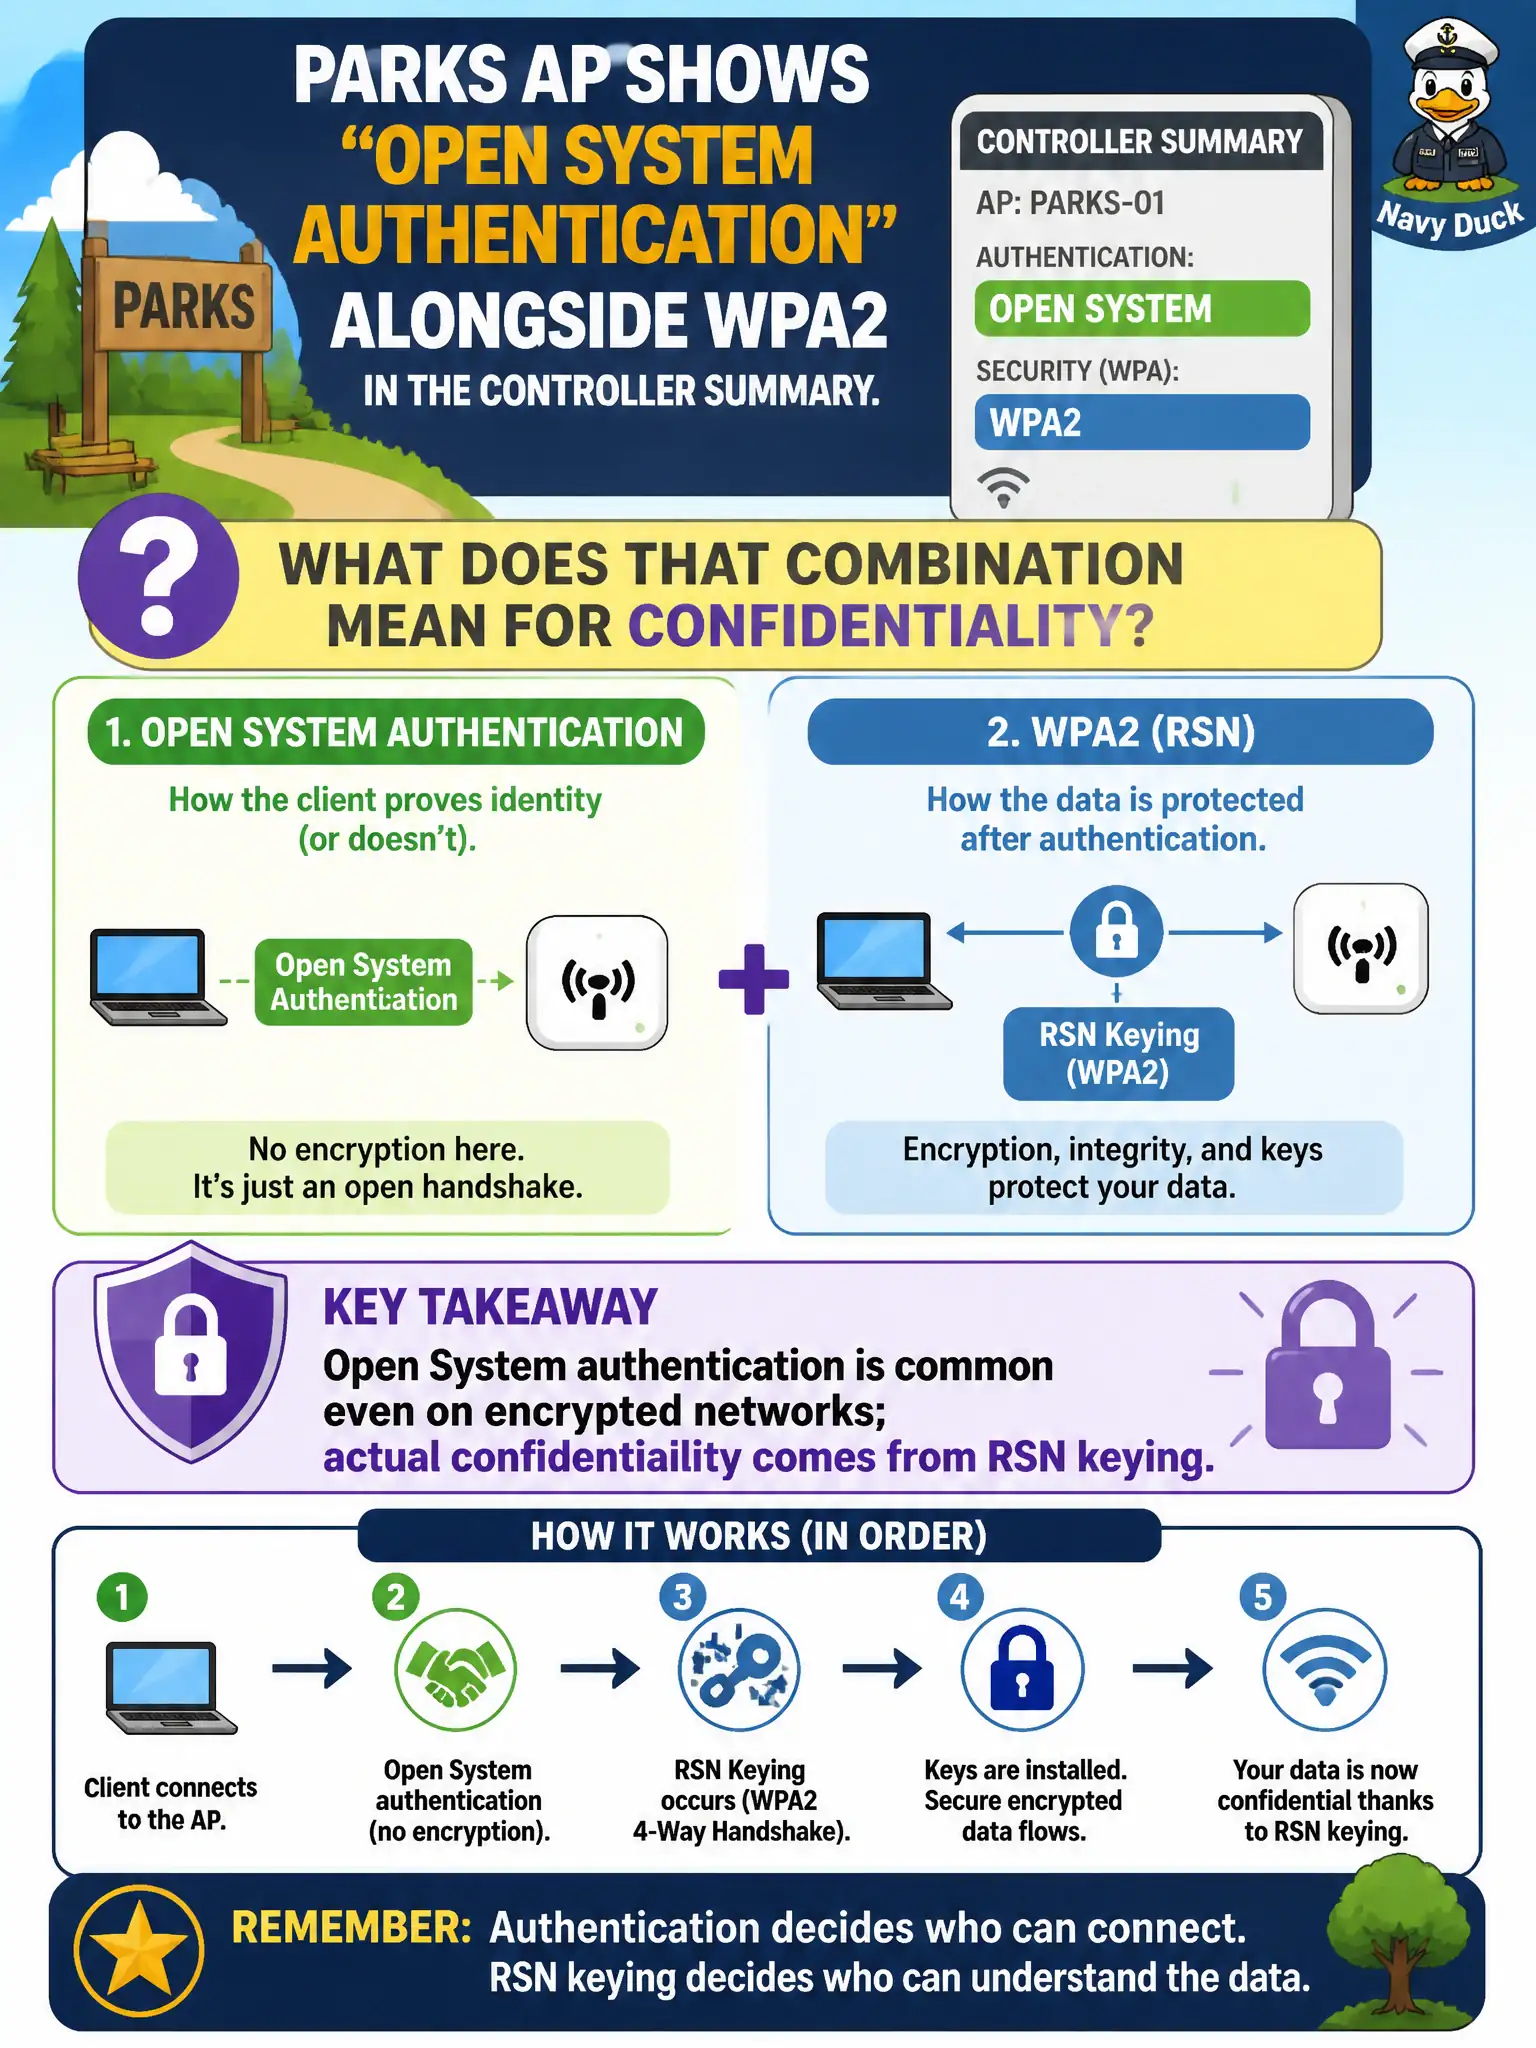
A parks AP lists 'Open System authentication' alongside WPA2 in the controller summary. What does that combination mean for confidentiality?
Select an answer to reveal the explanation.
Short Explanation
Open System here is just the polite handshake at the door—not the deadbolt. WPA2 still locks the room with RSN keys after that hello. Do not panic that the label says 'Open' when the cipher suite is doing the real secrecy work.
Full Explanation
Open System authentication is the common 802.11 authentication algorithm used even on many encrypted networks before RSN keying completes. Seeing “Open System authentication” beside WPA2 in a parks controller summary does not prove the BSS lacks encryption; confidentiality comes from RSN pairwise/group keying after association. Assessors should separate the 802.11 auth algorithm label from the presence or absence of CCMP/SAE/802.1X protections. Treating Open System authentication as proof of no encryption and captive-portal-only status over-reads the label. Saying it replaces the 4-way handshake whenever WPA2-PSK is configured is incorrect. Claiming it forces WEP shared-key mode before CCMP can start confuses historical WEP modes with modern RSN. Exam caveat: Always corroborate with RSN IE cipher/AKM fields rather than the word “Open” alone in summaries. Operational check: Cross-check the controller summary against a beacon decode for the parks BSSID and confirm whether RSN ciphers are advertised despite Open System authentication. In civic WLAN stewardship, keep authorization boundaries explicit, prefer the least disruptive technique class allowed by RoE, and record BSSID, channel, band, and security mode beside every conclusion so another assessor can reproduce the observation.