
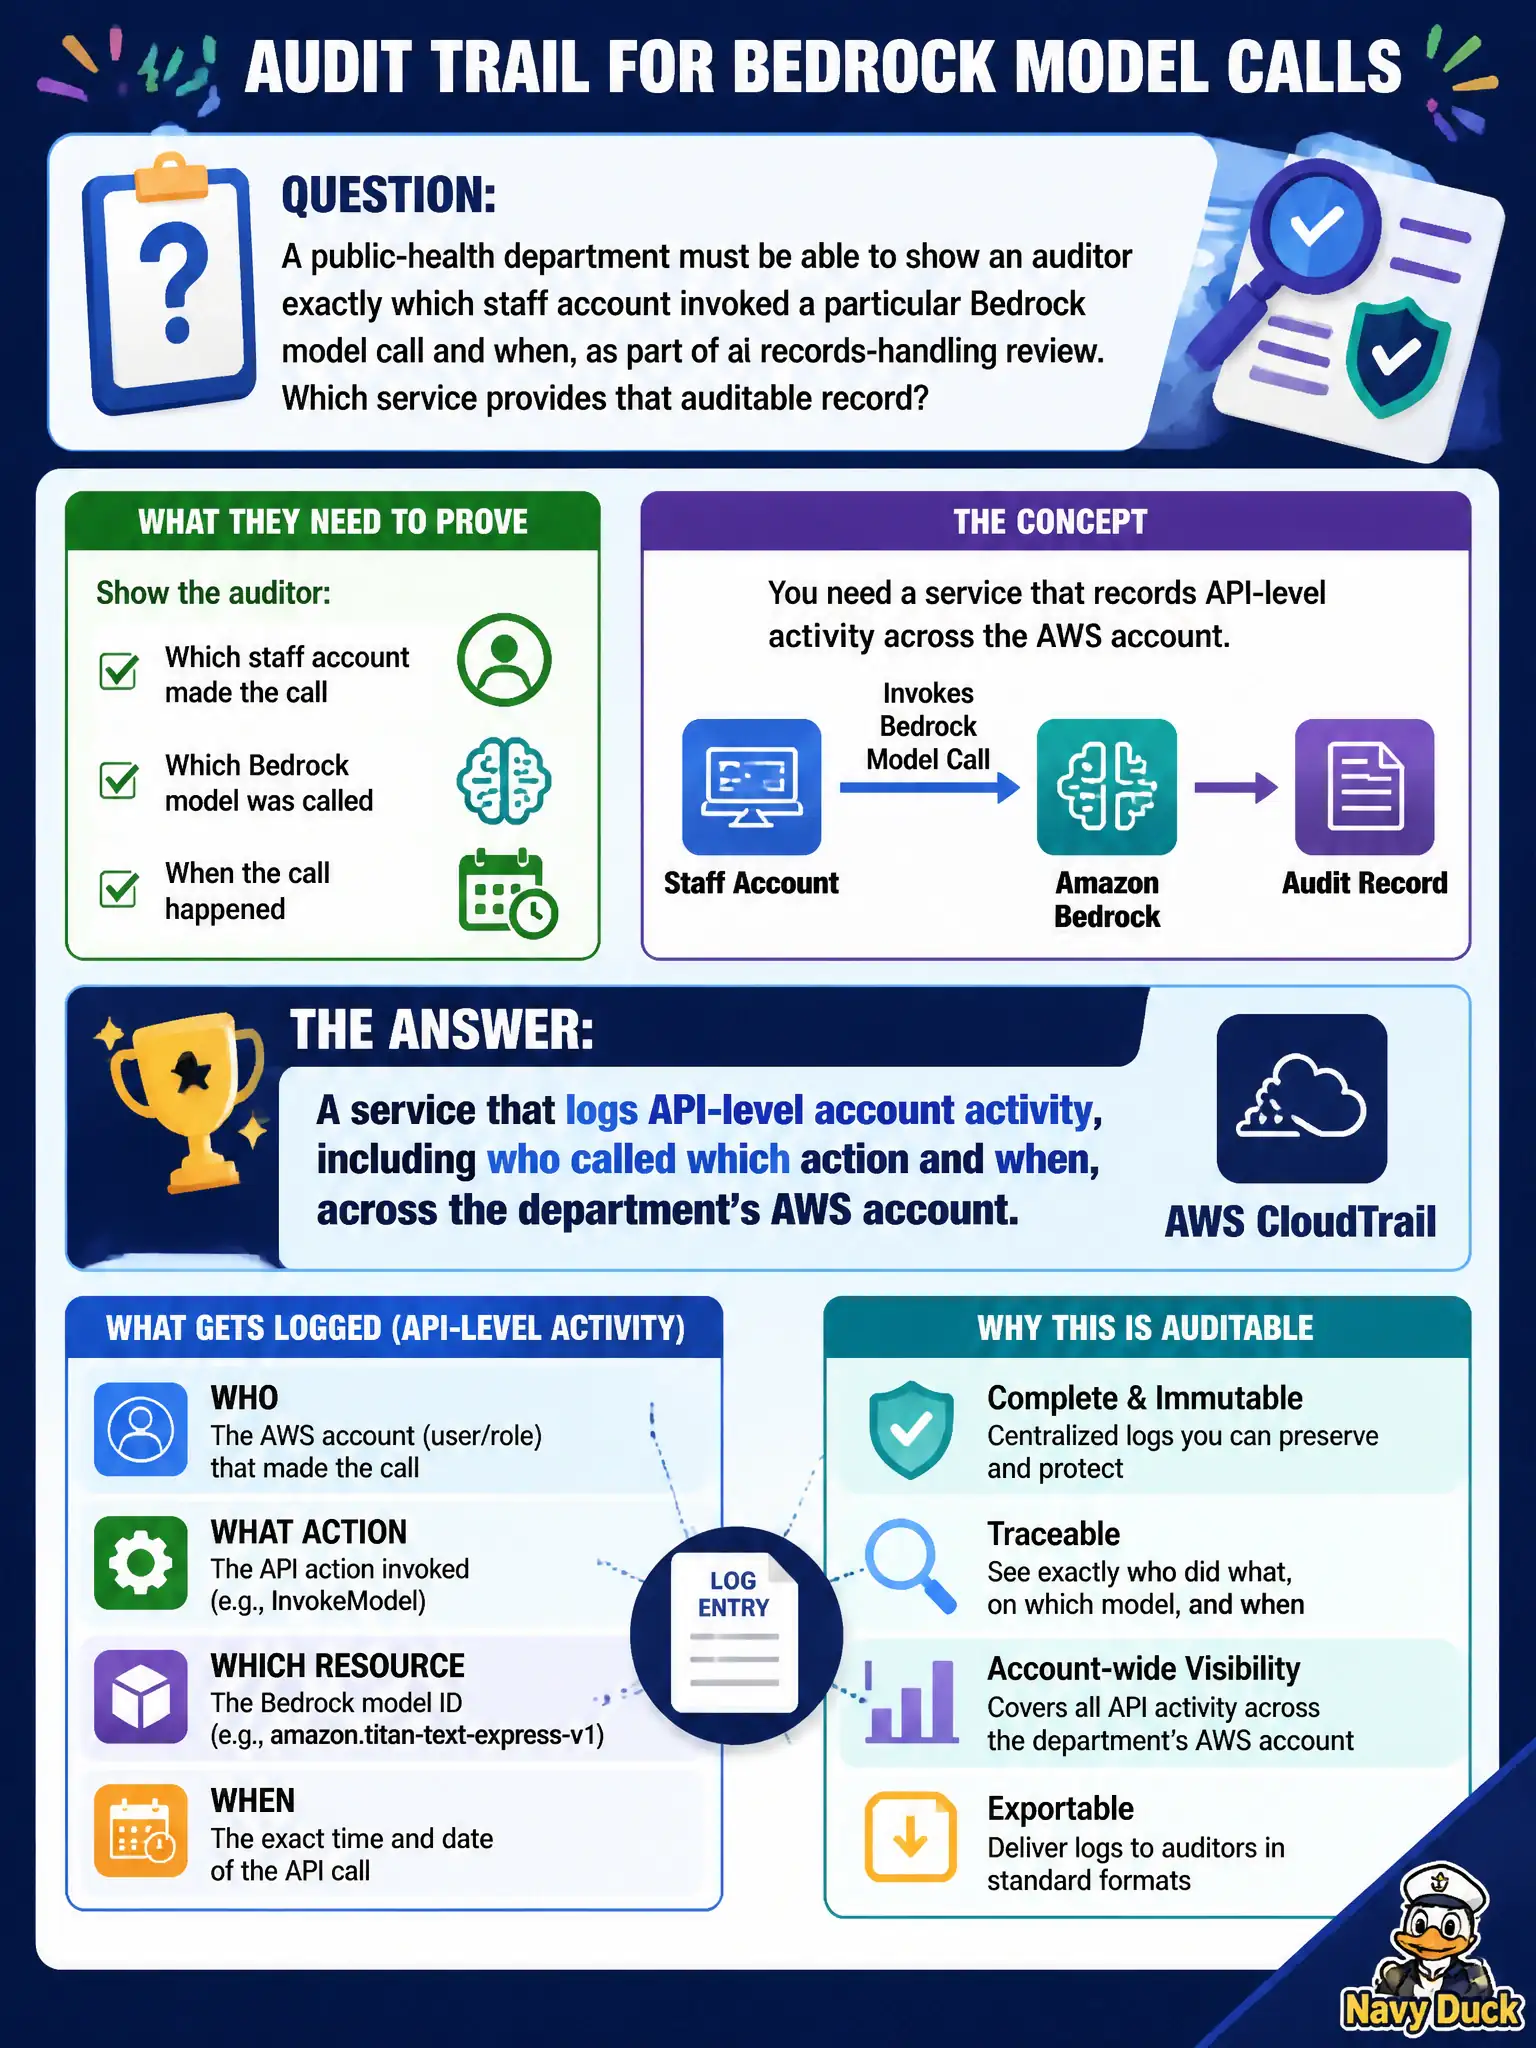
A public-health department must be able to show an auditor exactly which staff account invoked a particular Bedrock model call and when, as part of a records-handling review. Which service provides that auditable record?
Select an answer to reveal the explanation.
Short Explanation
When someone asks 'who did this, and when,' you want a receipt, not a memory. Account-activity logging is that receipt for every API call, including who invoked which model and at what timestamp. That's the record an auditor is actually asking to see.
Full Explanation
Account-level API activity logging records who called which action, on which resource, and when, across the account — which is precisely the auditable trail an external auditor needs to confirm which staff account invoked a specific Bedrock model call and at what time. A configuration-compliance service evaluates whether resources match a desired configuration state over time; it can tell you a setting drifted, but it doesn't record who made an individual API call the way activity logging does. An operational metrics dashboard shows aggregate figures like latency and error rate, which is useful for performance monitoring but carries no per-caller identity or timestamp detail. A workflow orchestration service tracks the state of pipeline steps, which is unrelated to auditing who invoked a specific model call outside that pipeline's context. Scope caveat: activity logs need to be enabled and retained for a long enough window to cover the audit period in question — confirm retention settings match the compliance requirement before relying on them. Operational check: pull a sample of the logged events for a known recent model call and confirm the caller identity and timestamp match what's expected.