
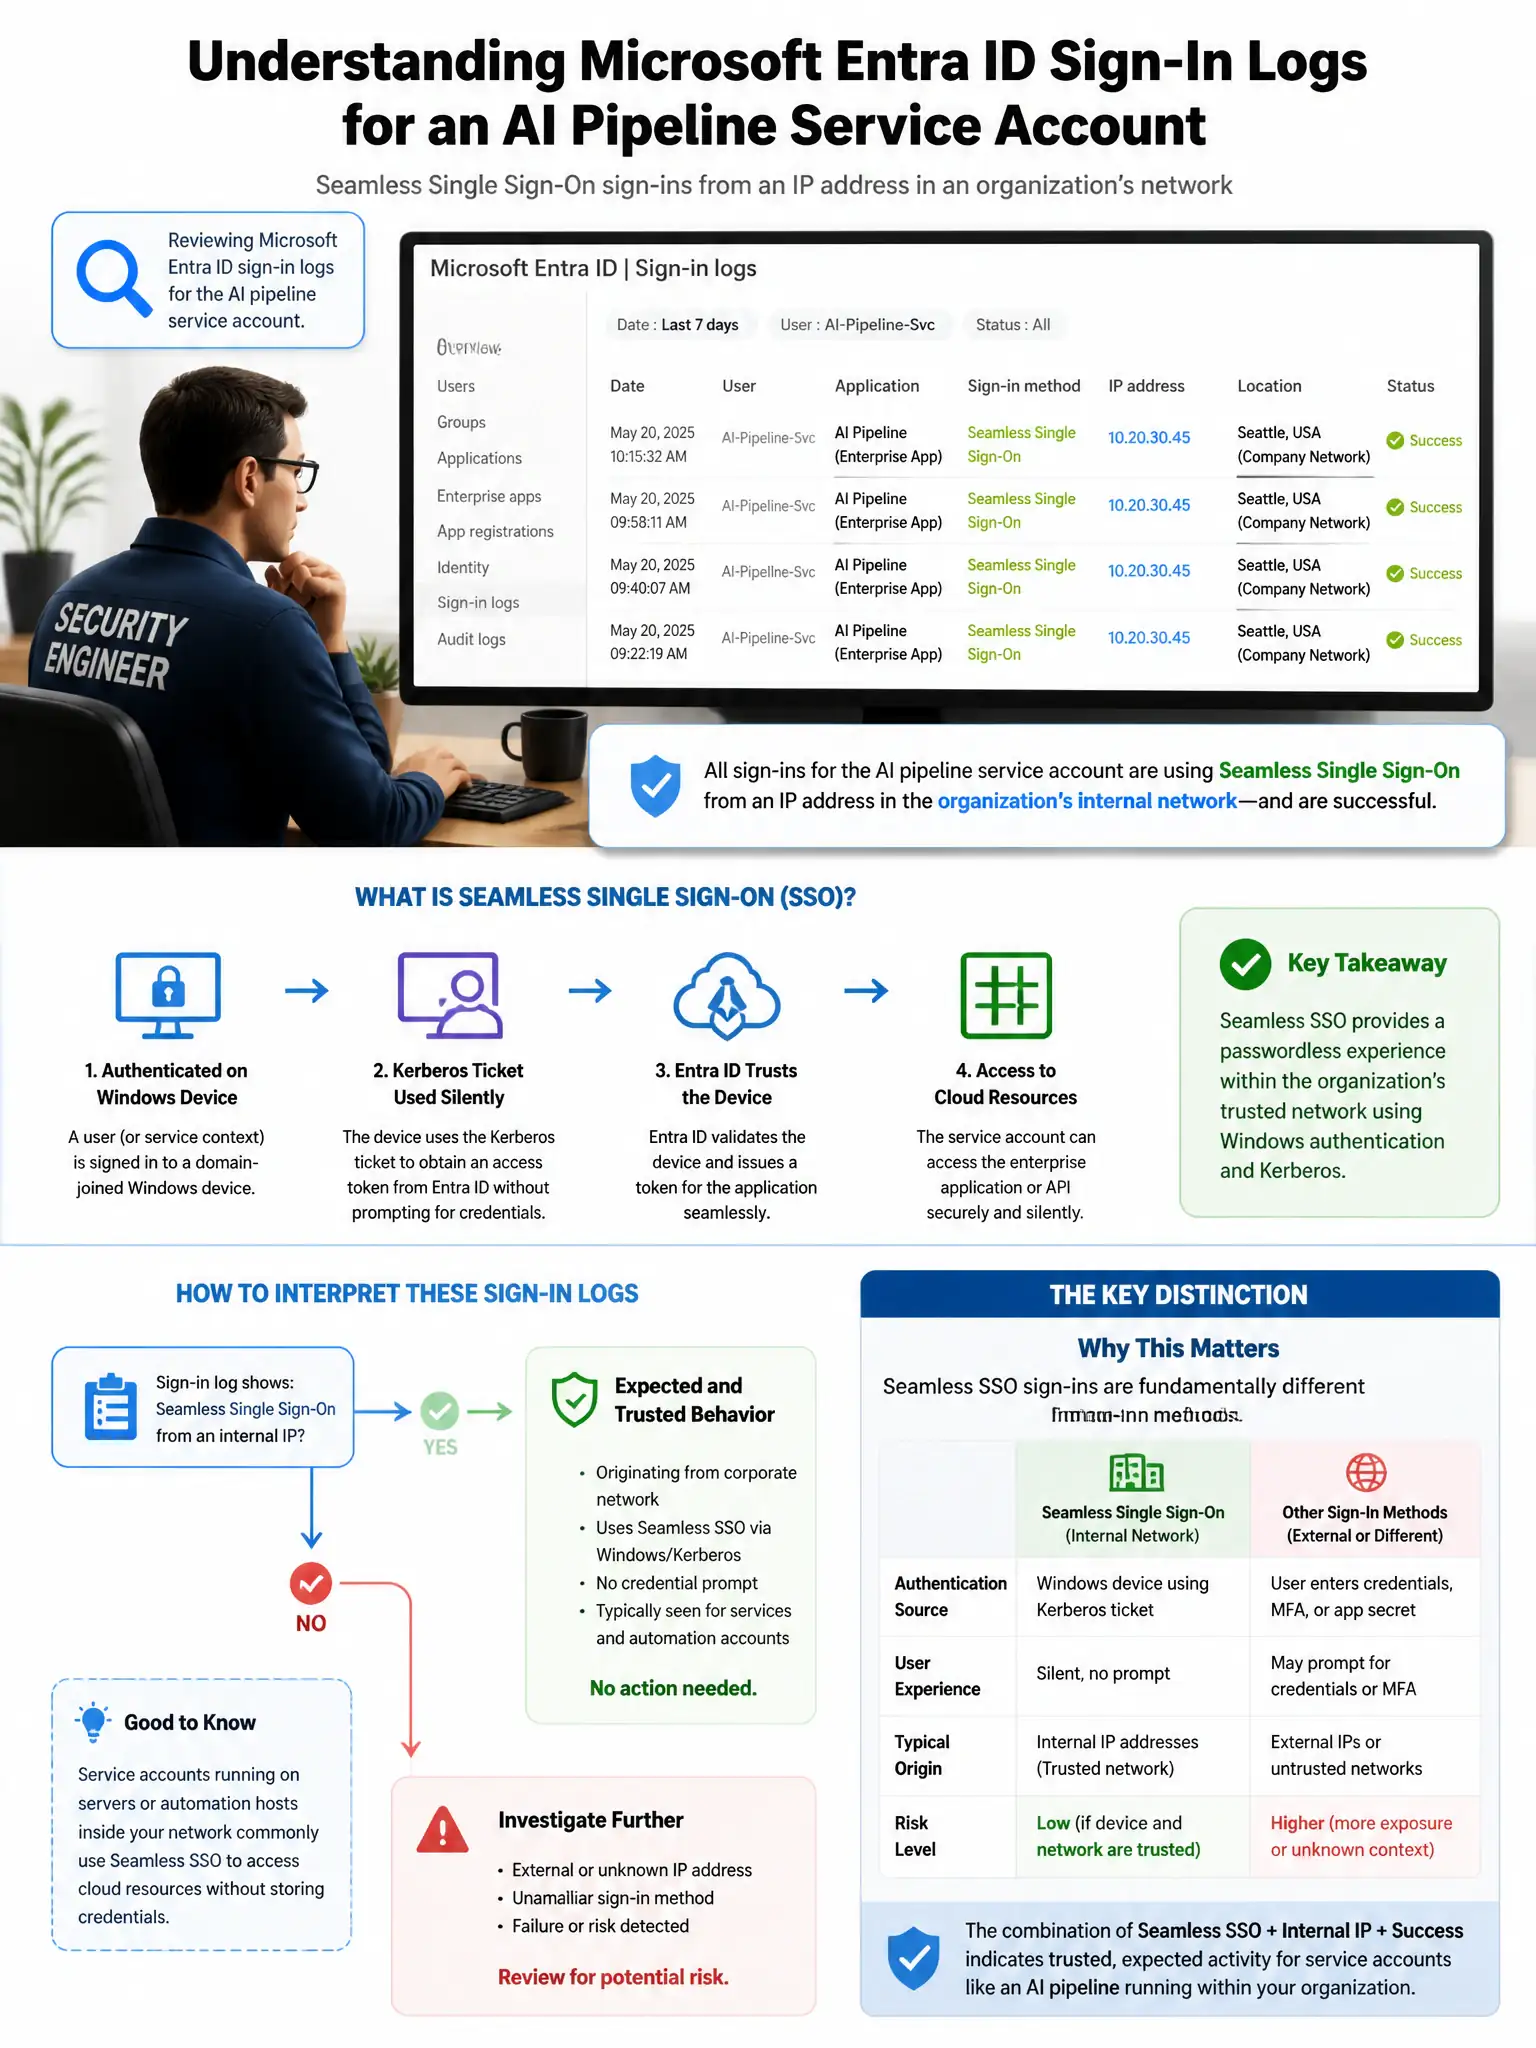
A security engineer is reviewing Microsoft Entra ID sign-in logs for an AI pipeline service account. The logs show sign-ins using 'Seamless Single Sign-On' from an IP address in an unexpected country. The service account is supposed to run only in Azure datacenters. What is the most appropriate immediate action?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to reset the AZUREADSSOACC computer account password and investigate the sign-in, because Seamless SSO uses Kerberos tickets issued by on-premises AD and the AZUREADSSOACC account. Such a sign-in from an unexpected country for a datacenter-only service account smells like on-prem compromise or forged tickets.
Full Explanation
Resetting the AZUREADSSOACC computer account password and investigating the sign-in to determine if the on-premises domain is compromised is the most appropriate immediate action because Seamless SSO sign-ins use Kerberos tickets issued by on-premises Active Directory and the AZUREADSSOACC computer account. Seamless SSO sign-in from an unexpected international location for a service account that should only authenticate from Azure datacenters indicates potential on-premises AD compromise or Kerberos ticket forgery. The immediate action is to reset the AZUREADSSOACC password to invalidate any forged tickets and investigate the on-premises domain for signs of compromise. The option to block the service account in Entra ID and create a new service account with a different UPN stops current harm but leaves the attacker able to compromise the new account through the same vector because it does not address the root cause, which may be on-premises compromise. The option to add the unexpected IP to Entra ID named locations and dismiss the risk detection is wrong because it would dismiss a genuine threat indicator; the sign-in pattern is anomalous for a datacenter-only service account. The option to rotate the service account password and monitor for 24 hours before taking further action is wrong because a 24-hour monitoring period before action gives an attacker significant time to continue unauthorized activities.