
An organization's AI operations team wants to implement a self-service model to allow data scientists to request access to production AI model deployment permissions via Microsoft Entra ID Governance. The request must trigger an automated security review that checks whether the requester has completed required AI security training. Which Microsoft Entra ID Governance capability supports this requirement?
Select an answer to reveal the explanation.
Short Explanation
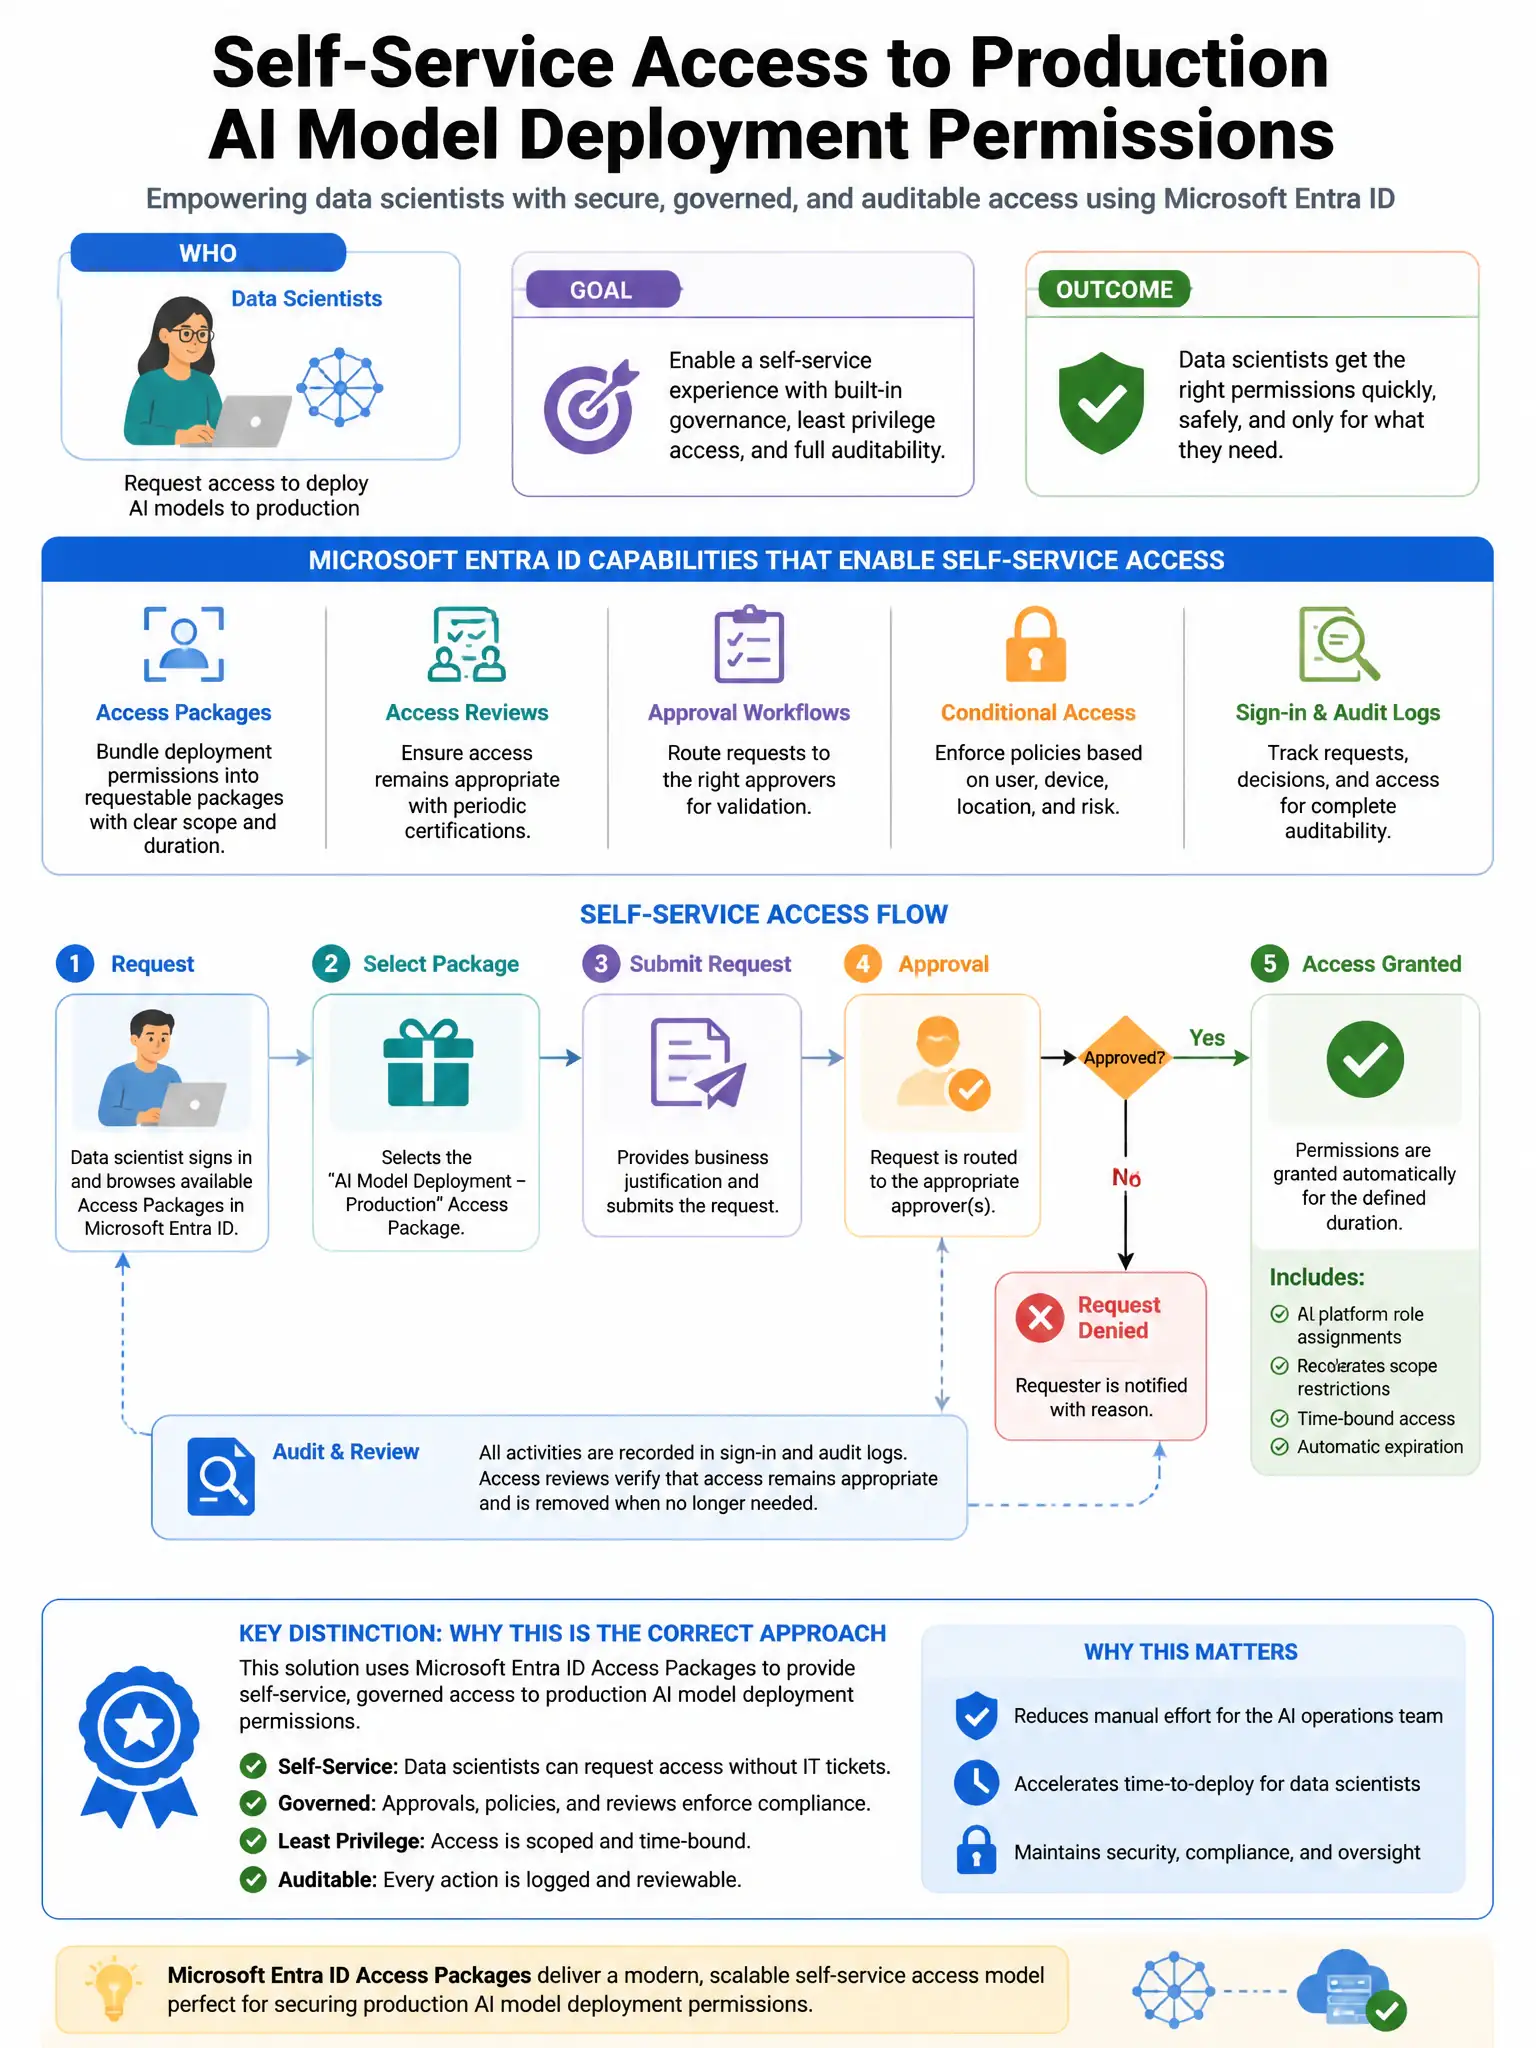
You need an access package with a custom approval workflow that can call an external training check. That lets the request trigger an automated security review before production model deployment permissions are granted. It is the only fit for self-service access requests with a training-completion condition.
Full Explanation
The access package with a custom approval workflow that includes a step checking the requester's training completion record via an external API is correct because Microsoft Entra ID Governance access packages support custom approval stages that can include custom extensions, such as Logic Apps or Azure Functions, as approval steps. A custom extension can query an external training management system to verify whether the requester has completed the required AI security training, making that check a condition of access package approval. The entitlement management access reviews requiring the requester's manager to verify training completion is incorrect because access reviews validate existing access, not approve new access requests, and they cannot query external training systems as part of a new access request workflow. The lifecycle workflows with a pre-joinee workflow checking training records before access is granted is incorrect because lifecycle workflows automate tasks at specific life events, such as joiner, mover, and leaver events, not in response to self-service access requests for specific permissions. The conditional access authentication context requiring AI security training completion as a custom claim is incorrect because Conditional Access authentication context enforces additional controls during authentication, not access request approval workflows.