
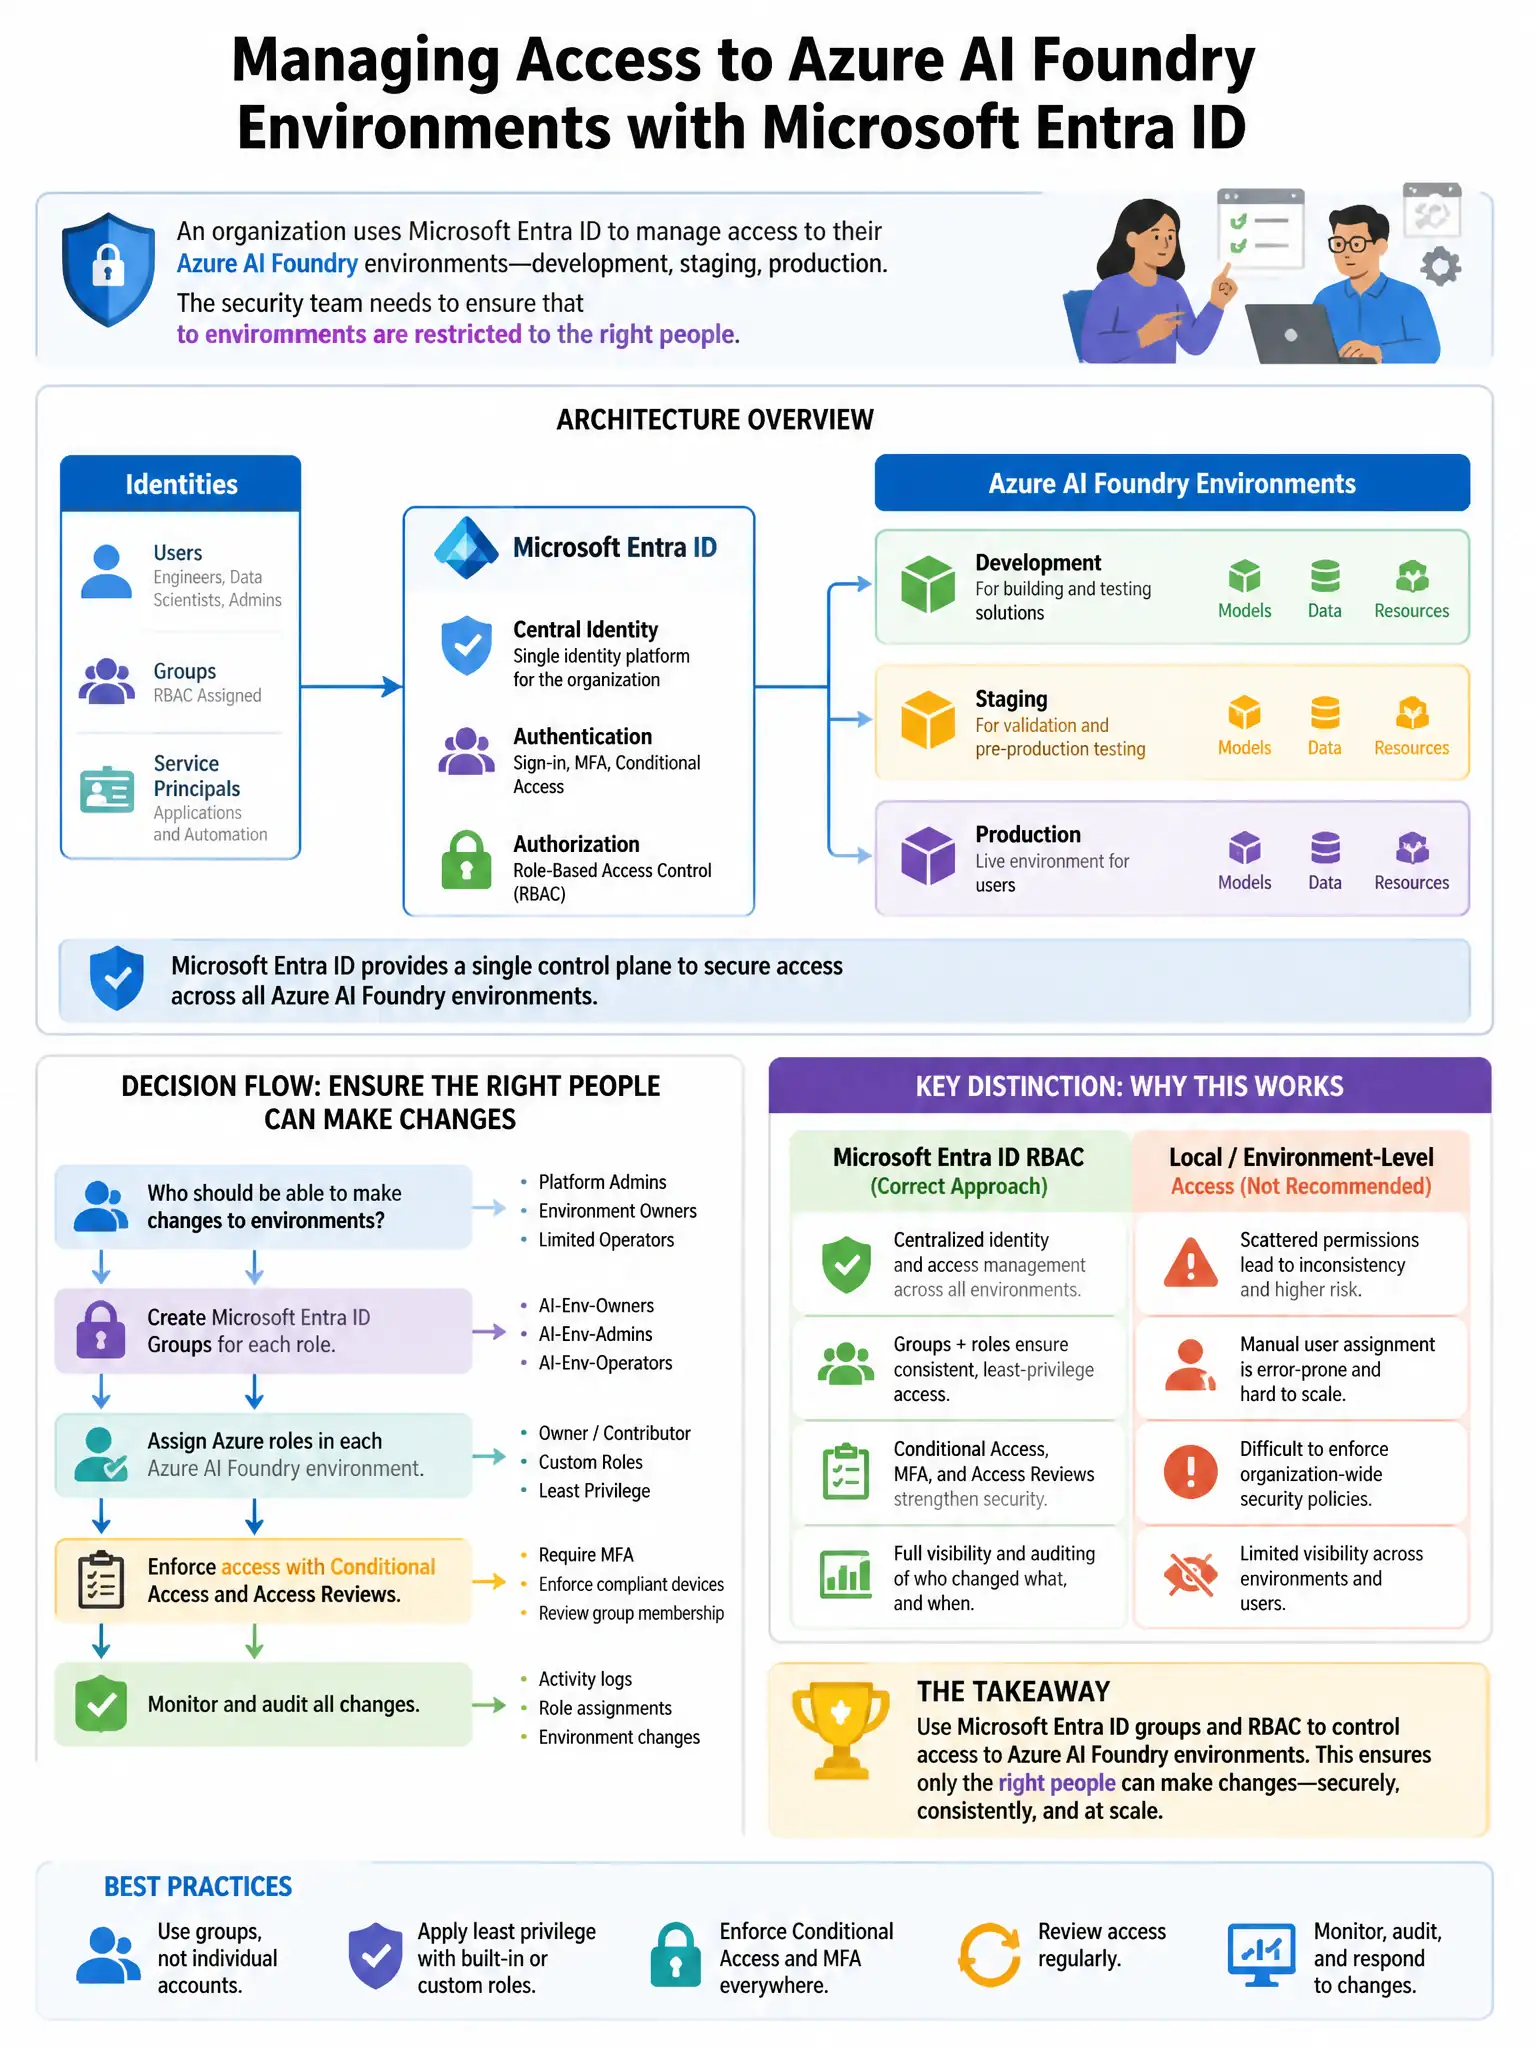
An organization uses Microsoft Entra ID to manage access to their Azure AI Foundry environments (development, staging, production). The security team needs to ensure that changes to production AI model deployments require approval from two members of the AI Security Review team. Which Microsoft Entra feature provides this approval workflow for Azure resource modifications?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need Microsoft Entra PIM for Azure resource roles with a policy requiring two approvers for the production AI Foundry Contributor role. It makes that role eligible and forces two AI Security Review team members to approve activation before anyone can change production AI model deployments.
Full Explanation
The Microsoft Entra PIM for Azure resource roles option is correct because Microsoft Entra Privileged Identity Management (PIM) for Azure resource roles supports configuring approval requirements for role activation. By setting up the production AI Foundry Contributor (or equivalent) role as eligible with a PIM policy requiring approval from two specified AI Security Review team members, anyone needing to make changes to production AI model deployments must request and receive approval from two reviewers before the role is activated. The Azure Resource Manager deployment stacks option is incorrect because deployment stacks manage related resource deployments as a unit but do not provide an identity-based approval workflow for role-level access to make changes. The Microsoft Entra ID Access Reviews option is incorrect because Access Reviews periodically validate existing role assignments but do not enforce approval for individual production changes. The Azure Policy with a deny effect requiring a tag 'ApprovedBy' with two reviewer names option is incorrect because required tags are a resource governance control but do not enforce an identity-based approval workflow; tags can be added by anyone with appropriate permissions.