
A security engineer discovers that Microsoft Copilot for Security is generating responses that reference stale threat intelligence that is over 12 months old. The engineer needs to ensure Copilot for Security uses the most current threat intelligence. Which configuration should be verified?
Select an answer to reveal the explanation.
Short Explanation
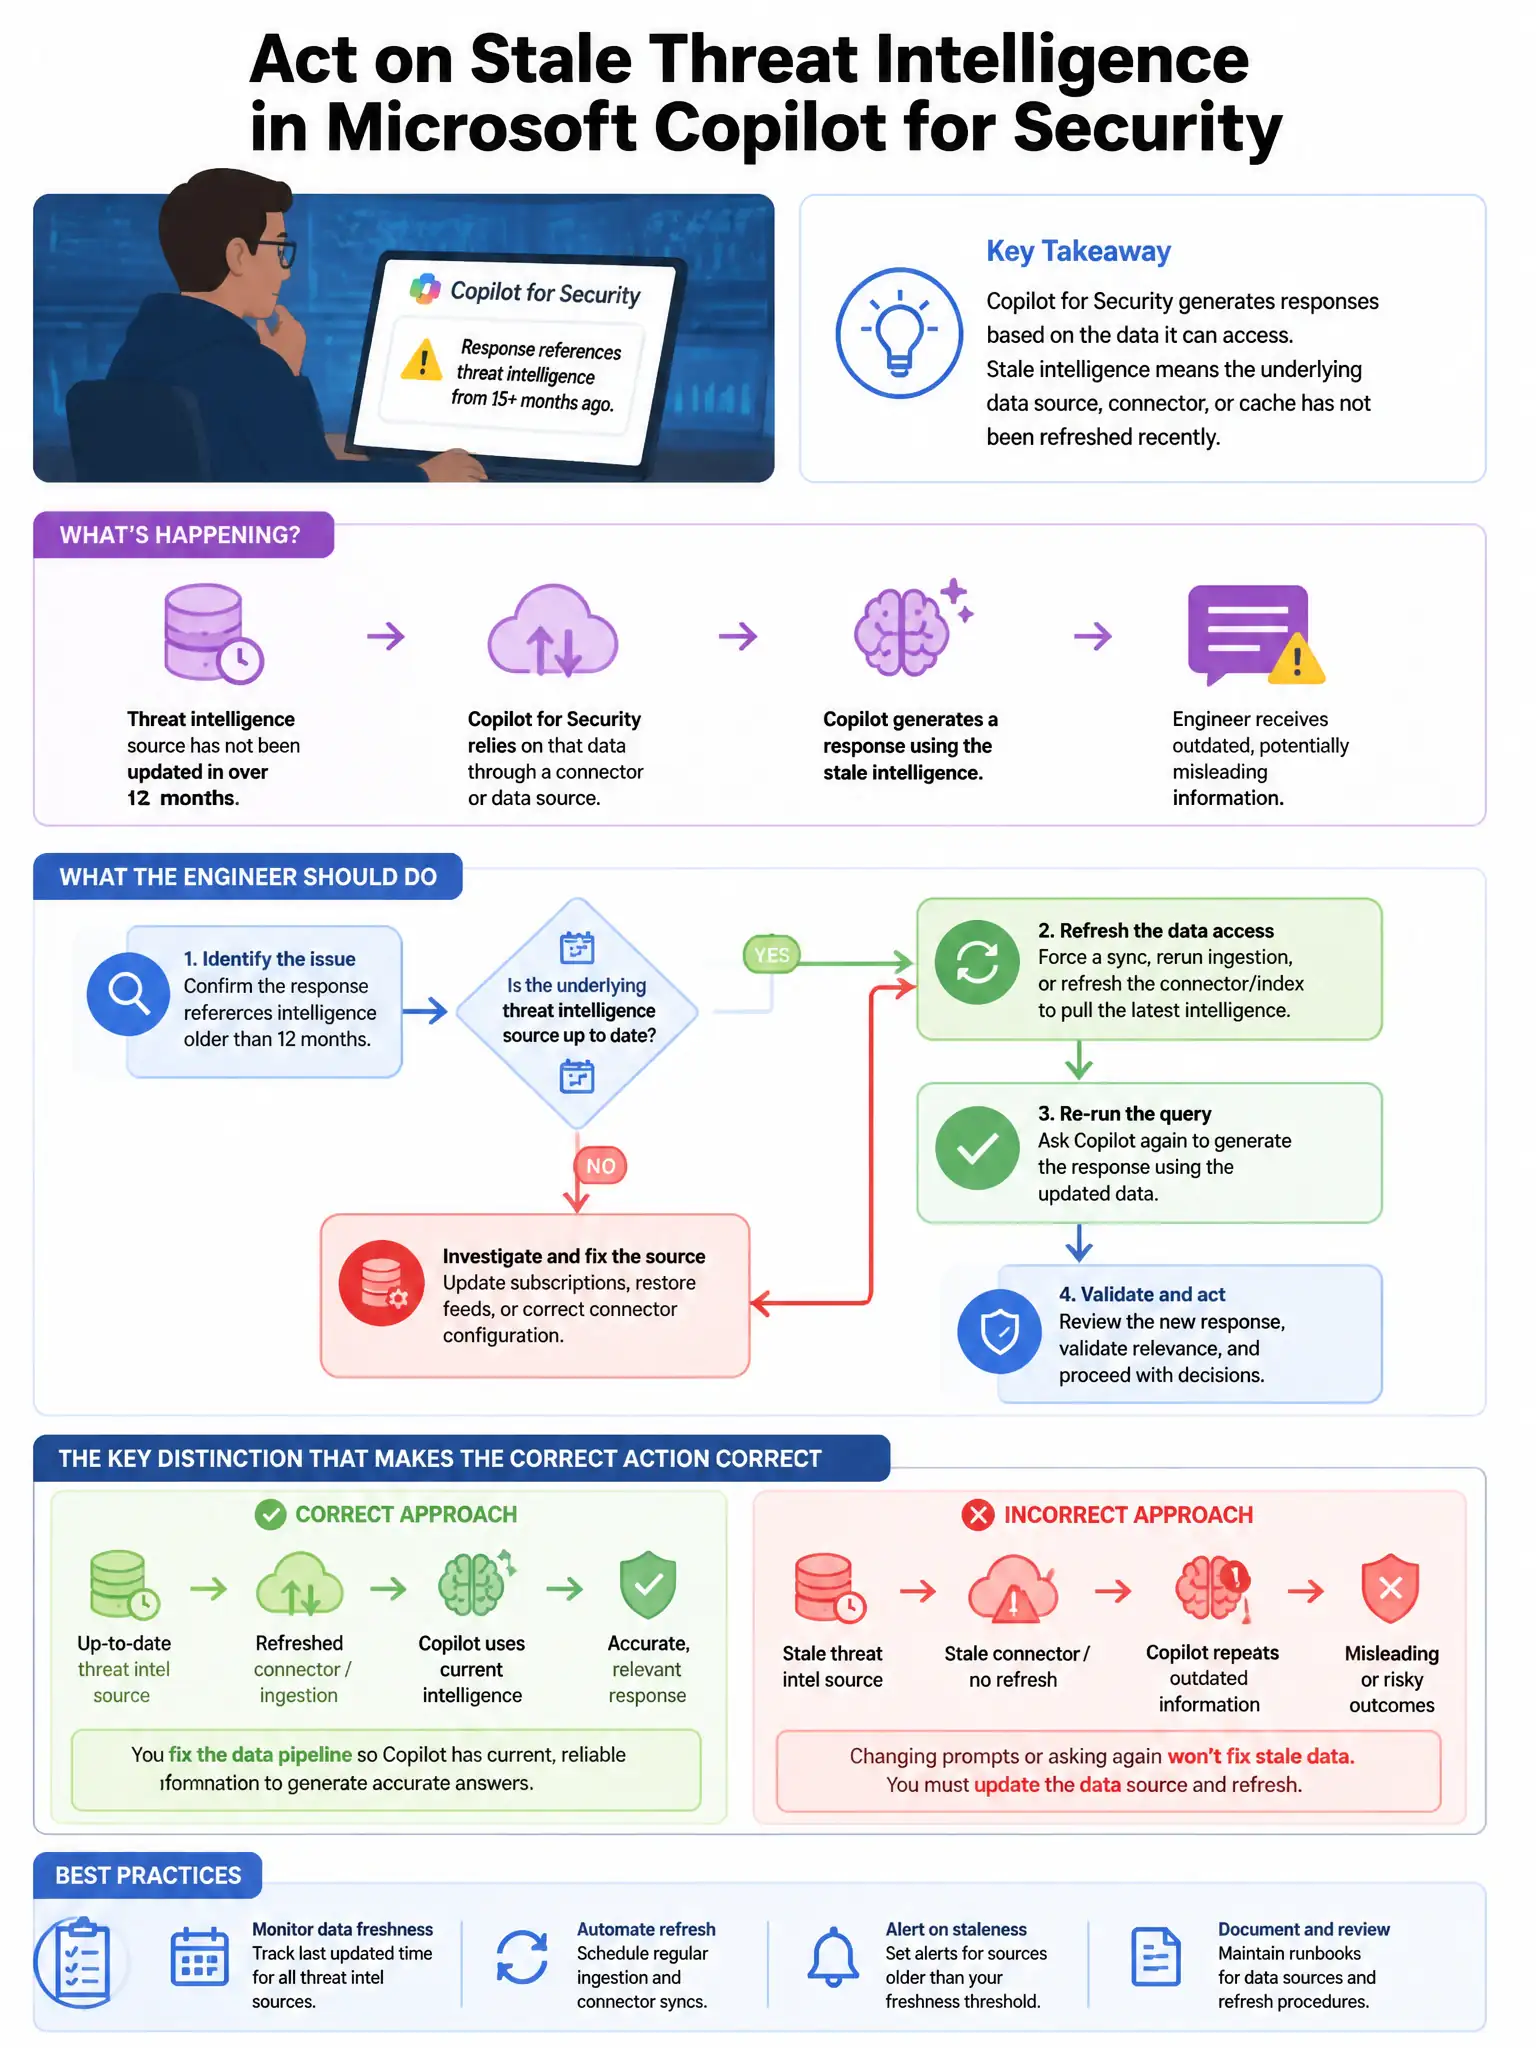
Here's the deal — you need to verify that the Microsoft Defender Threat Intelligence plugin is enabled in Copilot for Security Owner settings. That's what lets Copilot pull live threat intel instead of falling back to stale training data.
Full Explanation
The correct configuration is to ensure the Microsoft Defender Threat Intelligence (MDTI) plugin is enabled in Copilot for Security Owner settings. Microsoft Copilot for Security retrieves current threat intelligence through the MDTI plugin. If MDTI is disabled or not properly configured, Copilot may rely on its training data, which has a knowledge cutoff. Enabling the MDTI plugin in Owner settings allows Copilot to query live, up-to-date threat intelligence, including recently emerged threat actors, CVEs, and attack campaigns. Updating the Copilot for Security model training data refresh schedule in Azure OpenAI settings is incorrect because Copilot for Security's underlying model is managed by Microsoft and cannot be configured for custom training data refresh by customers. Configuring a Microsoft Sentinel Threat Intelligence data connector to feed current threat intelligence to Copilot is incorrect because Sentinel threat intelligence data enhances Sentinel detections; Copilot for Security accesses threat intelligence through its dedicated MDTI plugin, not indirectly through the Sentinel data connector. Subscribing to Microsoft Defender for Threat Intelligence Premium to unlock current threat data is incorrect because, while MDTI Premium provides additional threat intelligence access, the core current threat data access requires enabling the MDTI plugin in Copilot, which is the configuration to verify first.