
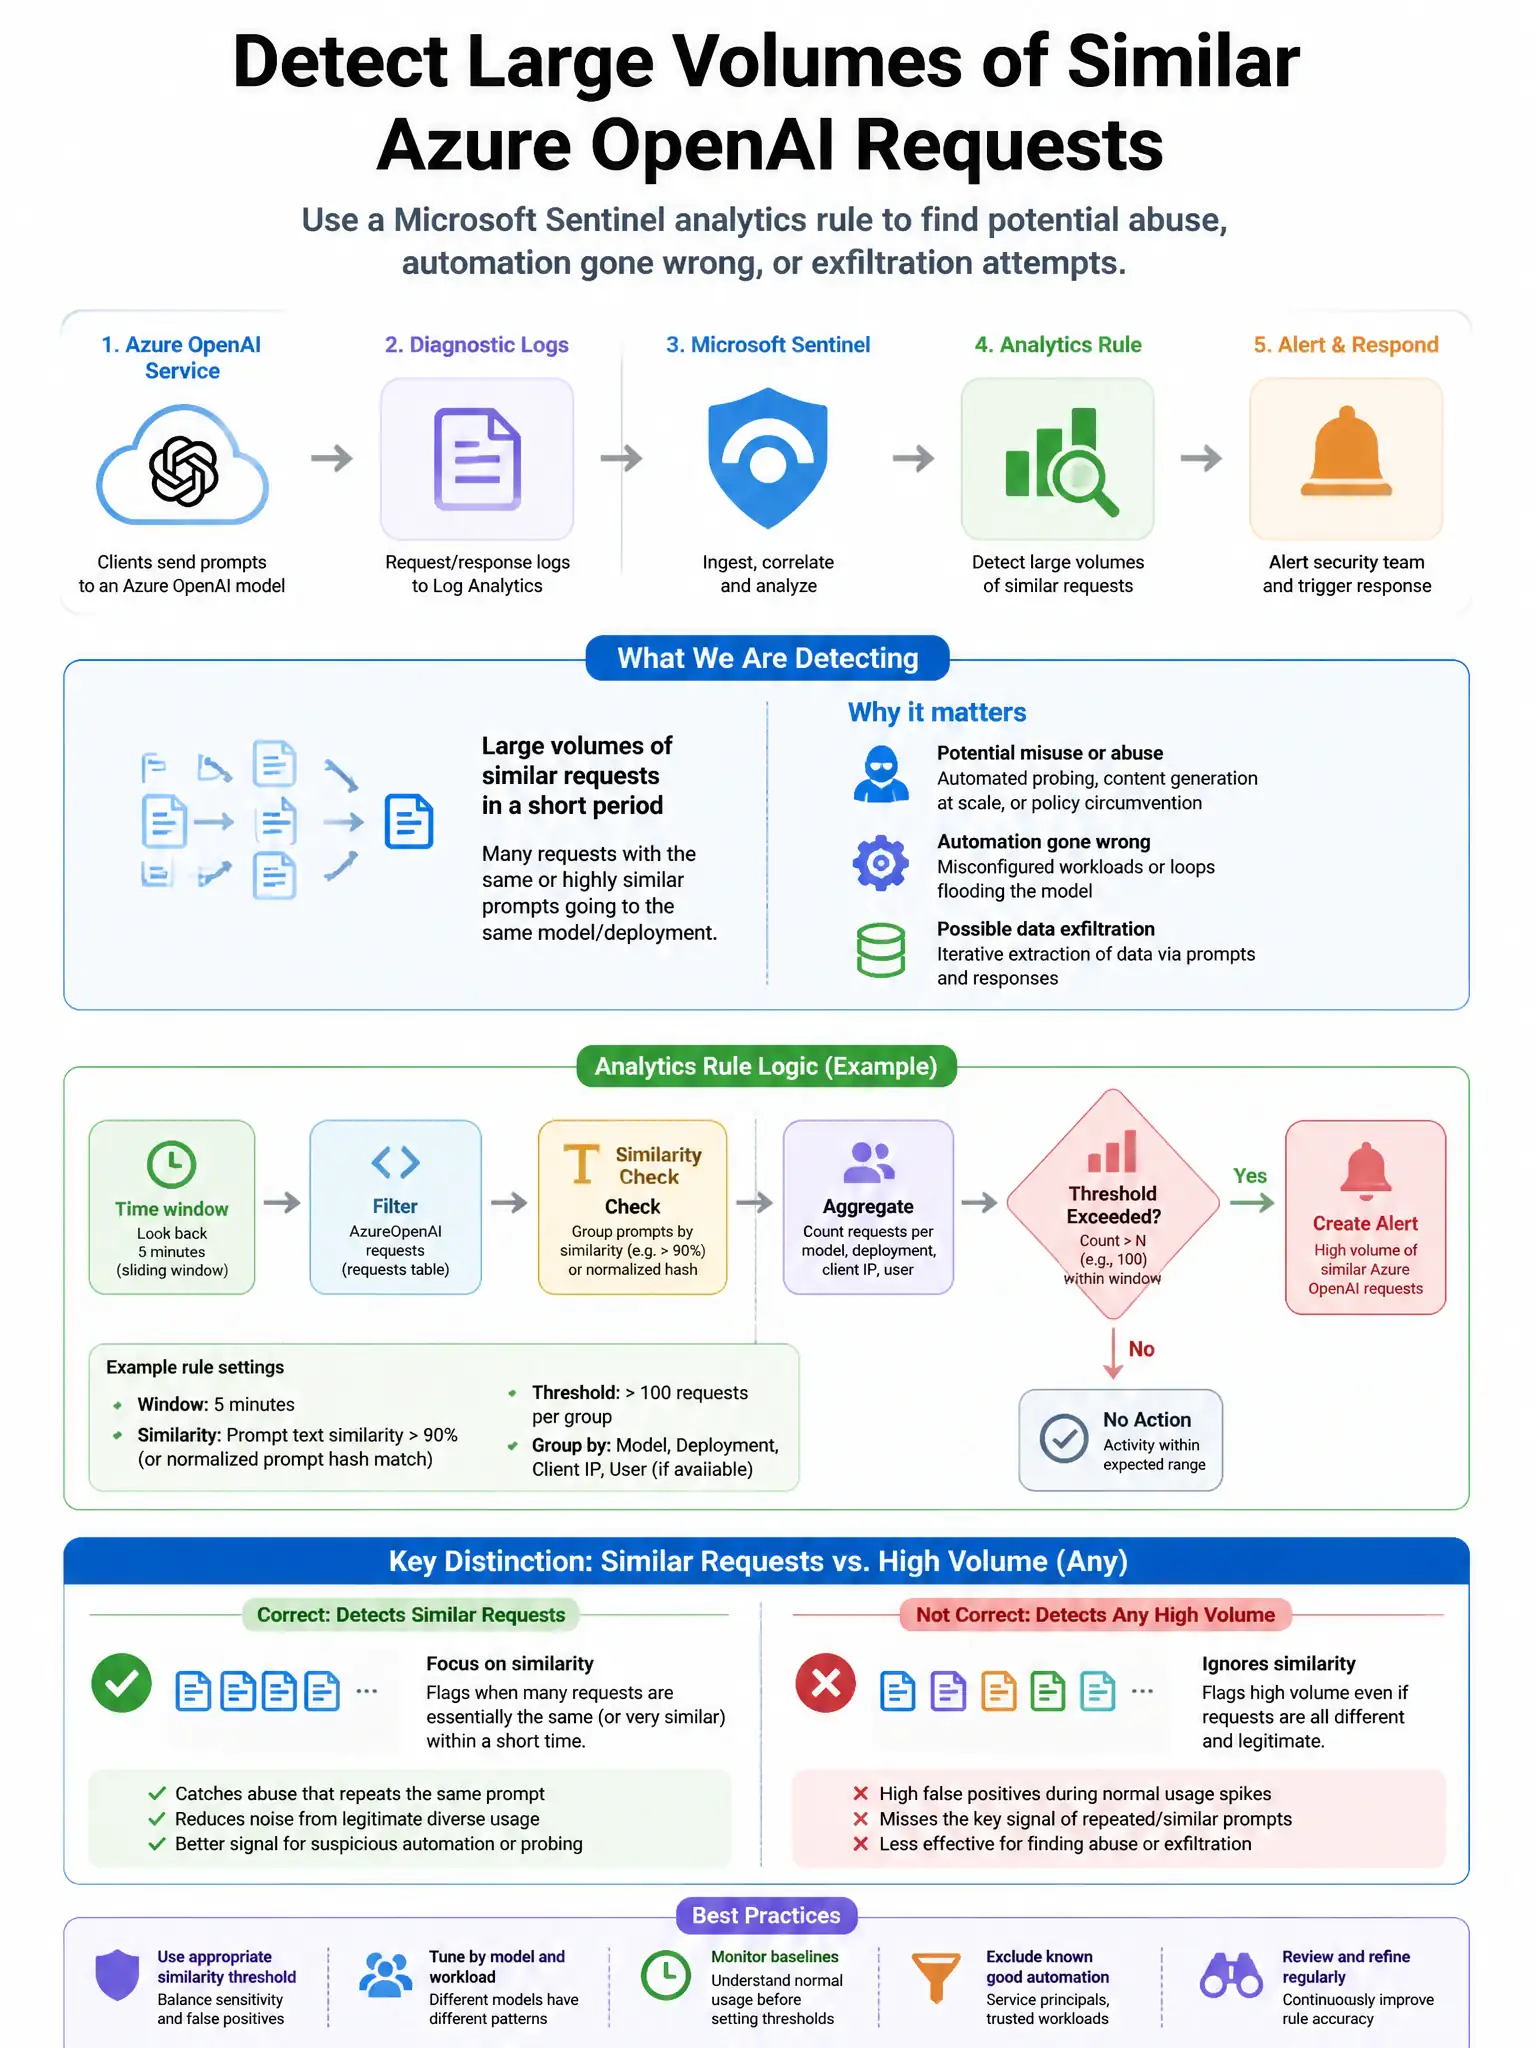
A Microsoft Sentinel analytics rule needs to detect when an Azure OpenAI model is being used to generate large volumes of similar requests in a short period, potentially indicating automated abuse. A security engineer writes a KQL query to detect this. Which KQL operator is most appropriate for identifying time-windowed frequency anomalies?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need summarize with bin() on TimeGenerated because it buckets events into time windows and counts requests per caller, which is how you spot bursty automated abuse.
Full Explanation
The correct answer is summarize with the bin() function on TimeGenerated. This is the standard KQL approach for time-series aggregation: it groups events into fixed time buckets, such as per minute or per 5 minutes, and counts requests from the same caller. That makes it possible to detect high-frequency patterns that may indicate automated abuse. Using a self-join on the Azure Diagnostics table is not appropriate because it would be computationally expensive and is not the standard approach for time-windowed frequency detection. Using an extend operator with a calculated field for request velocity is not sufficient because extend adds calculated fields, but it alone cannot aggregate across multiple requests to compute frequency; summarize is required for aggregation. Using mv-expand to expand multi-value request fields is also incorrect because it is used to expand multi-value or dynamic array fields into individual rows, not for time-window frequency analysis.