
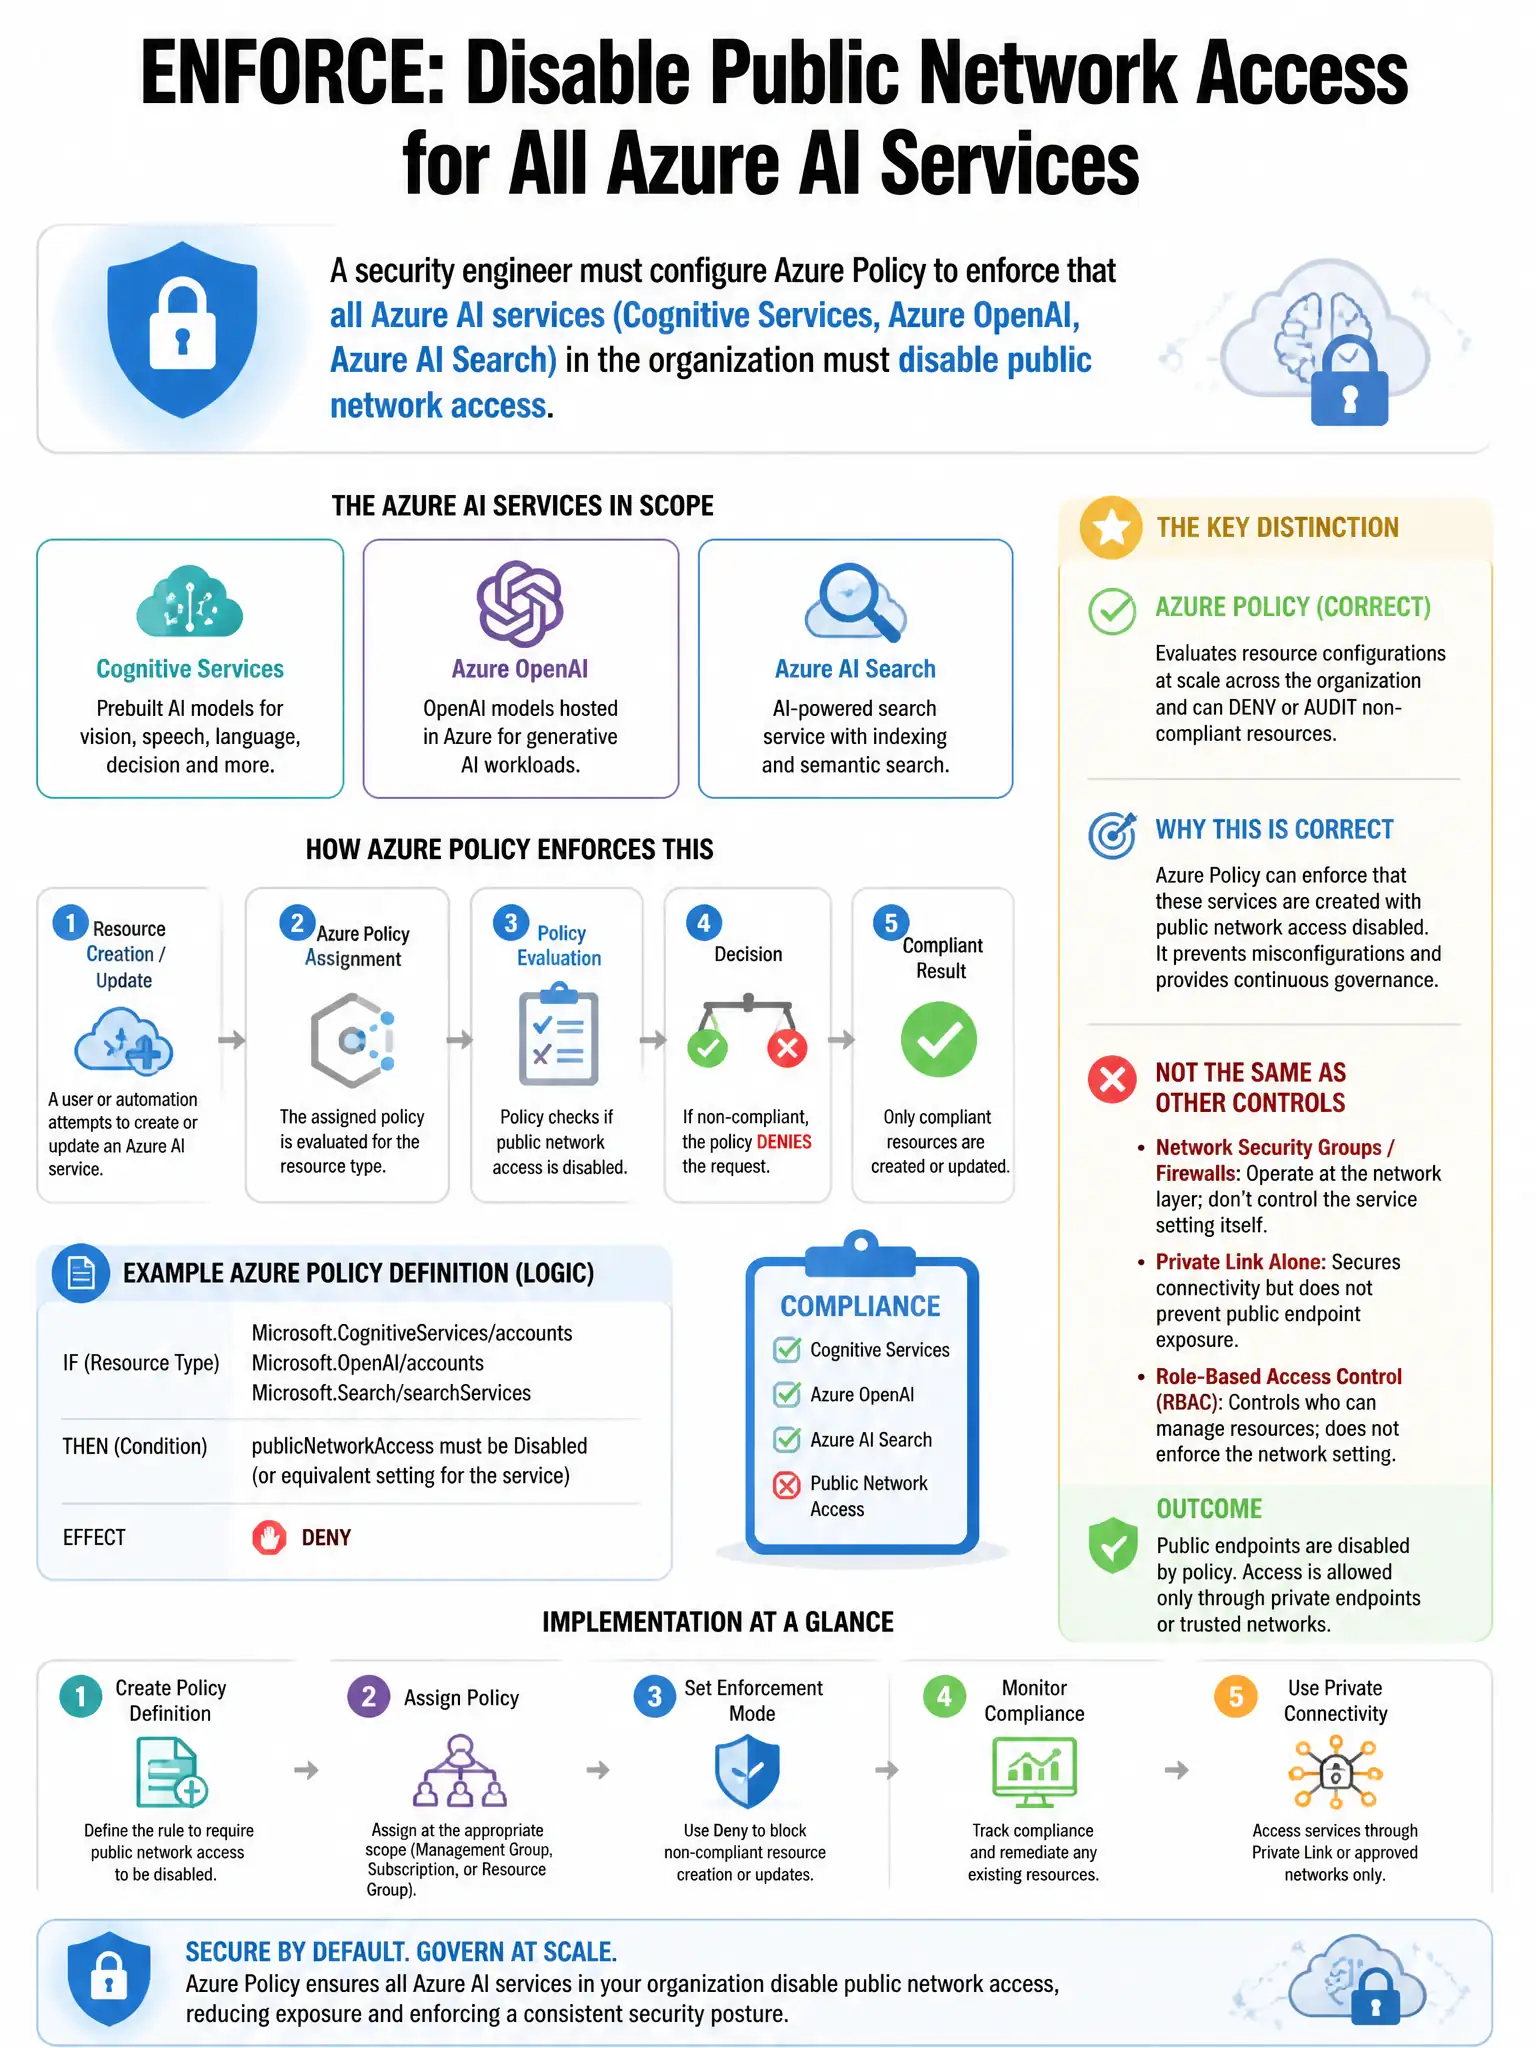
A security engineer must configure Azure Policy to enforce that all Azure AI services (Cognitive Services, Azure OpenAI, Azure AI Search) in the organization must disable public network access. Which Azure Policy effect should be used to enforce this requirement on existing and new resources?
Select an answer to reveal the explanation.
Short Explanation
You need enforcement, so the Modify effect is the right choice because it automatically changes public network access to disabled on new deployments and existing resources through remediation tasks. It enforces compliance without simply blocking deployments.
Full Explanation
The Modify effect is correct because it can automatically change resource properties, such as setting public network access to disabled, on both new resource deployments and existing resources through remediation tasks. This provides enforcement without completely blocking deployments while ensuring compliance. The audit effect to identify non-compliant resources, then manually remediate is incorrect because audit-only provides visibility without enforcement, which does not meet the enforce requirement. The deny effect to block creation of new non-compliant resources and DeployIfNotExists to remediate existing ones is incorrect because deny only blocks new non-compliant resources, and DeployIfNotExists is for deploying additional resources, such as diagnostic settings, not for modifying existing resource properties. The append effect to add the public network access disabled property to resource deployments is incorrect because append adds properties to resource requests during deployment but cannot modify existing resources and may not override explicitly set values.