
A security engineer is hardening an Azure AI Search instance used in a RAG pipeline. The requirement is that data indexed by Azure AI Search must be encrypted at rest using a key that can be revoked instantly if a breach is detected. What must be configured?
Select an answer to reveal the explanation.
Short Explanation
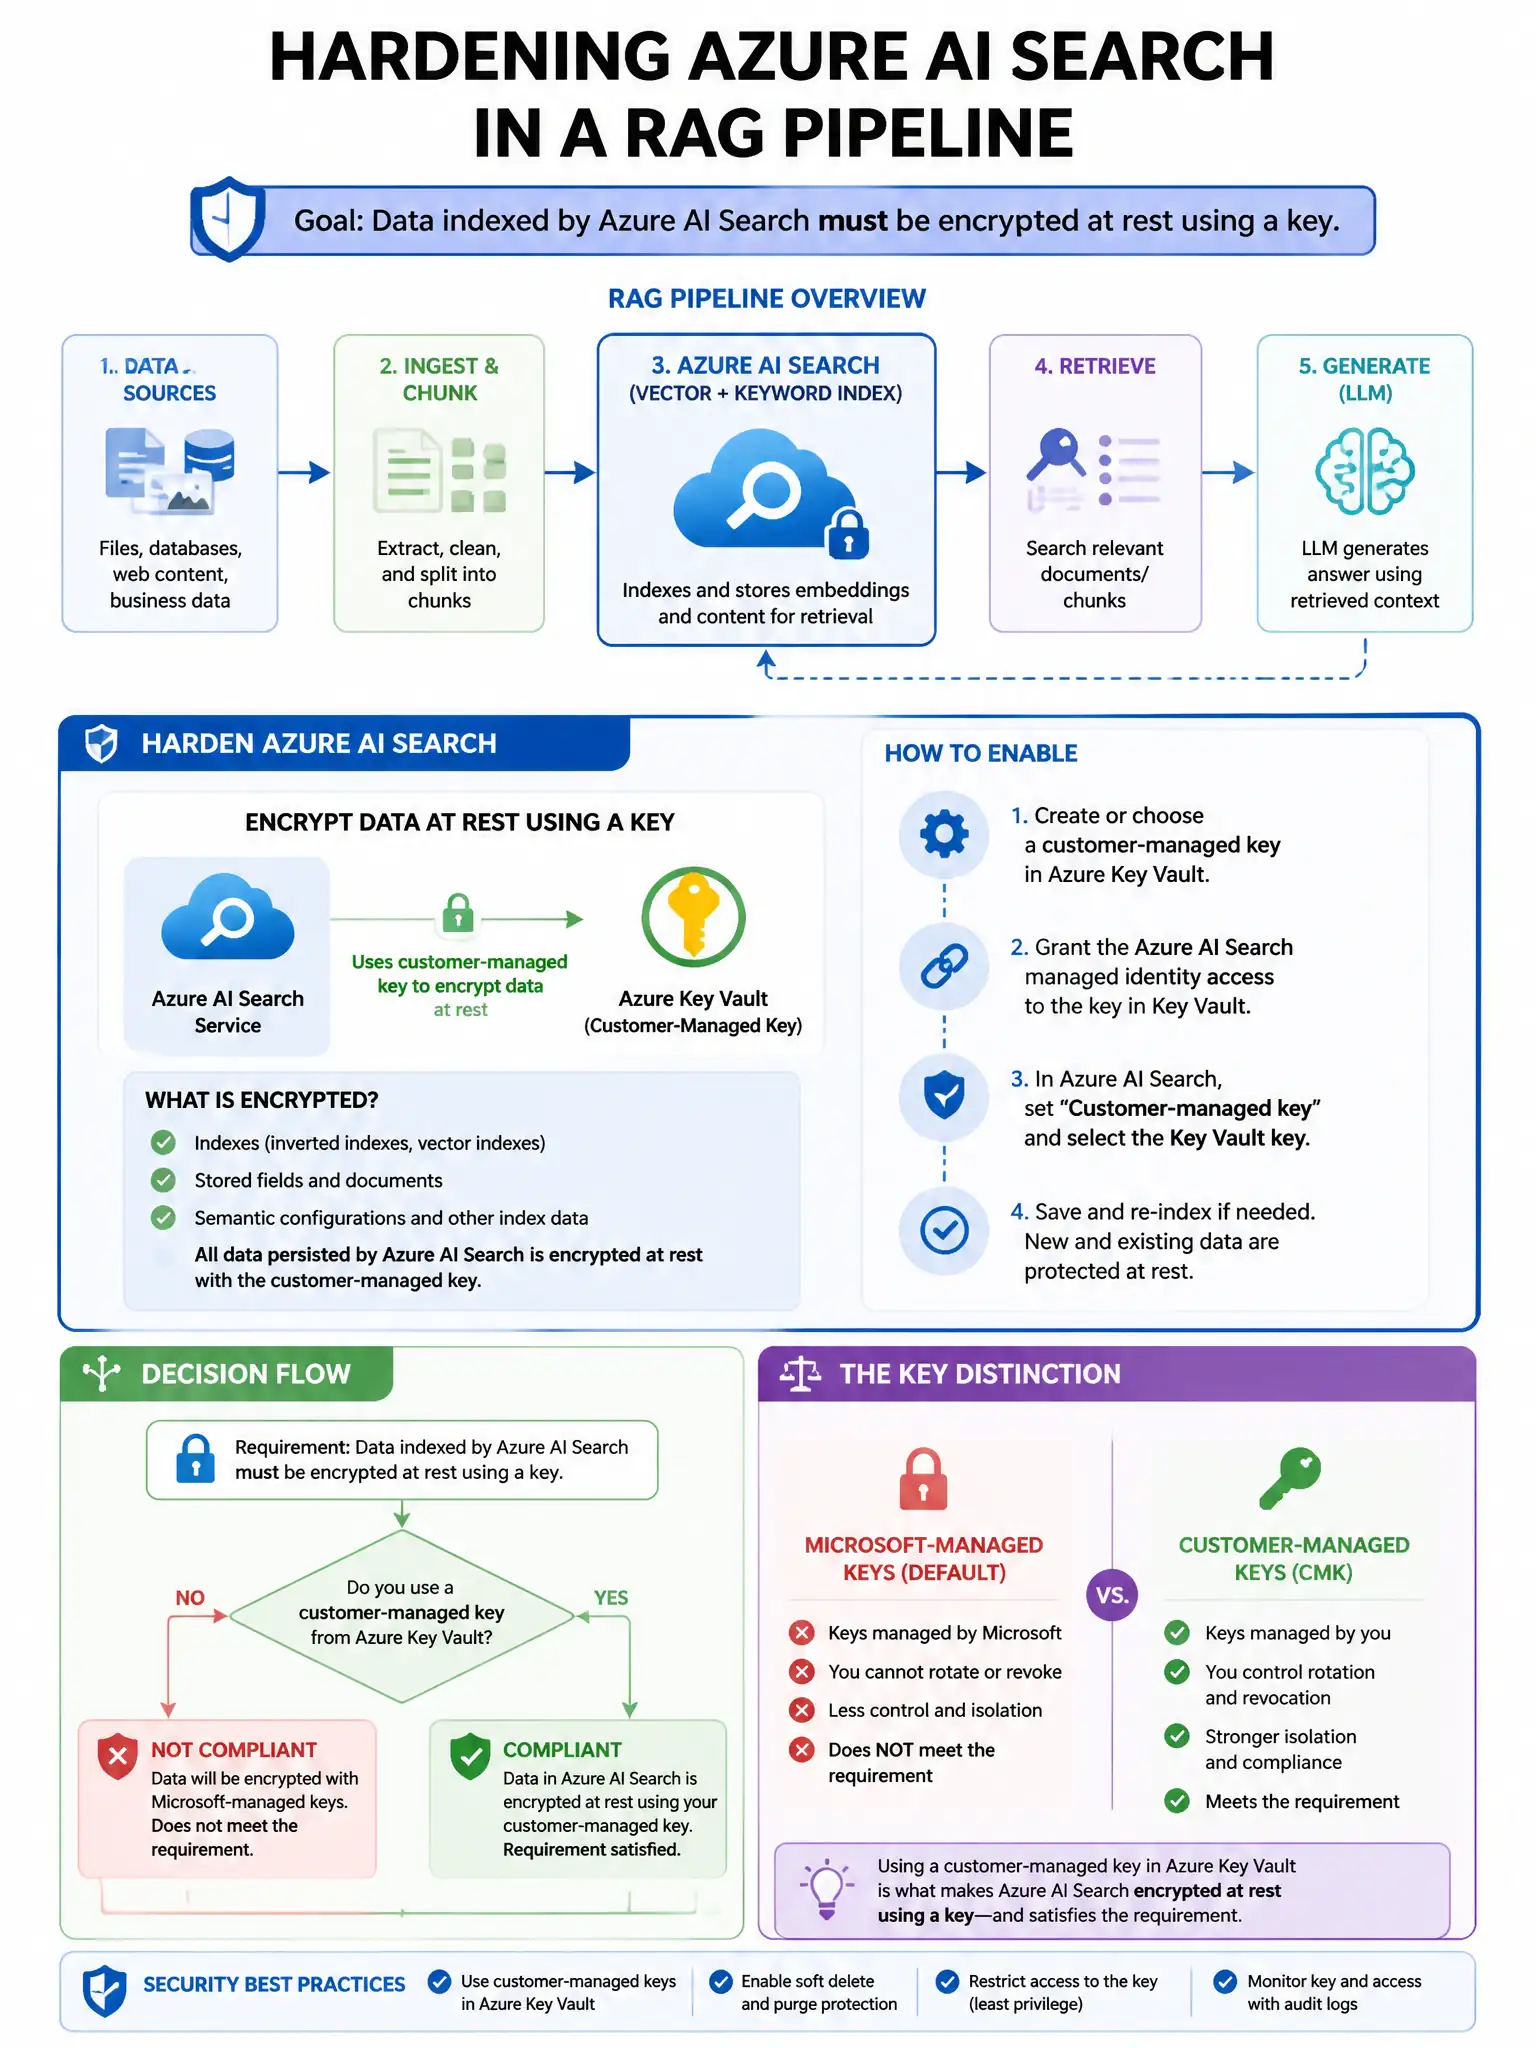
Here's the deal — you need Azure AI Search customer-managed key encryption with the key in Azure Key Vault, and you need soft-delete and purge protection enabled. That way, you can revoke access to the key instantly if a breach happens, while preventing accidental permanent deletion of the key.
Full Explanation
Azure AI Search supports customer-managed key encryption where the key is stored in Azure Key Vault. The correct setup uses that key with soft-delete and purge protection enabled, so you can revoke key access instantly to render indexed data inaccessible while preventing accidental permanent key deletion. Microsoft-managed storage encryption on the underlying storage account is wrong because the customer security team cannot revoke the key. Disabling soft-delete and purge protection is wrong because it risks unrecoverable key deletion. Azure Disk Encryption on service nodes is wrong because Azure AI Search is PaaS, and disk encryption applies to IaaS VM disks.