
A security operations team wants to use Microsoft Copilot for Security to accelerate incident triage. A new analyst asks which built-in promptbook they should use to quickly summarize a Microsoft Sentinel incident and recommend next steps. What is the correct promptbook to use?
Select an answer to reveal the explanation.
Short Explanation
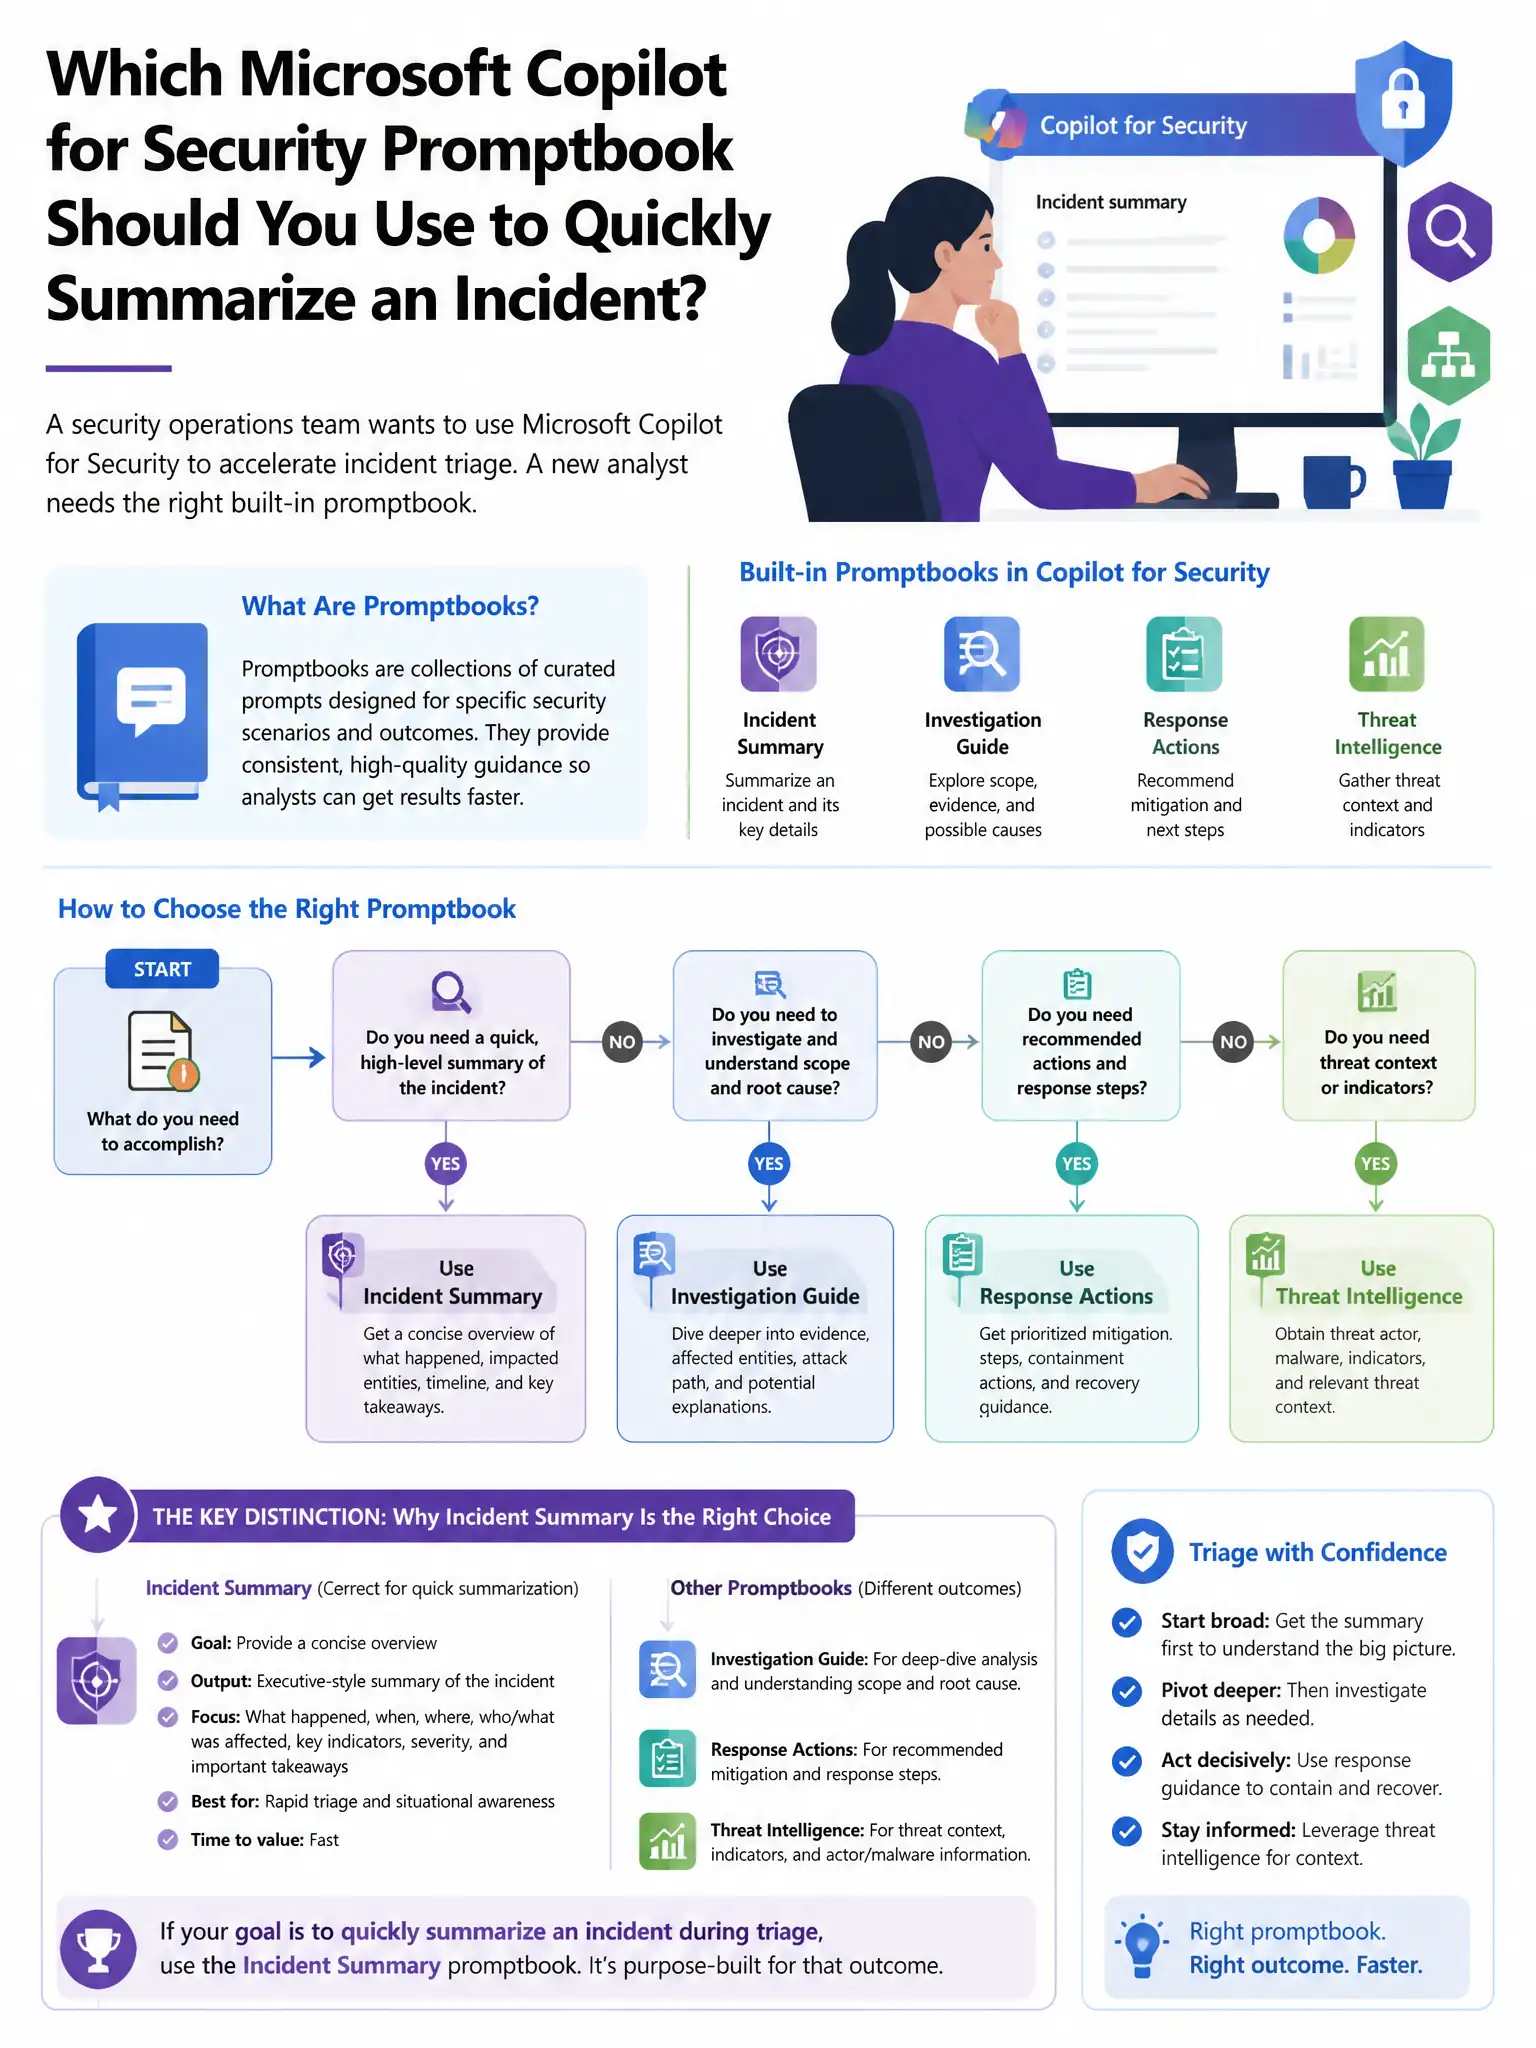
Here's the deal — use the Incident Investigation promptbook because it summarizes Sentinel incidents, identifies key entities, and recommends next steps. The threat-actor, vulnerability, and device promptbooks are built for other tasks.
Full Explanation
The Incident Investigation promptbook in Microsoft Copilot for Security is specifically designed to summarize security incidents from connected sources like Microsoft Sentinel, identify key entities, and provide recommended investigative steps. The Threat Actor Profile promptbook is incorrect because it focuses on intelligence about known threat groups, not specific incidents. The Vulnerability Impact Assessment promptbook is incorrect because it targets CVE analysis and exposure, not incident triage. The Device Investigation promptbook is incorrect because it focuses on a specific device's security posture, not a broader incident.