
An organization wants to use Microsoft Purview Exact Data Match (EDM) to prevent Azure OpenAI from generating responses that contain specific patient identifiers from their patient database (patient IDs, SSNs, and date-of-birth combinations). How does EDM differ from a standard sensitive information type for this use case?
Select an answer to reveal the explanation.
Short Explanation
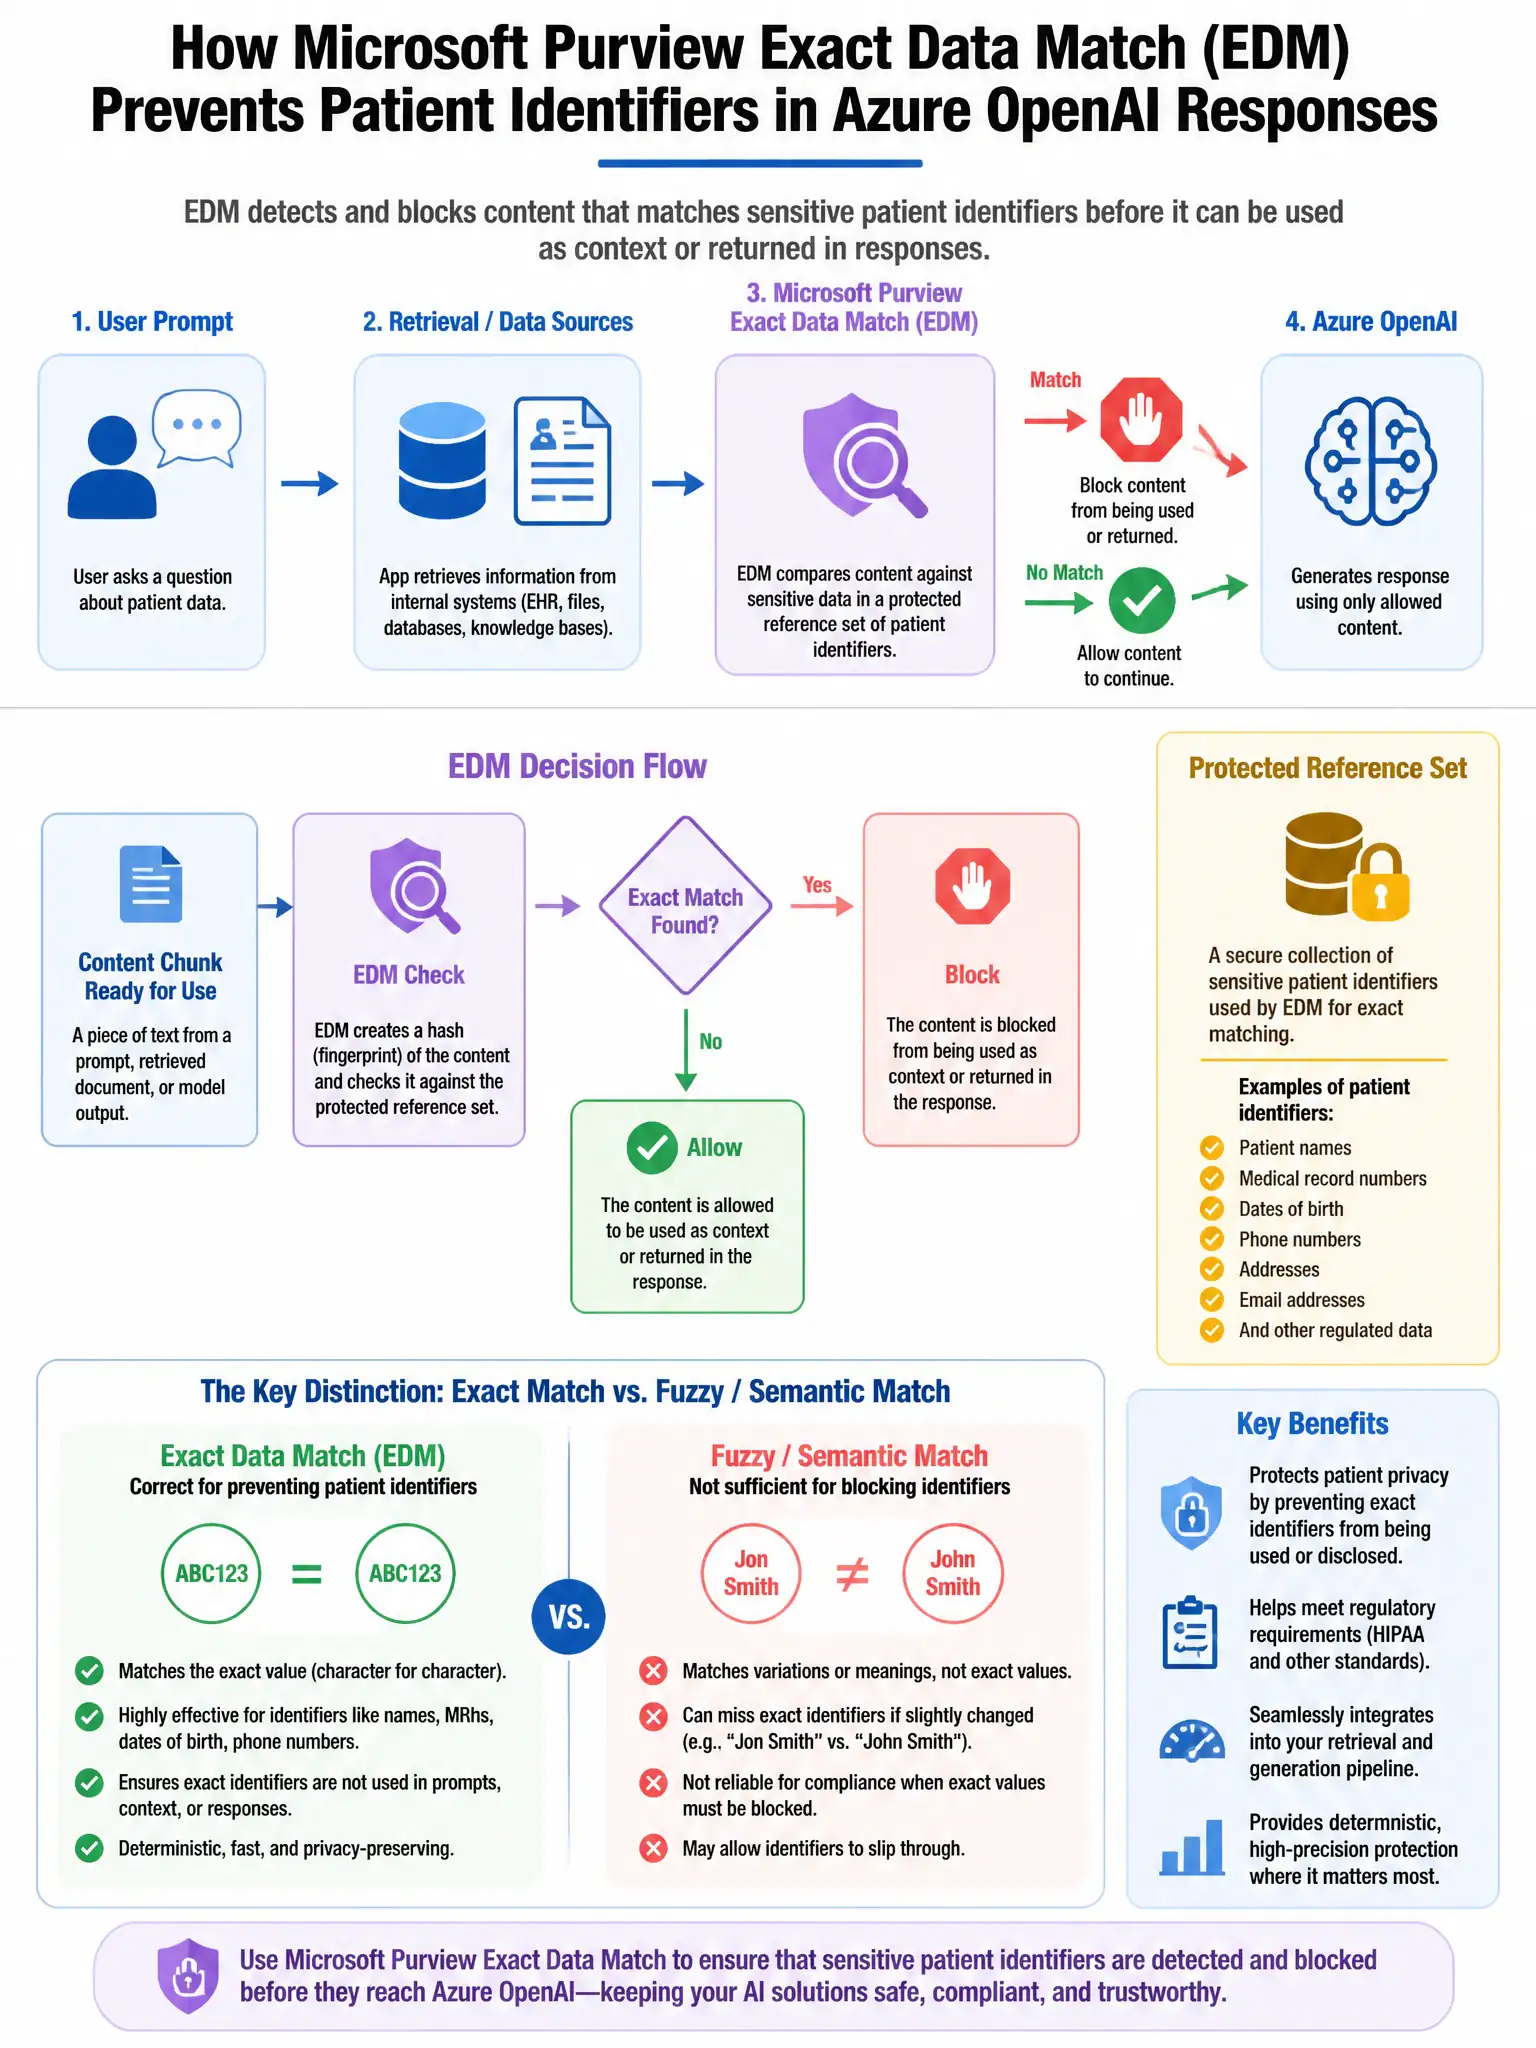
Here's the deal — you want the choice that says EDM matches exact values from a specific database, hashed for privacy, so it detects actual patient records rather than just values matching a pattern. Standard sensitive information types only catch structural formats, like any SSN-looking number. That's why EDM fits your Azure OpenAI patient-identifier use case.
Full Explanation
The correct choice states that EDM matches exact values from a specific database, hashed for privacy, enabling detection of actual patient records rather than just values matching a pattern; standard sensitive information types detect structural patterns, such as any value matching SSN format. Exact Data Match is a Purview feature that enables fingerprinting and detection of exact records from a specific dataset, such as a patient database. The patient records are hashed and uploaded to Purview; when content inspection finds a combination of values that matches an exact record from the database, such as a specific patient's ID, SSN, and date-of-birth combination, it triggers a match. Standard sensitive information types use regex patterns to detect any value matching a structural format, such as any 9-digit SSN-formatted number, regardless of whether it belongs to your actual patients. EDM dramatically reduces false positives for data specific to your organization. The choice claiming EDM detects content patterns using regular expressions, while standard sensitive information types use database lookups, is wrong because it reverses the descriptions: EDM uses database fingerprinting, not regex; standard sensitive information types use patterns including regex. The choice claiming EDM is faster for content inspection than standard sensitive information types is wrong because EDM involves additional processing against hashed records and may be computationally more complex than simple pattern matching. The choice claiming EDM can be applied only to on-premises repositories, not to cloud AI services, is wrong because EDM can be applied to cloud services, including M365 workloads and via DLP policies on cloud AI services.