
A company uses Azure Machine Learning with a managed online endpoint that authenticates callers using a key. The security team wants to migrate to token-based authentication using managed identities. The endpoint will be called by an Azure App Service. Which steps correctly implement this migration?
Select an answer to reveal the explanation.
Short Explanation
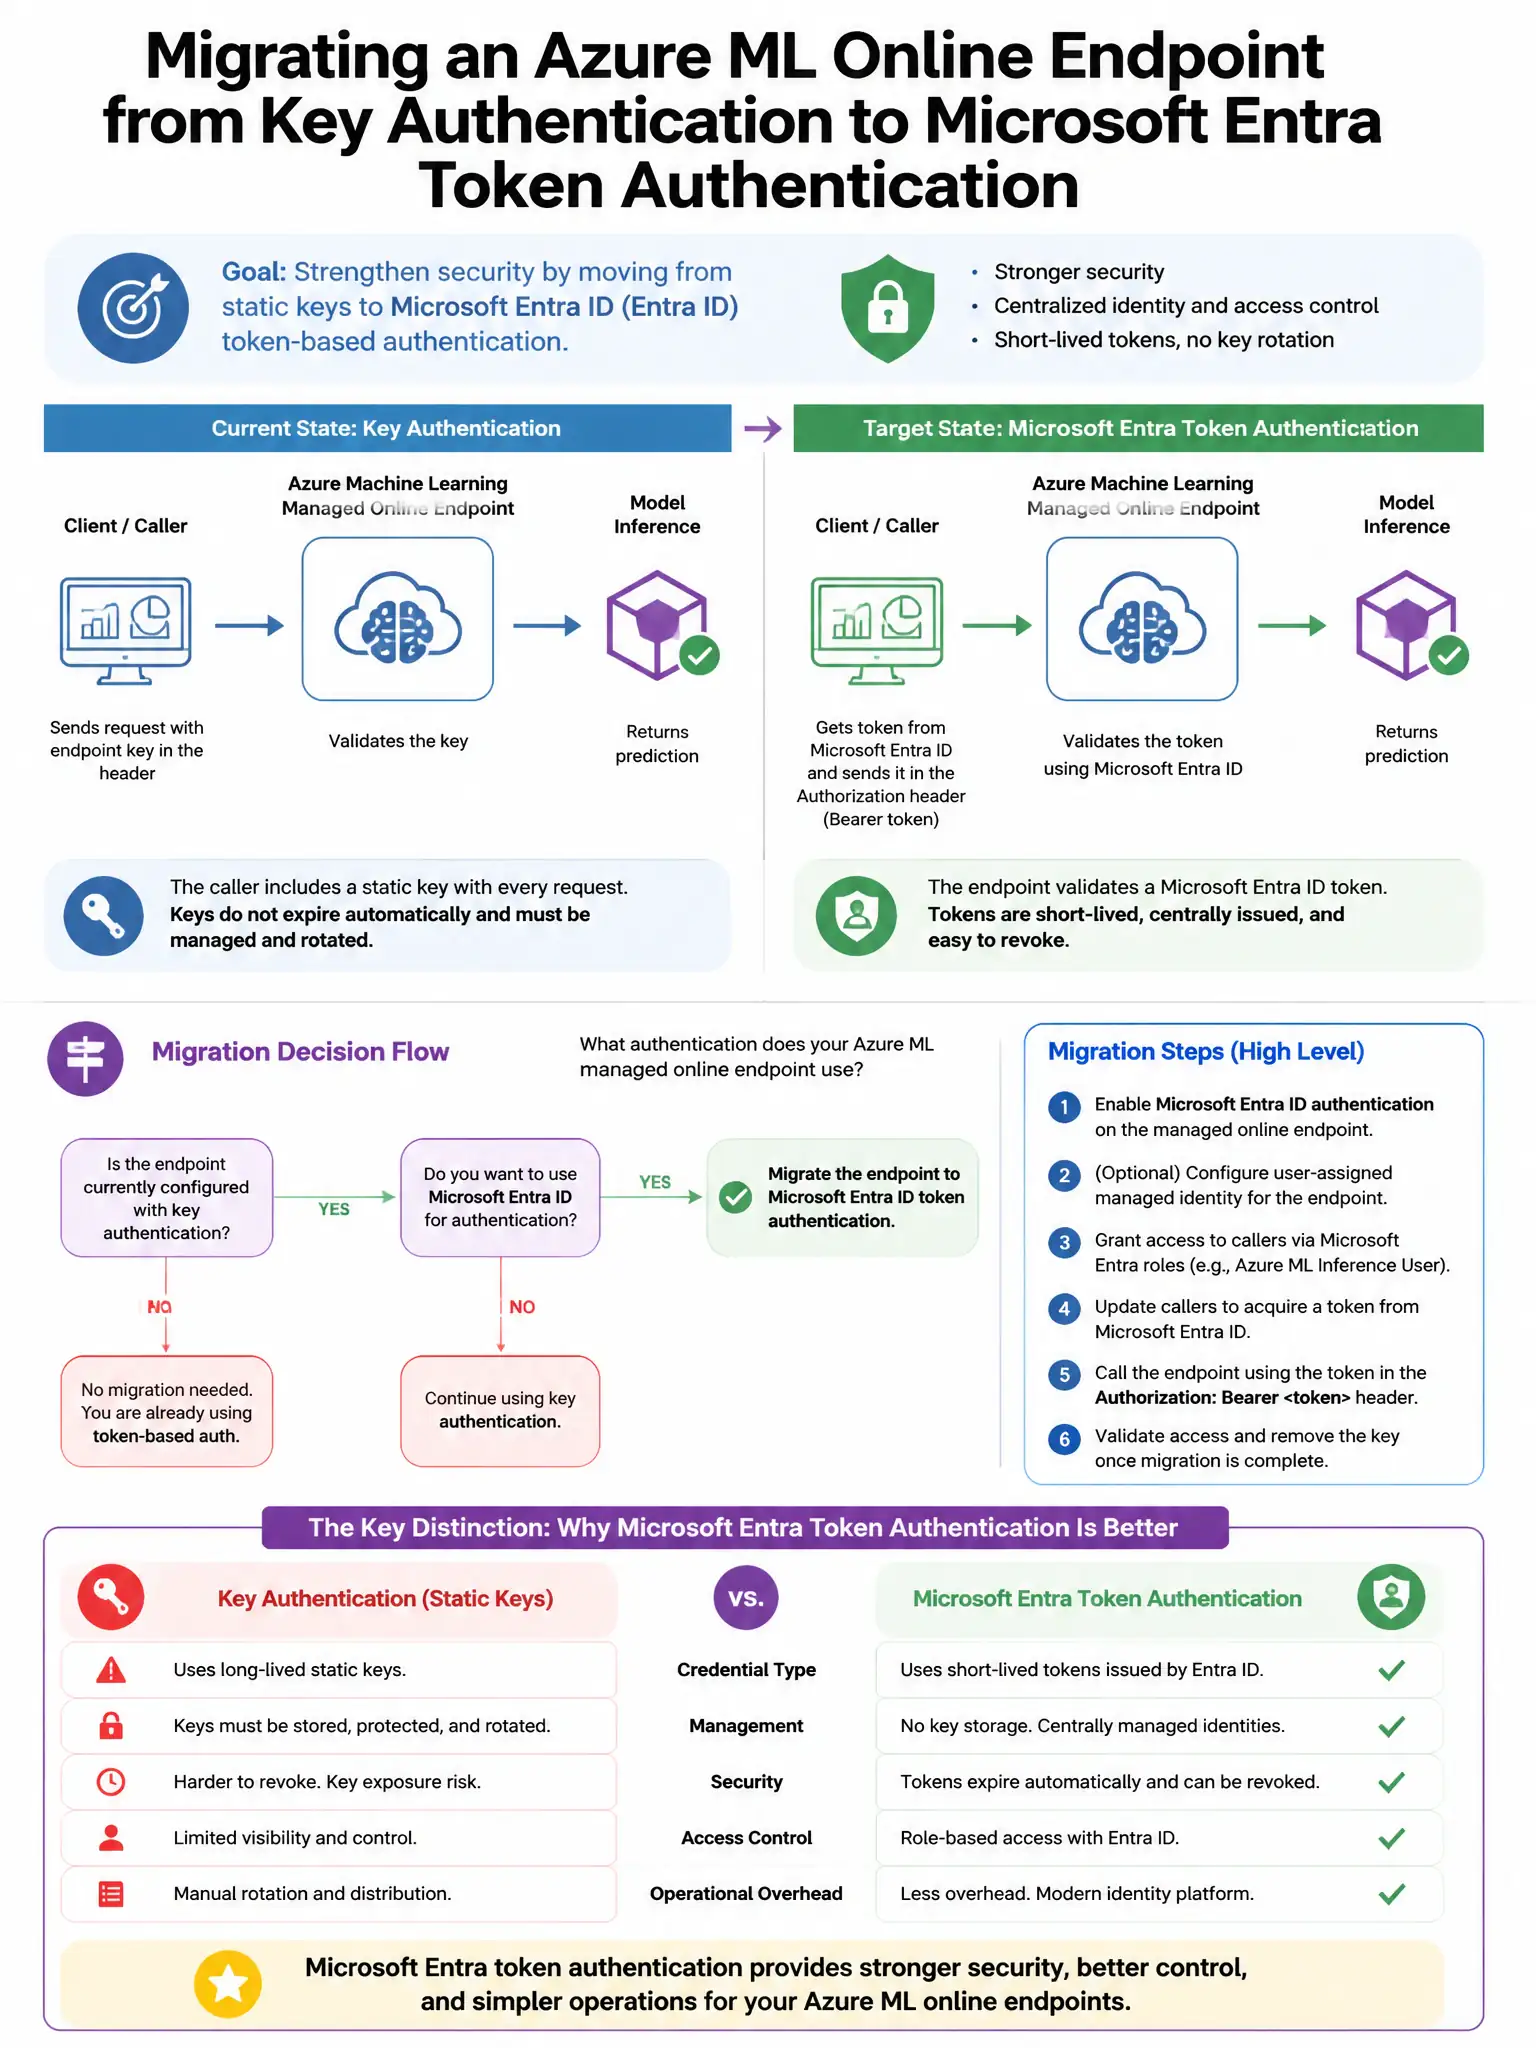
Here's the deal: you disable key authentication on the managed online endpoint, give the App Service a system-assigned managed identity, and grant that identity the 'AzureML Data Scientist' role so it can call the endpoint with Entra ID tokens. No keys, no secrets.
Full Explanation
The correct approach is to disable key authentication on the Azure Machine Learning managed online endpoint, enable a system-assigned managed identity on the Azure App Service, and assign the App Service's managed identity the 'AzureML Data Scientist' role on the AML workspace. Azure Machine Learning managed online endpoints support Microsoft Entra ID token authentication in addition to key authentication. To migrate, you disable key-based authentication on the endpoint to enforce token-only access, enable a system-assigned managed identity on the Azure App Service caller to give it an Entra ID identity without stored credentials, and assign the AML-appropriate role to the App Service's managed identity so it can call the endpoint. The 'AzureML Data Scientist' role or a custom role with endpoint invoke permissions grants the App Service access to submit scoring requests. The wrong option that enables managed identity on the AML endpoint itself and assigns it the Contributor role is incorrect because the endpoint having a managed identity controls what the endpoint itself can access, such as storage, not who can call the endpoint. The wrong option that configures the App Service with a service principal and adds the principal to the AML workspace owner group is incorrect because service principals with manual credentials are not credential-free, and the question requires managed identity-based authentication. The wrong option that sets the AML managed online endpoint scoring URI to require OAuth2 client credentials flow with App Service credentials is incorrect because Azure App Service does not natively use OAuth2 client credentials flow on its own; managed identity is the credential-free approach.