
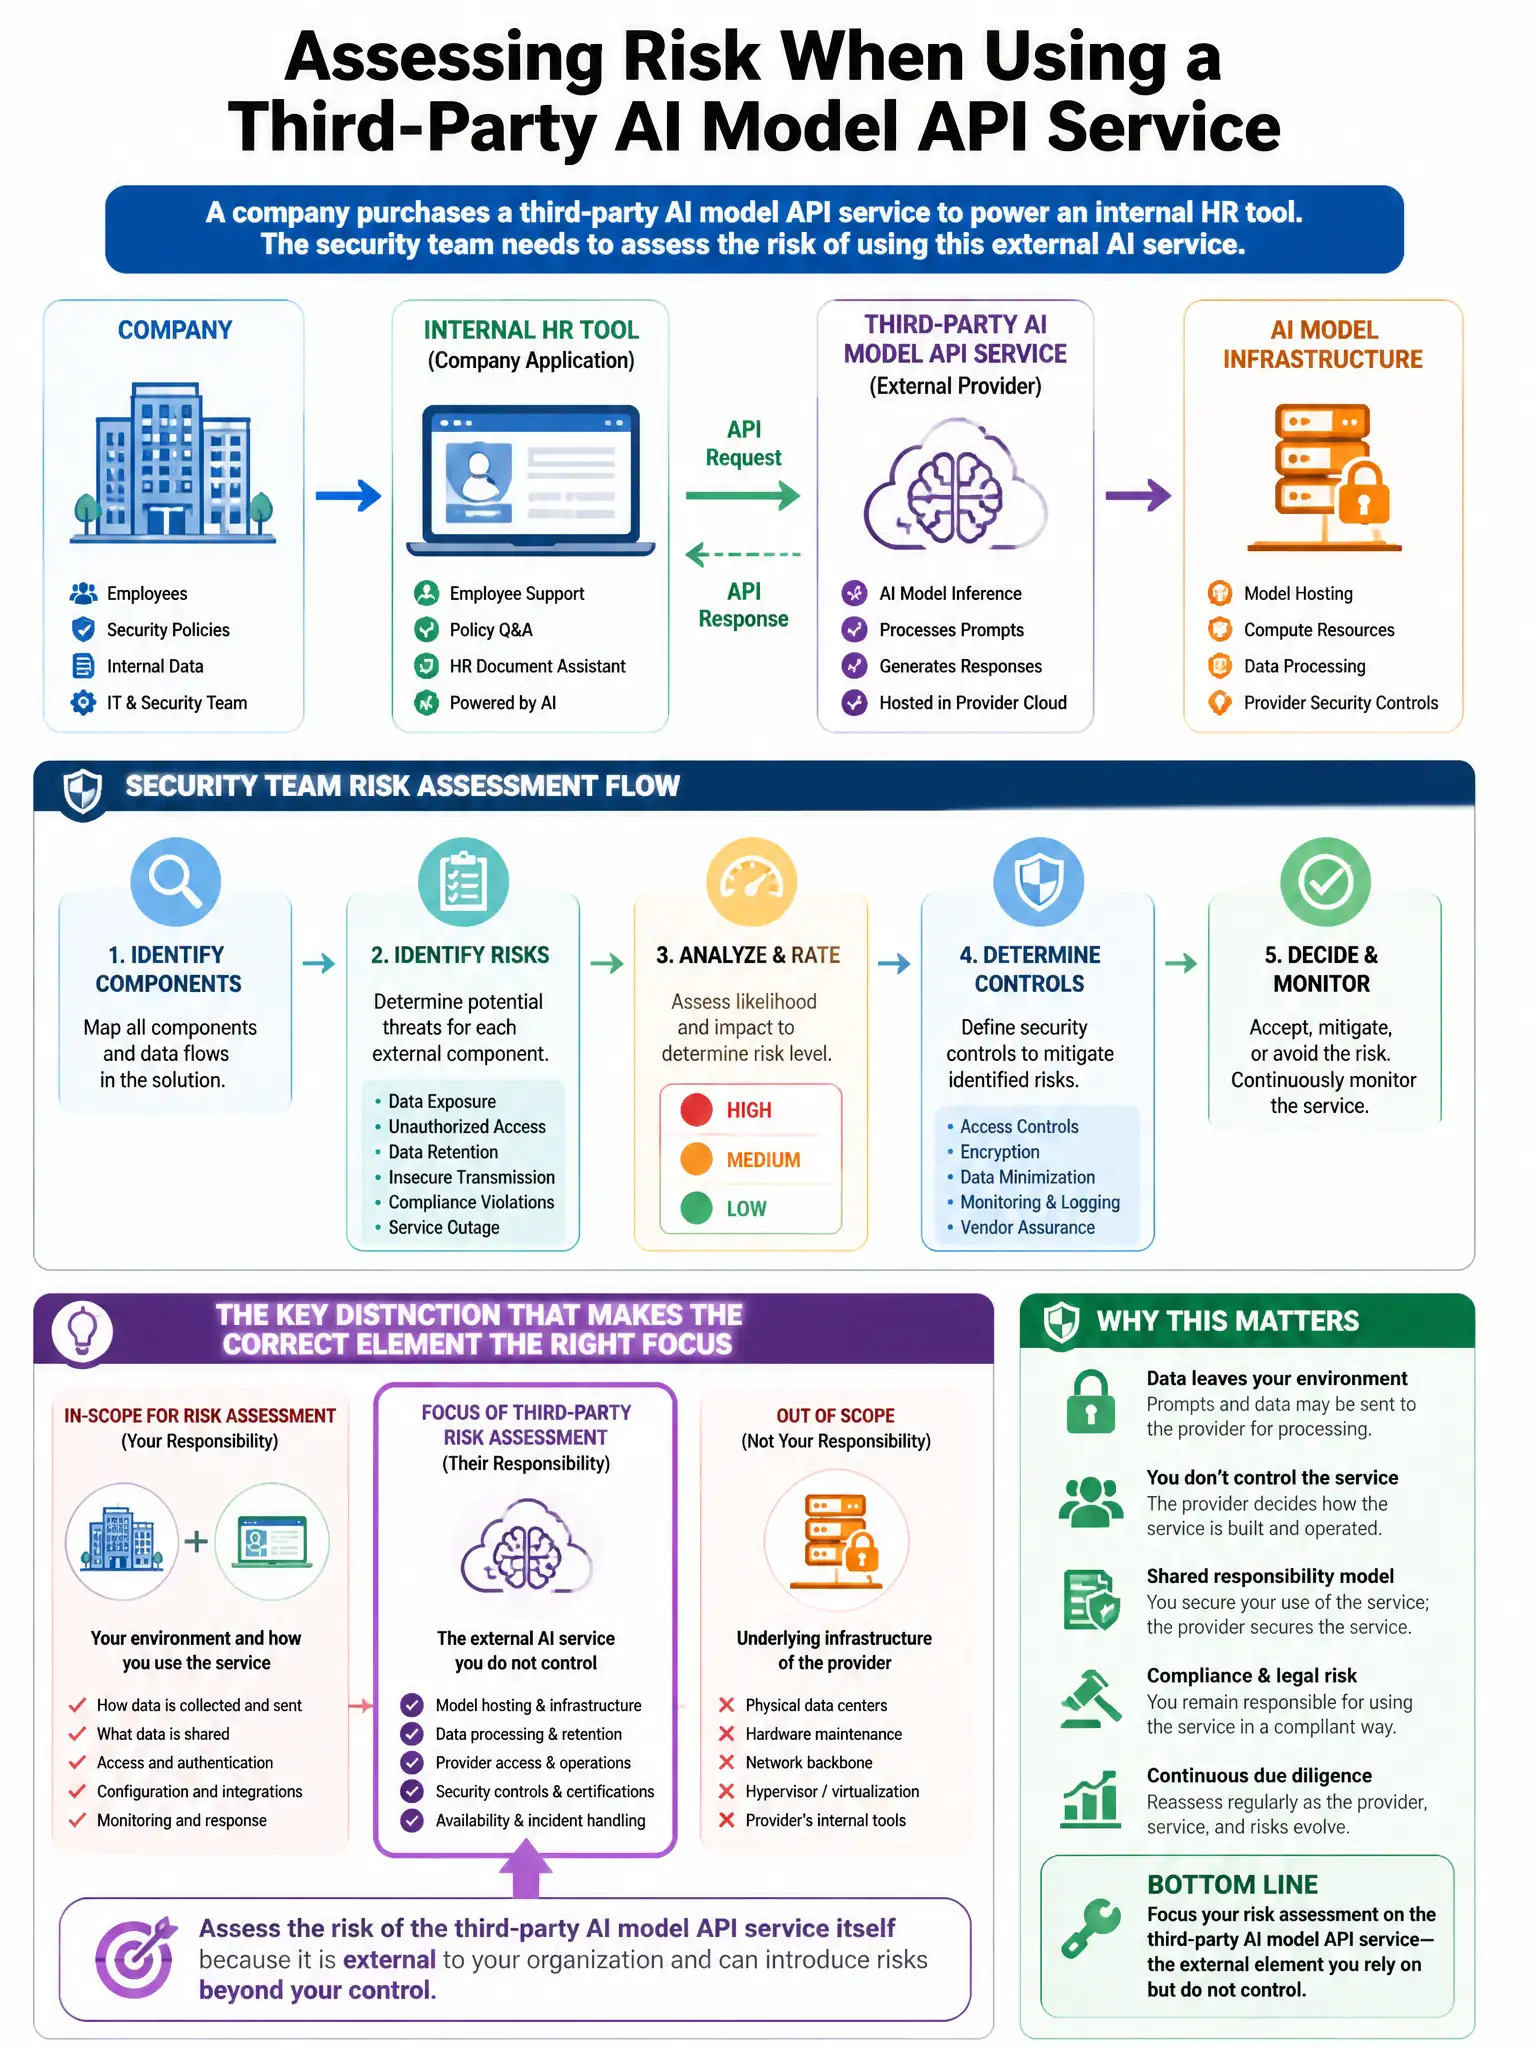
A company purchases a third-party AI model API service to power an internal HR tool. The security team needs to assess the risk of using this external AI service. Which element is most critical to evaluate in the vendor security review for an AI API service?
Select an answer to reveal the explanation.
Short Explanation
You need to look at the vendor's data processing agreement, model training data provenance, and security certifications like SOC 2 and ISO 27001. That tells you how your HR data will be used, protected, and independently audited. Everything else is secondary.
Full Explanation
The correct element is the vendor's data processing agreement (DPA), model training data provenance, and security certifications (SOC 2 Type II, ISO 27001), because a comprehensive third-party AI vendor security review must examine: (1) the Data Processing Agreement to understand what data the vendor can use and how it is protected, (2) model training data provenance to assess risks of biased, poisoned, or legally encumbered training data, and (3) security certifications (SOC 2 Type II, ISO 27001) that provide independent assurance of the vendor's security controls. These directly address the security and compliance risks of entrusting sensitive HR data to an external AI API. The geographic headquarters location option is wrong because headquarters location is relevant for data sovereignty analysis but is a secondary consideration compared to the data handling, security controls, and certification evidence. The number of enterprise customers option is wrong because customer count is a business indicator, not a security risk assessment criterion. The pricing model and SLA uptime guarantee option is wrong because pricing and SLA uptime address cost and availability, not security risk.