
A security team needs to audit all access to Azure Key Vault secrets used by Azure AI services. They want to generate alerts when a secret is accessed more than 100 times within one minute, which may indicate unauthorized automated secret scraping. Which Azure service combination achieves this monitoring and alerting?
Select an answer to reveal the explanation.
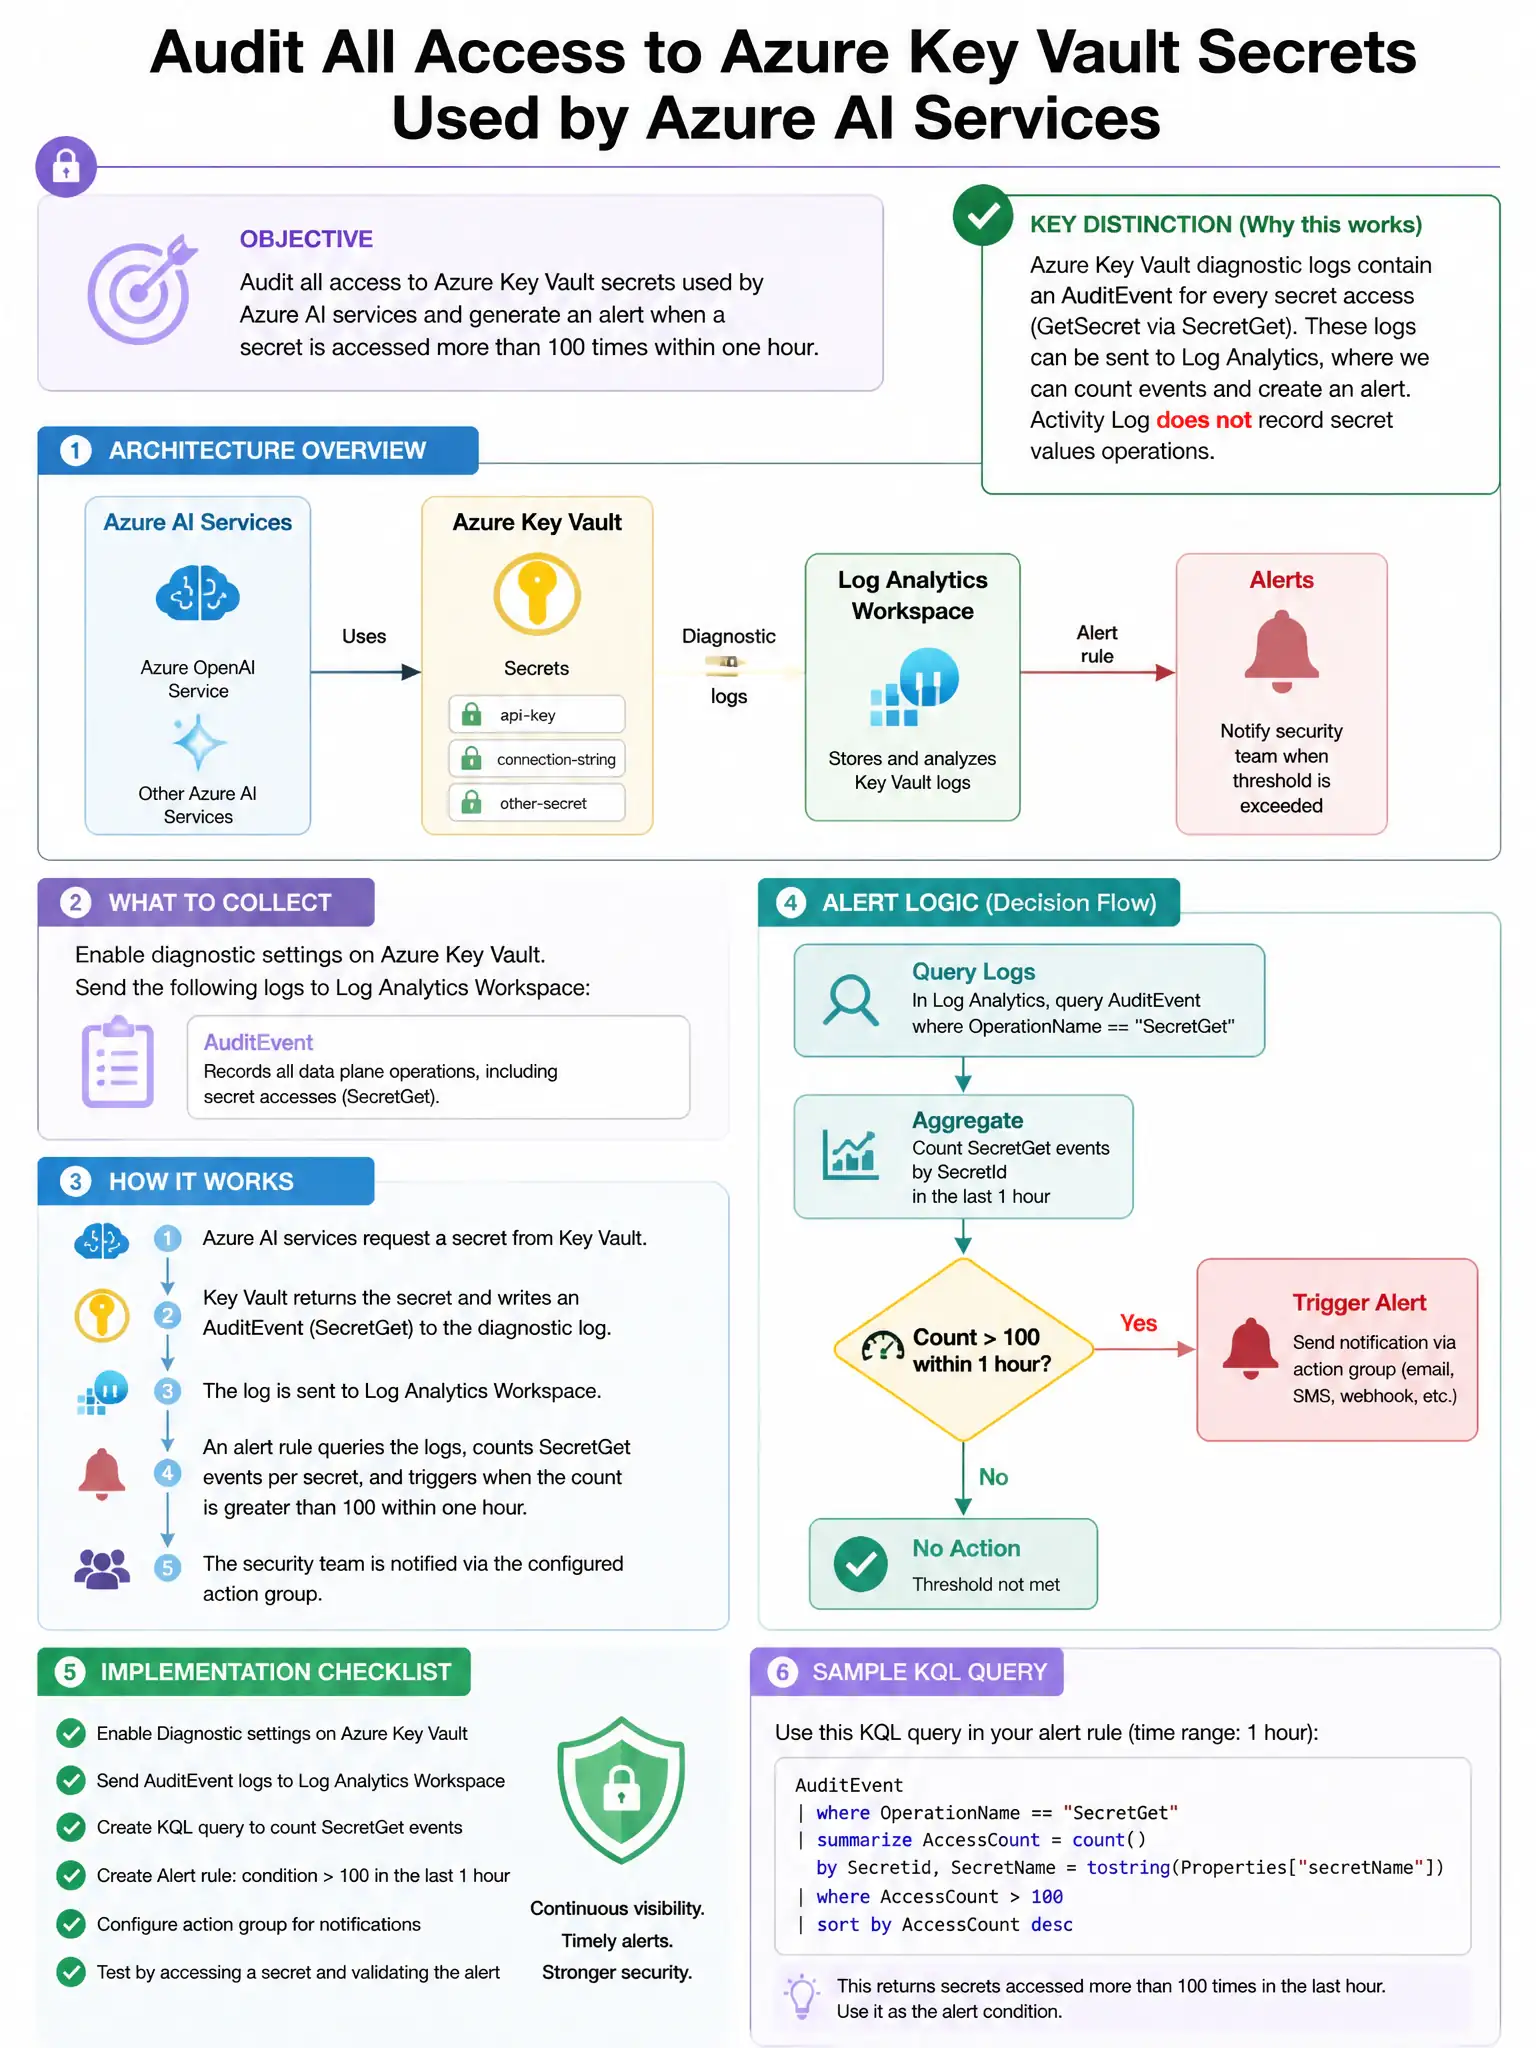
Short Explanation
You need Key Vault diagnostic logs in Log Analytics and an Azure Monitor alert rule with a KQL query. That lets you count SecretGet events per minute and fire when access exceeds 100, catching automated scraping.
Full Explanation
The correct approach is to enable Azure Key Vault diagnostic logging to a Log Analytics workspace and create an Azure Monitor alert rule based on a KQL query. Key Vault diagnostic logs include data plane audit events such as SecretGet, so the logs contain the secret access operations the security team needs to audit. In Log Analytics, you can write a KQL query that counts SecretGet events per minute and per source, then configure an Azure Monitor alert rule to fire when the count exceeds 100 within one minute. This combination provides both the audit trail and the threshold-based alerting required to detect possible automated secret scraping.
The Microsoft Defender for Key Vault option with a custom threat detection rule is wrong because Defender for Key Vault uses built-in anomaly detection and machine learning to identify suspicious patterns, but it does not provide the kind of custom threshold-based rule needed to alert specifically when secret accesses exceed 100 times per minute. The Azure Policy audit effect option is wrong because Azure Policy evaluates resource configuration and compliance state, not runtime access event frequency or patterns such as repeated secret reads. The Azure Activity Log alerts option is wrong because Activity Logs capture management plane operations, such as creating or modifying Key Vault resources and changing access policies, not data plane operations like reading secrets or downloading certificates; those data plane access events require Key Vault diagnostic logs.