
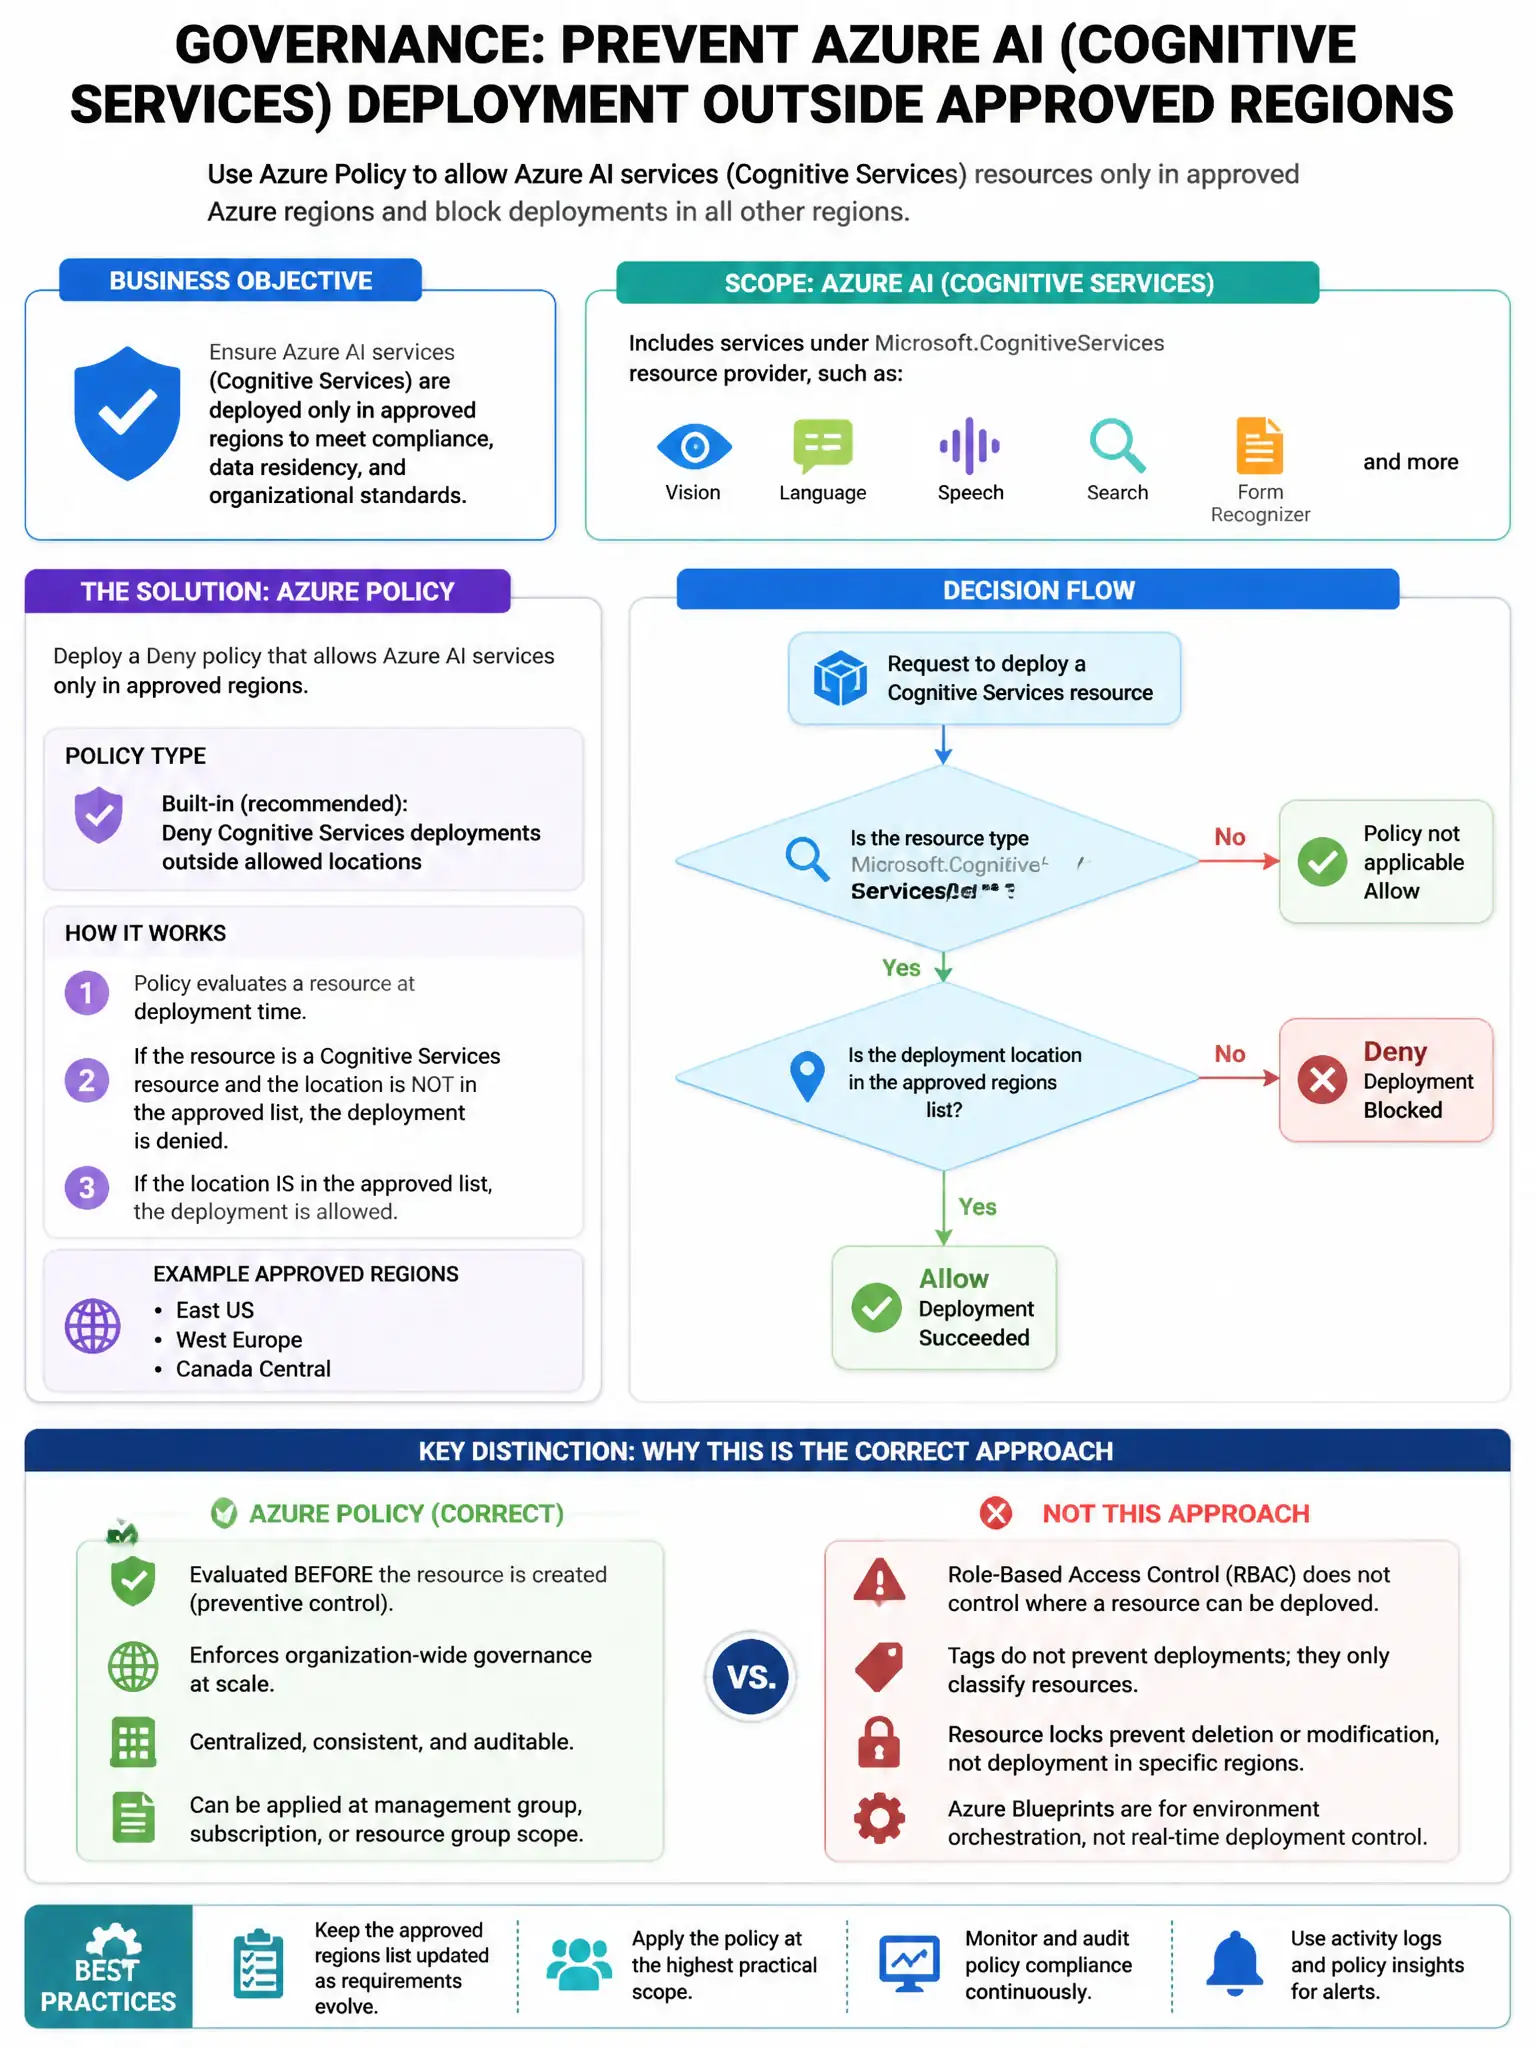
An organization wants to prevent Azure AI services (Cognitive Services) resources from being deployed outside of approved Azure regions. The governance policy should also prevent deploying AI resources without enabling private endpoints. Which Azure service enforces these requirements at scale?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need Azure Policy with deny effects for non-compliant AI resource configurations. It can block Cognitive Services deployments in unapproved regions and block resources that don't use private endpoints.
Full Explanation
Azure Policy with deny effects for non-compliant AI resource configurations is correct because Azure Policy can enforce organizational standards at scale through policy definitions with 'deny' effects. You can create policies that deny creation of Cognitive Services resources in non-approved regions and deny resources where public network access is enabled, which is the condition where private endpoints are not configured. Policy initiatives can group multiple policies for AI governance. Microsoft Defender for Cloud security recommendations is wrong because Defender for Cloud recommendations are advisory, audit-mode findings that generate alerts but do not prevent resource deployment. Azure Blueprints with resource lock assignments is wrong because Azure Blueprints, deprecated in favor of Azure Deployment Environments and Template Specs, can assign policies but add a layer of complexity; Azure Policy alone is the direct mechanism for enforcement. Microsoft Purview data governance policies is wrong because Microsoft Purview manages data assets and classification, not Azure resource deployment enforcement.