
A security engineer is configuring a Microsoft Purview Communication Compliance policy to detect when employees use Microsoft Copilot for Microsoft 365 to generate content that contains discriminatory language. Which configuration is required?
Select an answer to reveal the explanation.
Short Explanation
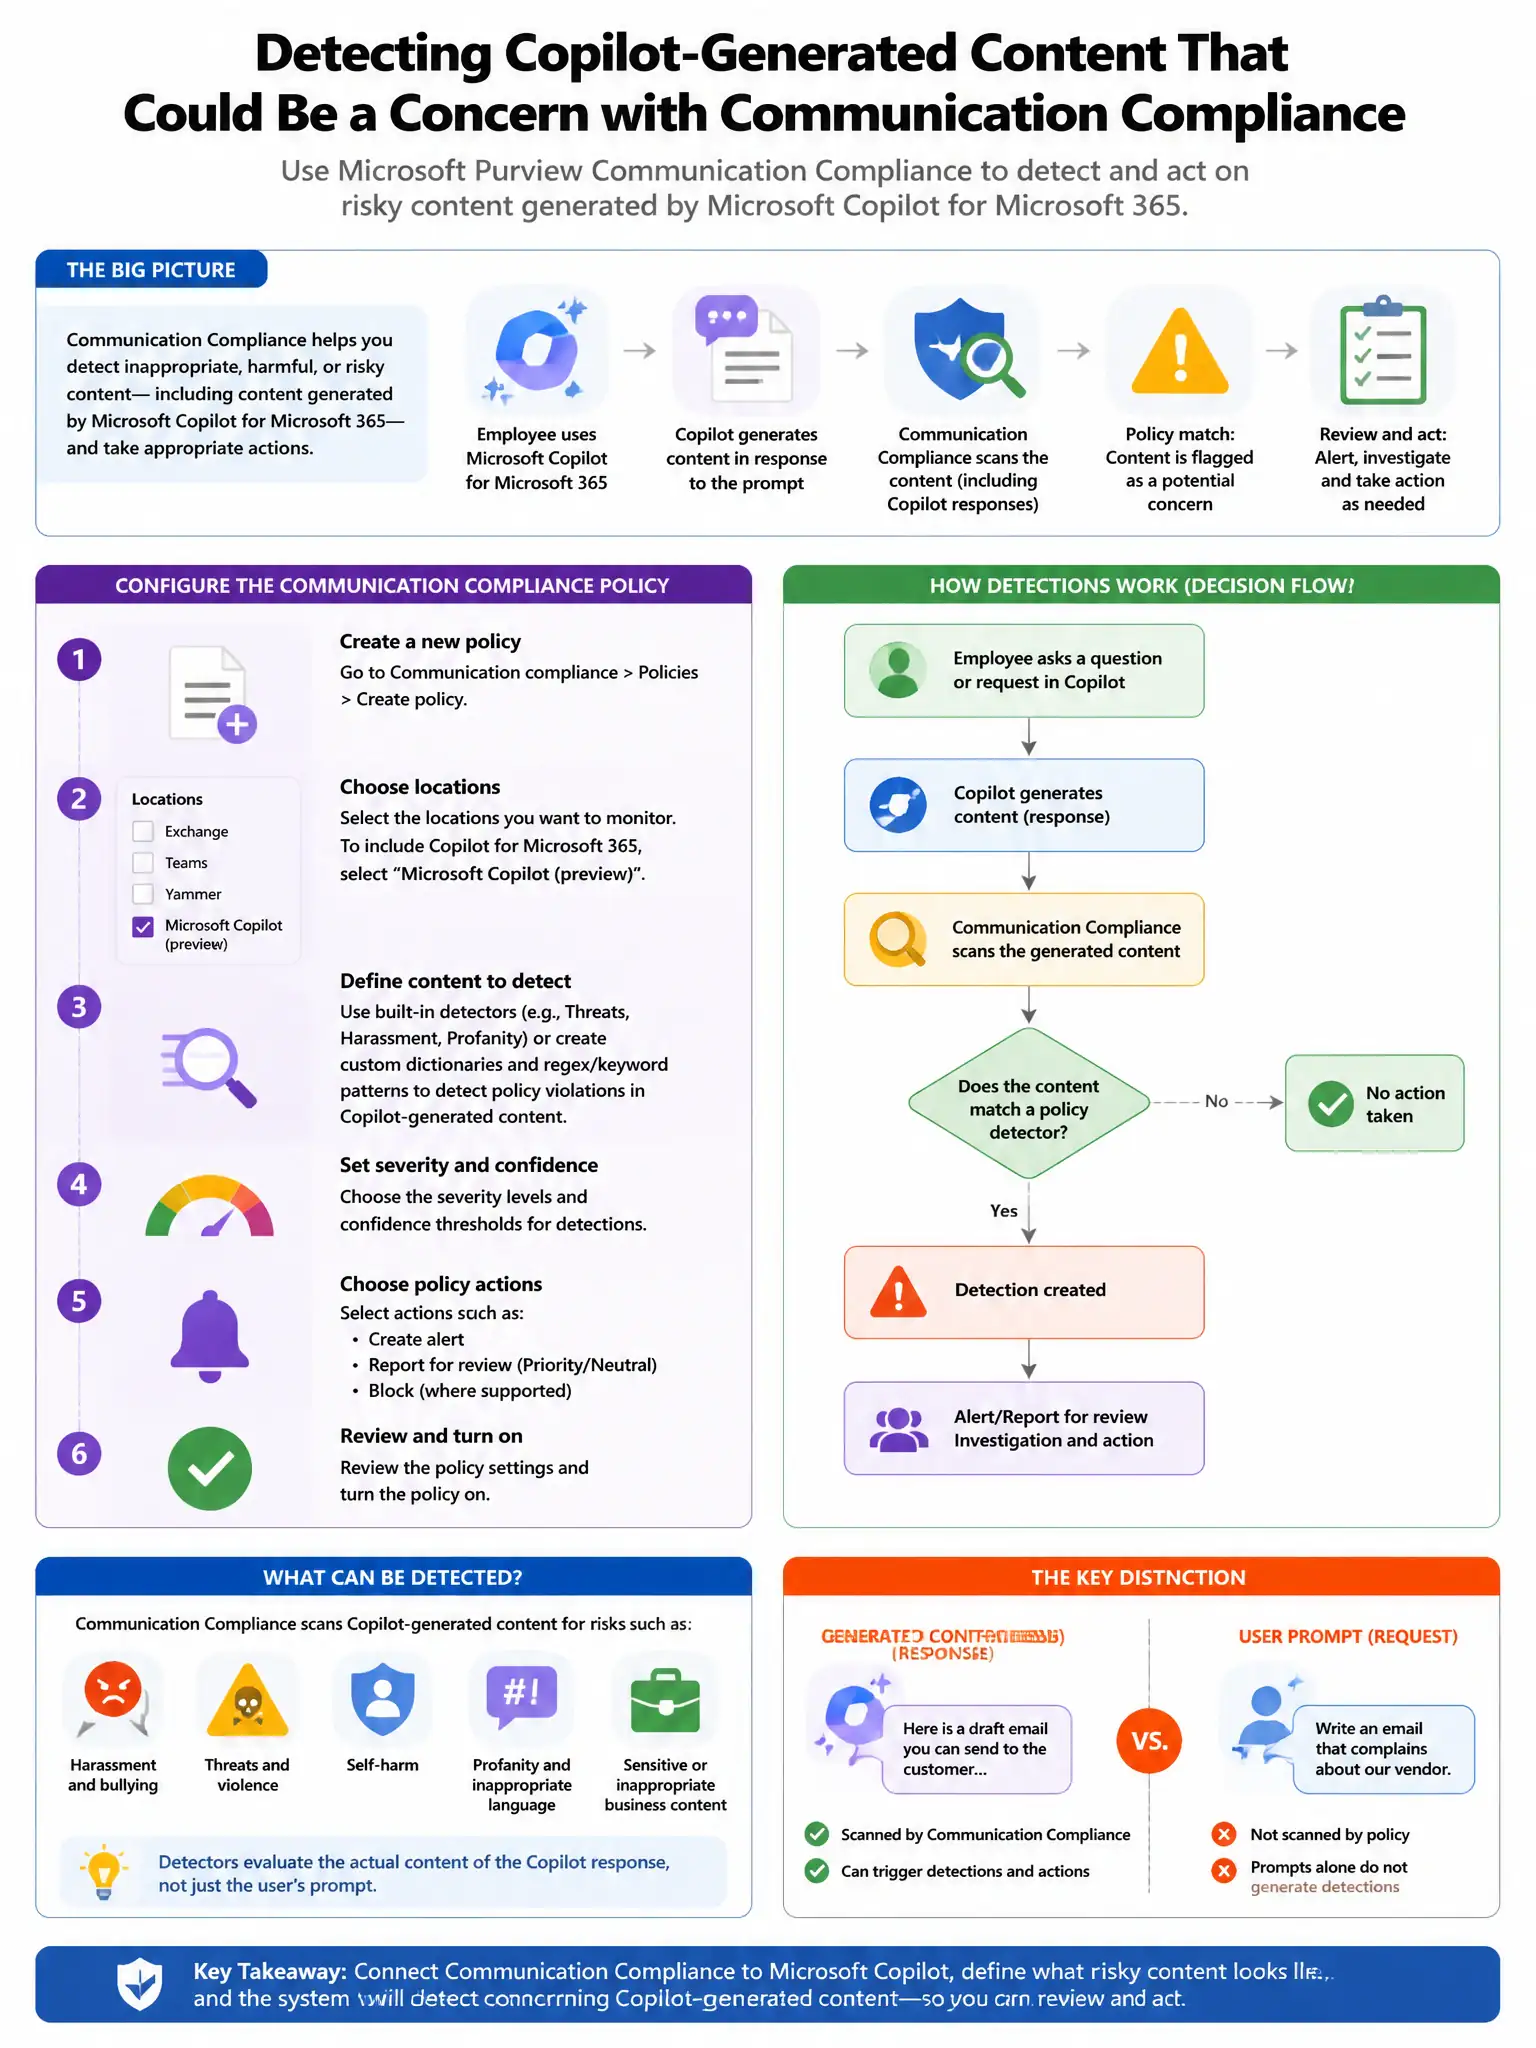
Here's the deal — you need a Communication Compliance policy with Microsoft 365 Copilot as a supervised location, then use the built-in Offensive language classifier to catch discriminatory text. That's how Purview scans Copilot interactions for policy-violating language.
Full Explanation
The correct configuration is a Communication Compliance policy with Microsoft 365 Copilot as a supervised location and the built-in Offensive language classifier. Microsoft Purview Communication Compliance supports Microsoft 365 Copilot as a supervised communication location. You can create a policy that monitors Copilot interactions and applies trainable classifiers such as the built-in Offensive language or Threat classifier to detect discriminatory or policy-violating content generated by or submitted to Copilot. The DLP policy targeting Copilot with a custom sensitive information type for discriminatory language is wrong because DLP policies use sensitive information types, such as structured patterns like SSN or credit card numbers, and do not use trainable classifiers for nuanced language like discriminatory content. The Insider Risk Management policy with a data leak indicator for Copilot is wrong because Insider Risk Management focuses on behavioral risk indicators around data handling, not detecting specific language content in artificial intelligence outputs. Enabling Microsoft Defender for Cloud Apps monitoring for Copilot with a session policy is wrong because Defender for Cloud Apps session policies manage application-level controls, not content classification of generated text.