
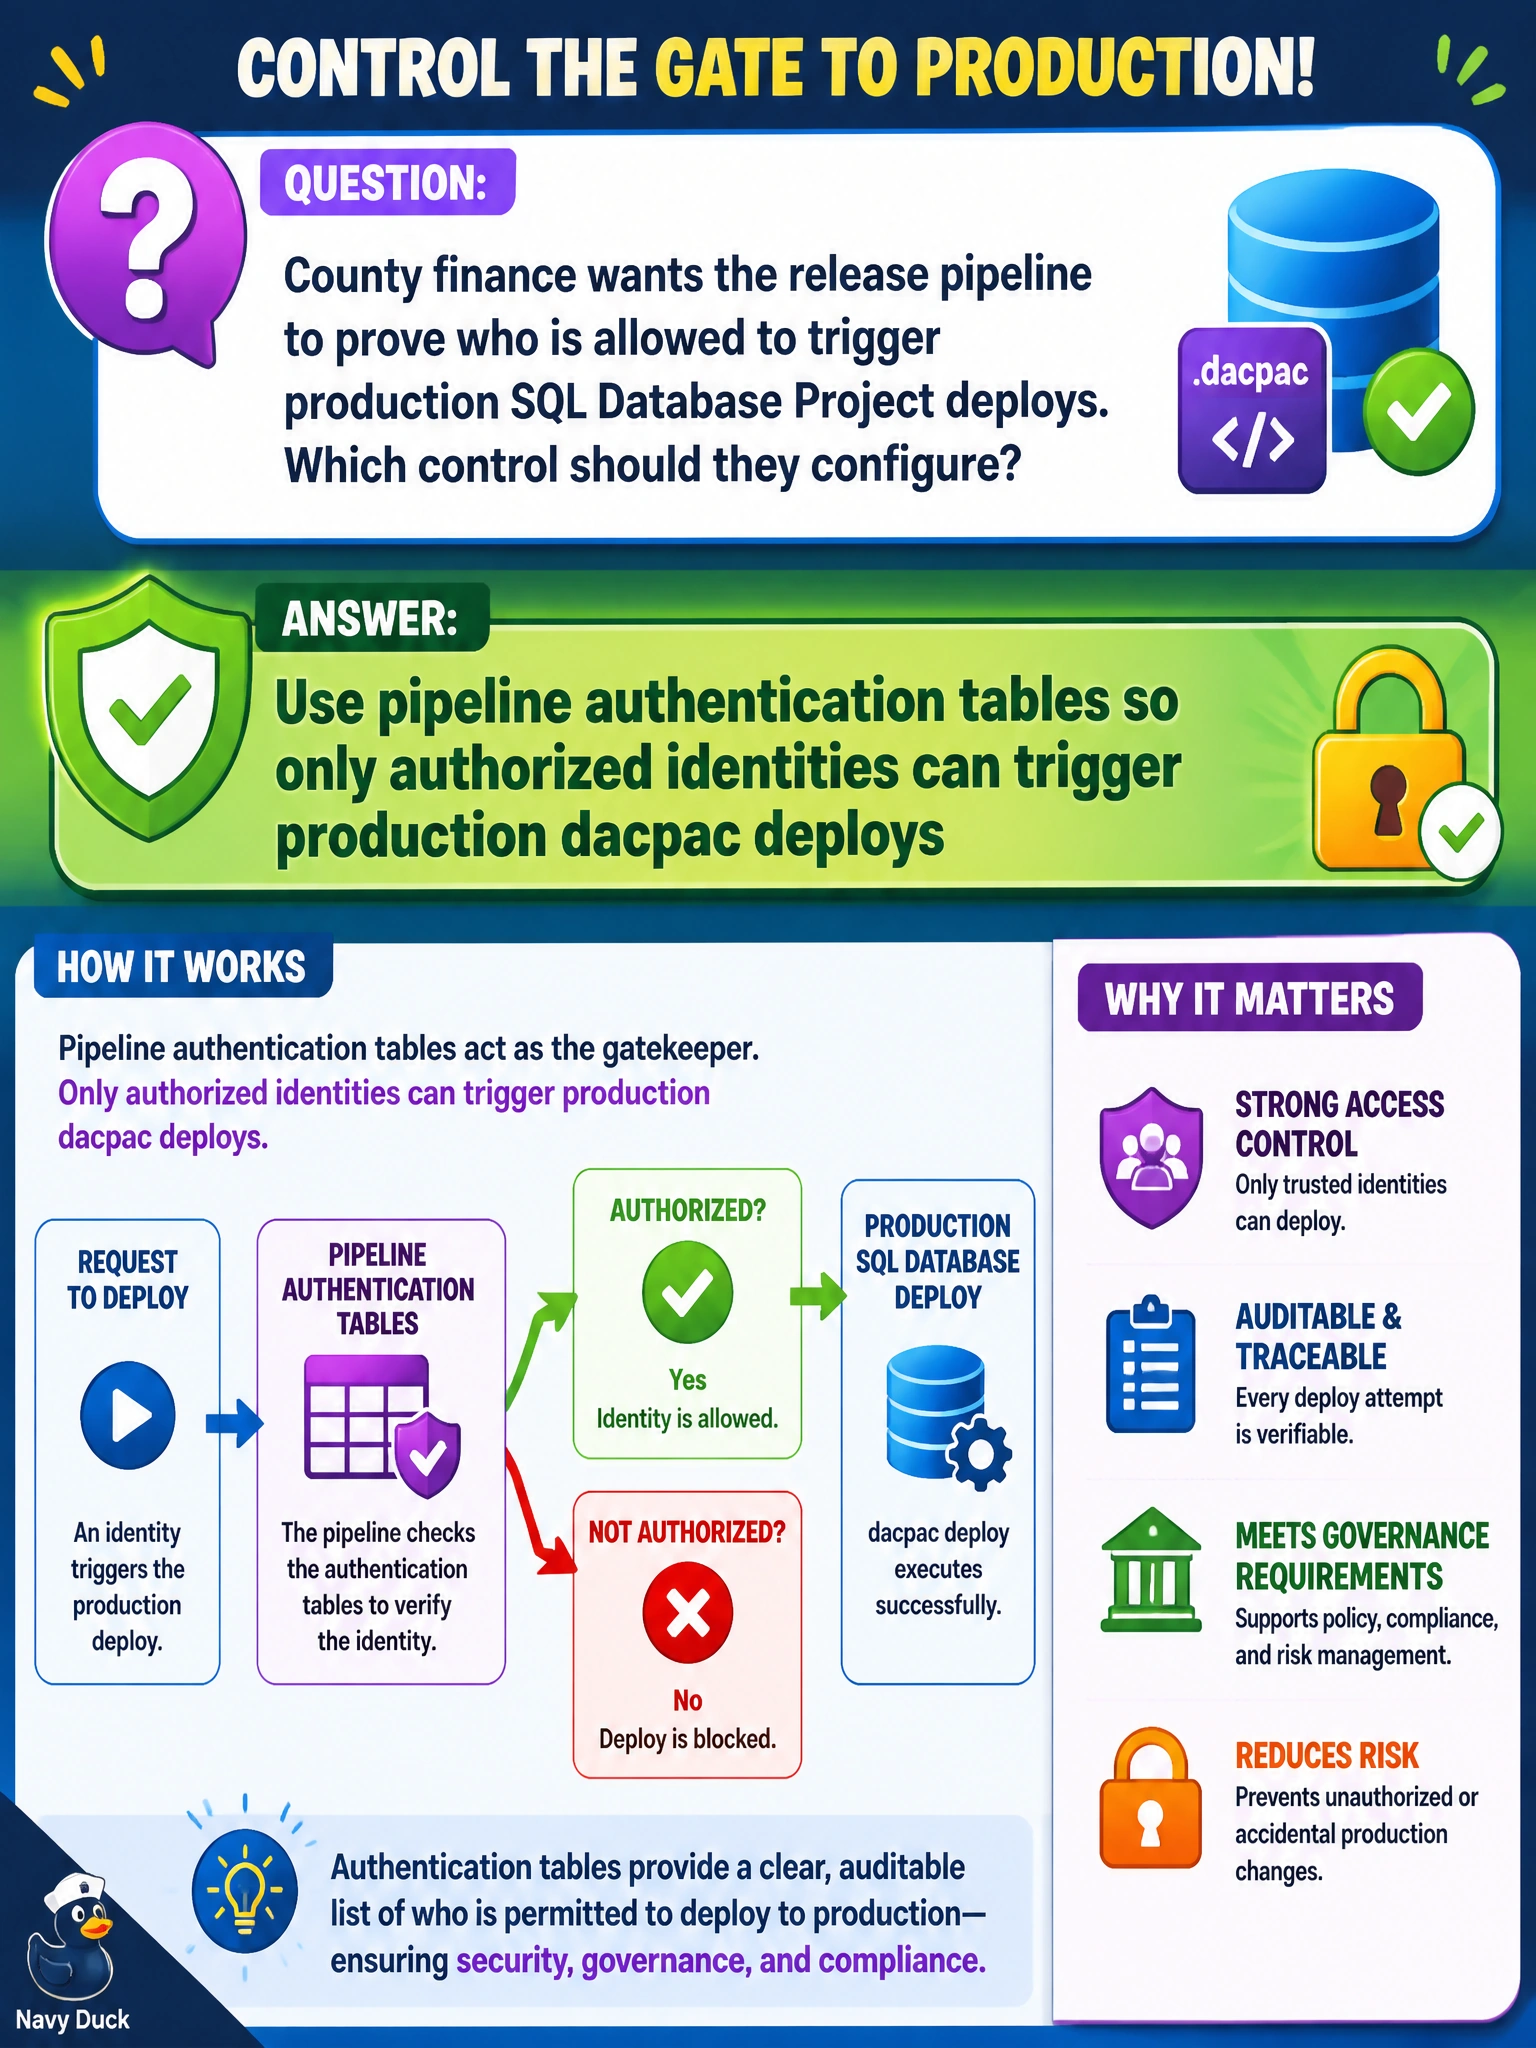
County finance wants the release pipeline to prove who is allowed to trigger production SQL Database Project deploys. Which control should they configure?
Select an answer to reveal the explanation.
Short Explanation
Authentication tables are the guest list for finance’s prod deploy party—if your identity isn’t on it, you don’t get to push the dacpac button.
Full Explanation
County finance needs the release pipeline to prove which identities may trigger production SQL Database Project deploys. Pipeline authentication tables (or equivalent pipeline permission/authorization controls that bind who can start production jobs) enforce that only authorized principals can kick off dacpac releases. That control supports least privilege, separation of duties, and an auditable release trail for municipal finance databases—aligning with DP-800 expectations for securing deployment of database solutions rather than treating production publish as an open button.
Allowing anonymous pipeline runs with no identity checks fails by removing attribution and authorization; anyone who can reach the pipeline surface could push finance schema or data-tier changes without a principal to audit. Embedding a shared password in YAML checked into a public fork fails as credential leakage and shared-secret anti-pattern: the secret is durable in git history and not bound to individual deployers. Disabling authentication so weekend on-call can deploy without audit trails fails by trading convenience for unverifiable production change—finance controls require identity-bound triggers even during off-hours.
Exam caveat: DP-800 secure-deploy items favor identity-based pipeline authorization and secret stores over anonymous runs or credentials committed to source. “On-call speed” distractors that remove authentication are incorrect when the stem asks who is allowed to trigger production deploys.
Operational check: configure the production deploy stage so only the finance release service principal or named approver group can queue it; attempt a run as an unauthorized developer identity and confirm denial; succeed with an authorized identity and verify pipeline logs record which principal started the dacpac publish. Rotate any previously shared passwords out of YAML into Key Vault or Actions secrets as a companion hygiene step.