
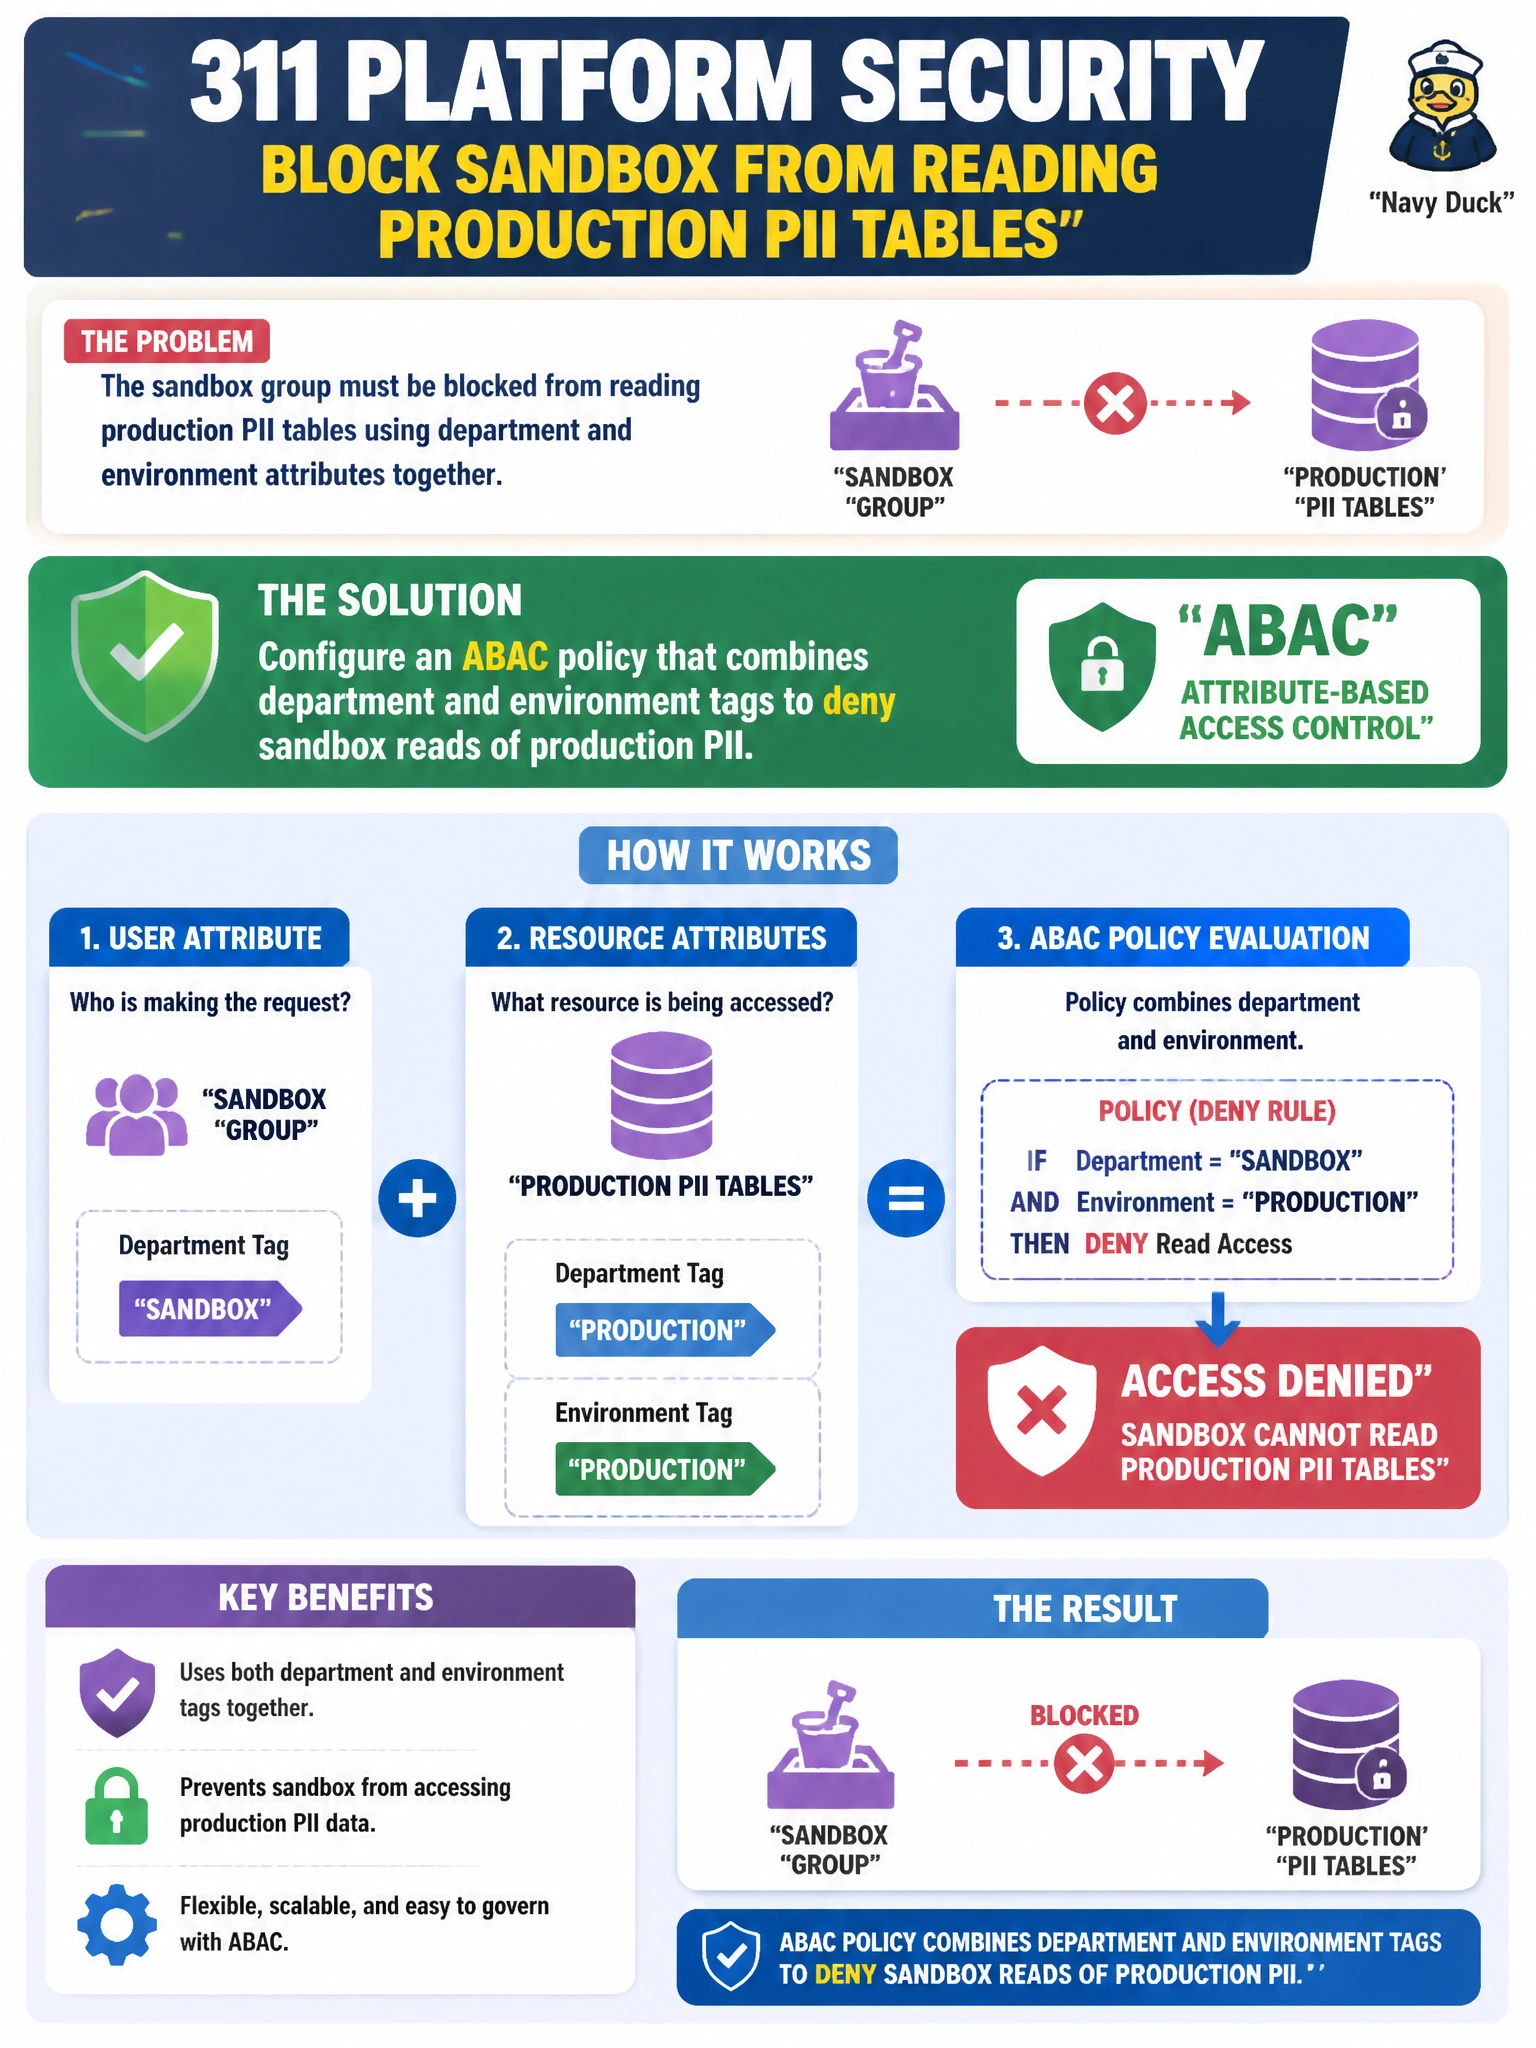
A 311 platform must block the sandbox group from reading production PII tables using department and environment attributes together. What should engineers configure?
Select an answer to reveal the explanation.
Short Explanation
Stacked tags are like two locks on the 311 PII vault—department and environment both have to line up before the sandbox group gets in, and in prod they do not.
Full Explanation
An ABAC policy that combines department and environment tags to deny sandbox reads of production PII is the correct configuration for a 311 platform that must block the sandbox group using department and environment attributes together. Attribute-based policies can require multiple predicates—for example, deny when environment is production and the caller is sandbox—so civic PII tables stay closed to non-production principals even if someone mistakenly grants a broad catalog browse right. A role-based policy that combines department and environment tags to deny sandbox reads of production PII fails by concept because it relies on role membership rather than ABAC evaluation of department and environment attributes together, so it cannot enforce the conjunctive ABAC block the stem requires. A retention policy that combines department and environment tags to deny sandbox reads of production PII fails by concept because retention governs data lifecycle and deletion rather than denying table reads, so it cannot block the sandbox path the stem requires. A data masking policy that combines department and environment tags to deny sandbox reads of production PII fails by concept because masking redacts column values after access rather than denying table reads on department and environment attributes together, so it cannot block the sandbox path the stem requires. Exam caveat: Multi-attribute ABAC denial is different from retention when the business rule is a conjunctive block (department AND environment) because retention governs lifecycle, not reads. ABAC denial for sandbox does not replace column masks on PII fields for authorized production analysts, nor does it replace audit logging of access attempts. Ensure principals and tables are tagged consistently or the combined policy will not match. Operational check: Tag production PII tables with environment=production and appropriate department tags, ensure sandbox principals carry sandbox environment attributes, validate that sandbox SELECT is denied by the combined policy, validate that an authorized production departmental principal can still read as intended, and review a denied attempt in audit logs.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.