
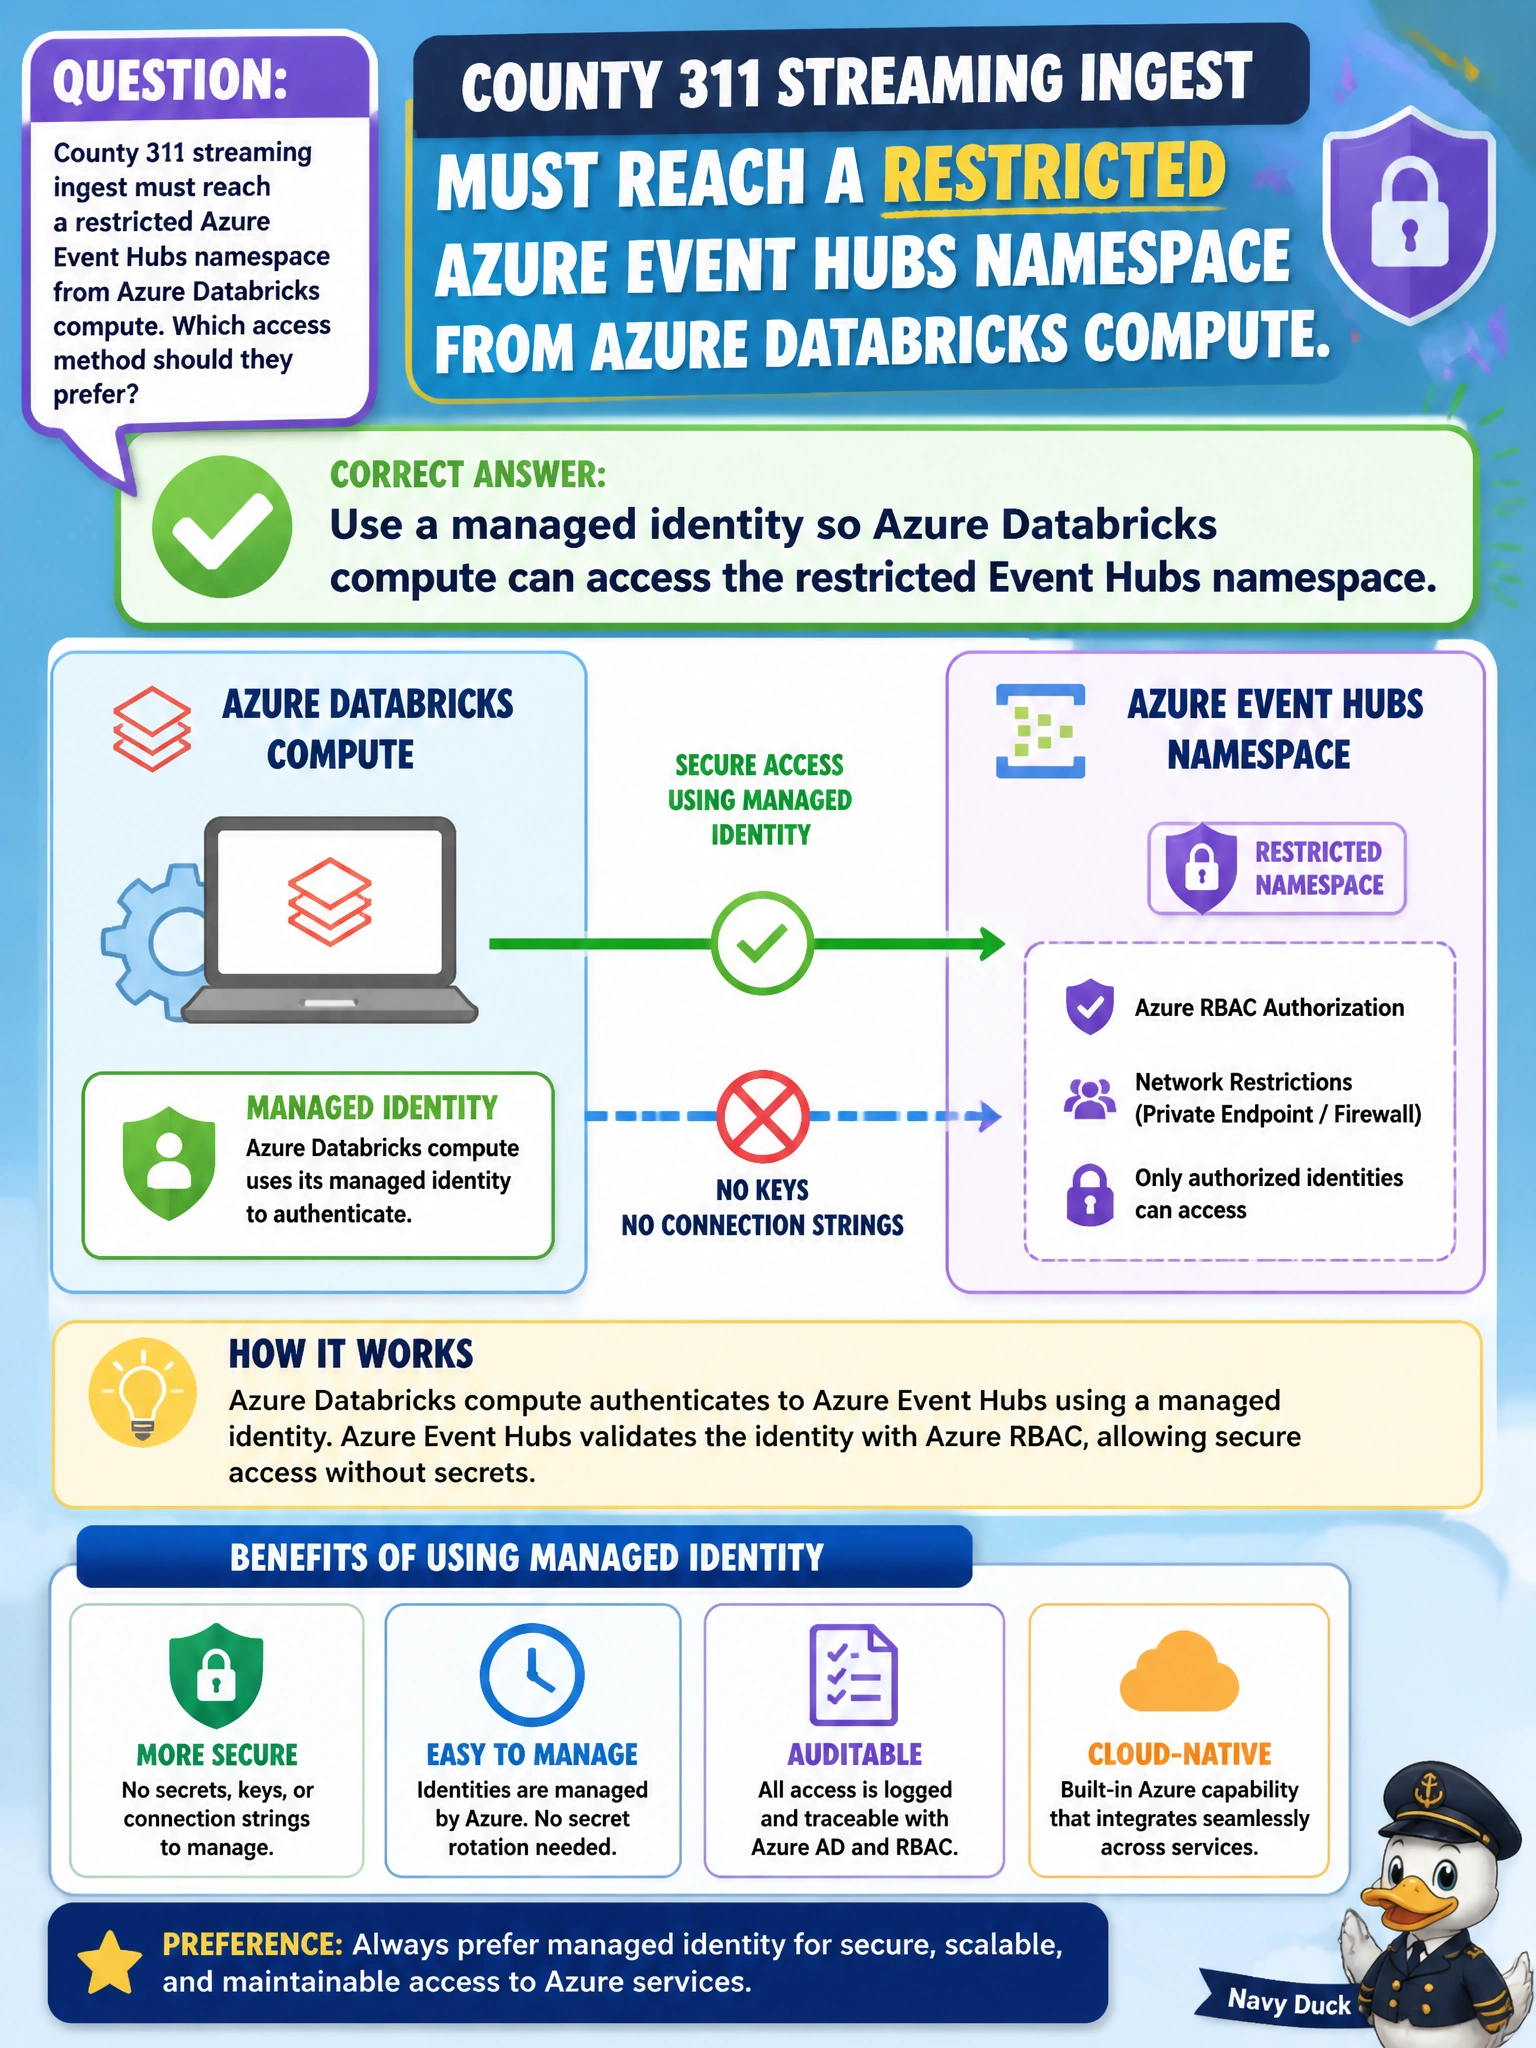
County 311 streaming ingest must reach a restricted Azure Event Hubs namespace from Azure Databricks compute. Which access method should they prefer?
Select an answer to reveal the explanation.
Short Explanation
Managed identity is the county badge reader on the Event Hubs door—compute proves who it is without mailing connection strings around. Public wikis full of keys are the opposite of restricted.
Full Explanation
County 311 streaming ingest to a restricted Azure Event Hubs namespace should authenticate Azure Databricks compute with a managed identity. Managed identity lets compute prove itself to Azure RBAC and network-restricted resources without distributing shared connection strings or keys. That matches restricted Event Hubs: firewall/VNet rules allow the Databricks egress identity, and no county staff wiki needs the keys.
Publishing Event Hubs connection strings on a public wiki for all staff defeats restriction and creates uncontrolled secret copies. Opening the Event Hubs firewall to the entire Internet for simpler tests expands attack surface on a municipal streaming backbone. Storing Event Hubs keys in plaintext notebook widgets shared across workspaces is secret sprawl without rotation discipline.
Exam caveat: managed identity must be assigned on the Databricks access mode/compute that supports it, and Azure RBAC on the Event Hubs namespace/data plane must grant that identity the right roles. Network rules and identity work together—identity alone may fail if the firewall still blocks Databricks subnets. Operational check: enable managed identity on the streaming compute, grant Azure Event Hubs data sender (or appropriate) role, confirm network allowlists include Databricks, remove wiki keys, and validate a test stream into the 311 hub.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.