
A multi-agent solution in Azure calls internal knowledge indexes and MCP tools hosted on private APIs. Compliance forbids agent traffic to those backends over the public internet. Which control should you specify?
Select an answer to reveal the explanation.
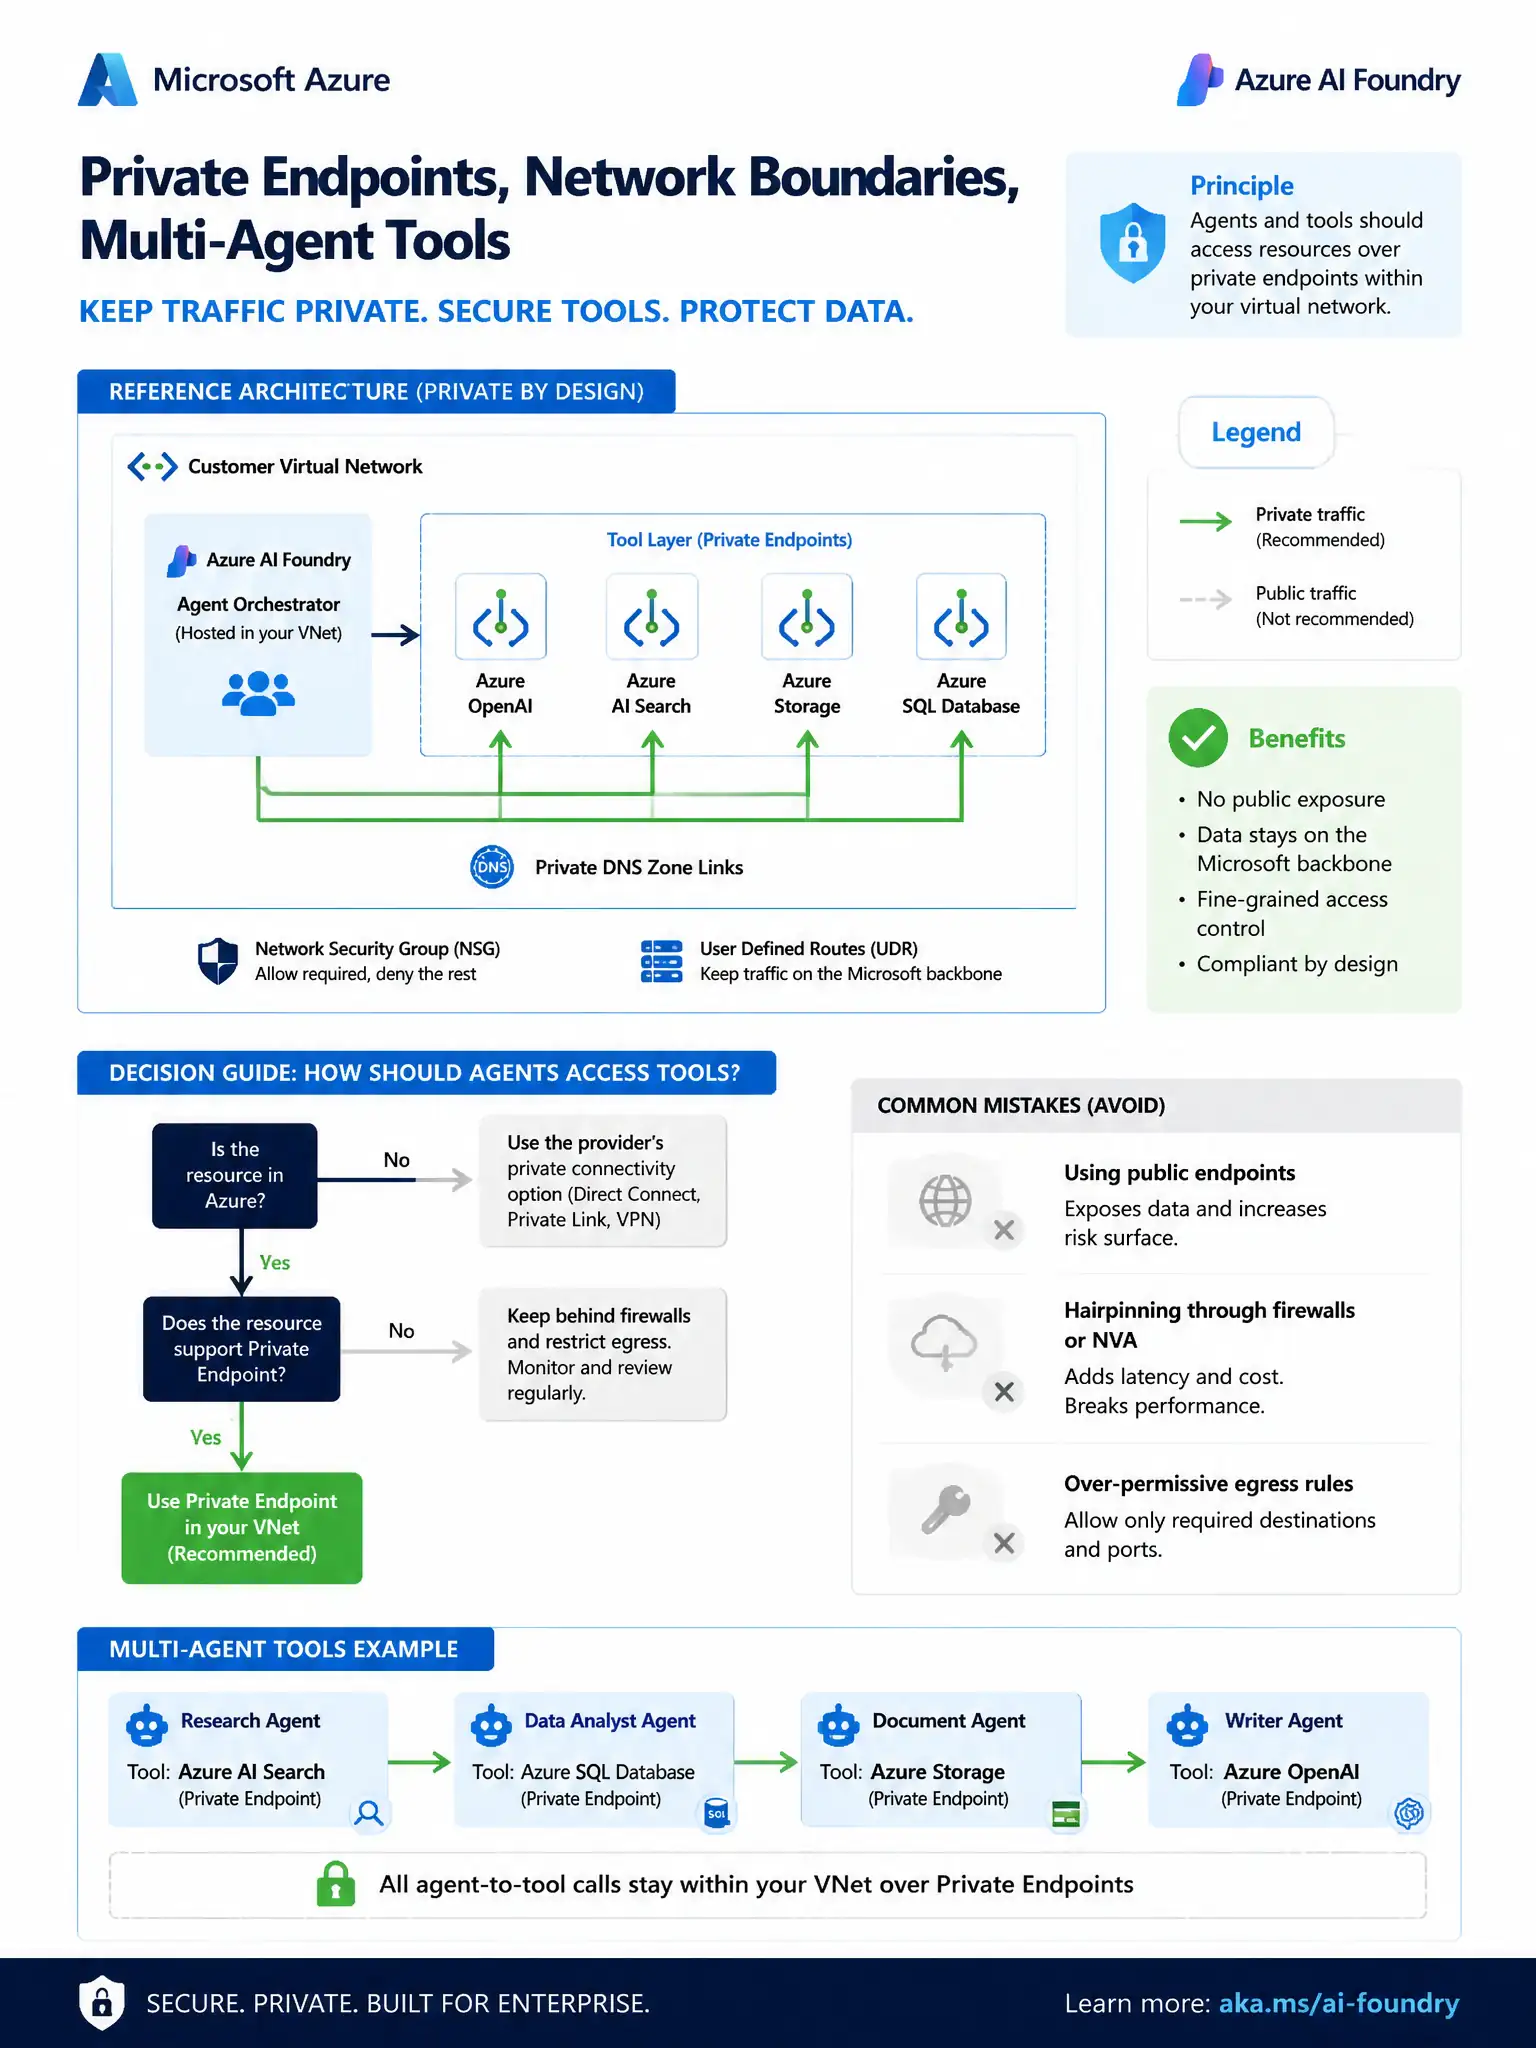
Short Explanation
You need private endpoints or VNet integration so agent compute reaches knowledge indexes and MCP tool APIs without crossing the public internet. Pair that with identity-based access controls so only authorized callers can use the backends. Don't expose APIs, disable TLS, or publish connection strings.
Full Explanation
Zero Trust multi-agent deployments combine network isolation with least-privilege identity. Place Foundry/agent compute so egress to RAG indexes and MCP backends uses private networking; deny public data-plane paths where policy requires. Network boundaries using private endpoints/VNet integration and related private connectivity keep agent traffic off the public internet while identity-based access controls authorize callers. Exposing all internal APIs on 0.0.0.0/0 with no firewall expands attack surface. Disabling TLS to simplify packet inspection removes required transport protection. Publishing database connection strings in the public agent directory leaks secrets. Document network and identity controls together in architecture decision records.